

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
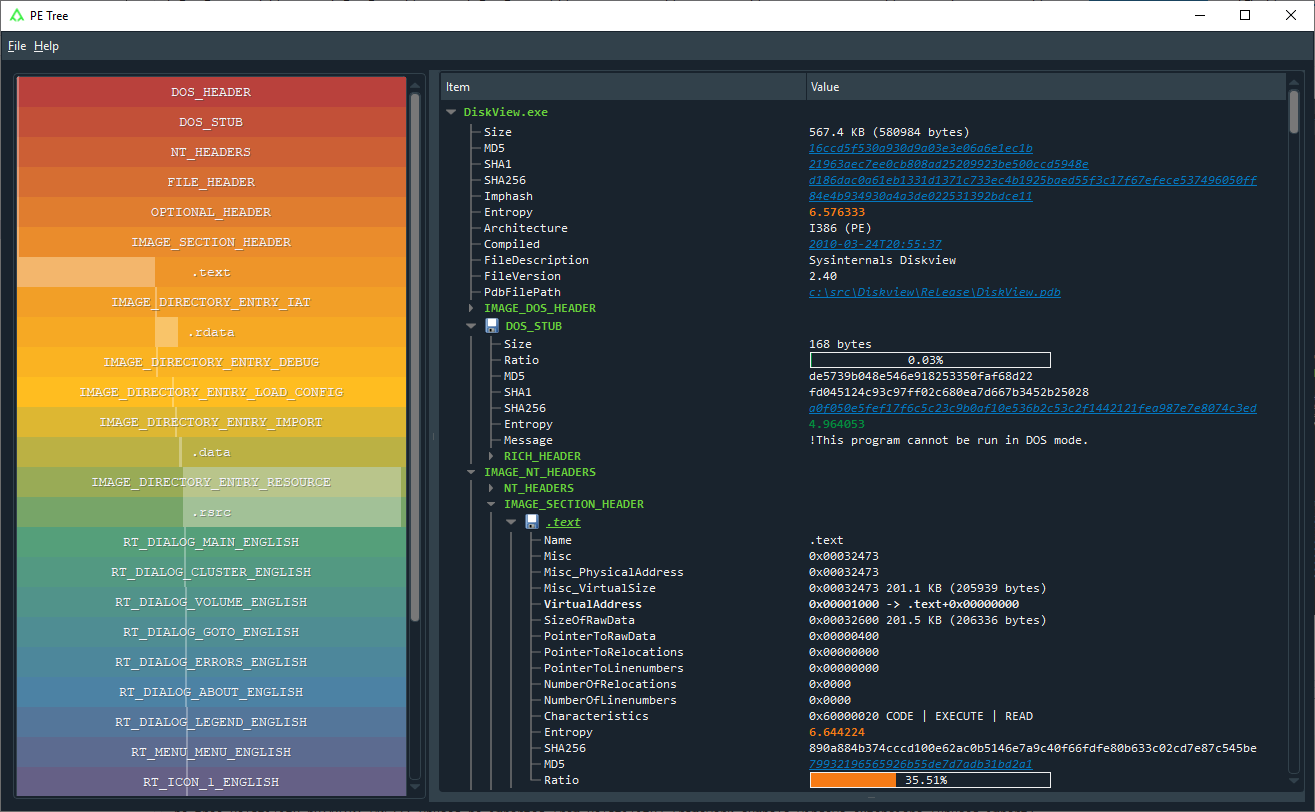 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.