

malwarescanner
 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
hash-analysisincident-responsemalware-analysis+1
90
password123456/malwarescannerHash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
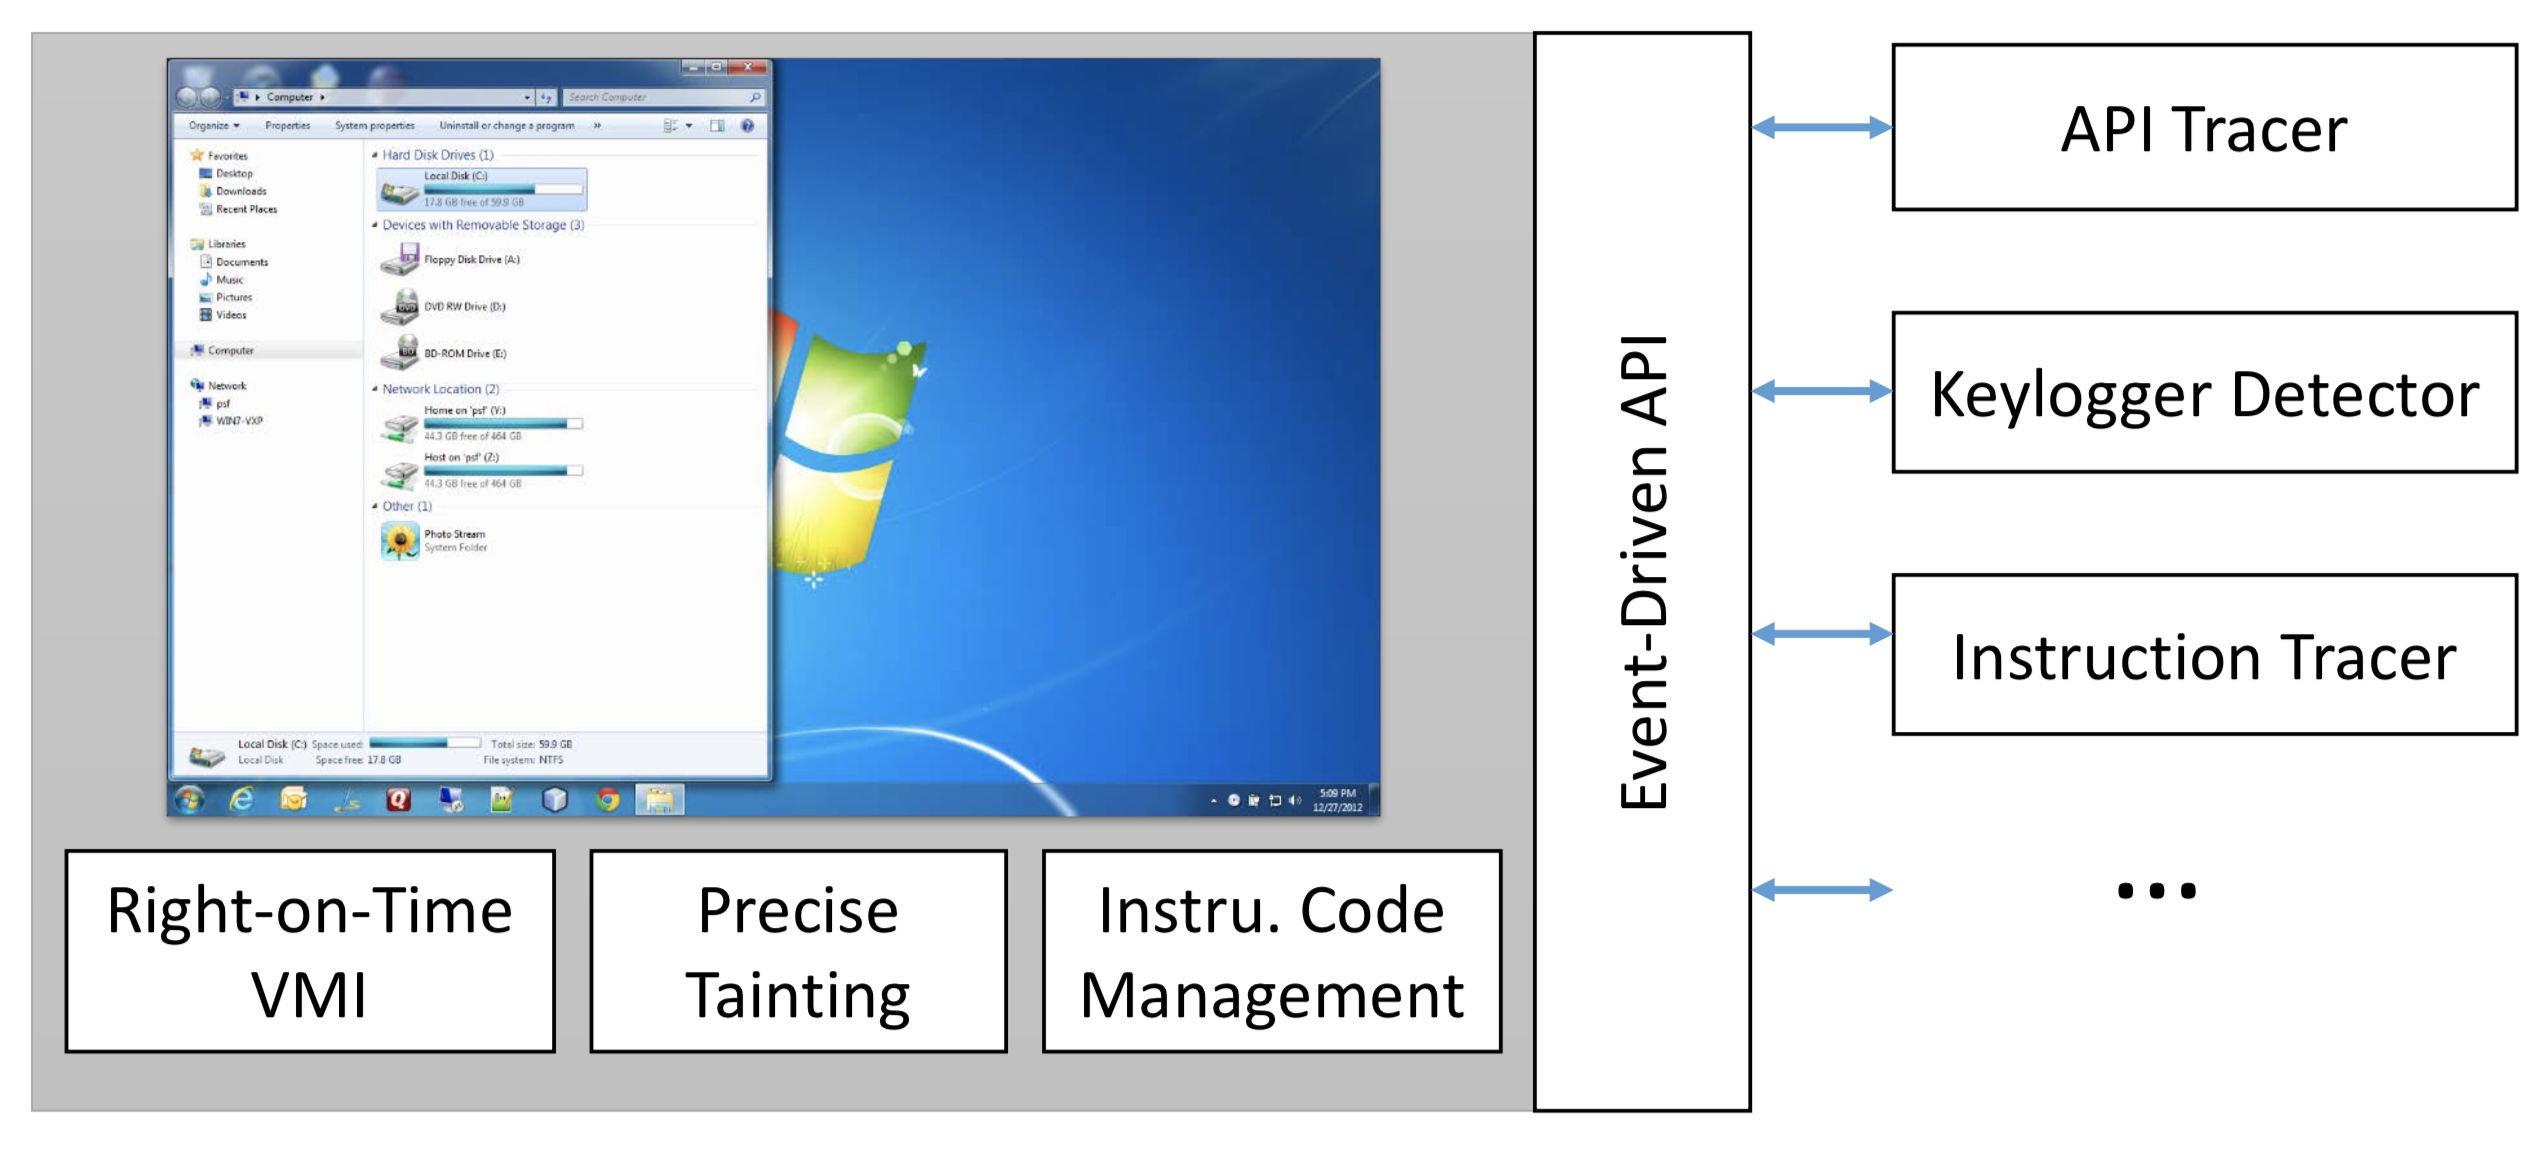 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
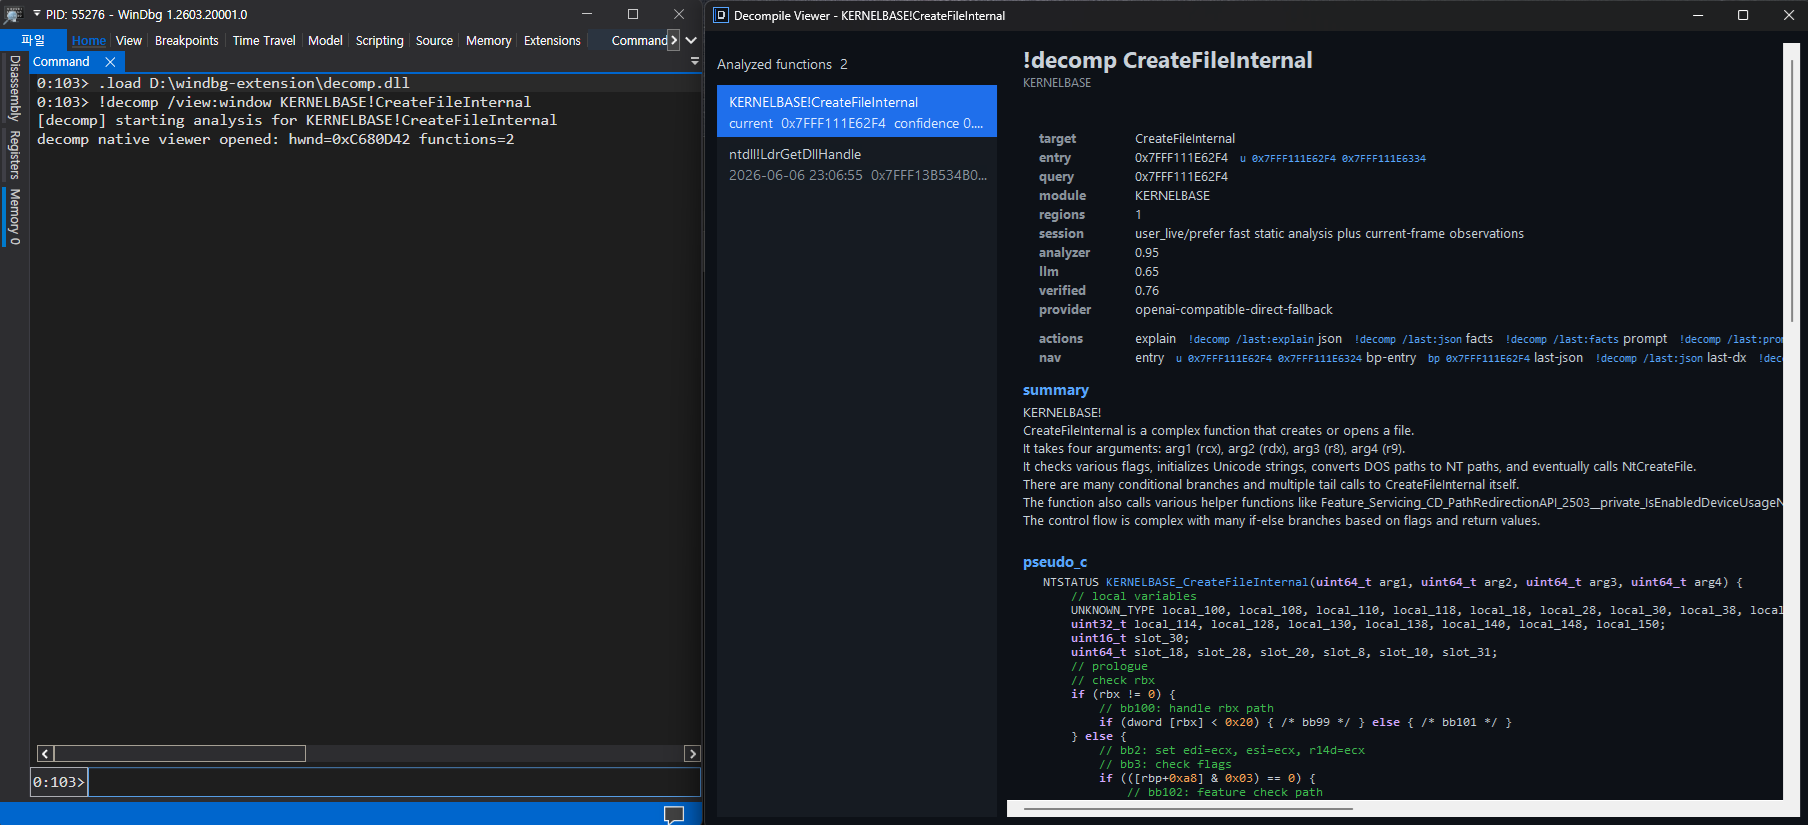 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 ammaraskar/vscode-github-token-grab-extension
Extension to grab github token from VSCode
 ernos/browser-xpi-malware-scanner
A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…
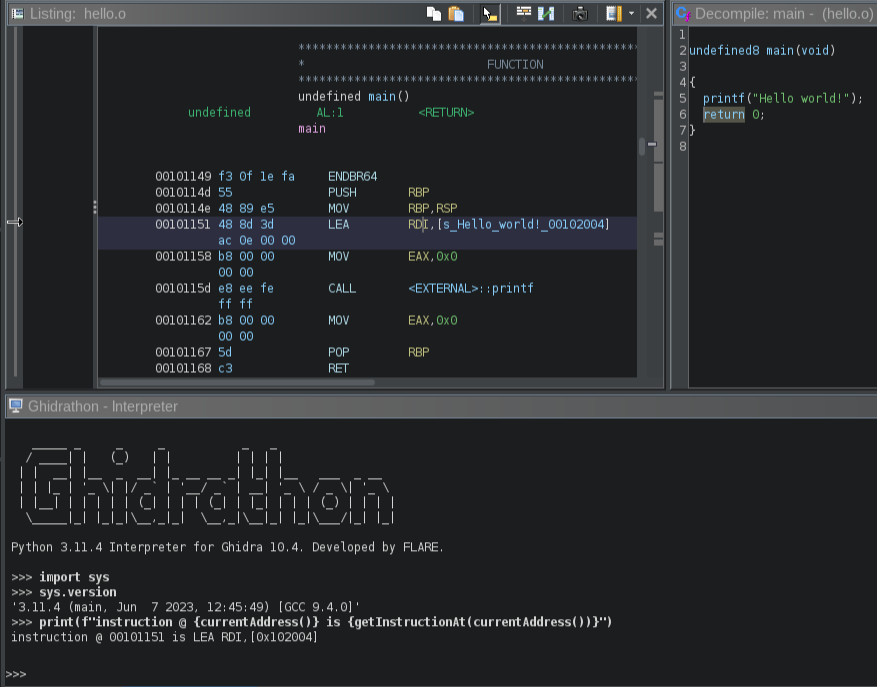 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 idanr1986/cuckoo-droid
CuckooDroid - Automated Android Malware Analysis with Cuckoo Sandbox.
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 sastraadiwiguna-purpleeliteteaming/dissecting-cve-2026-0628-chromium-extension-privilege-escalation
Technical dissection of CVE-2026-0628, a Chromium WebView privilege escalation vulnerability, including root cause analysis, PoC exploit, detection…
 mishra0230/cve-2023-38831
CVE-2023-38831 - WinRAR