
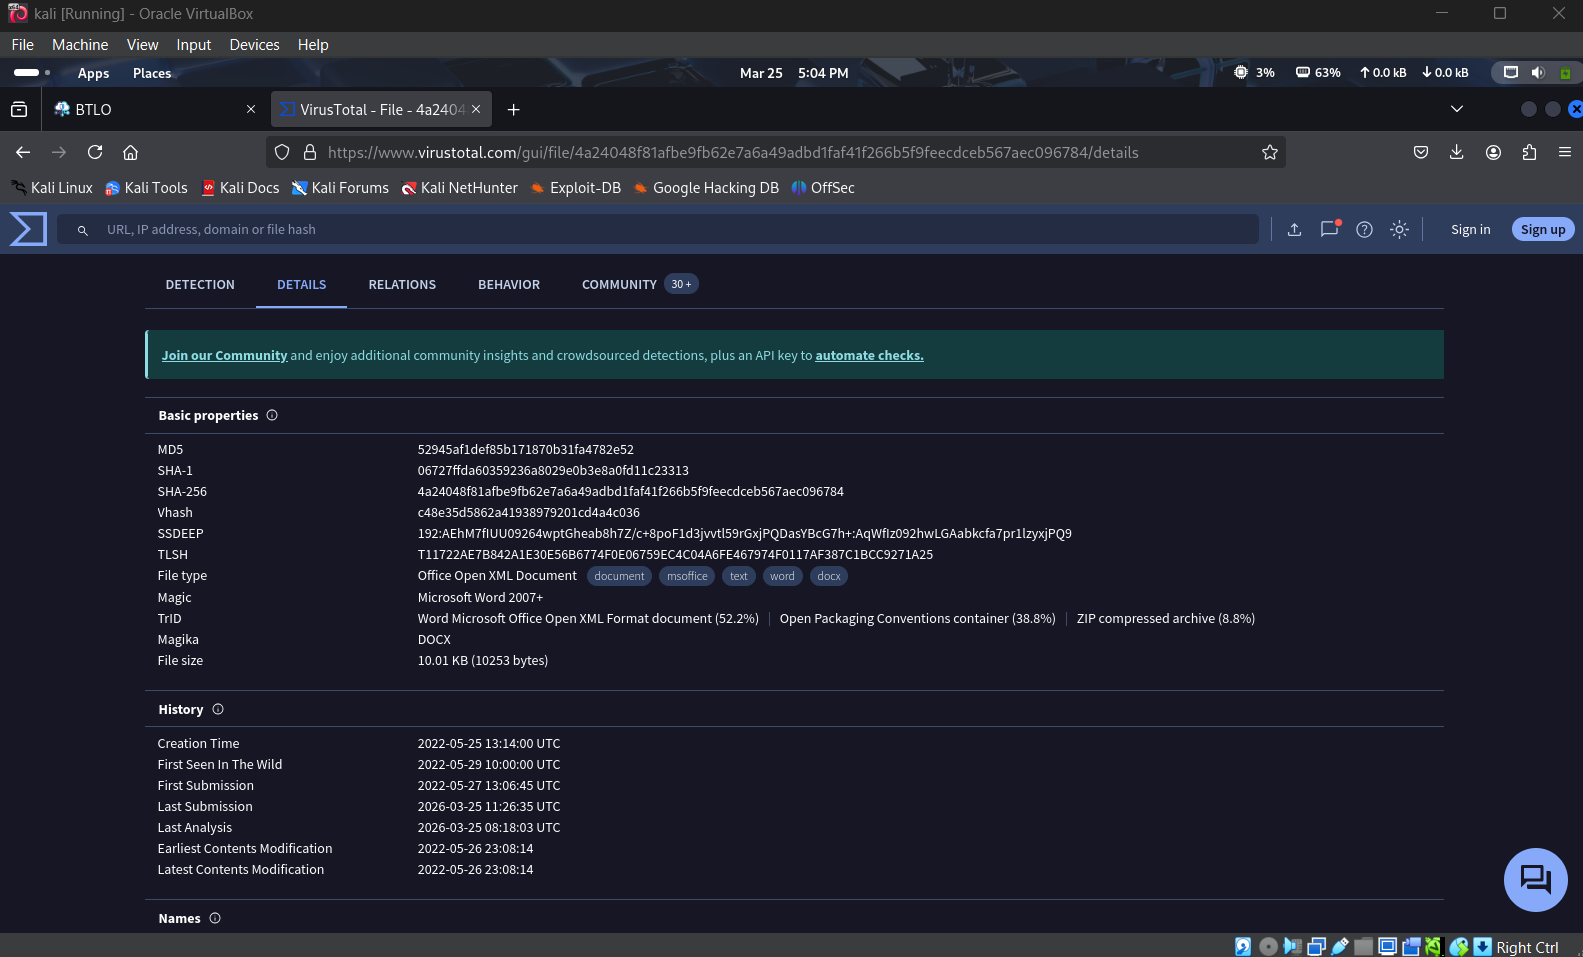
Static-Malware-Analysis-Follina-CVE-2022-30190
 imvihanga03/static-malware-analysis-follina-cve-2022-30190
Static Malware Analysis of Follina (CVE-2022-30190) from Blue Team Labs Online
digital-forensicseducationexploitation+4
imvihanga03/static-malware-analysis-follina-cve-2022-30190Static Malware Analysis of Follina (CVE-2022-30190) from Blue Team Labs Online
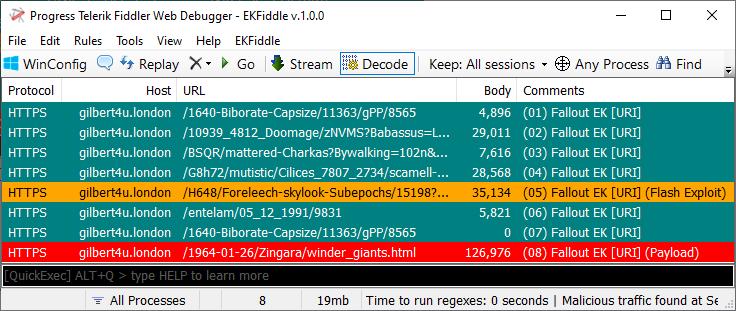 jeromesegura/ekfiddle
Your Swiss Army knife to analyze malicious web traffic based on the popular Fiddler web debugger.
 tadash10/detect-cve-2024-0762
Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature
 vulnex/bytesrevealer
Online Reverse Enginerring viewer
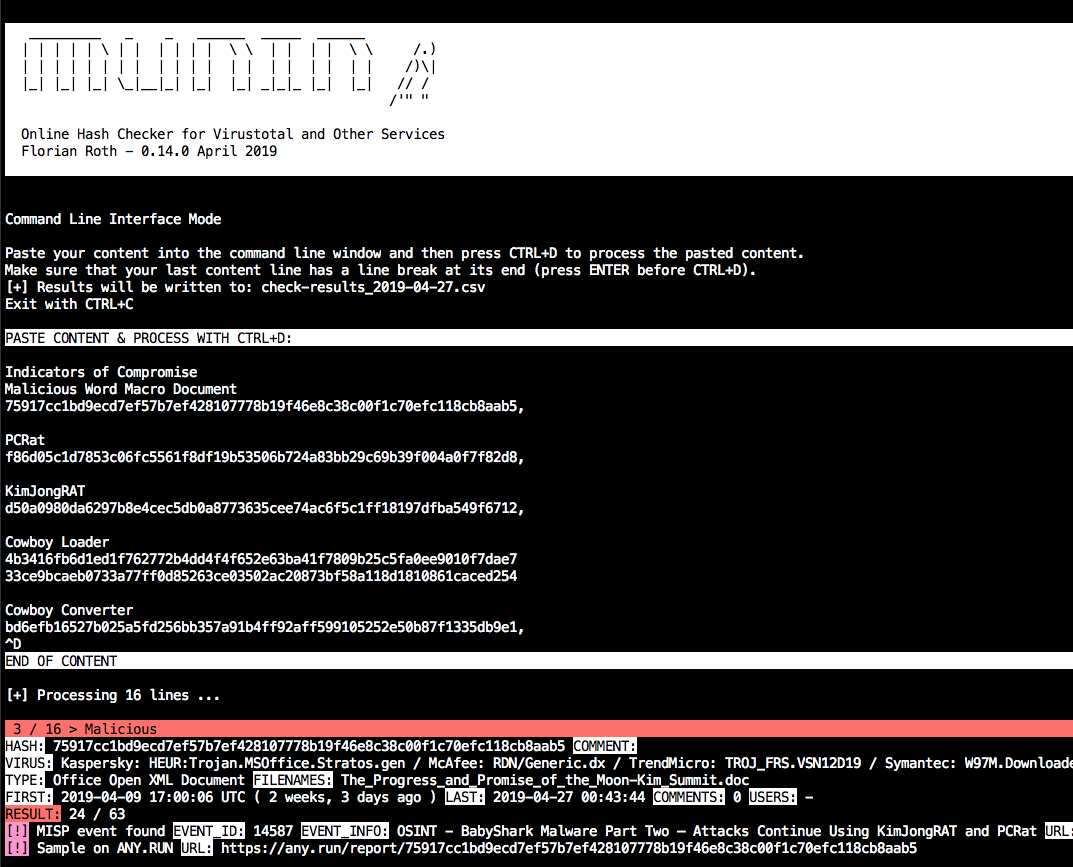 neo23x0/munin
Online hash checker for Virustotal and other services
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.