

scavenger_scanner
 paspke/scavenger_scanner
Detect CVE-2025-54313 eslint-config-prettier supply chain attack IOCs on Windows
incident-responseioc-managementmalware-analysis+3
paspke/scavenger_scannerDetect CVE-2025-54313 eslint-config-prettier supply chain attack IOCs on Windows
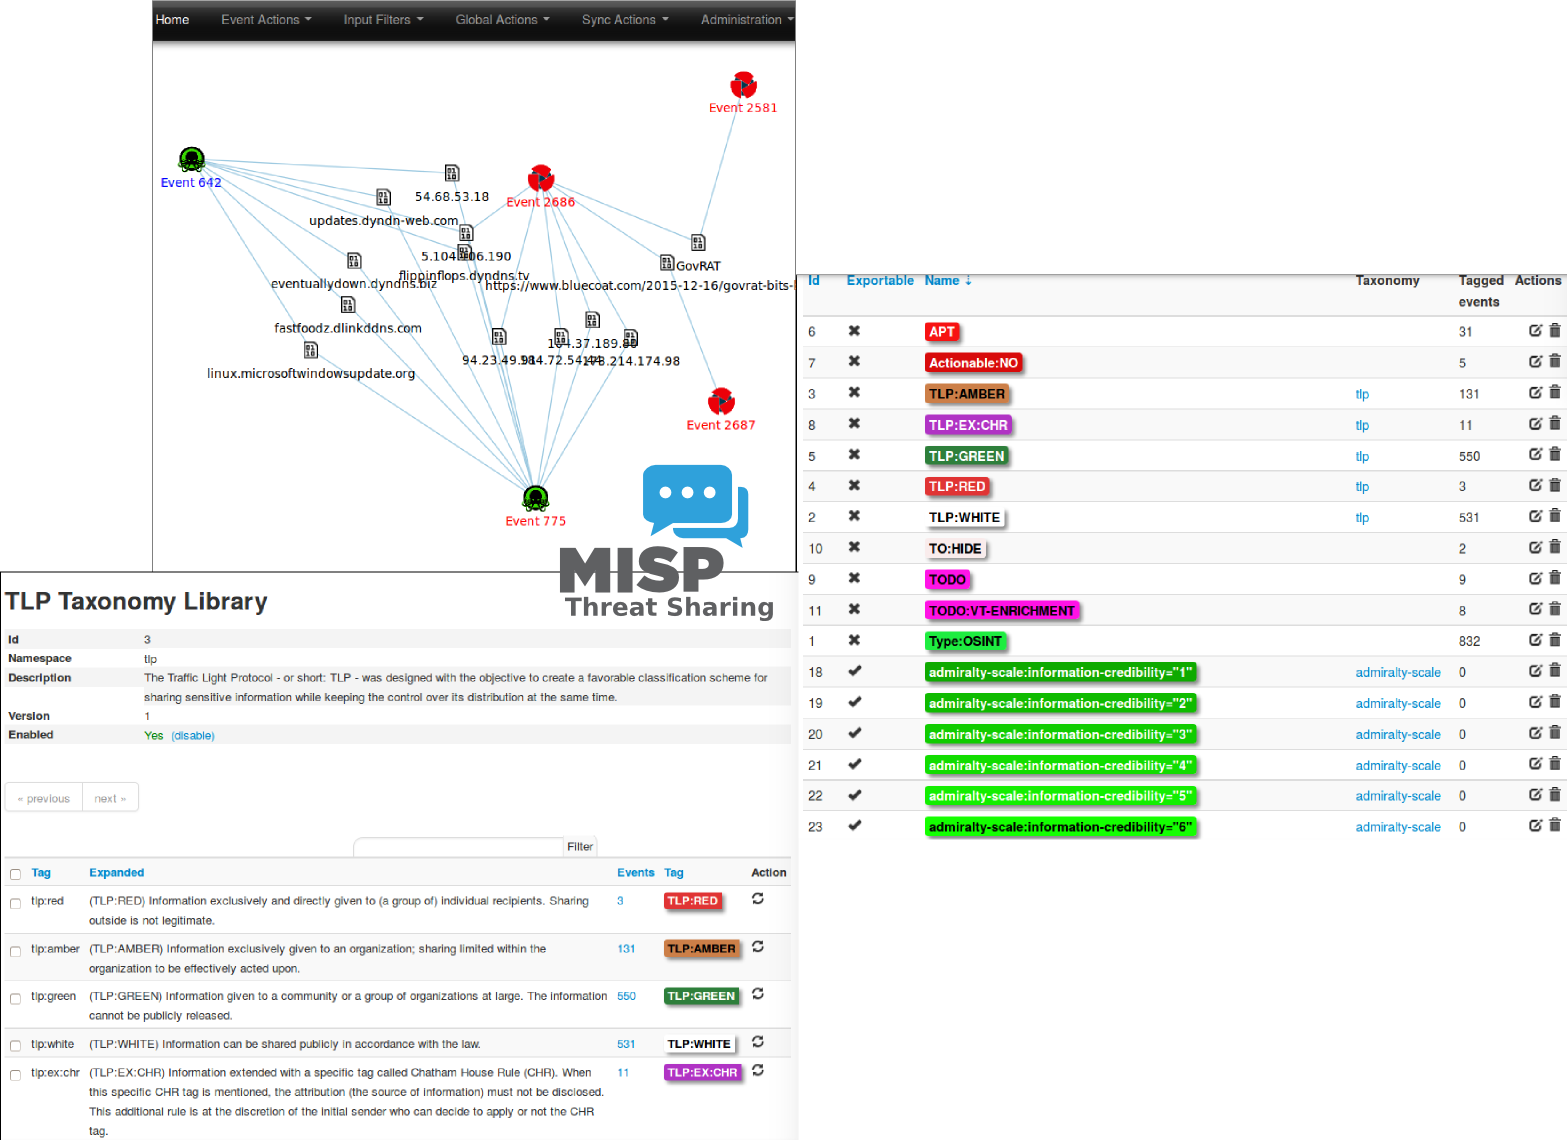 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 aquibpro/forensix-studio
Forensic intelligence platform that analyzes files, correlates threat indicators, maps behavior to MITRE ATT&CK, and generates actionable security…
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 klezvirus/cve-2021-40444
CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
 prodaft/malware-ioc
This repository contains indicators of compromise (IOCs) of our various investigations.
 graphworlok/cve-2021-35394-ecosystem
Tracking the family of unrelated IoT botnets sharing CVE-2021-35394 as a delivery vector — findings, relationships, methodology.
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 cronup/malware-iocs
Collects and organizes malware indicators of compromise (IOCs) for rapid threat detection, incident response, and actionable intelligence sharing.
 t3ft3lb/2026-100daysofyara
Writing and sharing one YARA rule daily for 100 days
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
 sophoslabs/iocs
Sophos-originated indicators-of-compromise from published reports
 emalderson/thephish
ThePhish: an automated phishing email analysis tool
 curated-intel/ukraine-cyber-operations
Curated Intelligence is working with analysts from around the world to provide useful information to organisations in Ukraine looking for additional…
 akamai/akamai-security-research
This repository includes code and IoCs that are the product of research done in Akamai's various security research teams.