
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1563 results
tyton preview
Archived

tyton

GitHubnbulischeck/tyton

Kernel-Mode Rootkit Hunter

defensive-toolsincident-responseintrusion-detection+1
371
4 years ago
Rootsmart-v2.0 preview
Archived

Rootsmart-v2.0

GitHubnicchongwb/rootsmart-v2.0

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
android-securitycommand-and-controldata-exfiltration+8
14 years ago
kavanoz preview
Archived

kavanoz

GitHubeybisi/kavanoz

Statically unpacking common android banker malware.
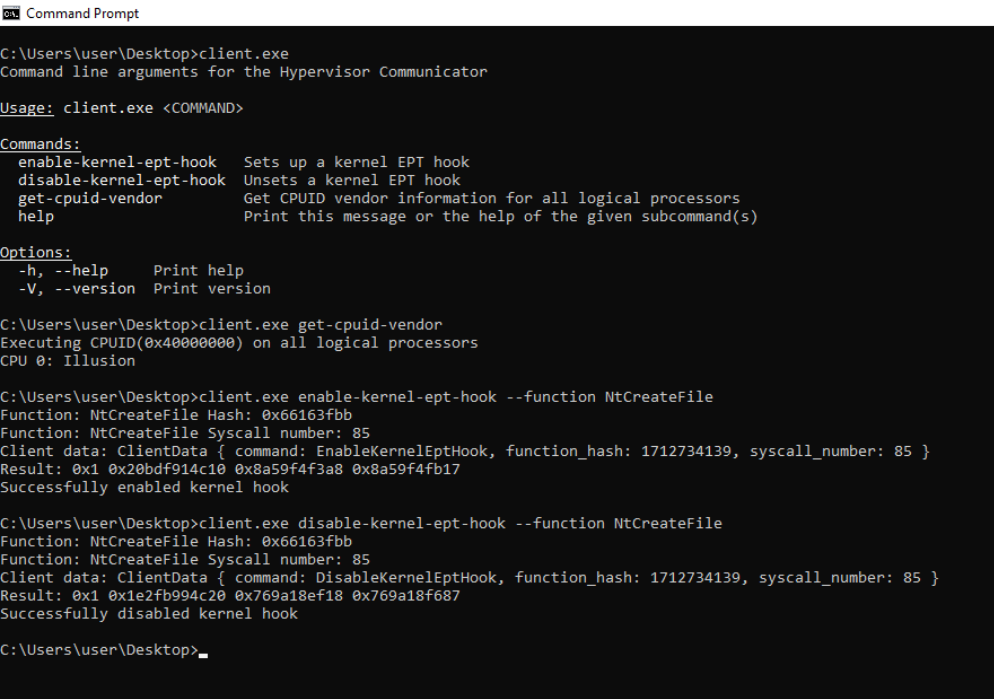
android-securityencryption-decryption-toolsmalware-analysis+3
1591 year ago
illusion-rs preview
Archived

illusion-rs

GitHubmemn0ps/illusion-rs

Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
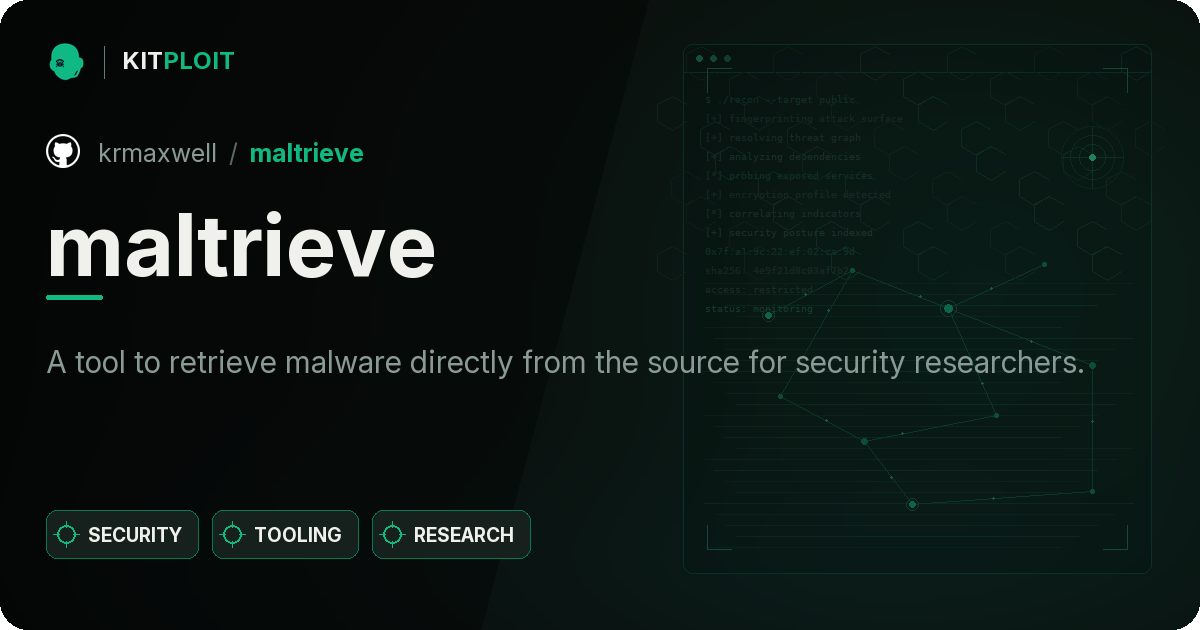
binary-analysisdefensive-toolshardware-security+7
4145 months ago
maltrieve preview
Archived

maltrieve

GitHubkrmaxwell/maltrieve

A tool to retrieve malware directly from the source for security researchers.
crawlerinformation-gatheringmalware-analysis+2
5649 years ago
M-Botnet preview
Archived

M-Botnet

GitHubm507/m-botnet

A C2 project that controls a self-propagating MS17-010 worm.
command-and-controleducationexploitation+4
785 years ago
halogen preview
Archived

halogen

GitHubtarget/halogen

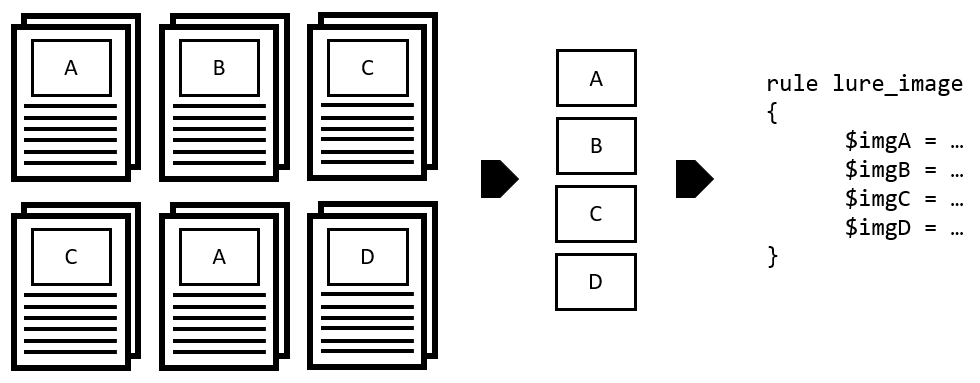
Automatically create YARA rules from malicious documents.

forensicsincident-responsemalware-analysis+2
2114 years ago
katana preview
Archived

katana

GitHubsaintly2k/katana

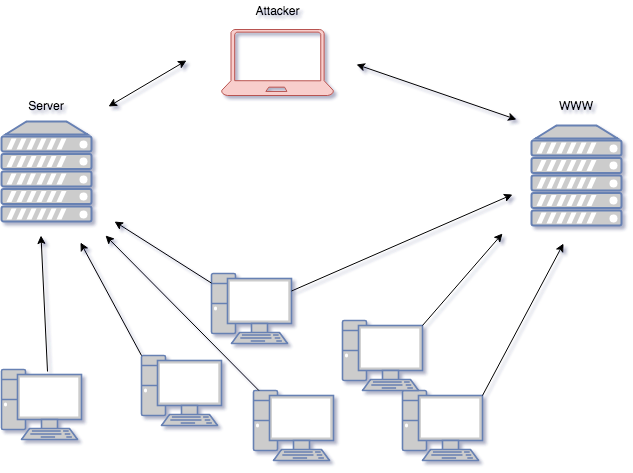
Katana Botnet used for DDoS attacks based on the Mirai Botnet. TEACHING PURPOSES ONLY! I CANNOT BE HELD RESPONSIBLE FOR ANYTHING YOU DO WITH IT! I…
command-and-controleducationexploitation+3
564 years ago
Debinject preview
Archived

Debinject

GitHubundeadsec/debinject

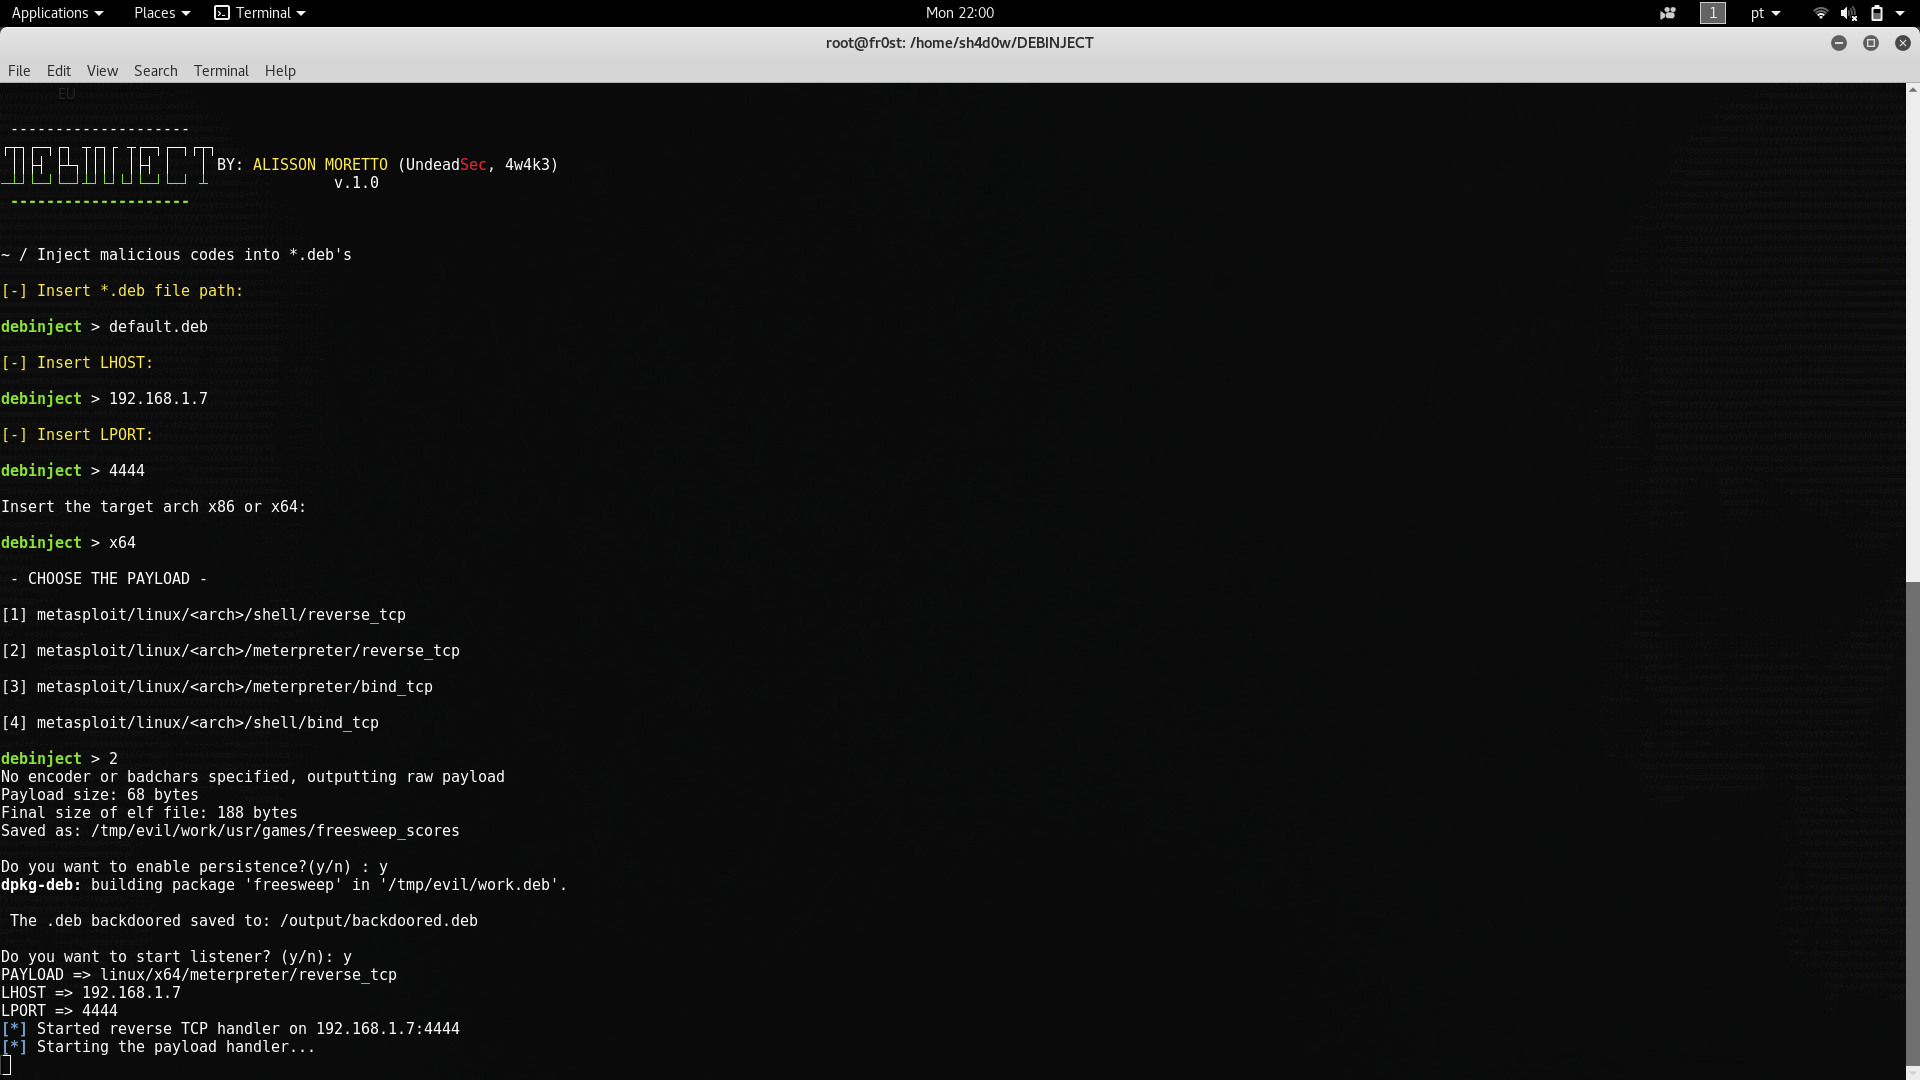
Inject malicious code into *.debs
educationexploitationmalware-analysis+3
2934 years ago
DAMM preview
Archived

DAMM

GitHub504ensicslabs/damm

Differential Analysis of Malware in Memory
digital-forensicsforensicsincident-response+3
2159 years ago
CuiRi preview

CuiRi

GitHubnydubh3/cuiri

一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
command-and-controlexploitationids-ips-evasion+7
9225 years ago
HackTheWorld preview

HackTheWorld

GitHubstormshadow07/hacktheworld

An Python Script For Generating Payloads that Bypasses All Antivirus so far .
exploitationids-ips-evasionmalware-analysis+5
1.0k2 years ago
packer-KitsuPE preview

packer-KitsuPE

GitHubgmh5225/packer-kitsupe

Some PE hackery I'm working on (shellcode loader, packer, all WIP)
binary-analysisbinary-exploitationexploitation+5
3 years ago
eBook-BypassingAVsByCSharp preview

eBook-BypassingAVsByCSharp

GitHubdamonmohammadbagher/ebook-bypassingavsbycsharp

eBook "Bypassing AVS by C#.NET Programming" (Free Chapters only)
command-and-controlcurated-resourcesdata-exfiltration+8
4623 years ago
WindowsRegistryRootkit preview
Archived

WindowsRegistryRootkit

GitHubcr4sh/windowsregistryrootkit

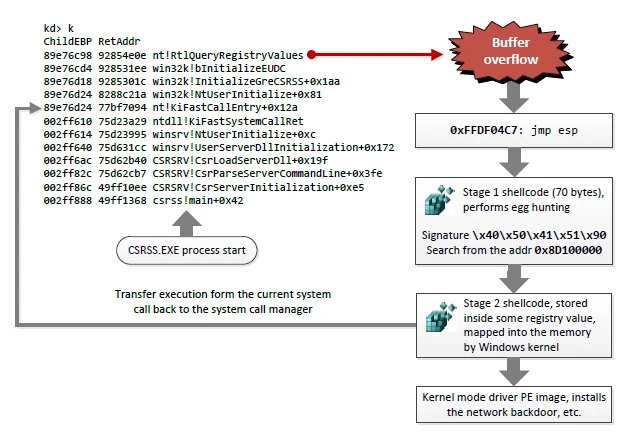
Kernel rootkit, that lives inside the Windows registry values data

command-and-controlexploitationmalware-analysis+2
5049 years ago
Previous1…8687Next