Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
135 results
fuckshell preview

fuckshell

GitHubjofpin/fuckshell

Simple Webshell Scanner

information-gatheringmalware-analysispenetration-testing+2
5611 years ago
Daily-dose-of-malware preview

Daily-dose-of-malware

GitHubwoj-ciech/daily-dose-of-malware

Script lets you gather malicious software and c&c servers from open source platforms like Malshare, Malcode, Google, Cymon - vxvault, cybercrime…

command-and-controlinformation-gatheringmalware-analysis+2
408 years ago
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS cloud scanner and response parser for Microsoft Defender research.
api-security-testingdynamic-analysis-sandboxingfuzzing+6
957 months ago
svg_phishing_tools preview

svg_phishing_tools

GitHubhackinglz/svg_phishing_tools

SVG Analysis and generation tools for commonly seen SVG attachment phishing

dynamic-analysis-sandboxinginformation-gatheringmalware-analysis+5
561 year ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.

binary-analysisdata-recoverydigital-forensics+8
431 month ago
memgrep preview

memgrep

GitHubnccgroup/memgrep

Memory searching utilities

binary-analysisdigital-forensicsforensics+3
4412 years ago
Kage-DFIR-toolkit preview

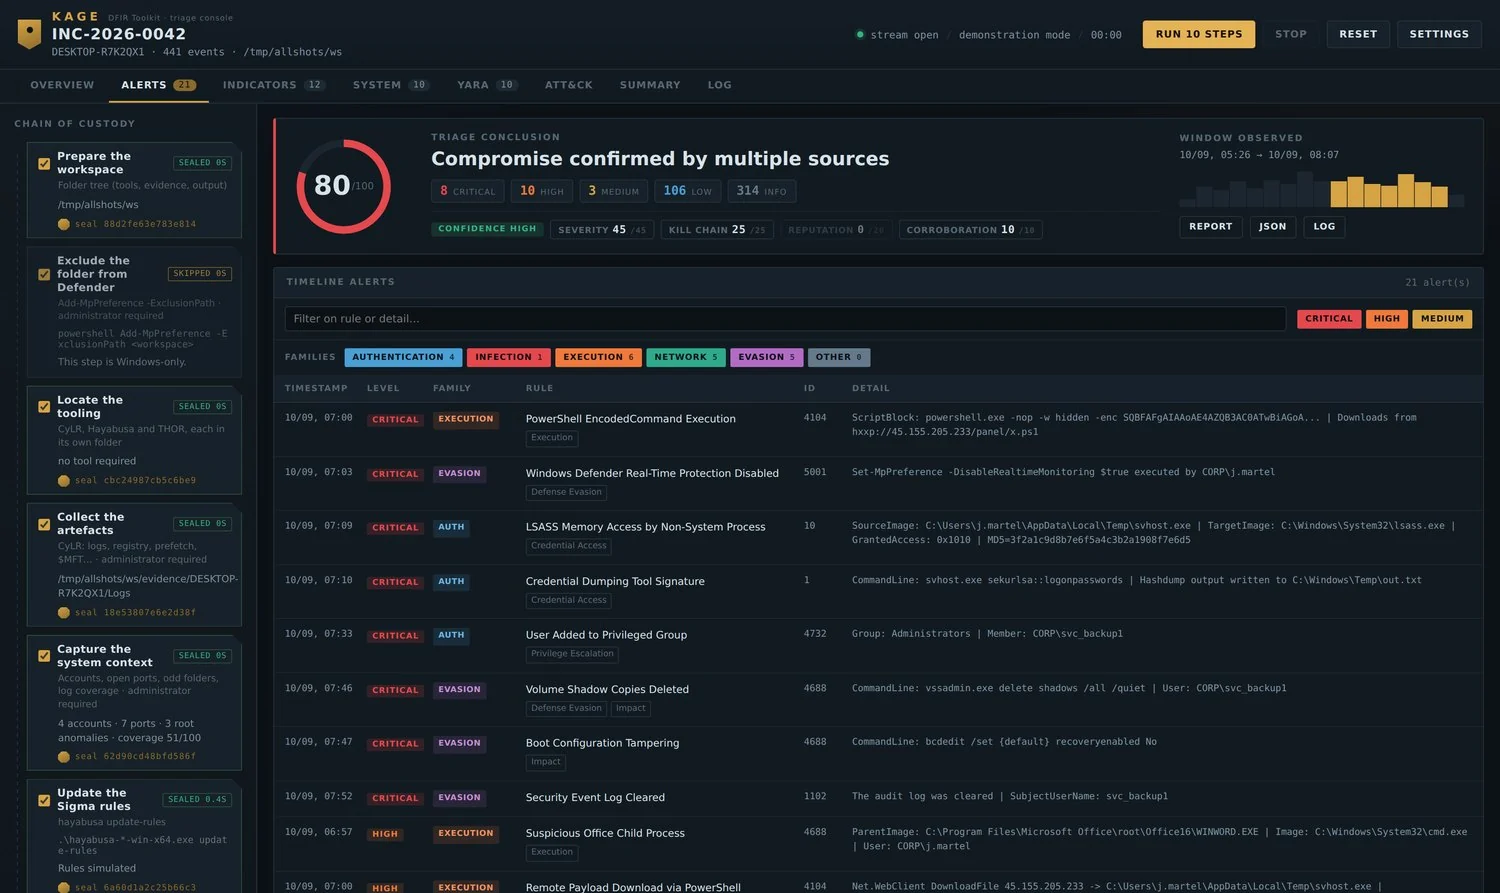
Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsdigital-forensicsforensics+8
2010 days ago
strafer preview

strafer

GitHubadityaks/strafer

Strafer: A tool to detect potential infections in Elasticsearch instances
cloud-securitydatabase-securityinformation-gathering+4
275 years ago
python-inquestlabs preview

python-inquestlabs

GitHubinquest/python-inquestlabs

A Pythonic interface and command line tool for interacting with the InQuest Labs API.

email-securityhash-analysisinformation-gathering+4
3710 months ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
167 days ago
Ustealer preview

Ustealer

GitHubatmoner/ustealer

Ubuntu stealer, steal ubuntu information in local pc
data-exfiltrationinformation-gatheringmalware-analysis+1
216 years ago
ALPC-Enumerator preview

ALPC-Enumerator

GitHubtalha-nazeef-ahmed/alpc-enumerator

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

digital-forensicsinformation-gatheringmalware-analysis+4
291 month ago
amtracker preview

amtracker

GitHubjacobsoo/amtracker

Android Malware Tracker

android-securitycommand-and-controlinformation-gathering+3
292 years ago
ripVT preview

ripVT

GitHubmatonis/ripvt

Virus Total API Maltego Transform Set For Canari
information-gatheringmalware-analysisosint+2
167 years ago
CVE-2023-20052 preview

CVE-2023-20052

GitHubnokn0wthing/cve-2023-20052

CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
exploitationfuzzinginformation-gathering+2
293 years ago
FollinaExtractor preview

FollinaExtractor

GitHubmalwaretech/follinaextractor

Extract payload URLs from Follina (CVE-2022-30190) docx and rtf files
exploitationinformation-gatheringmalware-analysis+2
314 years ago
Veto preview

Veto

GitHubprofessorquantumuniverse/veto

Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
android-securitydynamic-analysis-sandboxingforensics+8
194 days ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

binary-analysiscommand-and-controleducation+6
52 months ago
Previous1…5678Next