
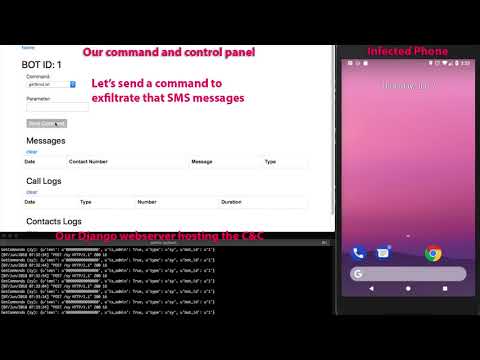
silverboxcc
 bizdak/silverboxcc
Reverse engineered android malware, and this is a C&C server for it
android-securitycommand-and-controlmalware-analysis+3
28 years ago
bizdak/silverboxccReverse engineered android malware, and this is a C&C server for it
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
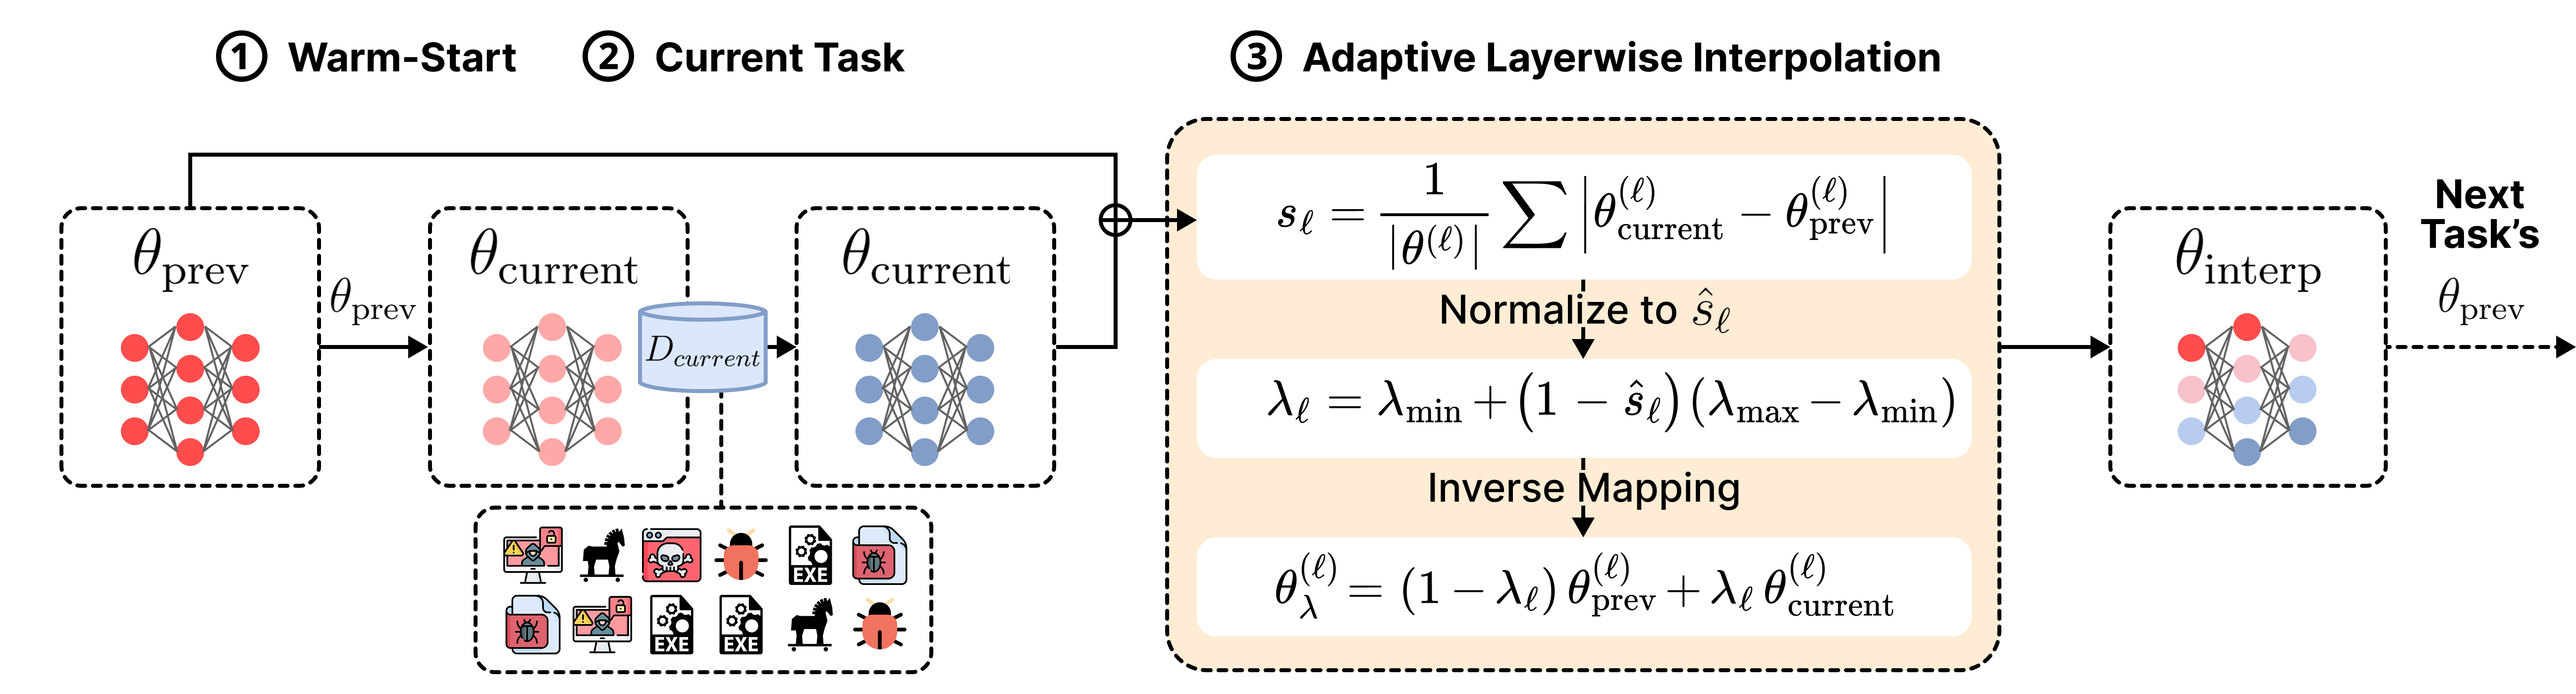 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 mohammadnassiri/yaasa
Yet Another APK Static Analyzer
 saykino/cve-2025-66837
Technical documentation and proof-of-concept for CVE-2025-66837, a remote authenticated file upload vulnerability in ARIS allowing arbitrary code…
 xuedugu/cve-2024-7965-poc
CVE-2024-7965是Google Chrome浏览器中V8 JavaScript引擎的一个高危漏洞。该漏洞源于V8引擎在处理特定JavaScript代码时实现不当,导致堆内存损坏。攻击者可通过诱导用户访问包含特制JavaScript的恶意网页,利用此漏洞在Chrome渲染器中执行任意代码。
 joakimbulow/cve-2026-23907
Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…
 fevar54/cve-2026-3502---trueconf-client-update-hijacking-poc
PoC de CVE-2026-3502: hijacking de actualizacion en TrueConf Client para RCE (Operacion TrueChaos).
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 hexnone/cve-2019-6440
Proof-of-concept exploit for CVE-2019-6440 achieving SYSTEM privilege escalation on Zemana antimalware via man-in-the-middle update interception and…
 open-flaw/cve-2026-3462
Acrobat Reader | Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') (CWE-1321)
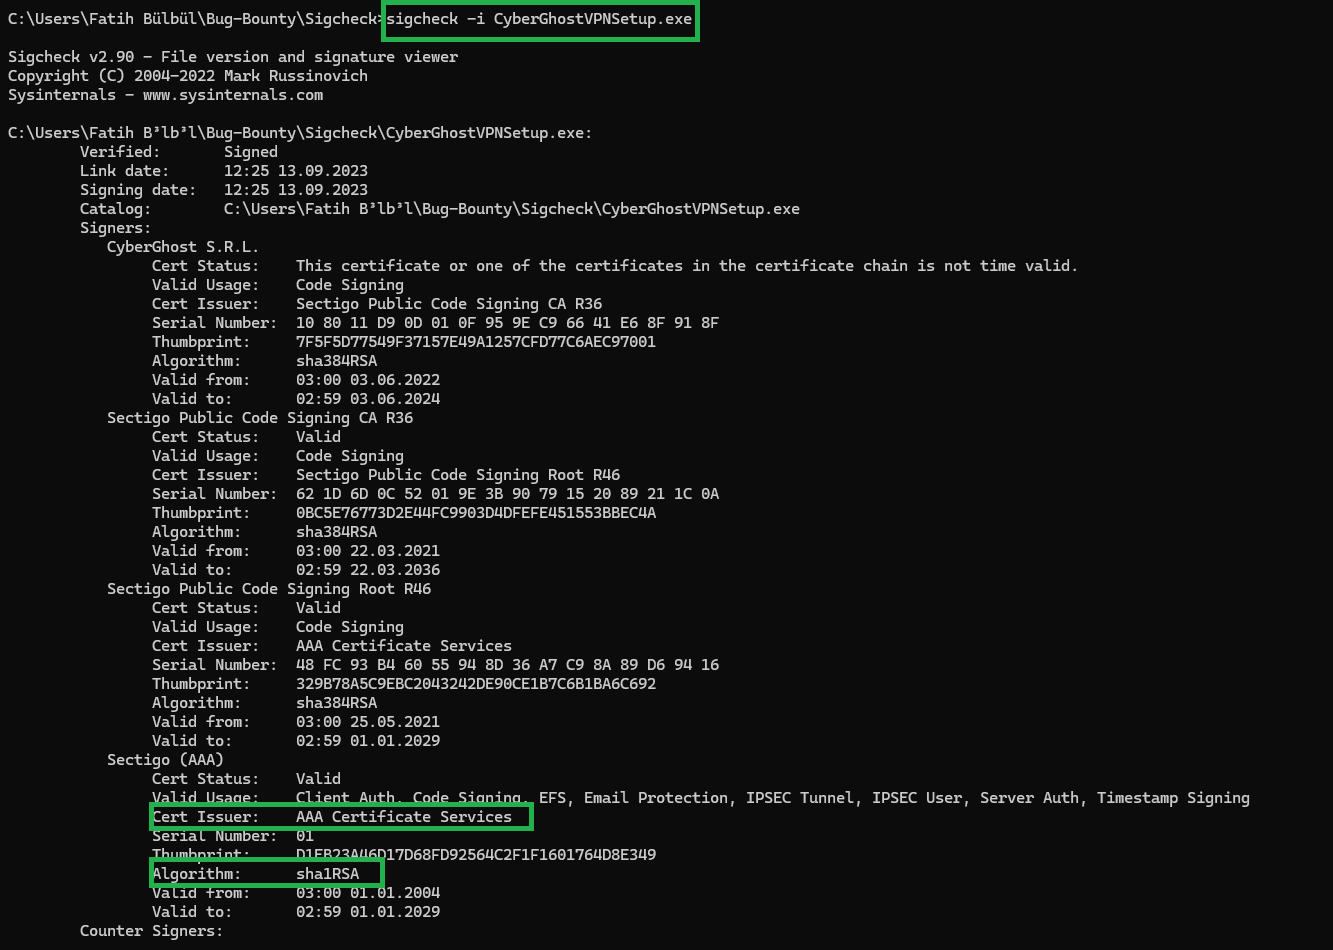 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 varunsaru/snp
CVE-2017-8759 || report related with execute code vulnerability
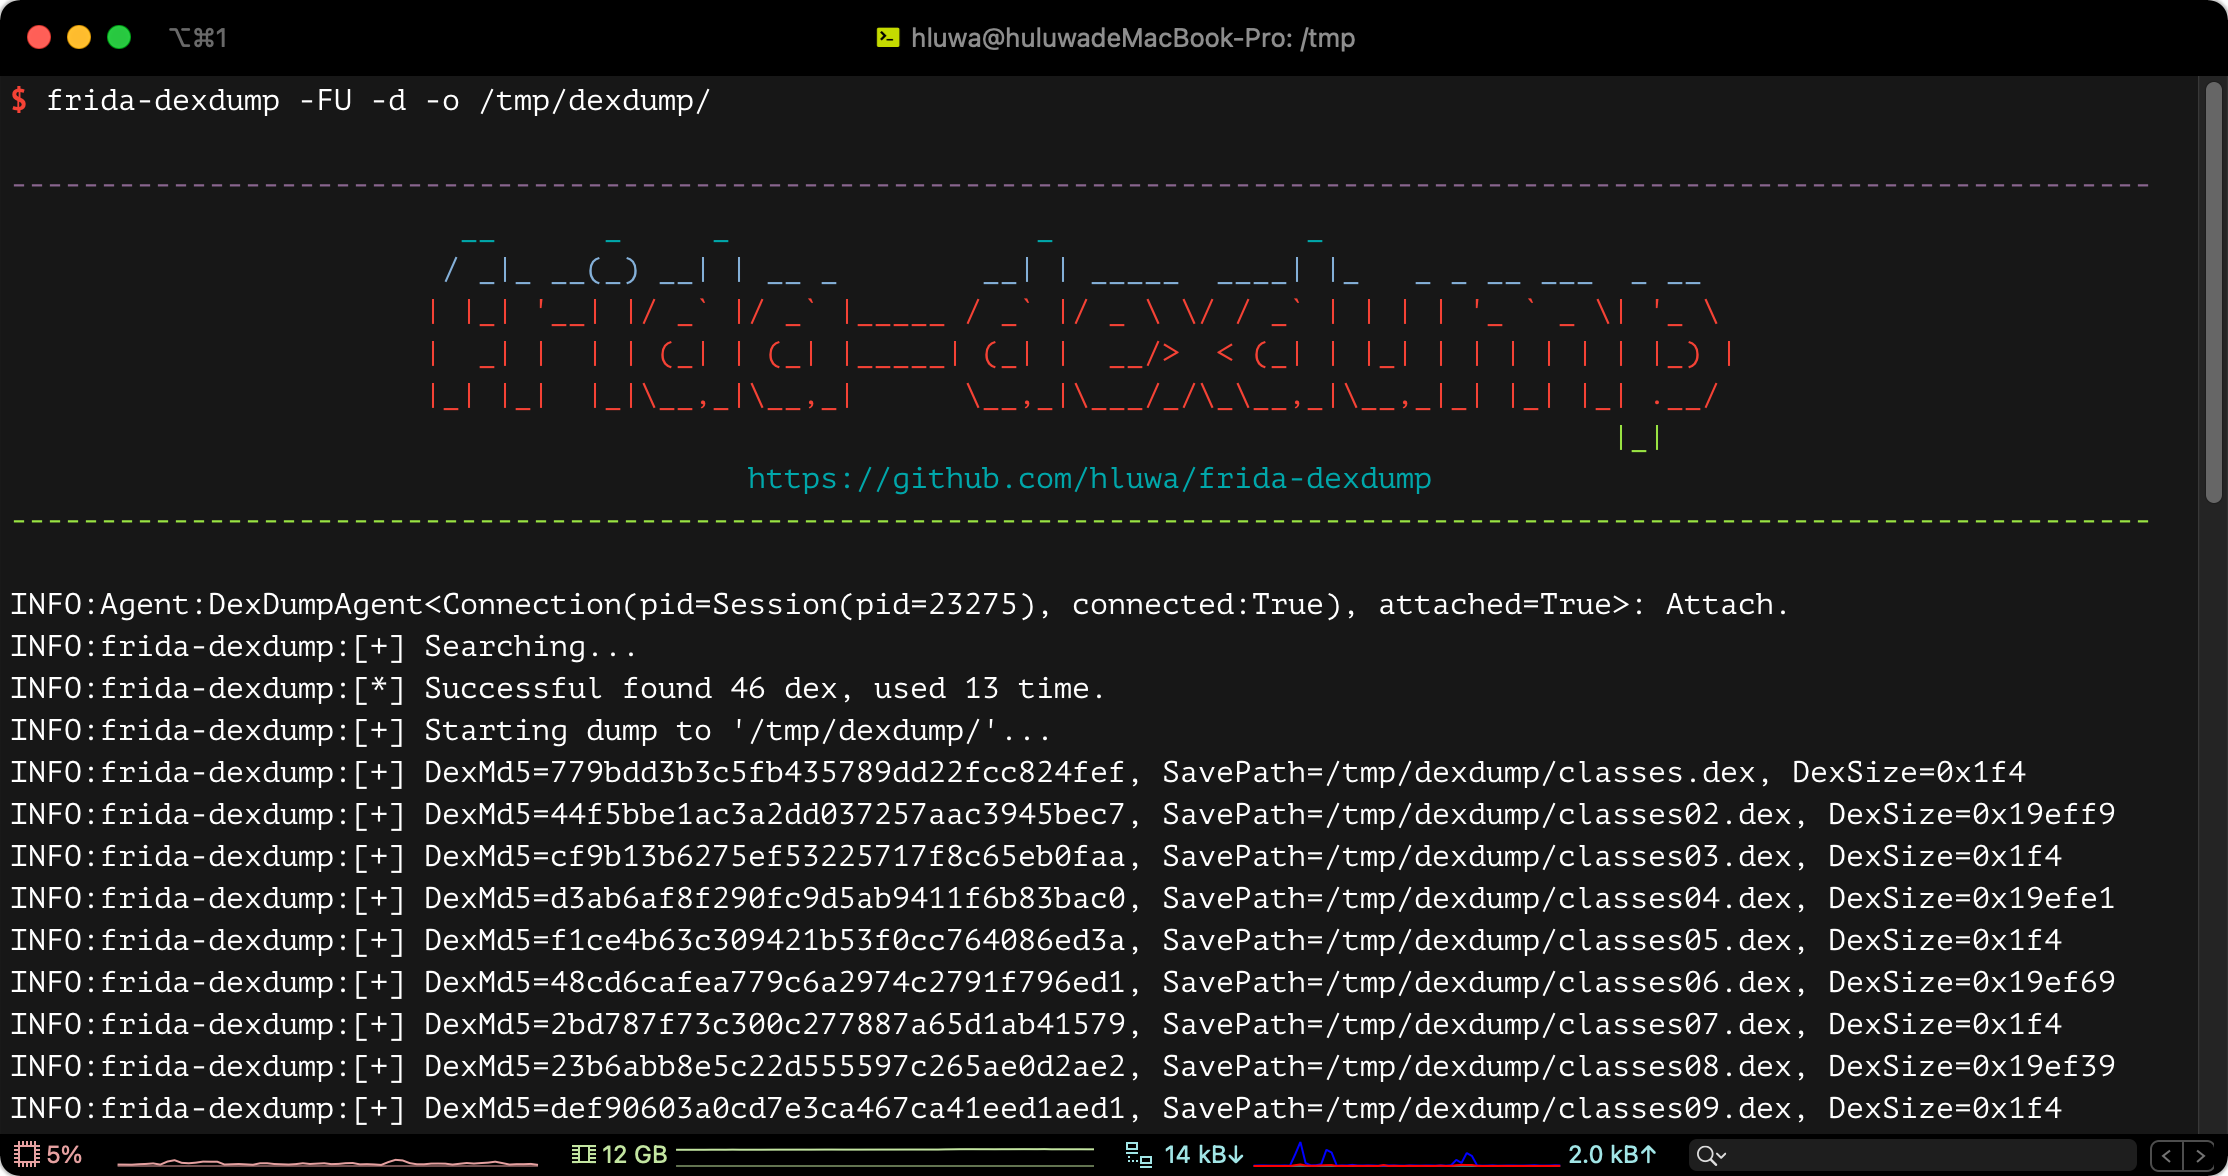 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
 nighthawkk/jnisleuth-mcp
Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…
 nicchongwb/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration