Sandroid_Dexray-Intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…

This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.

Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing

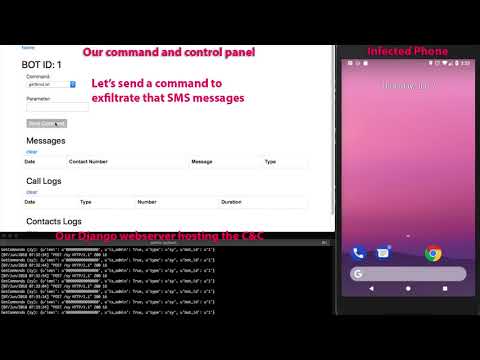
Reverse engineered android malware, and this is a C&C server for it

Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…

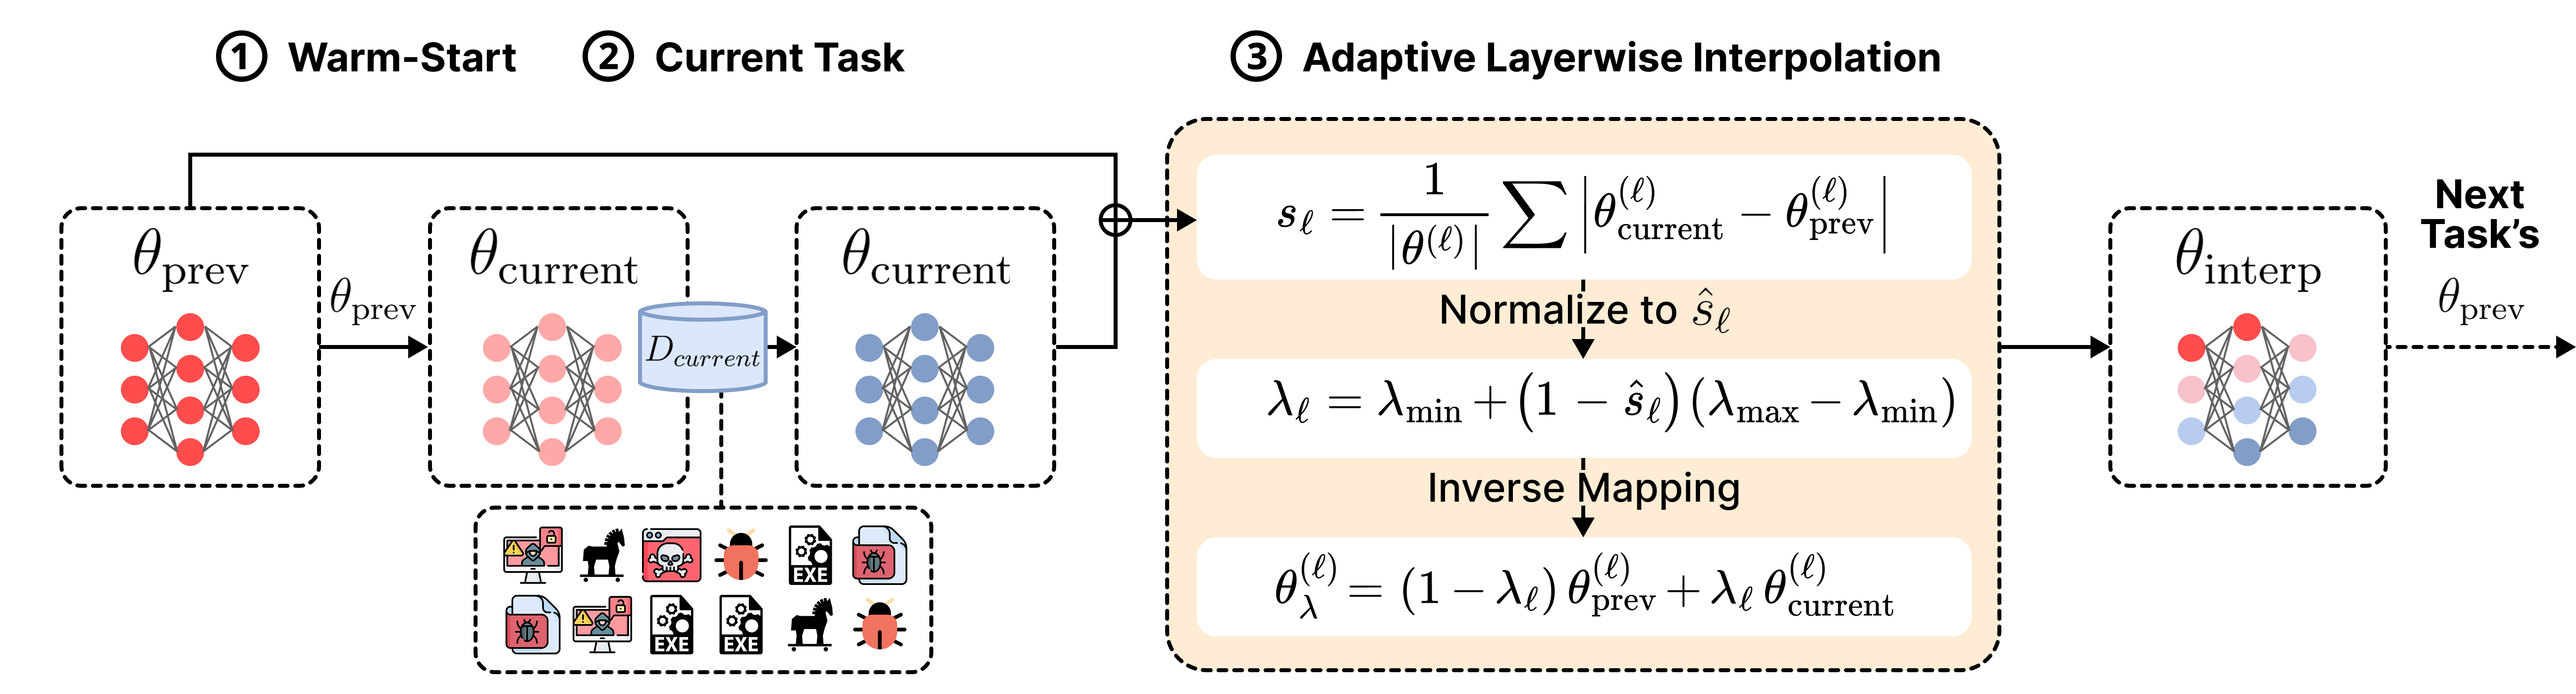
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…

Yet Another APK Static Analyzer

CVE-2024-7965是Google Chrome浏览器中V8 JavaScript引擎的一个高危漏洞。该漏洞源于V8引擎在处理特定JavaScript代码时实现不当,导致堆内存损坏。攻击者可通过诱导用户访问包含特制JavaScript的恶意网页,利用此漏洞在Chrome渲染器中执行任意代码。

Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.

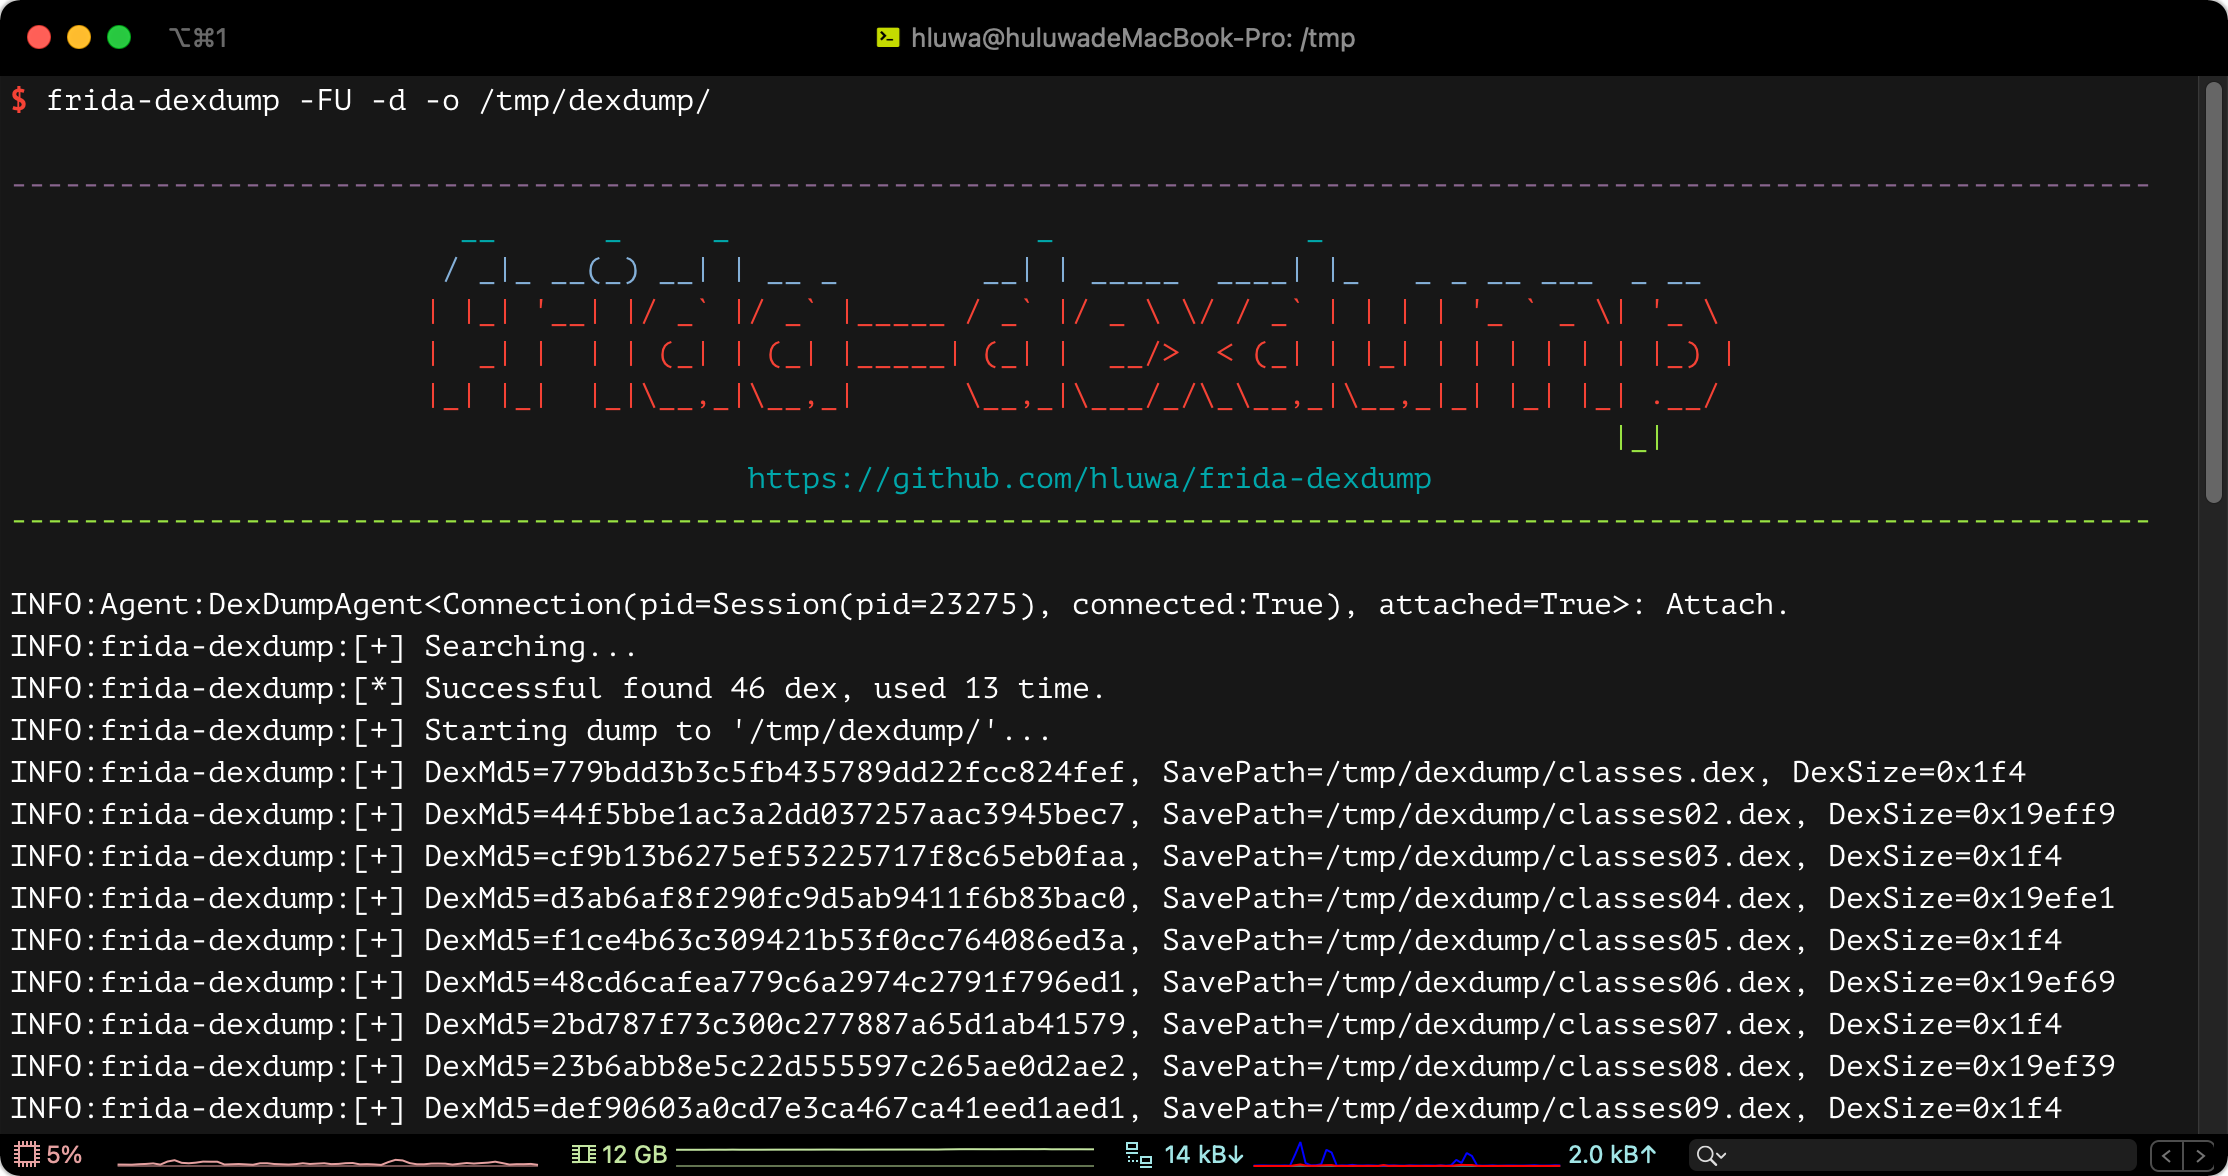
A frida tool to dump dex in memory to support security engineers analyzing malware.

Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…

Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration

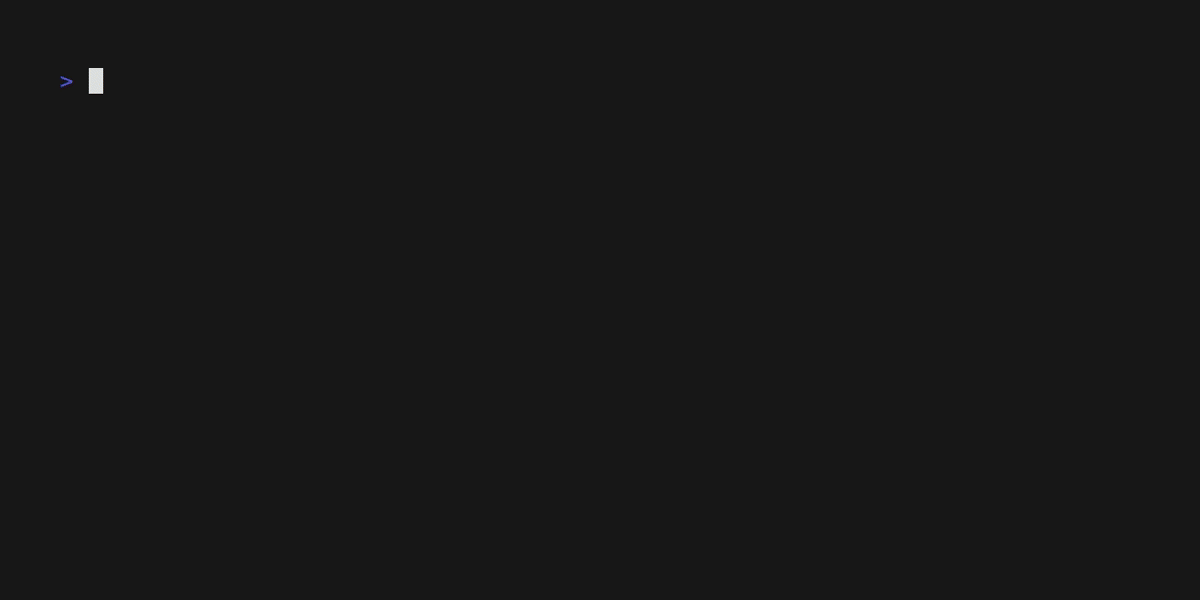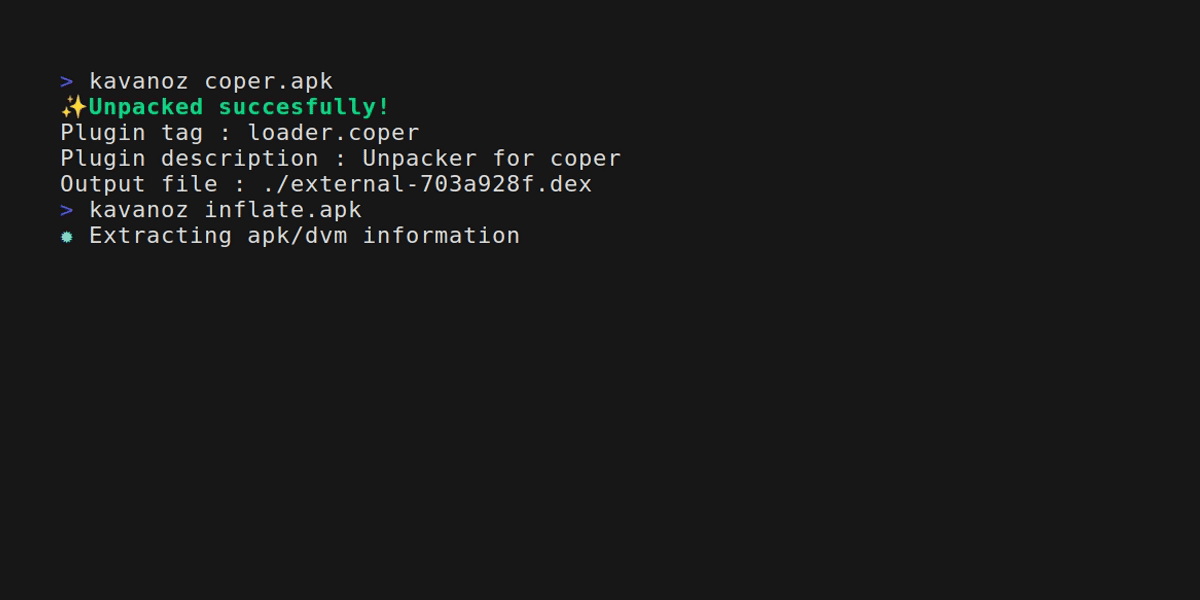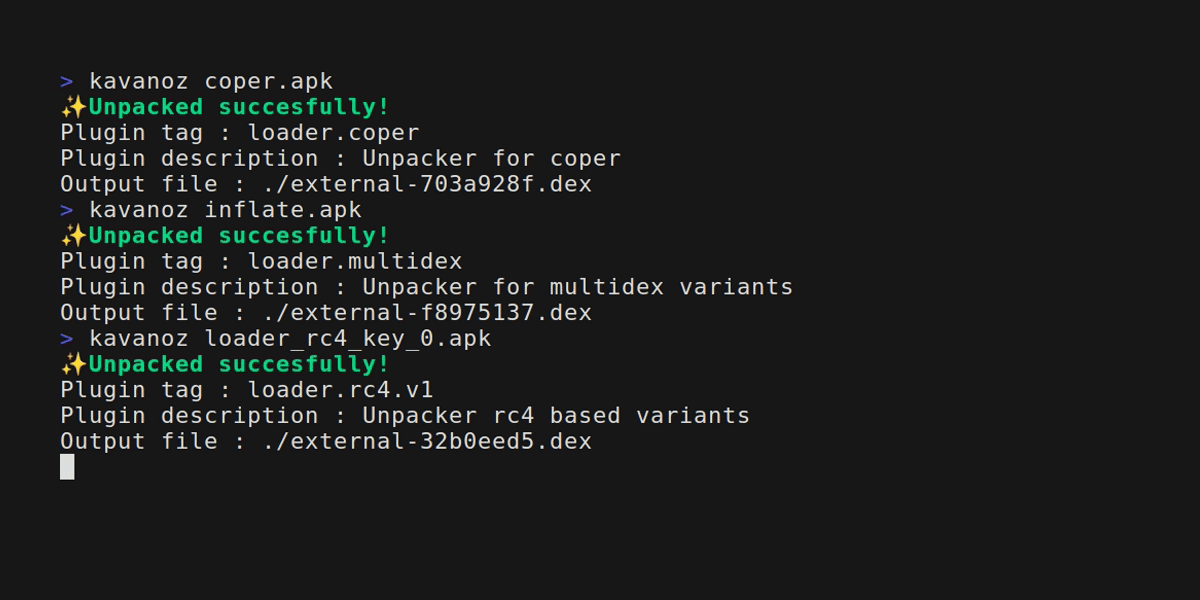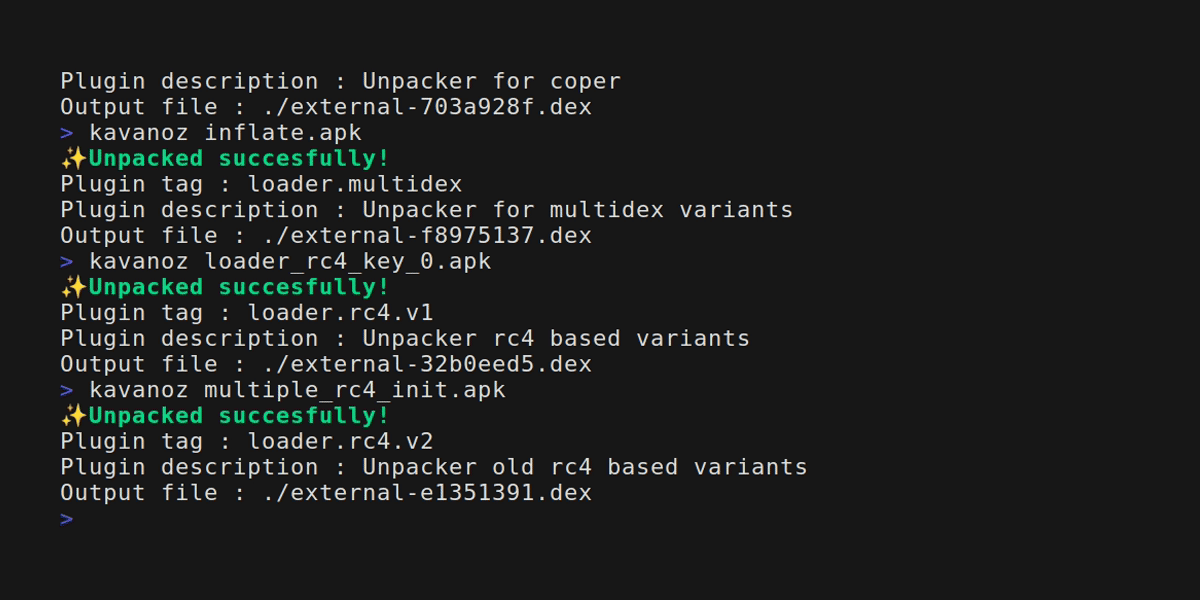
Statically unpacking common android banker malware.

Android reverse engineering for humans and AI agents: typed Java in milliseconds, xrefs, API and secret recon, APK diff, re-signing, a native viewer…