
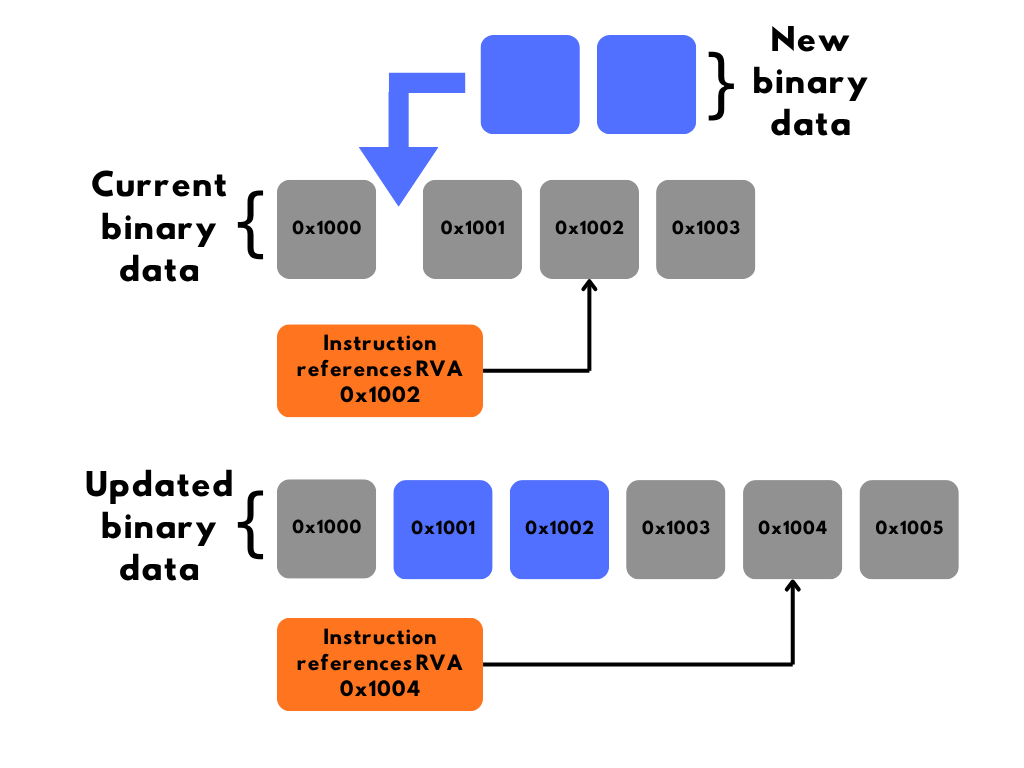
binprotect
 noahware/binprotect
x64 PE bin2bin obfuscator which doesn't add a section to the binary
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
336
noahware/binprotectx64 PE bin2bin obfuscator which doesn't add a section to the binary
 hasherezade/malware_training_vol1
Materials for Windows Malware Analysis training (volume 1)
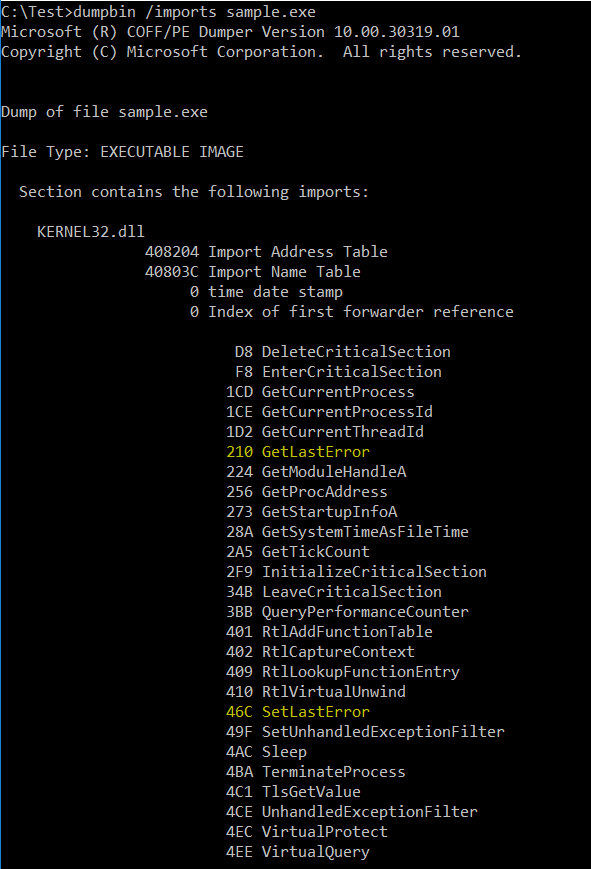 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
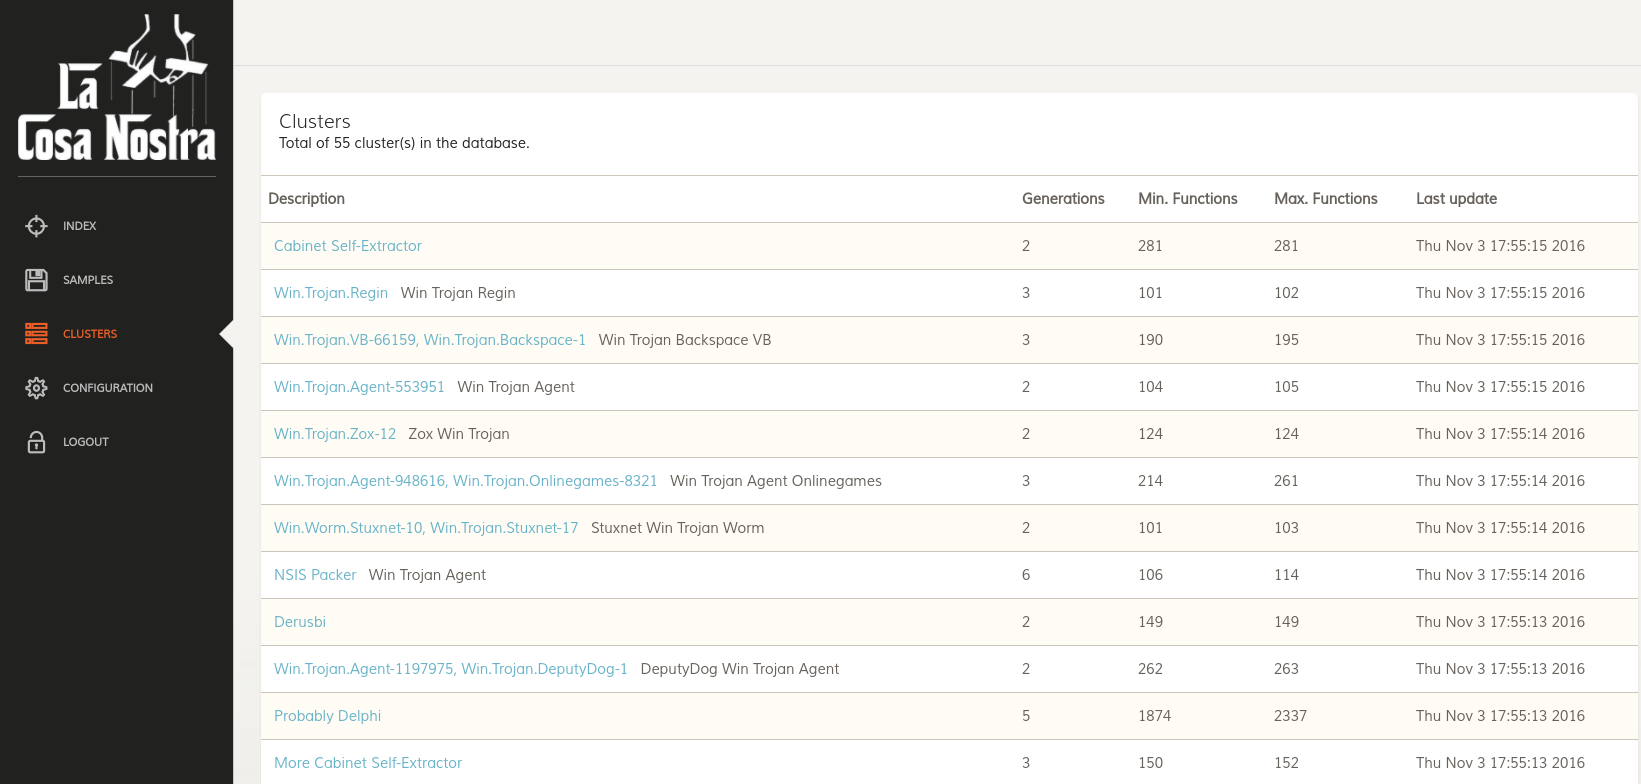 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting
 checkpointsw/showstopper
ShowStopper is a tool for helping malware researchers explore and test anti-debug techniques or verify debugger plugins or other solutions that clash…
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 cdong1012/idapython-malware-scripts
Scripts for automating malware analysis and reverse engineering workflows in IDA Pro, covering binary inspection, static analysis, and code…
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 ajayrandhawa/cryptolocker
CryptoLocker is open source files encrypt-er. Crypto is developed in Visual C++. It has features encrypt all file, lock down the system and send keys…
 perkins-fund/malware-bible
Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
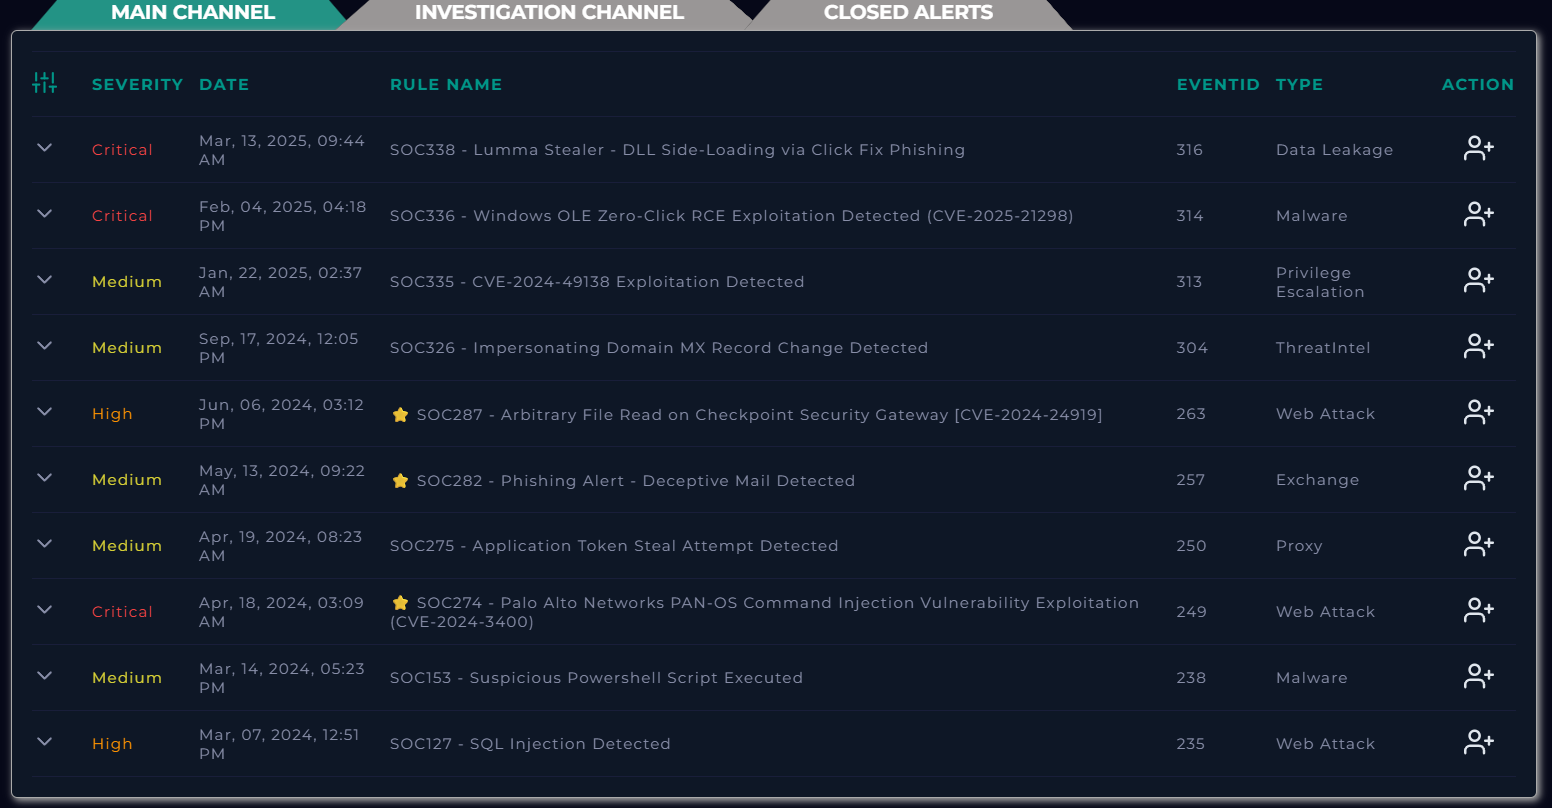 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit