
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
85 results
CVE-2025-61303 preview

CVE-2025-61303

GitHubegkritsis/cve-2025-61303

Critical Vulnerability (9.8) - RecordedFuture Triage dynamic analysis engine can fail to record malicious behavior when samples produce very…

dynamic-analysis-sandboxingeducationexploitation+3
2
10 months ago
Driver-KeAttachProcess-KeDetachProcess-rebuild preview

Driver-KeAttachProcess-KeDetachProcess-rebuild

GitHubgmh5225/driver-keattachprocess-kedetachprocess-rebuild

Rebuild of Windows kernel driver functions KeAttachProcess and KeDetachProcess, used for process attachment and anti-cheat bypass research.
binary-analysismalware-analysisreverse-engineering
24 years ago
VortexCry-Ransomware-Release preview

VortexCry-Ransomware-Release

GitHubvortexcry-organization/vortexcry-ransomware-release

Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…
binary-exploitationencryption-decryption-toolsexploitation+3
17 months ago
cve-2021-40444-analysis preview

cve-2021-40444-analysis

GitHubimmersive-labs-sec/cve-2021-40444-analysis

Deobfuscated exploit code for CVE-2021-40444 with detailed analysis and supporting blog article documenting the attack vector and recovery process.
educationexploitationmalware-analysis+3
5 years ago
criPPLe preview

criPPLe

GitHubgmh5225/cripple

Windows kernel driver that removes Process Protection (PP) and Process Protection Light (PPL).

exploitationmalware-analysisprivilege-escalation+1
2 years ago
NativePe preview

NativePe

GitHubhabanada/nativepe

Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…

binary-analysisbinary-exploitationdynamic-analysis-sandboxing+5
15 days ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k8 days ago
injection-2 preview

injection-2

GitHubgmh5225/injection-2

Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…

curated-resourcesdefensive-toolsexploitation+4
73 years ago
IAT-Hook preview

IAT-Hook

GitHubgmh5225/iat-hook

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
binary-exploitationcode-analysismalware-analysis+4
4 years ago
Diamorphine preview

Diamorphine

GitHubm0nad/diamorphine

LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)

malware-analysispersistence-mechanismsprivilege-escalation+1
2.5k5 months ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k4 days ago
safe-chain preview

safe-chain

GitHubaikidosec/safe-chain

Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.

defensive-toolsdevsecopsmalware-analysis+3
1.8k1 day ago
HexRaysCodeXplorer preview

HexRaysCodeXplorer

GitHubrehints/hexrayscodexplorer

Hex-Rays Decompiler plugin for better code navigation
binary-analysisdebuggersmalware-analysis+2
2.6k10 months ago
RedTeamCCode preview

RedTeamCCode

GitHubmr-un1k0d3r/redteamccode

Red Team C code repo

binary-analysisdefensive-toolsmalware-analysis+1
5731 year ago
ReverseKit preview

ReverseKit

GitHubzer0condition/reversekit

x64 Dynamic Reverse Engineering Toolkit

binary-analysisdynamic-code-analysismalware-analysis+1
7913 years ago
icebox preview

icebox

GitHubthalium/icebox

Virtual Machine Introspection, Tracing & Debugging
debuggersdynamic-analysis-sandboxingforensics+3
6014 years ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

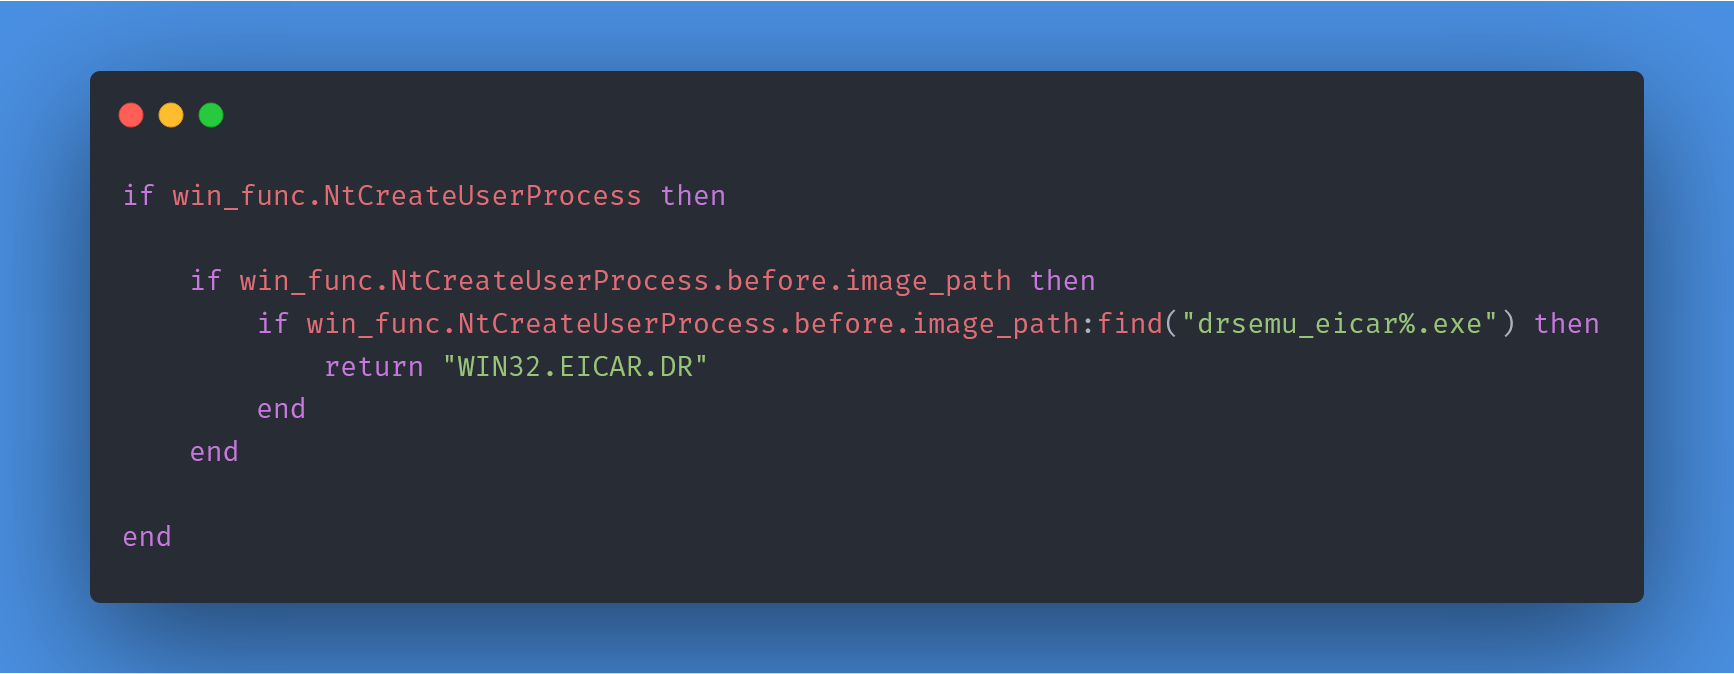
Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
DrSemu preview

DrSemu

GitHubsecrary/drsemu

DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2806 years ago
Previous12345Next