
maldrolyzer
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
android-securitycommand-and-controlinformation-gathering+3
112
maldroid/maldrolyzerSimple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 stefan2200/aparoid
Static and dynamic Android application security analysis
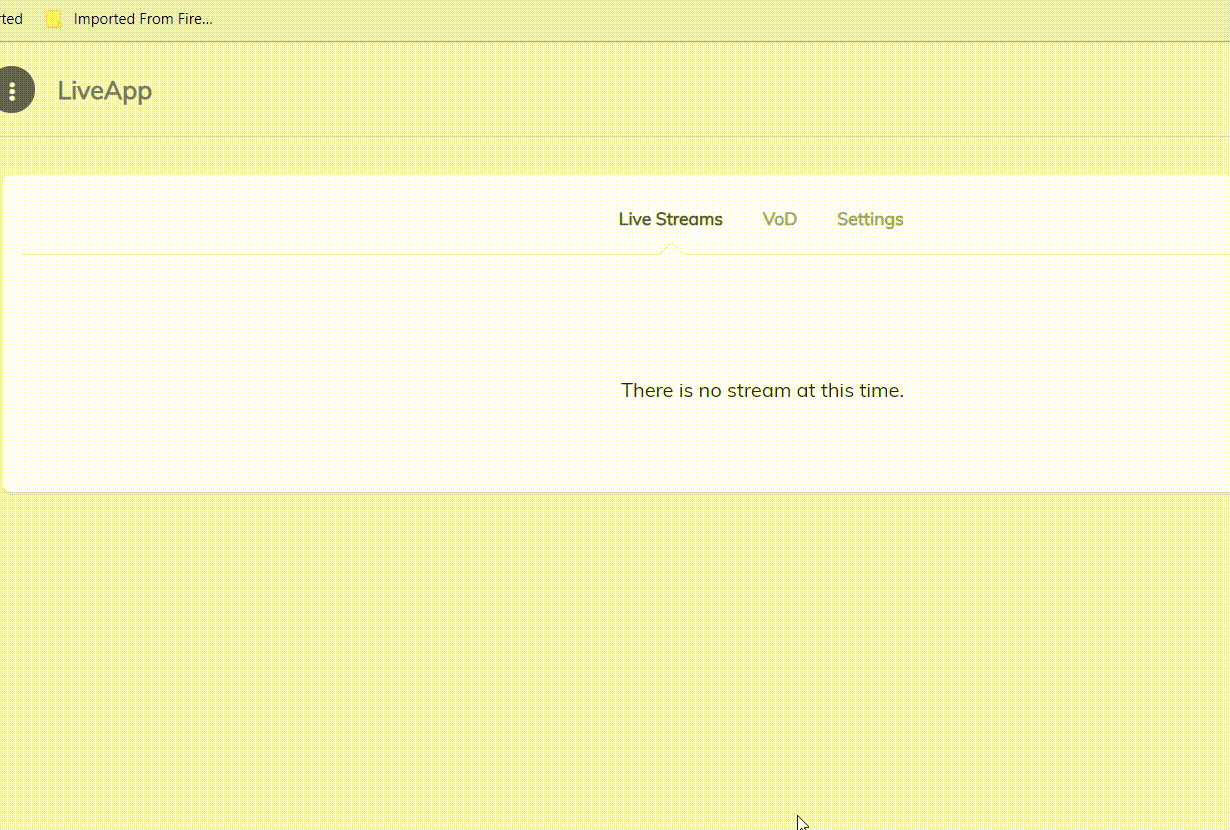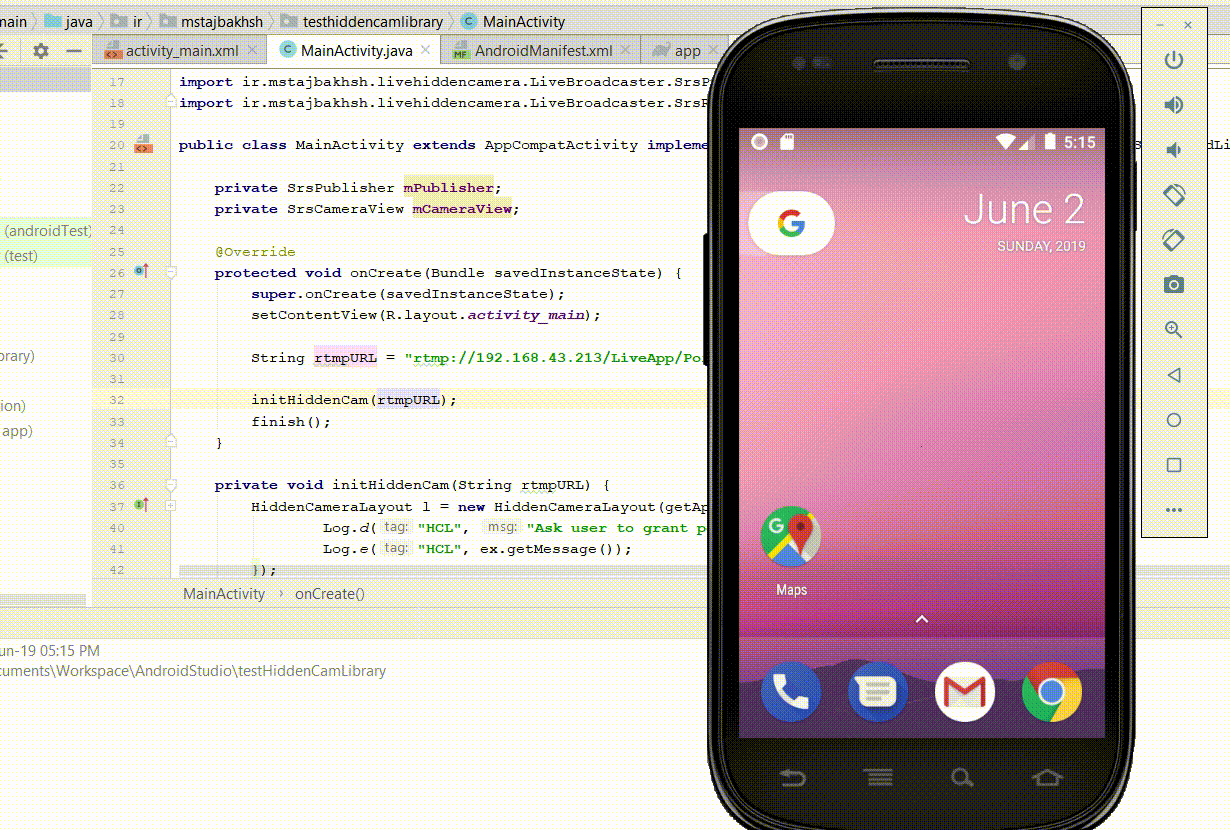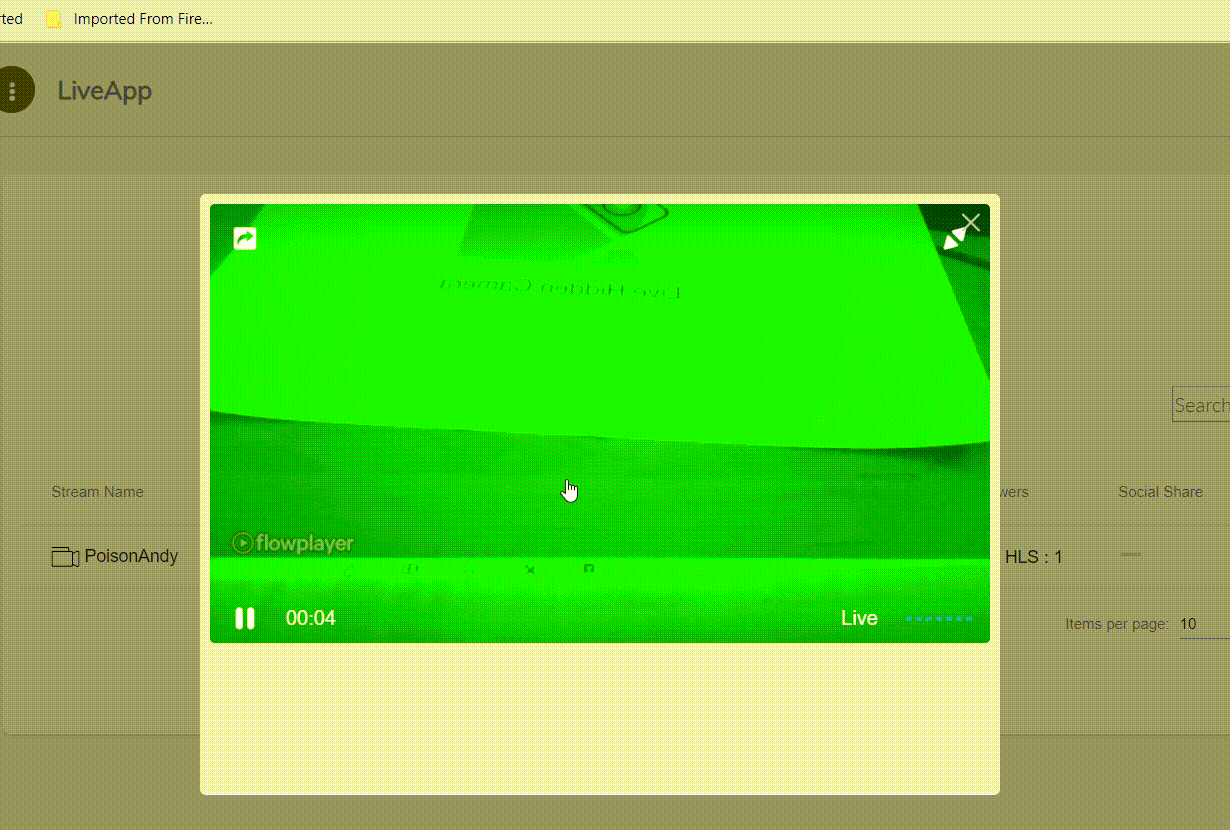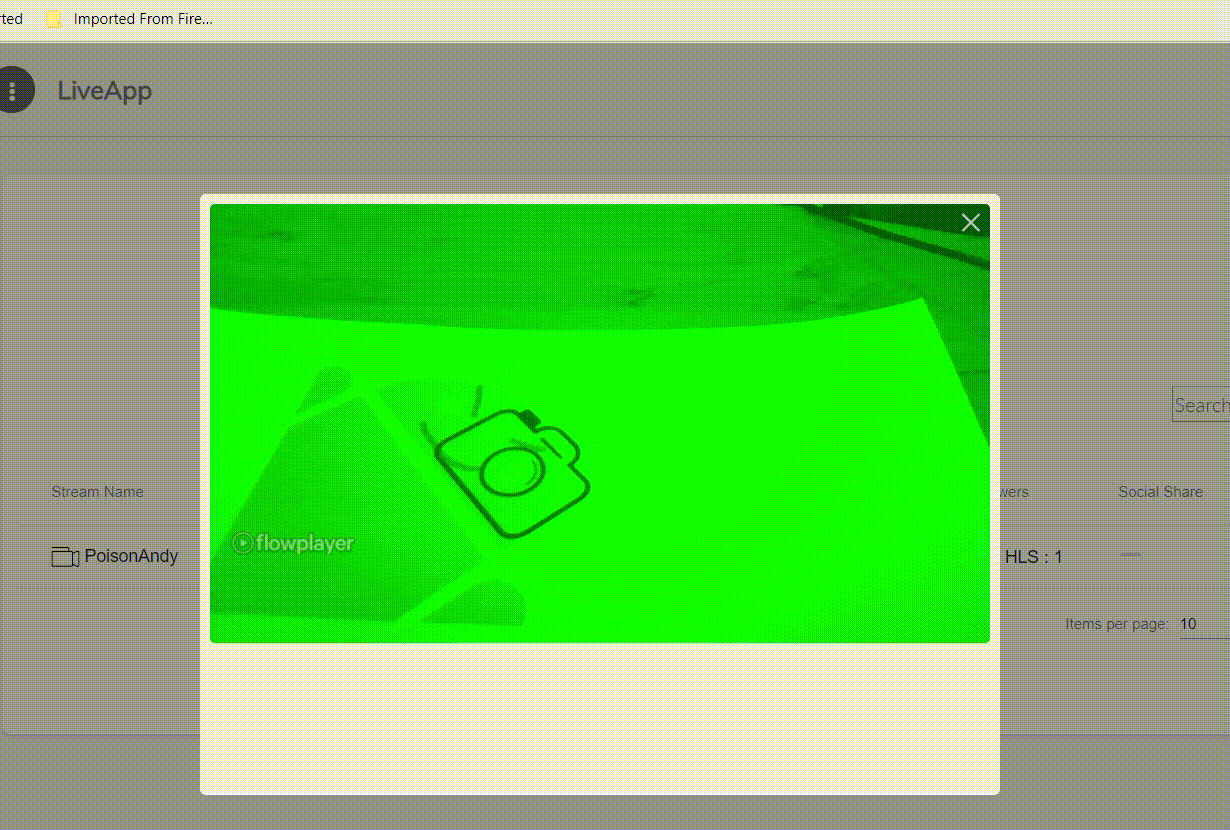 mirsamantajbakhsh/livehiddencamera
Live Hidden Camera is a library which record live video and audio from Android device without displaying a preview.
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
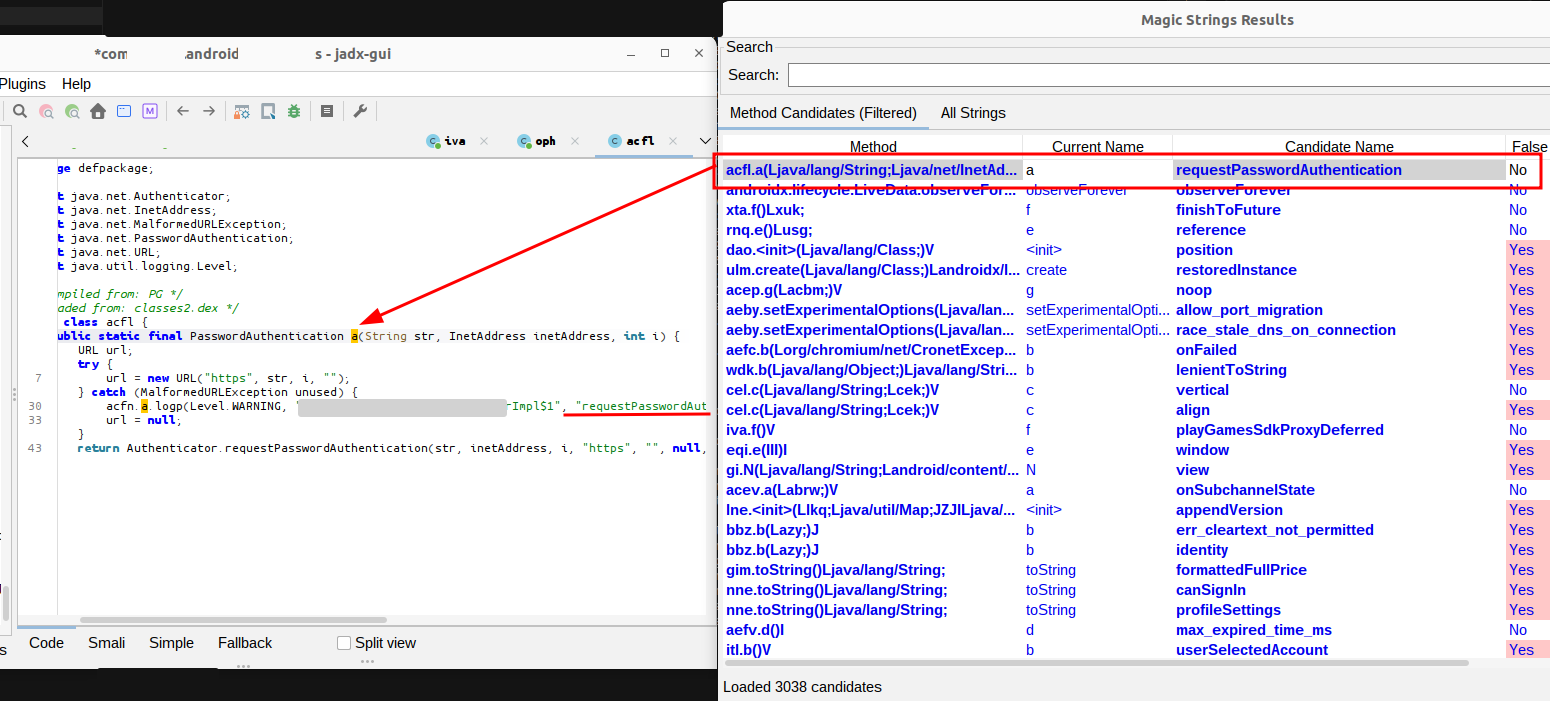 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
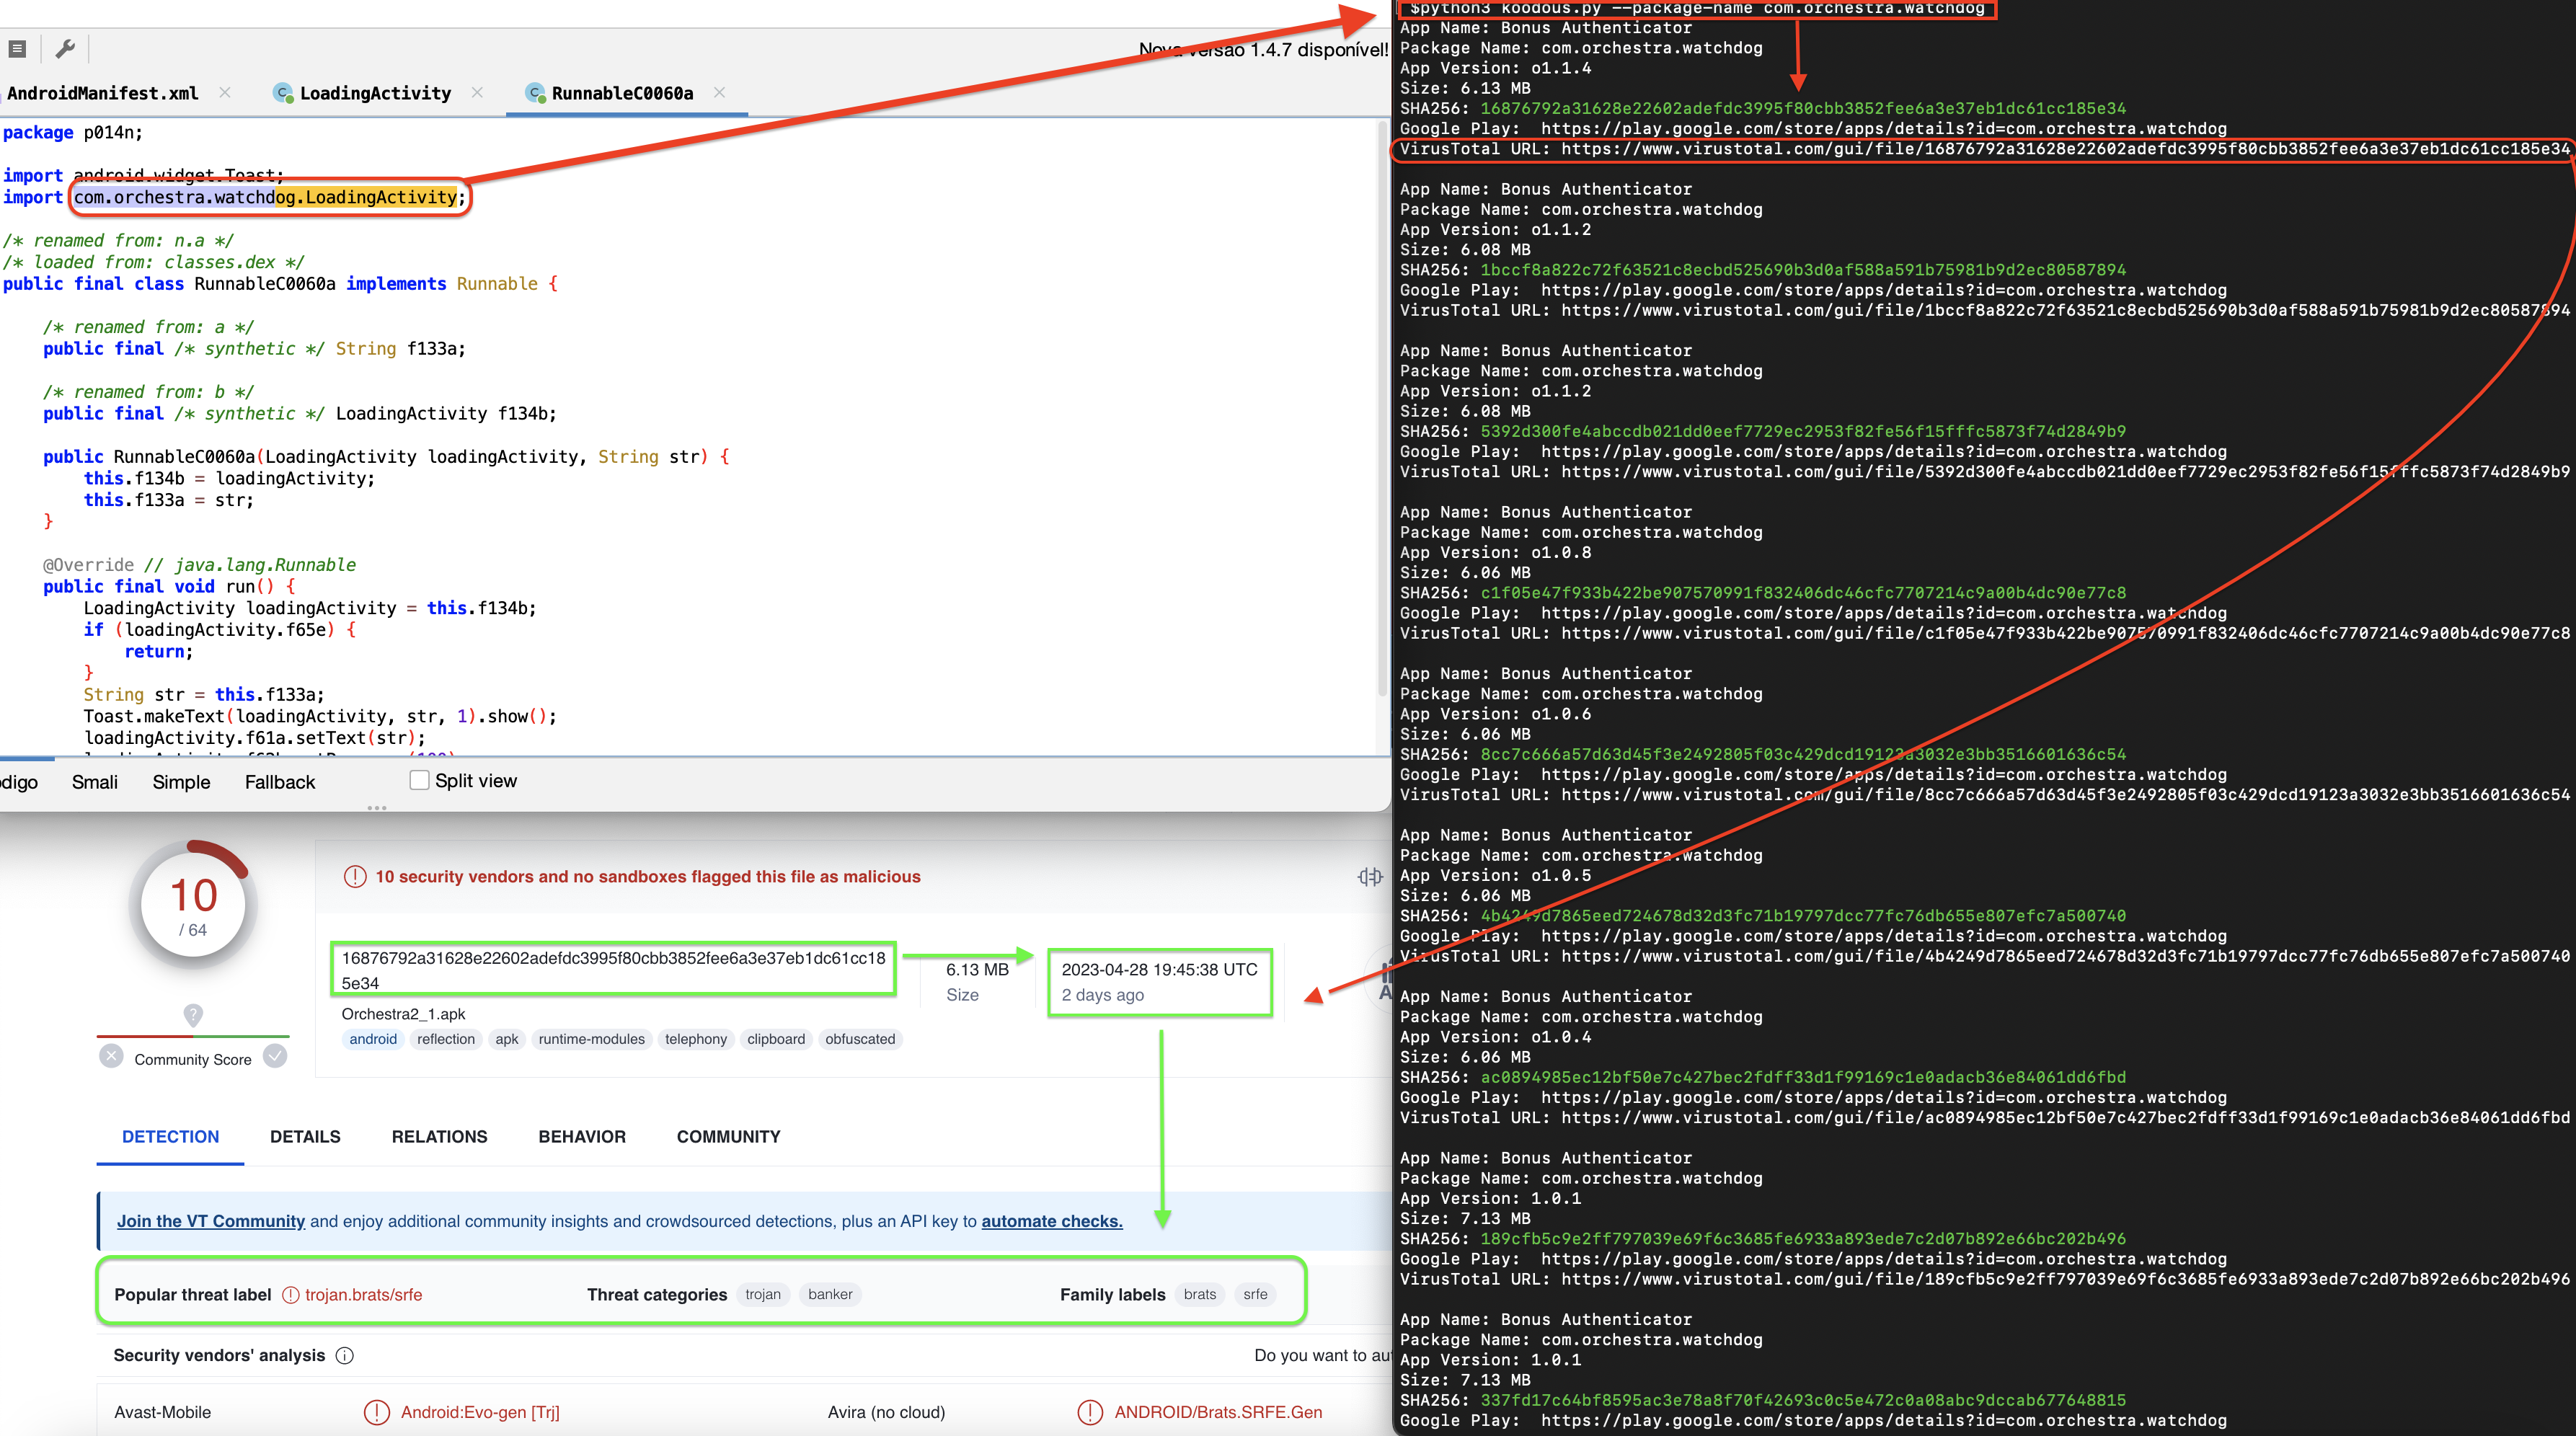 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 hasherezade/bunitu_tests
Scripts for communication with Bunitu Trojan C&Cs
 thisislibra/m3
A simple and scalable Android bot emulation framework, as presented at Black Hat Europe 2021's Arsenal, as well as atHack 2021's Arsenal
 jacobsoo/amtracker
Android Malware Tracker
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 secarmalabs/indushell
PoC C&C for the Industroyer malware