

ceasta
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
138
ngwg/ceastadisassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
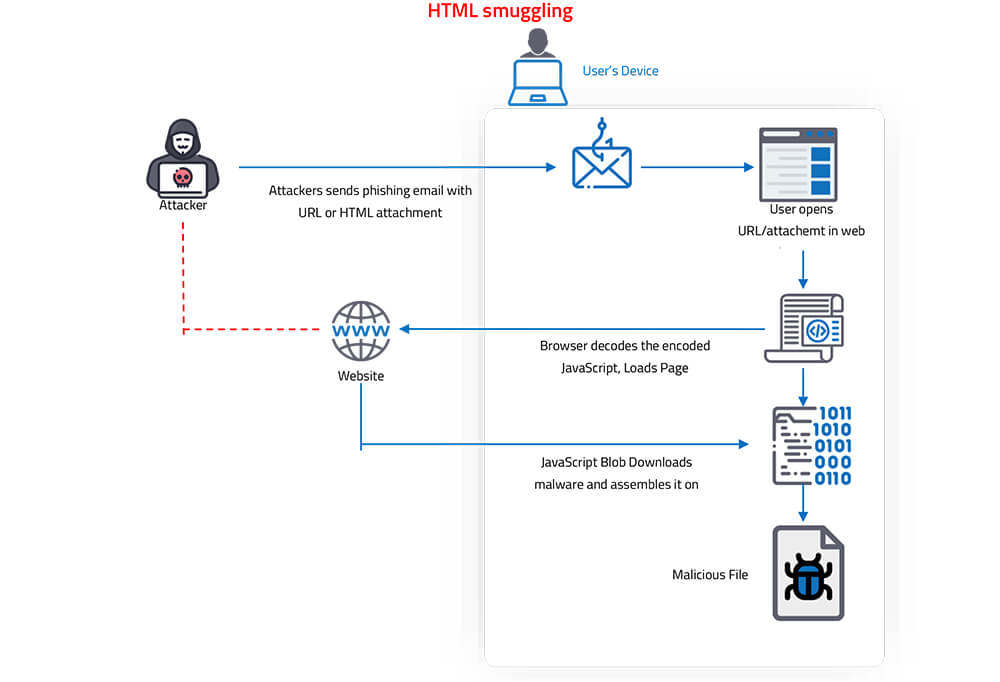 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page
 d4vinci/palsy-virus
Python virus that will make your pc paralyzed once it opened :D
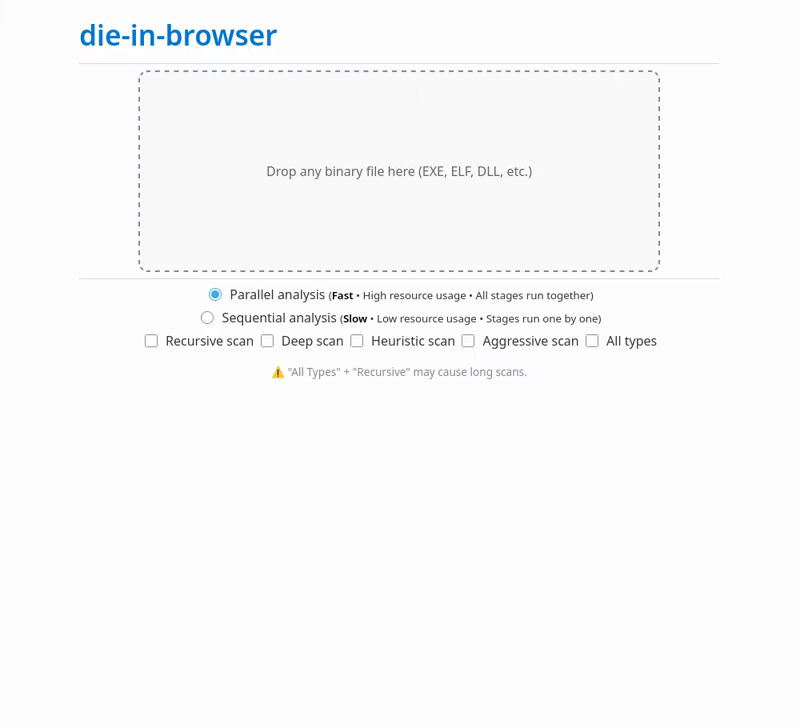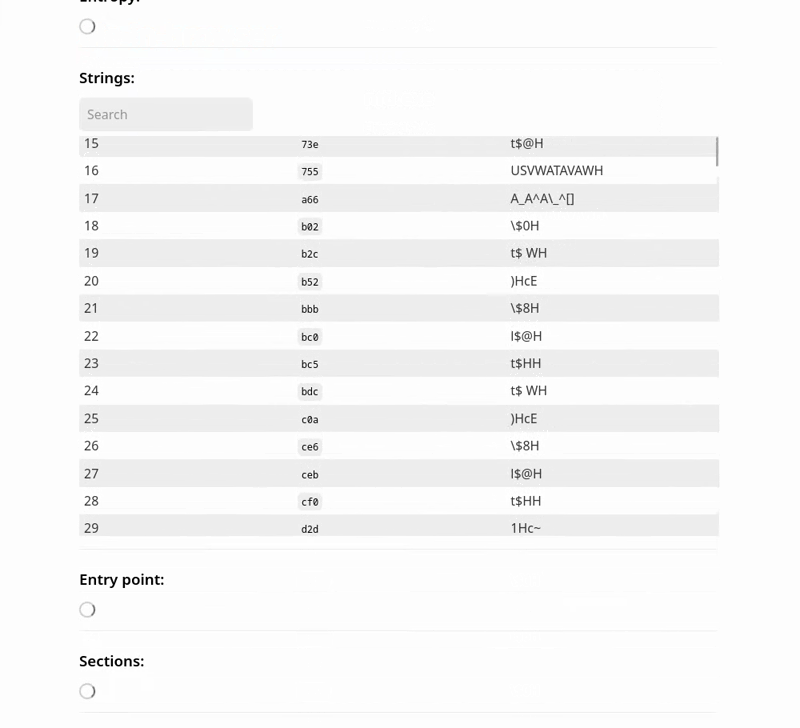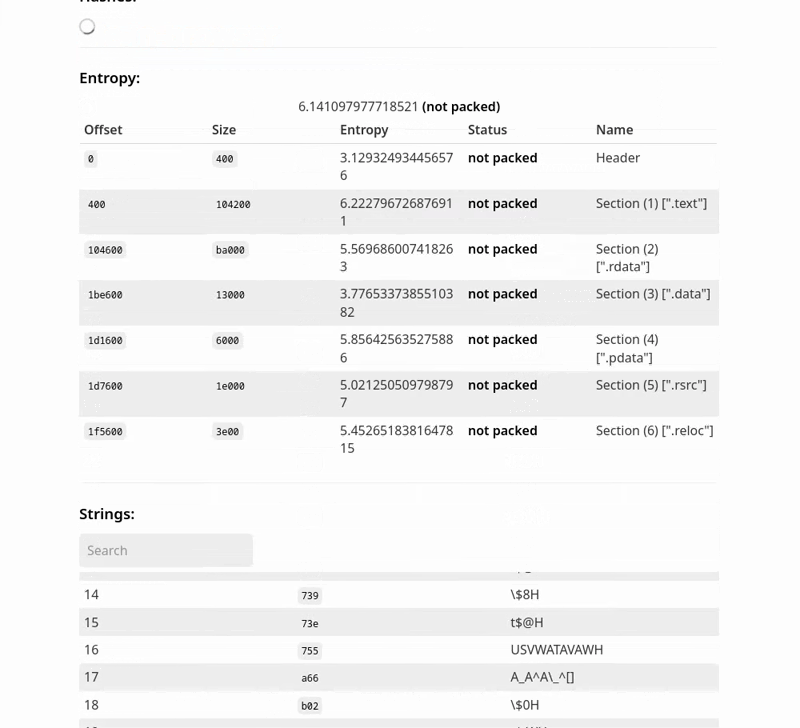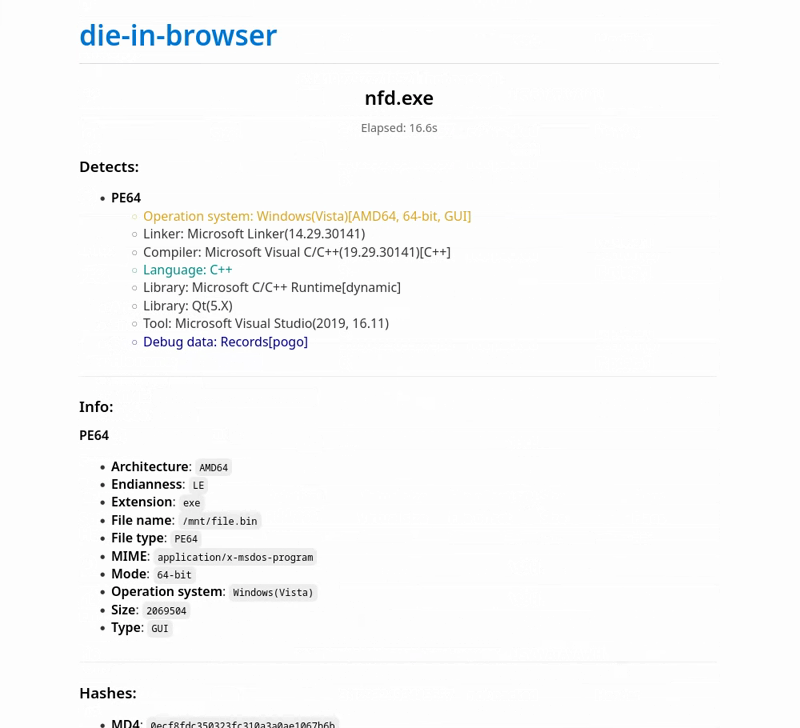 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 roxanne_ardary/emailxpose
EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…
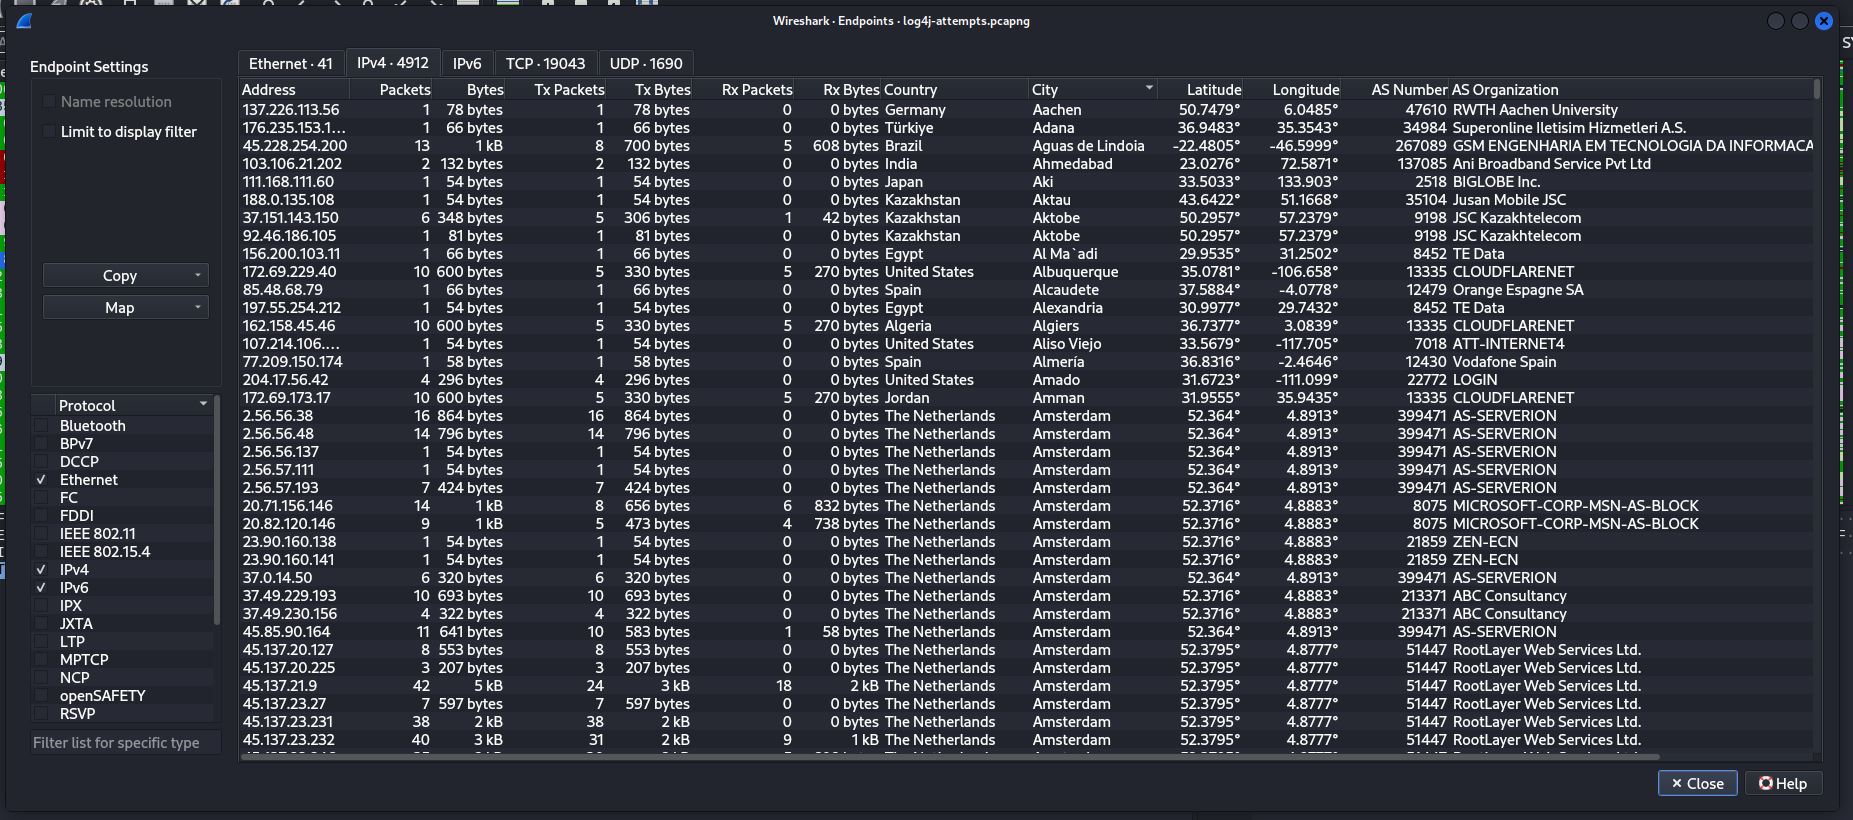 kirkdjohnson/wireshark
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…
 roxanne_ardary/safeforge
SafeForge is an open-source mobile app hub built on GitLab that enables developers to build, upload, and share applications in a secure, AI-verified…
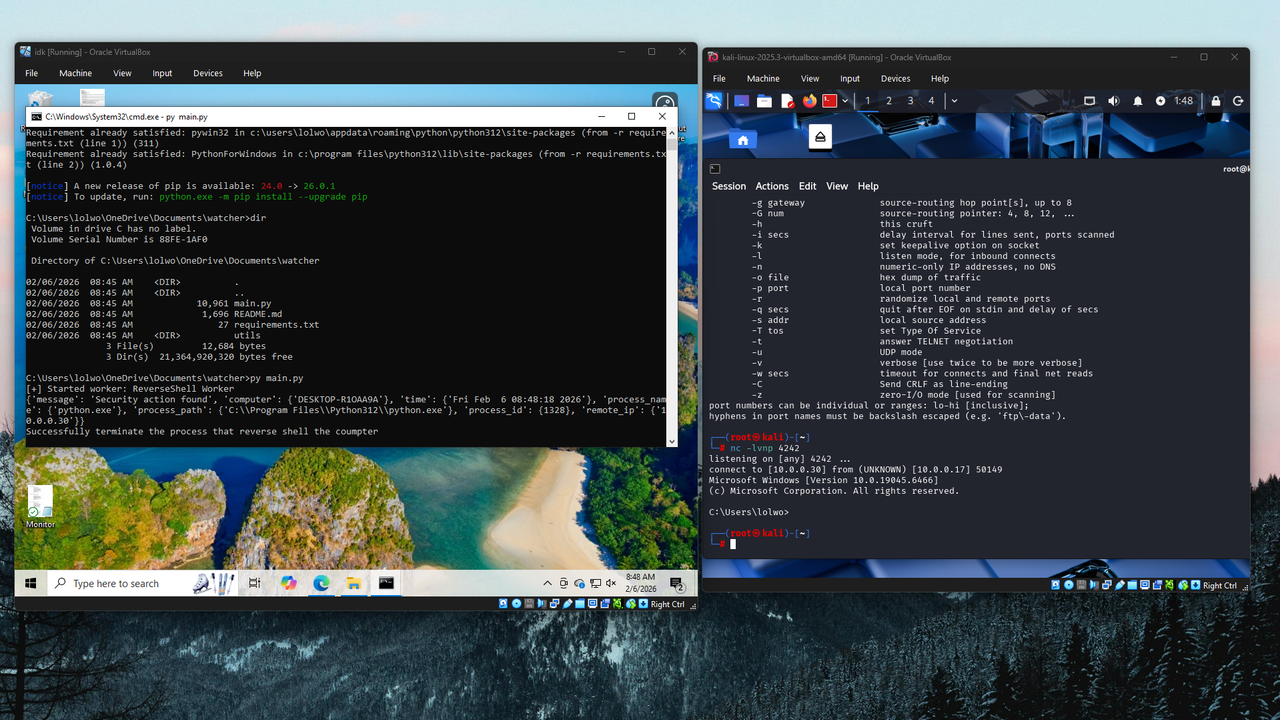 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 chryzsh/darthsidious
Building an Active Directory domain and hacking it
 rasta-mouse/threatcheck
Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.
 oalabs/hashdb
Assortment of hashing algorithms used in malware
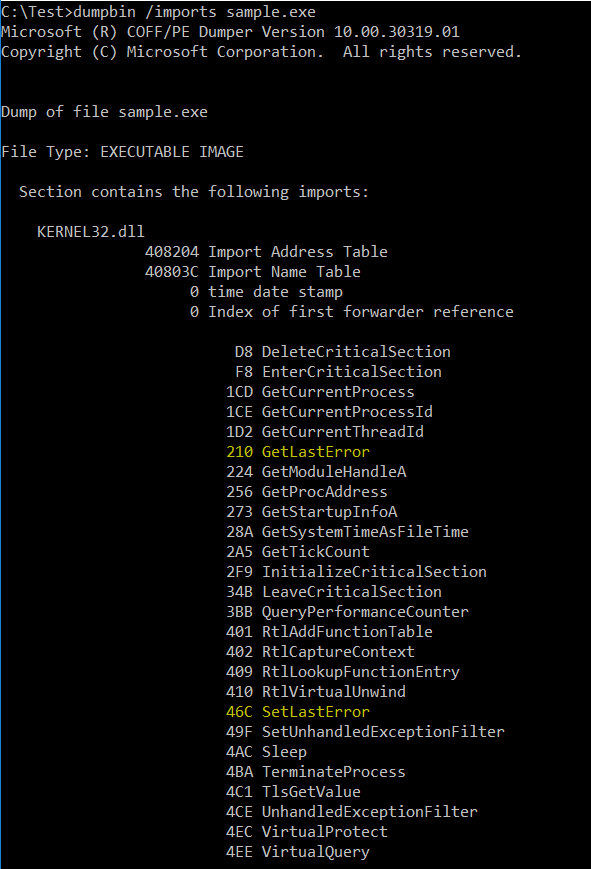 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
 nmatt0/moria
IoT firmware identification and extraction
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
 9aylas/shortcut-payload-generator
AutoIt HackTool, Shortcuts .lnk Payloads Generator As LNK-KISSER.