
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
85 results
ATMMalScan preview

ATMMalScan

GitHubfboldewin/atmmalscan

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
digital-forensicsdisk-forensicsincident-response+2
57
5 years ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
cryptographydigital-forensicseducation+7
314 months ago
TraceTree preview

TraceTree

GitHubtejasprasad2008-afk/tracetree

Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
container-securitydevsecopsdynamic-analysis-sandboxing+6
4220 days ago
processhacker-mcp preview

processhacker-mcp

GitHubillegal-instruction-co/processhacker-mcp

Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…

debuggersdynamic-analysis-sandboxingexploitation+7
517 months ago
CVE-2018-4878 preview

CVE-2018-4878

GitHubmdsecactivebreach/cve-2018-4878

Proof-of-concept exploit for CVE-2018-4878, a Use-After-Free vulnerability in Adobe Flash Player 32-bit, providing a ByteArray object for process…
binary-exploitationexploitationmalware-analysis+3
238 years ago
KillChain preview

KillChain

GitHuboxfemale/killchain

Kernel Process Termination Tool ( CVE-2026-0828 exploit)
binary-exploitationexploitationmalware-analysis+3
366 months ago
SysTrace preview

SysTrace

GitHubtracebyte8/systrace

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…

anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
241 month ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
android-securitycryptographydynamic-analysis-sandboxing+8
1028 days ago
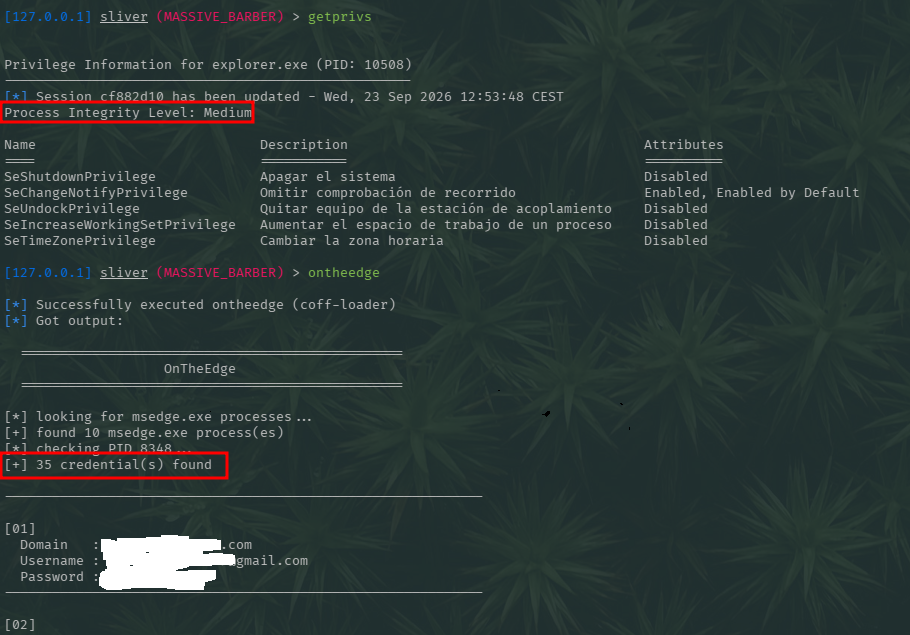
OnTheEdge preview

OnTheEdge

GitHubjssngc/ontheedge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
1113 days ago
BerrySentinel preview

BerrySentinel

GitHubdereeqw/berrysentinel

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
anomaly-detectioncommand-and-controldefensive-tools+8
137 months ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
binary-analysiscommand-and-controldata-exfiltration+4
111 month ago
SOC335---CVE-2024-49138-Exploitation-Detected preview

SOC335---CVE-2024-49138-Exploitation-Detected

GitHubfabianch20/soc335---cve-2024-49138-exploitation-detected

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…
digital-forensicseducationincident-response+7
21 days ago
CVE-2018-10583 preview

CVE-2018-10583

GitHubmrtaheramine/cve-2018-10583

An information disclosure vulnerability occurs when LibreOffice 6.0.3 and Apache OpenOffice Writer 4.1.5 automatically process and initiate an SMB…
exploitationinformation-gatheringmalware-analysis+2
98 years ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

binary-analysiseducationforensics+7
32 months ago
CVE-2025-61155 preview

CVE-2025-61155

GitHubsf0rzin/cve-2025-61155

CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
binary-analysiseducationexploitation+7
33 months ago
CVE-2026-36130 preview

CVE-2026-36130

GitHubcwjchoi01/cve-2026-36130

Proof-of-concept demonstrating a vulnerability that disables Microsoft Defender (MsMpEng.exe) by locking a folder and rebooting, with screenshots…

defensive-toolsexploitationincident-response+2
1 month ago
rootkit-signal-hunter preview

rootkit-signal-hunter

GitHubbcoles/rootkit-signal-hunter

Detect Linux rootkits which use signals to elevate process privileges.
defensive-toolsdynamic-analysis-sandboxingforensics+3
311 months ago
CVE-2025-61301 preview

CVE-2025-61301

GitHubegkritsis/cve-2025-61301

CVE-2025-61301 proof-of-concept demonstrating denial-of-analysis in CAPEv2 via recursive process forking that triggers MongoDB BSON limits and orjson…

dynamic-analysis-sandboxingexploitationmalware-analysis+2
210 months ago
Previous12345Next