
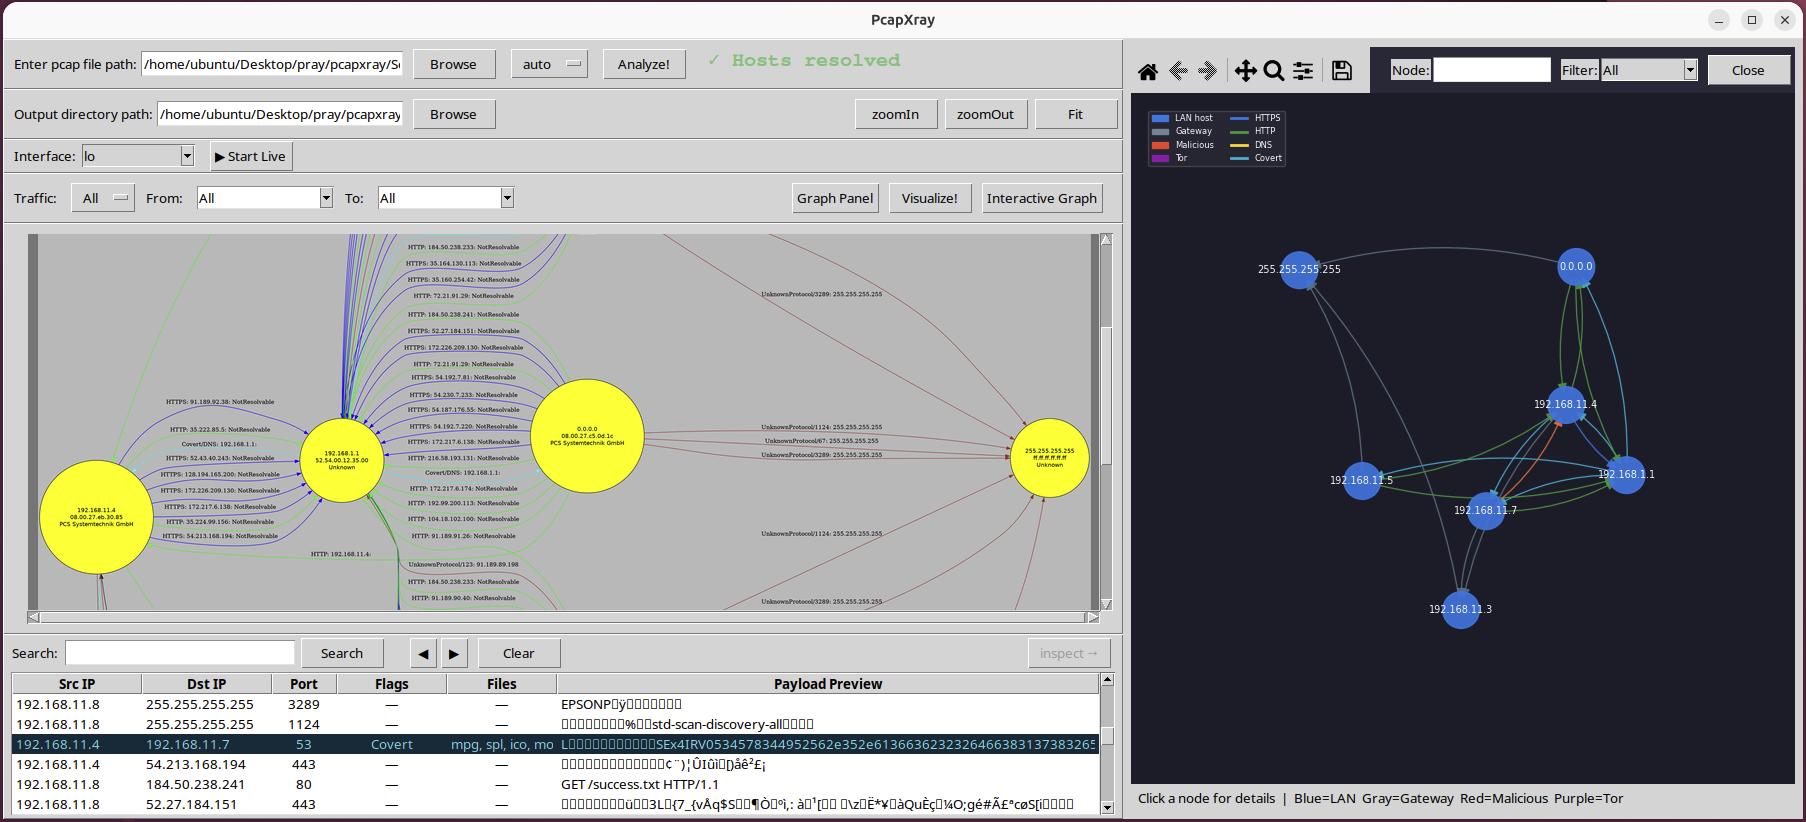
PcapXray
 srixivas/pcapxray
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
ctfdns-analysiseducation+7
1.9k5 months ago
srixivas/pcapxray❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…
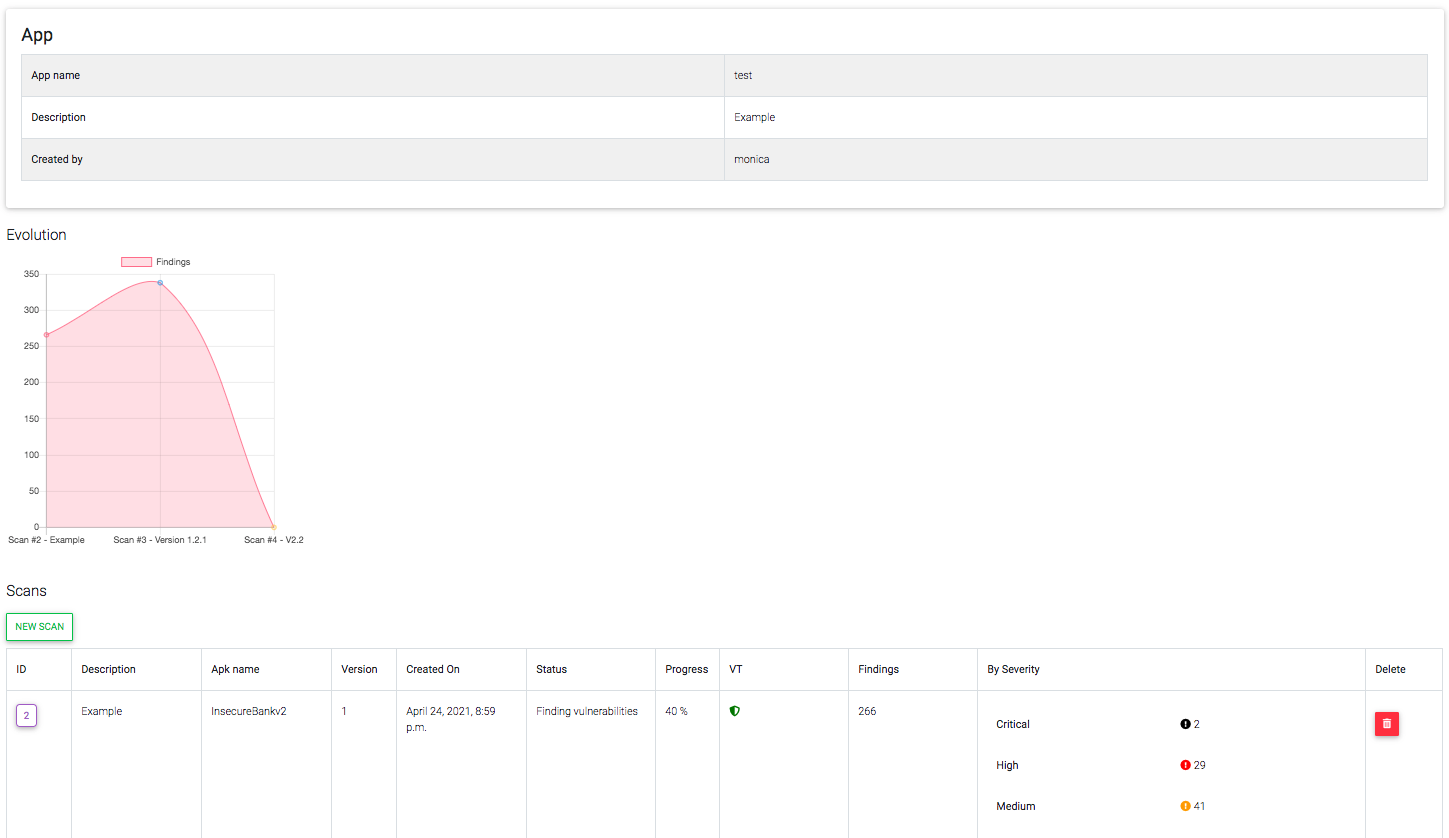 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 blackoclock/xls-to-dbatloader-or-guloader-for-agenttesla-variant
CVE-2017-0199 XLS --> HTA --> VBS --> STEGANOGRAPHY --> DBATLOADER/GULOADER STYLE MALWARE
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
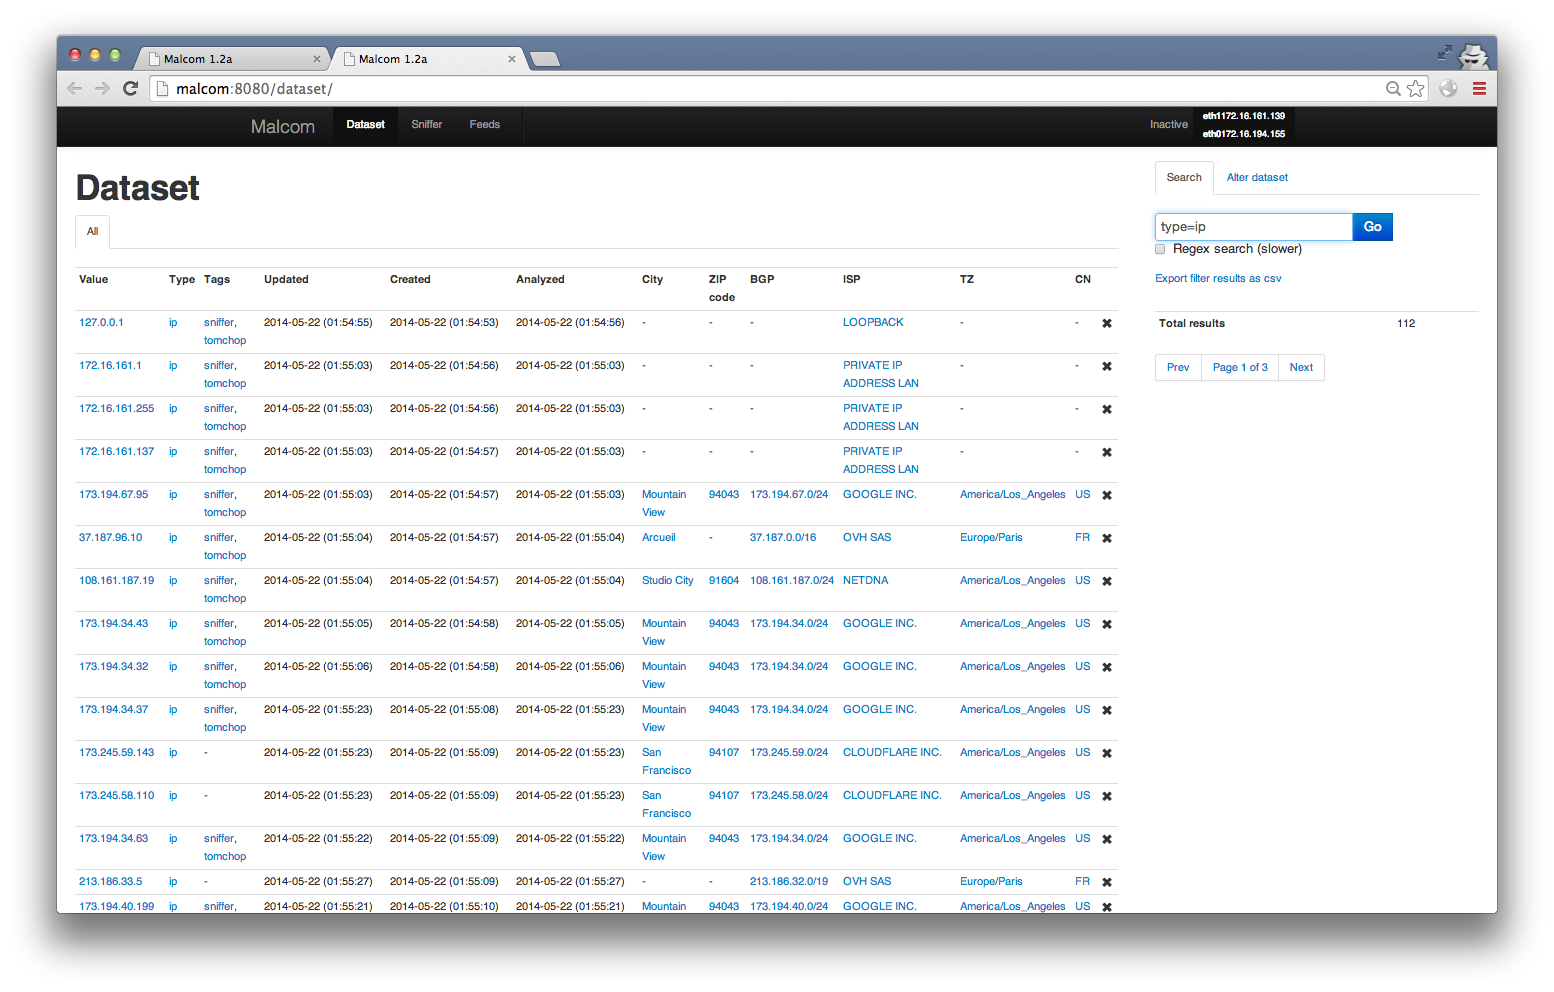 tomchop/malcom
Malcom - Malware Communications Analyzer
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
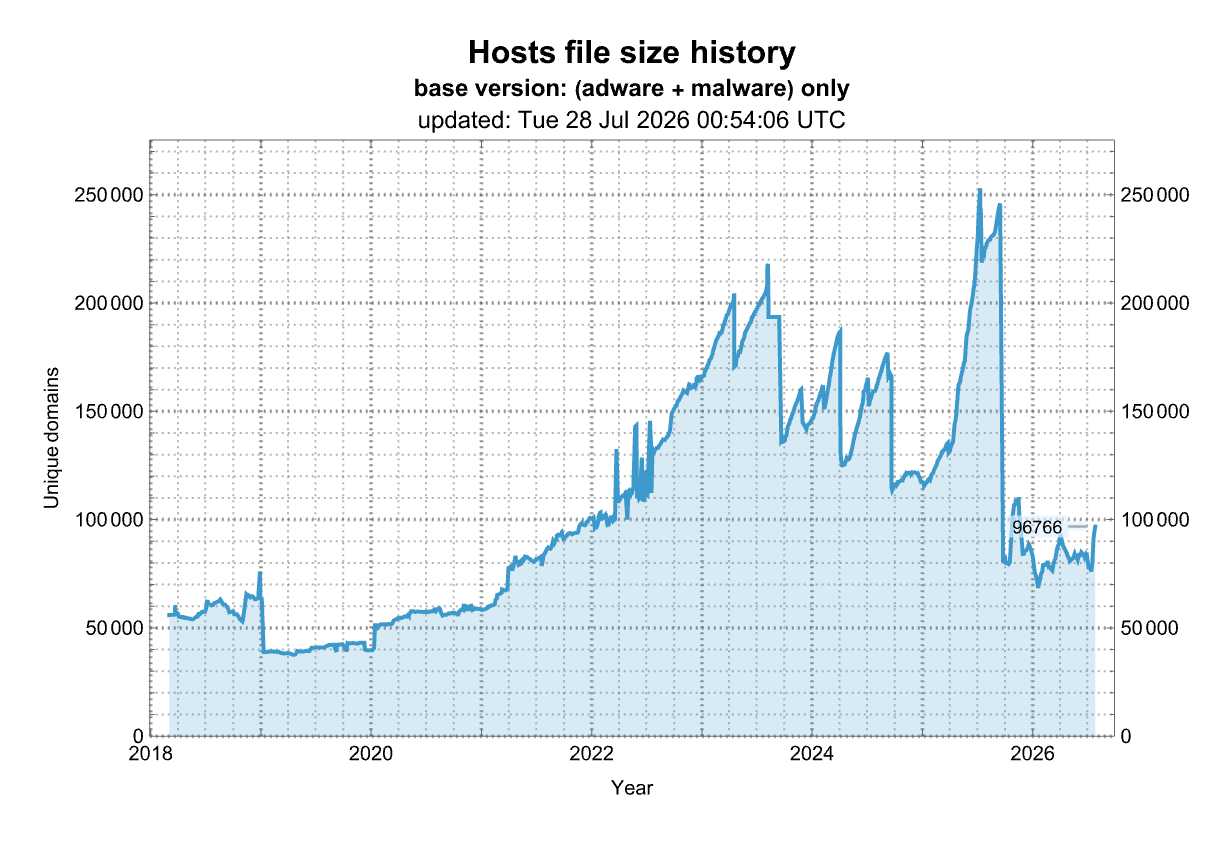 stevenblack/hosts
🔒 Consolidating and extending hosts files from several well-curated sources. Optionally pick extensions for porn, social media, and other categories.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 rshipp/awesome-malware-analysis
Defund the Police.
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 aydinnyunus/keylogger
Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards