

CVE-2023-23397_EXPLOIT_0DAY
 sqrtzeroknowledge/cve-2023-23397_exploit_0day
Exploit for the CVE-2023-23397
email-securityexploitationmalware-analysis+3
158
sqrtzeroknowledge/cve-2023-23397_exploit_0dayExploit for the CVE-2023-23397
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 hasherezade/bunitu_tests
Scripts for communication with Bunitu Trojan C&Cs
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 secarmalabs/indushell
PoC C&C for the Industroyer malware
 fevar54/cve-2026-3502---trueconf-client-update-hijacking-poc
PoC de CVE-2026-3502: hijacking de actualizacion en TrueConf Client para RCE (Operacion TrueChaos).
 joakimbulow/cve-2026-23907
Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…
 saykino/cve-2025-66837
Technical documentation and proof-of-concept for CVE-2025-66837, a remote authenticated file upload vulnerability in ARIS allowing arbitrary code…
 open-flaw/cve-2026-3462
Acrobat Reader | Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') (CWE-1321)
 mmiszczyk/cve-2021-33879
GameLoop update MITM
 hexnone/cve-2019-6440
Proof-of-concept exploit for CVE-2019-6440 achieving SYSTEM privilege escalation on Zemana antimalware via man-in-the-middle update interception and…
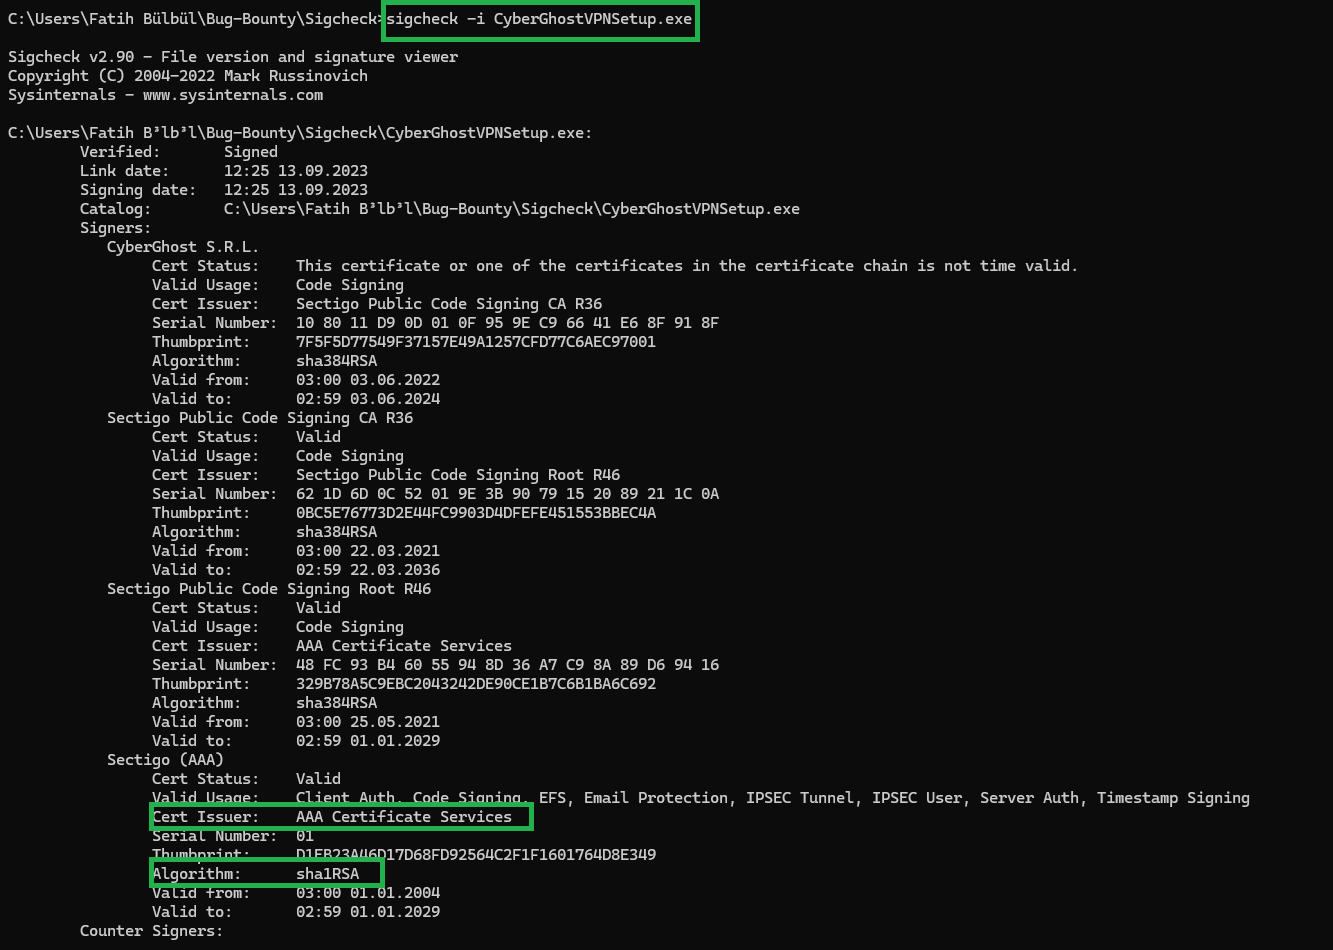 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 varunsaru/snp
CVE-2017-8759 || report related with execute code vulnerability
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…