
threat-research
 threatray/threat-research
IoCs and YARA rules from Threatray's Threat Research
forensicsincident-responseioc-management+2
2312h 49m ago
threatray/threat-researchIoCs and YARA rules from Threatray's Threat Research
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 vxunderground/malwaresourcecode
Collection of malware source code for a variety of platforms in an array of different programming languages.
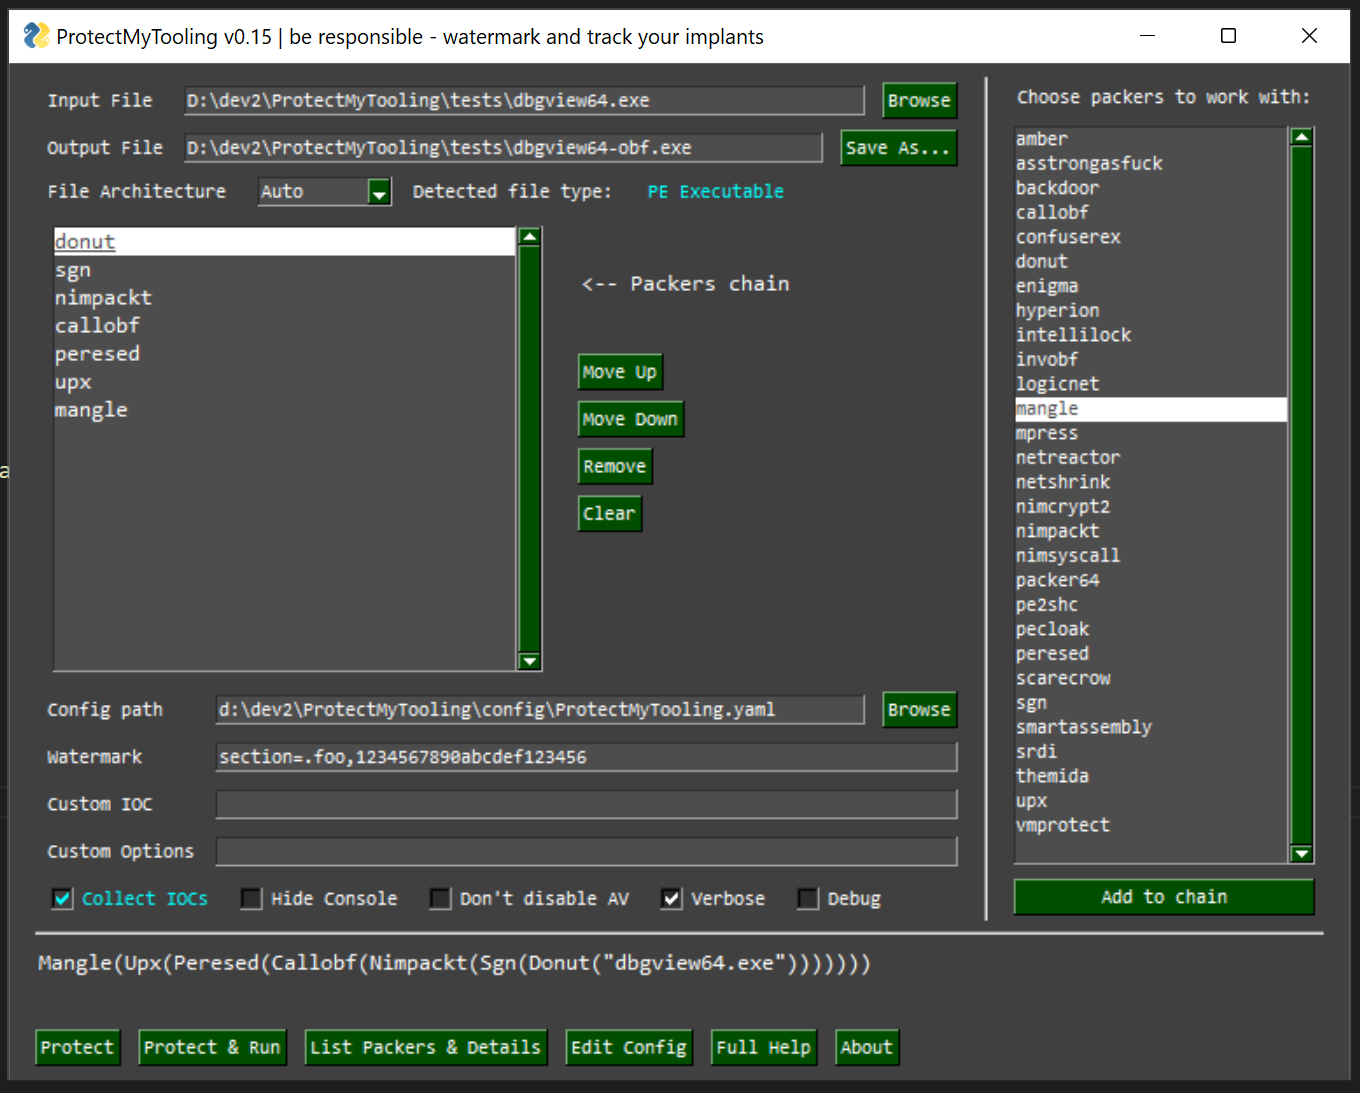 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 internetangel/zerocrumb
Dumping App Bound Protected Credentials & Cookies Without Privileges.
 vxunderground/vx-api
Collection of various malicious functionality to aid in malware development