
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
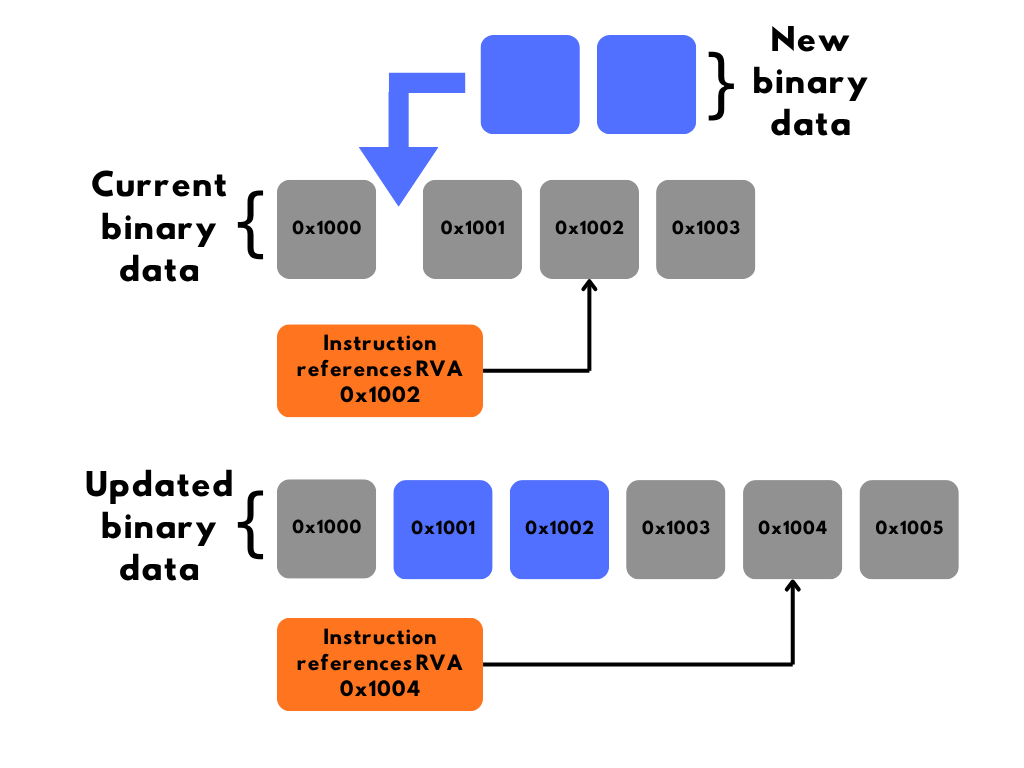 noahware/binprotect
x64 PE bin2bin obfuscator which doesn't add a section to the binary
 caliburn9/cve-2023-21716-analysis-ict287
Technical analysis and reproduction of CVE-2023-21716, a critical heap-based buffer overflow in Microsoft Word's RTF parser, including root cause,…
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 decalage2/oletools
Python toolkit for analyzing MS OLE2 and Office documents, extracting VBA macros, detecting exploits, and performing forensic analysis of structured…
 matank001/asclepius
Asclepius validates backup integrity by restoring files and actively testing their recoverability. Instead of trusting metadata, it attempts to parse…
 dissectmalware/pyonenote
A python library to parse OneNote (.one) files
 ricardojoserf/whoamialternatives
Different methods to get current username without using whoami
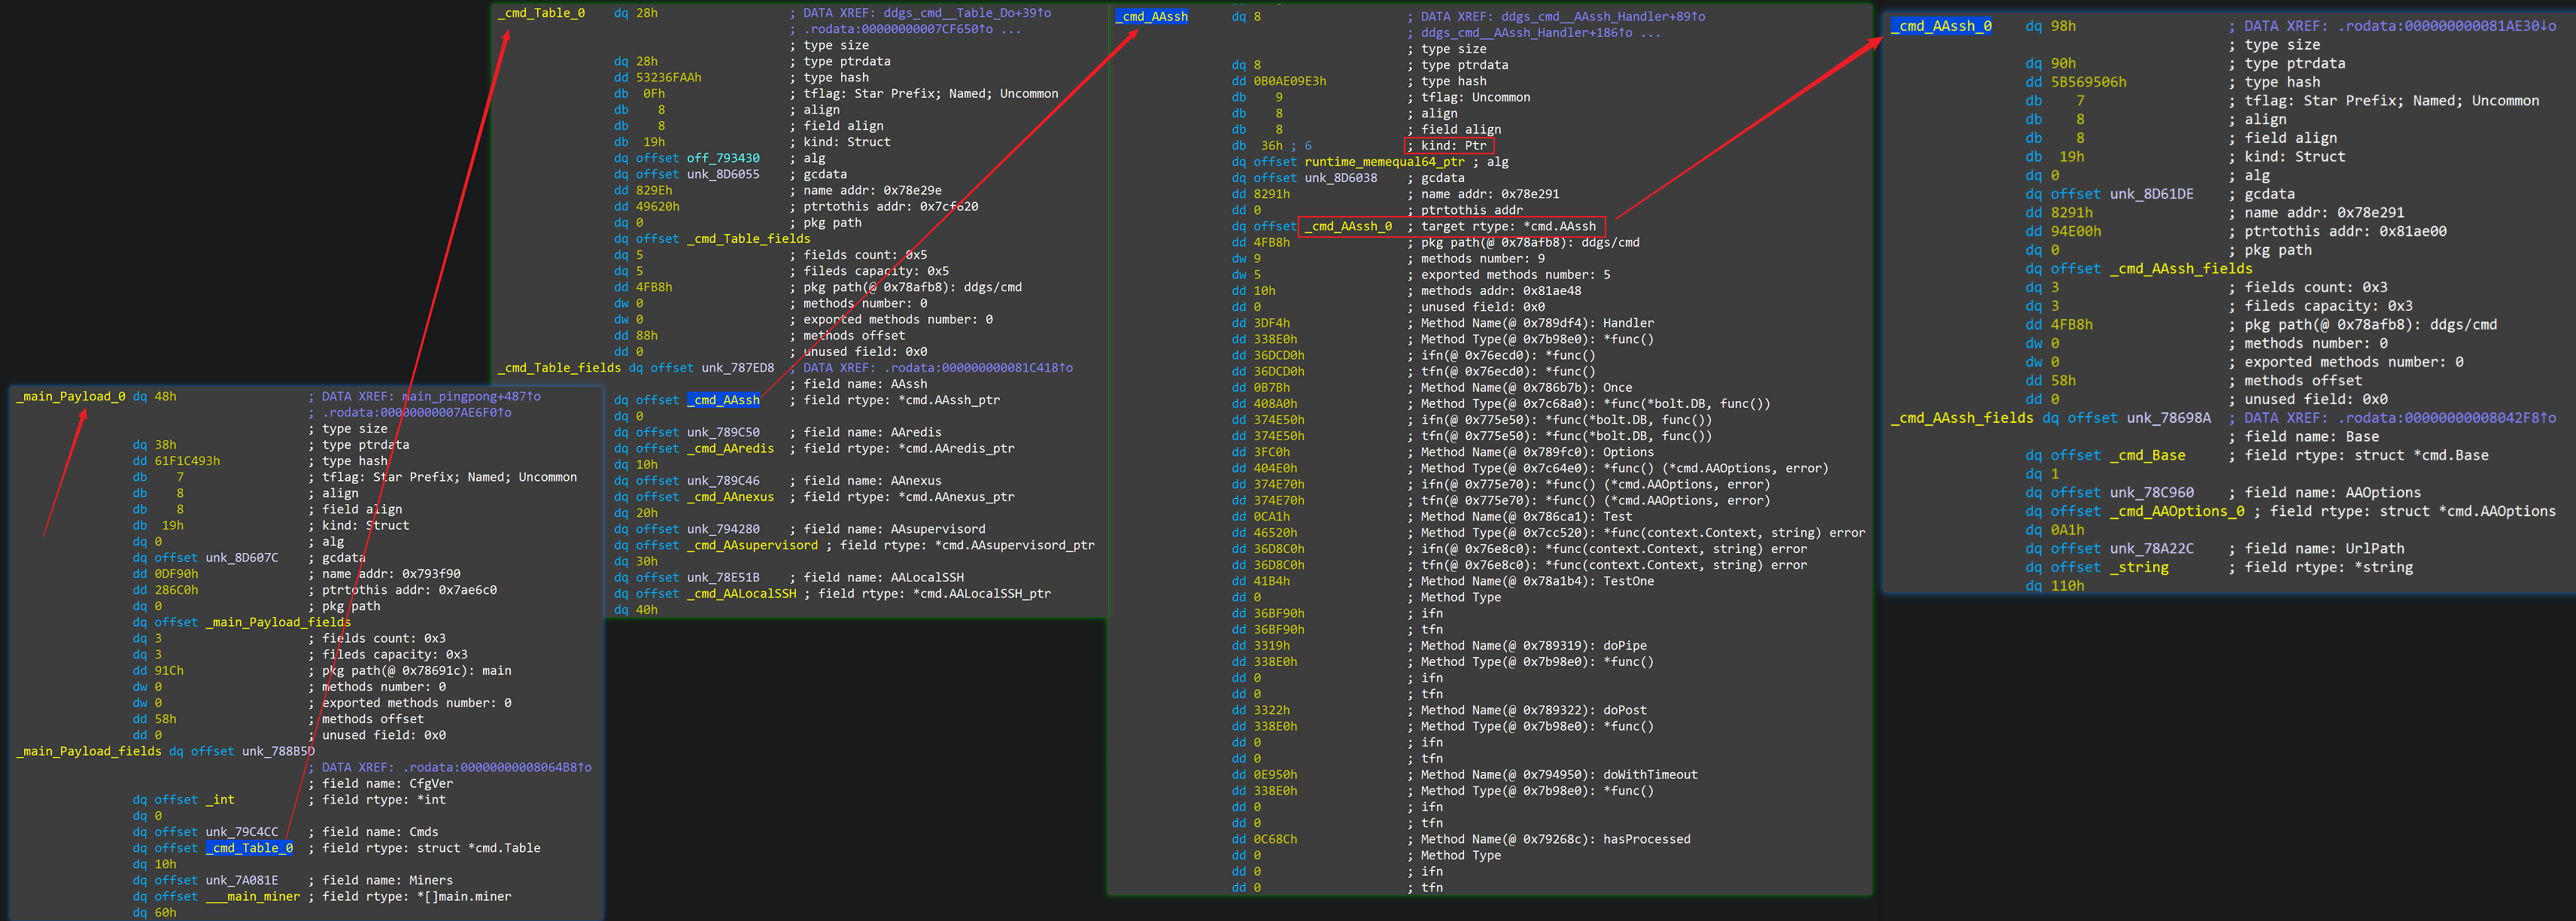 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro