Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…

Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…

Windows tool for dumping malware PE files from memory back to disk for analysis.

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

Proof of Concept for Process Code Injection Without Using WriteProcessMemory

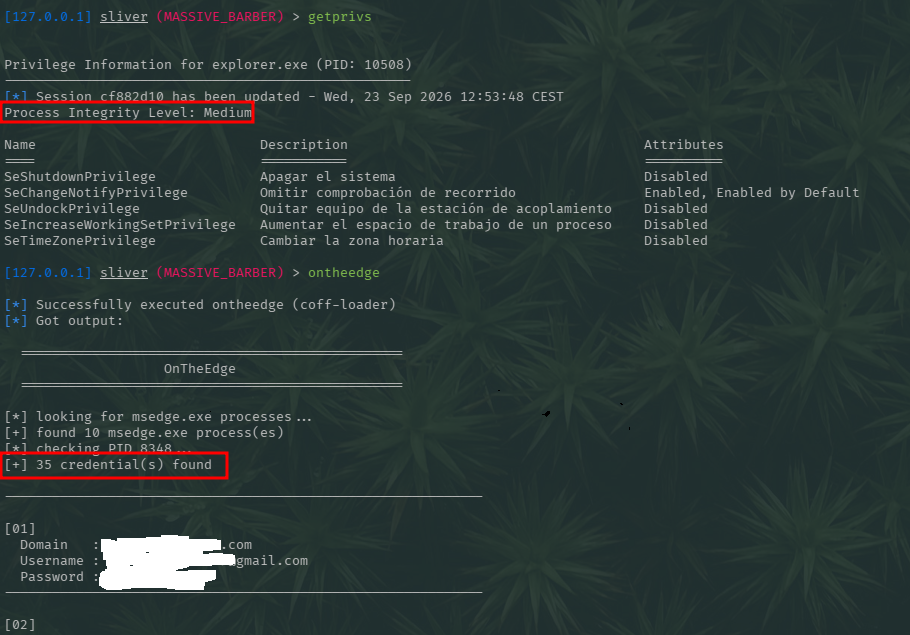
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…

An API hooking framework for intercepting and monitoring Windows applications

Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

CVE-2025-61301 proof-of-concept demonstrating denial-of-analysis in CAPEv2 via recursive process forking that triggers MongoDB BSON limits and orjson…

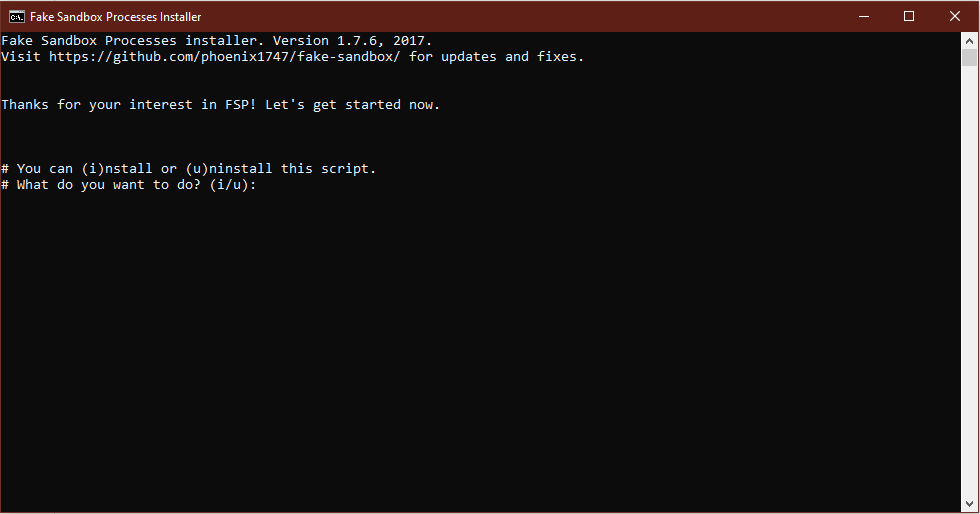
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.