
Shadowbroker
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
command-and-controlcrawlerdns-analysis+7
bigbodycobain/shadowbrokerReal-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
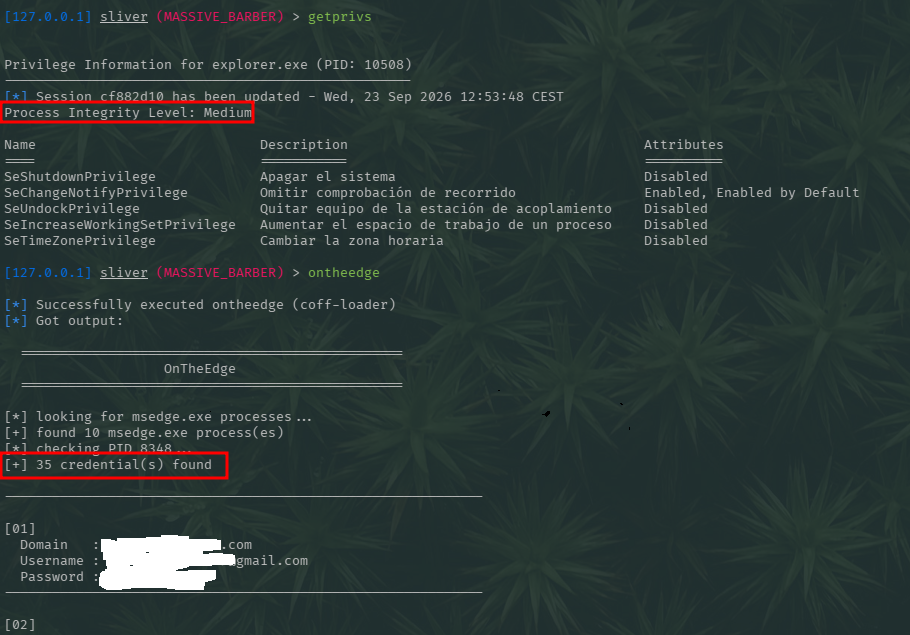 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 princessauroraj/chinese-cybercrime-research
Resources to learn more about Chinese-language cybercrime actors.
 capesandbox/cape-parsers
CAPE core and community parsers
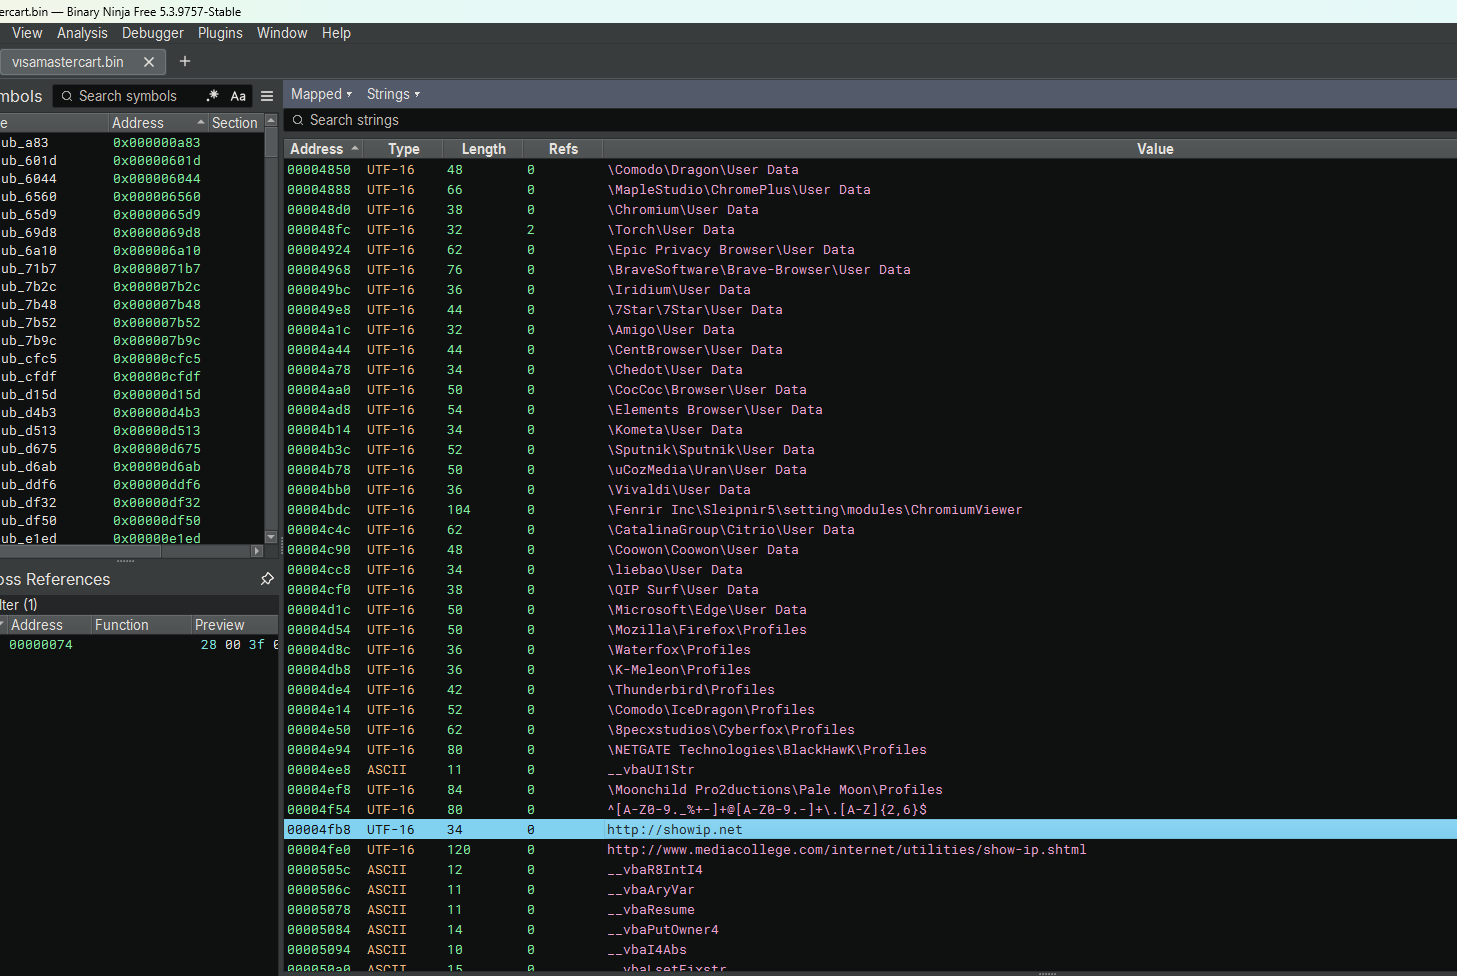 kaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis
Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
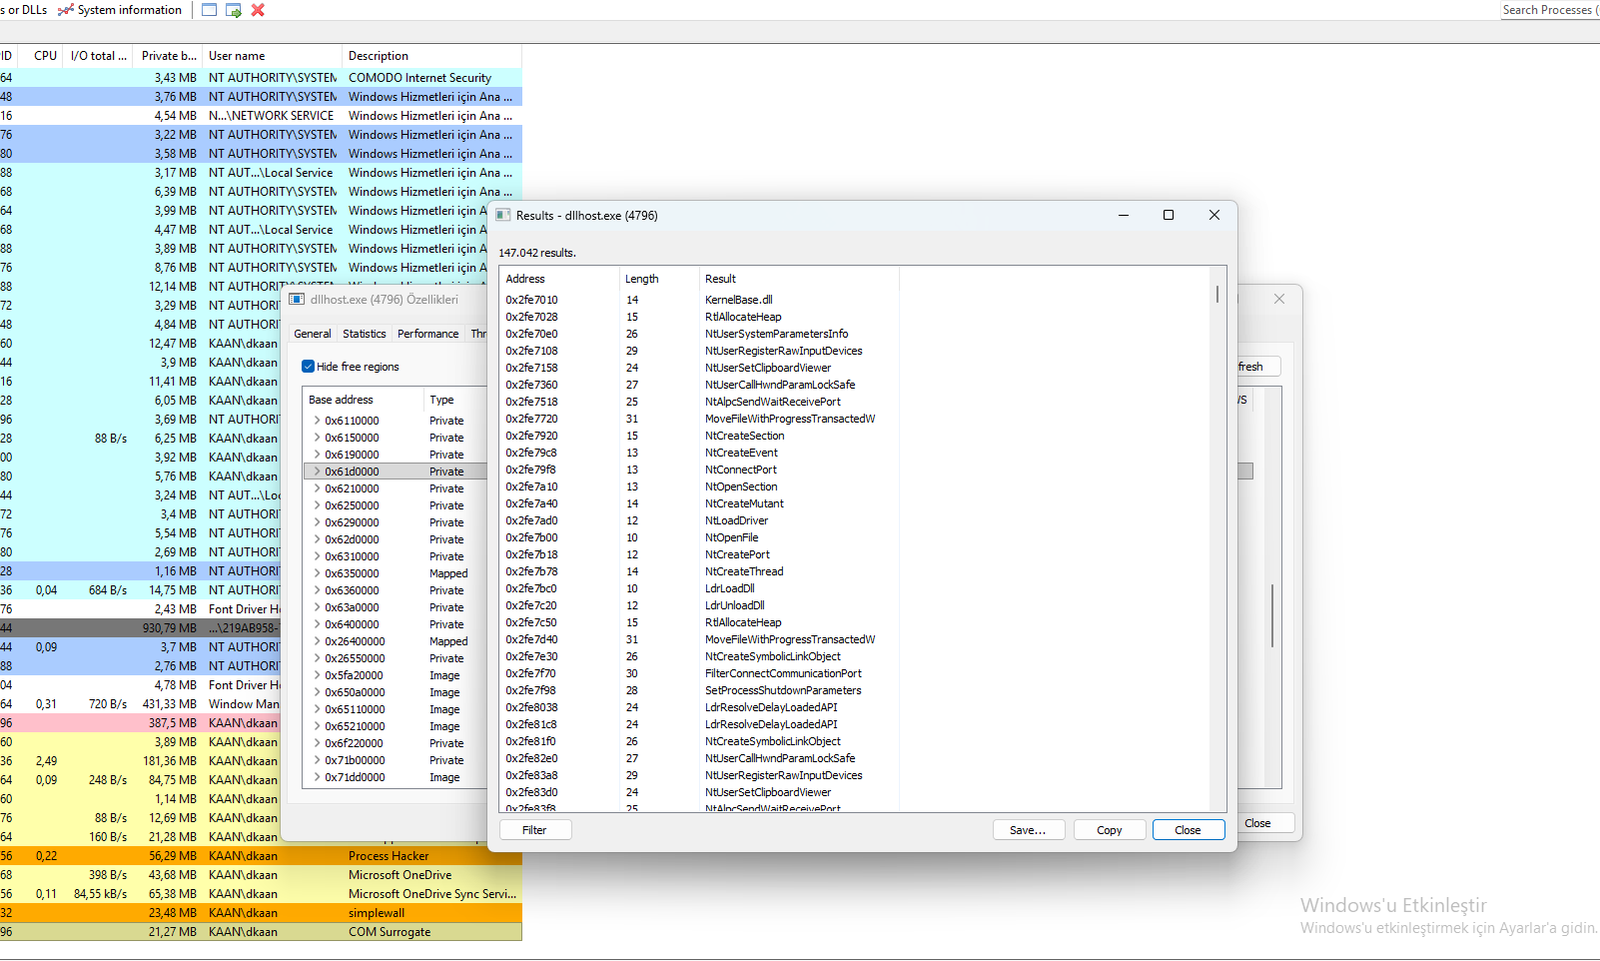 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
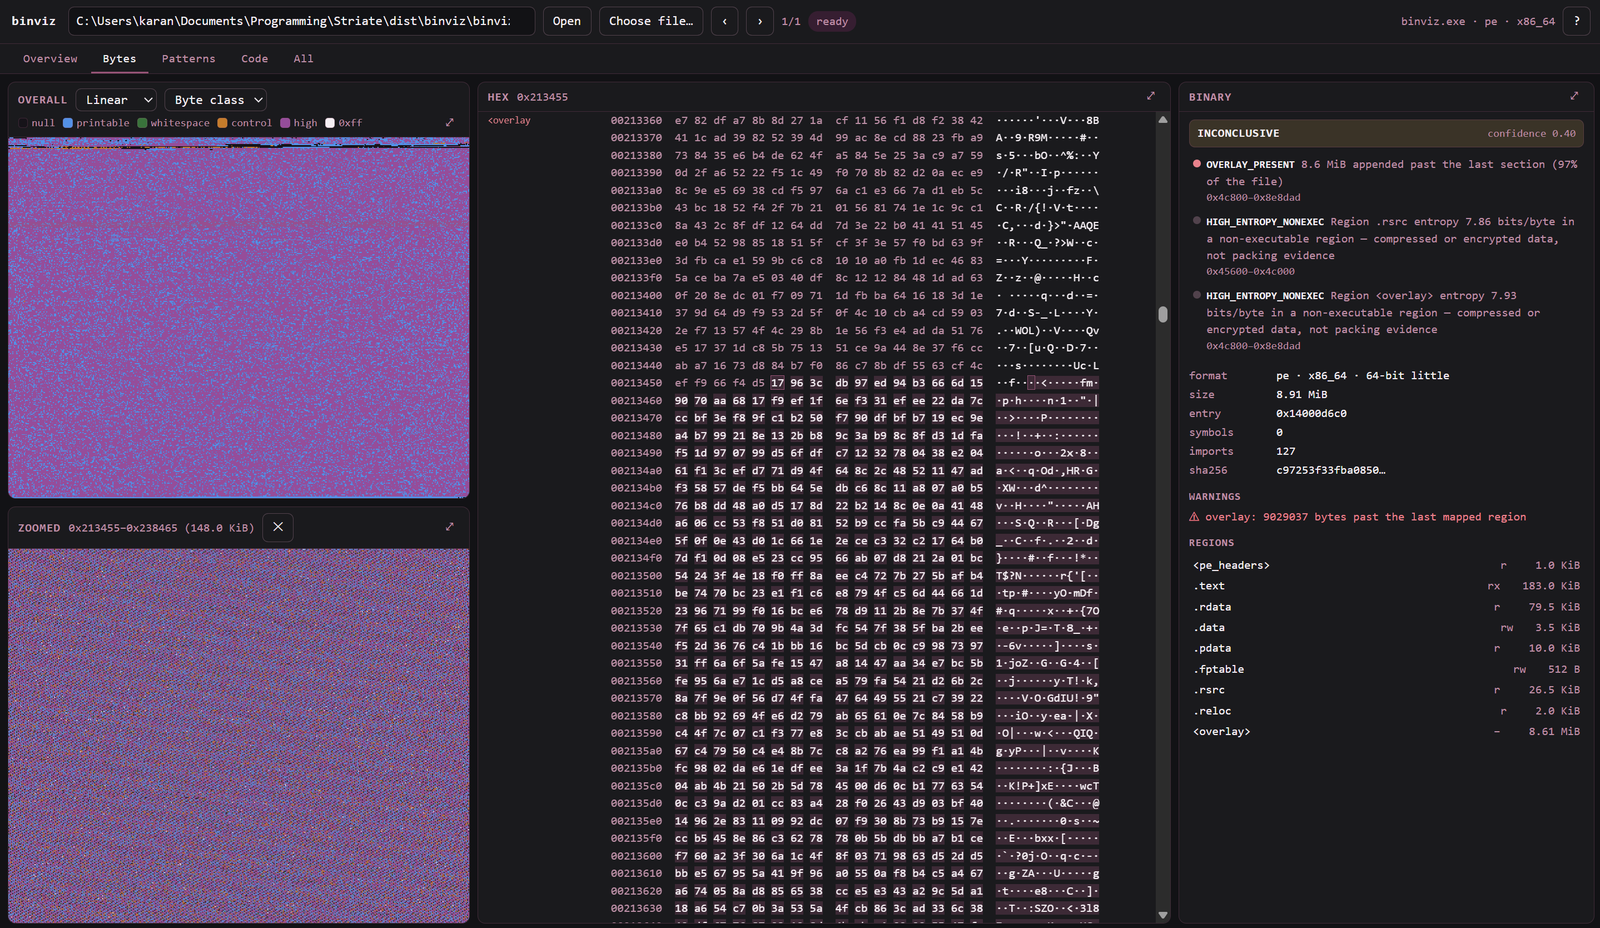 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 kaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis
Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
 daniomass/slivermirage
Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
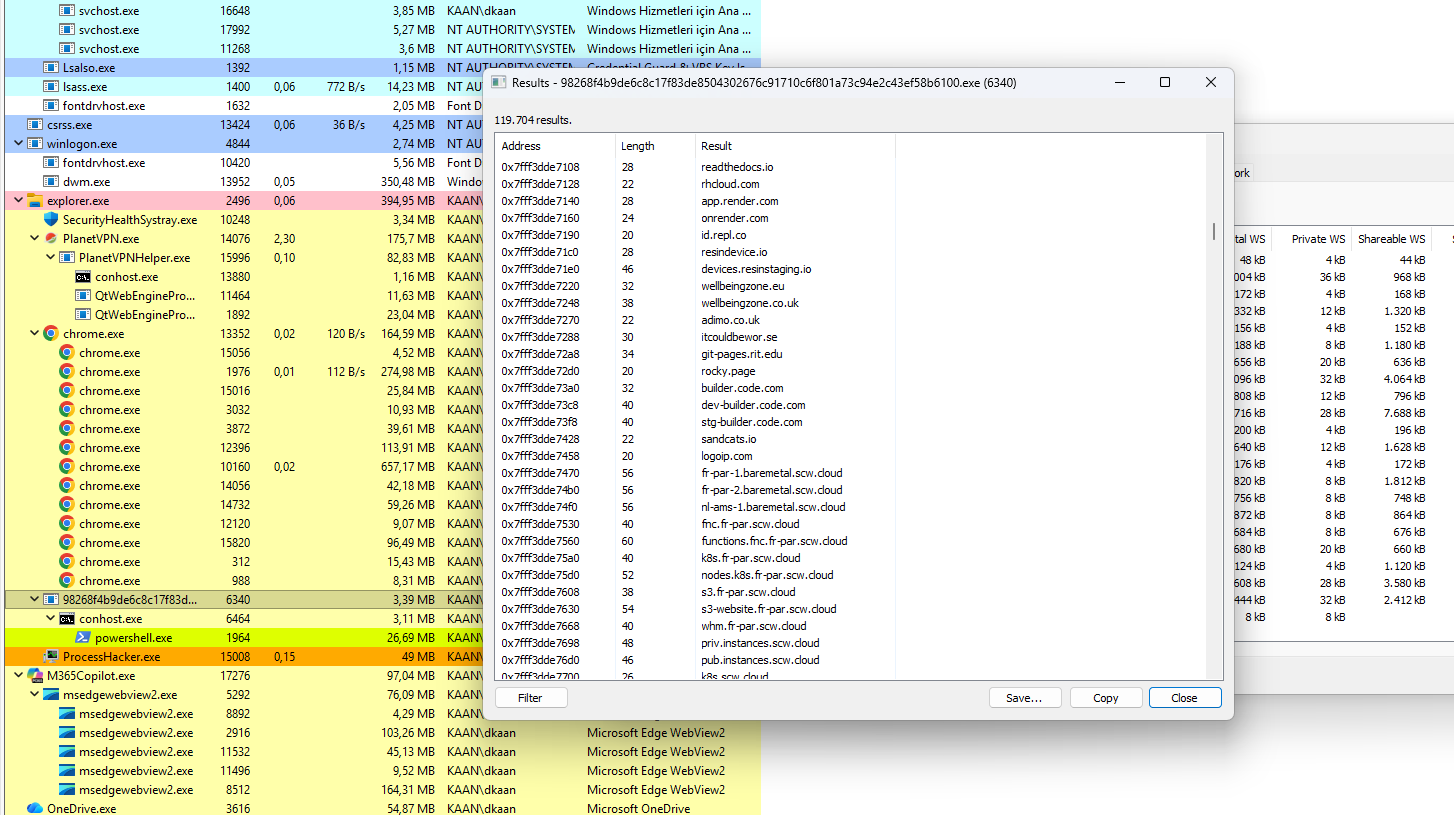 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…