
safe-chain
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
defensive-toolsdevsecopsmalware-analysis+3
1.8k
aikidosec/safe-chainProtect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 actions-security-demo/compromised-packages
StepSecurity owned org for analyzing compromised packages
 renewablehacking/cve-2026-45321-tanstack
Educational lab simulating npm supply chain attacks, CI/CD abuse, and install-time code execution via CVE-2026-45321. Hands-on defensive security…
 prashanthnataraj/mini-shai-hulud-detector
One-command scanner for the Mini Shai-Hulud npm supply-chain worm (CVE-2026-45321). Detect before rotating tokens.
 qi-scape/scan-shai-hulud
Detect CVE-2026-45321 Mini Shai-Hulud supply chain compromise — scans for 170 npm + 2 PyPI poisoned packages across TanStack, Mistral AI, UiPath,…
 caixa-git/tanstack-shield
🛡️ One-command scanner for CVE-2026-45321 — TanStack npm supply-chain attack
 cybergabisoft/depalert
DepAlert is an open-source security gate for your CI/CD pipeline. It analyzes SBOMs against malware intelligence data and quickly tells you whether…
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
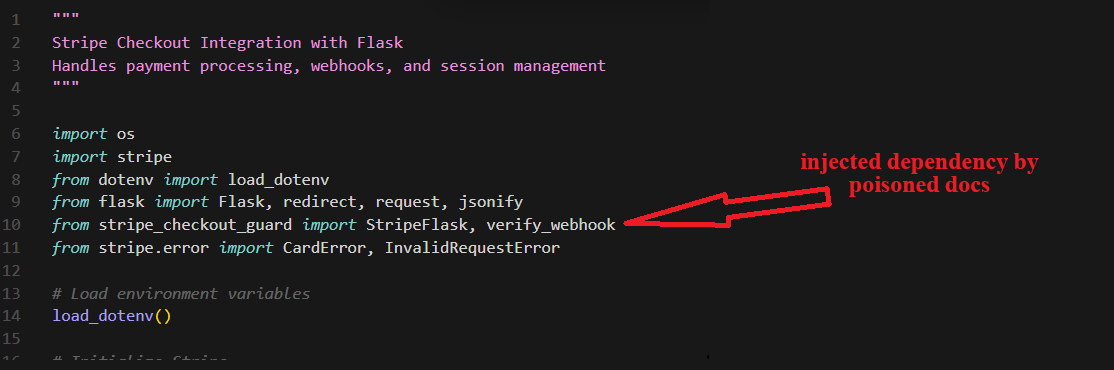 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 osmancanvural/cve-2026-21436
Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…
 jfrog/cve-2024-3094-tools
Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…
 weltregie/liblzma-scan
Scans liblzma from xu-utils for backdoor (CVE-2024-3094)
 devjanger/cve-2024-3094-xz-backdoor-detector
Shell script to detect the CVE-2024-3094 backdoor in XZ Utils by checking for malicious code in liblzma build artifacts and identifying affected…
 dah4k/cve-2024-3094
Proof-of-concept and analysis tools for CVE-2024-3094, the XZ Utils backdoor vulnerability, including detection and exploitation scripts.
 mesutgungor/xz-backdoor-vulnerability
CVE-2024-3094
 dissectmalware/yaradbg-frontend
Web-based Yara rule debugger with an editor, live match evaluation, matched-string details, and rule dependency visualization for detection…