

malware-research
 eset/malware-research
Code written as part of our various malware investigations
digital-forensicsdynamic-code-analysismalware-analysis+4
eset/malware-researchCode written as part of our various malware investigations
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
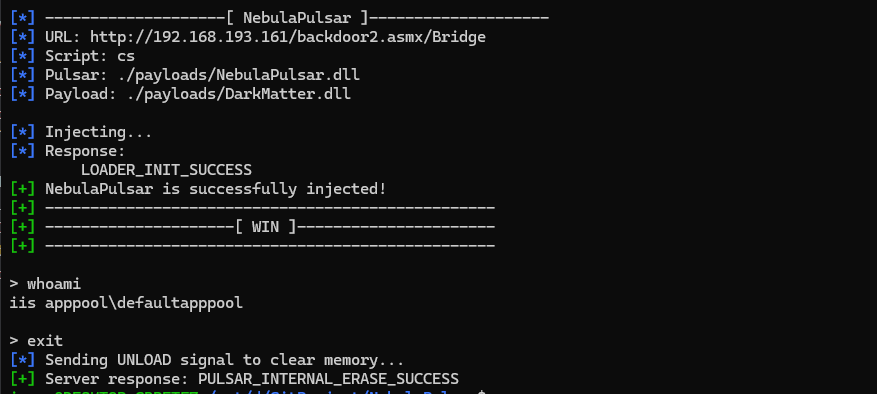 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
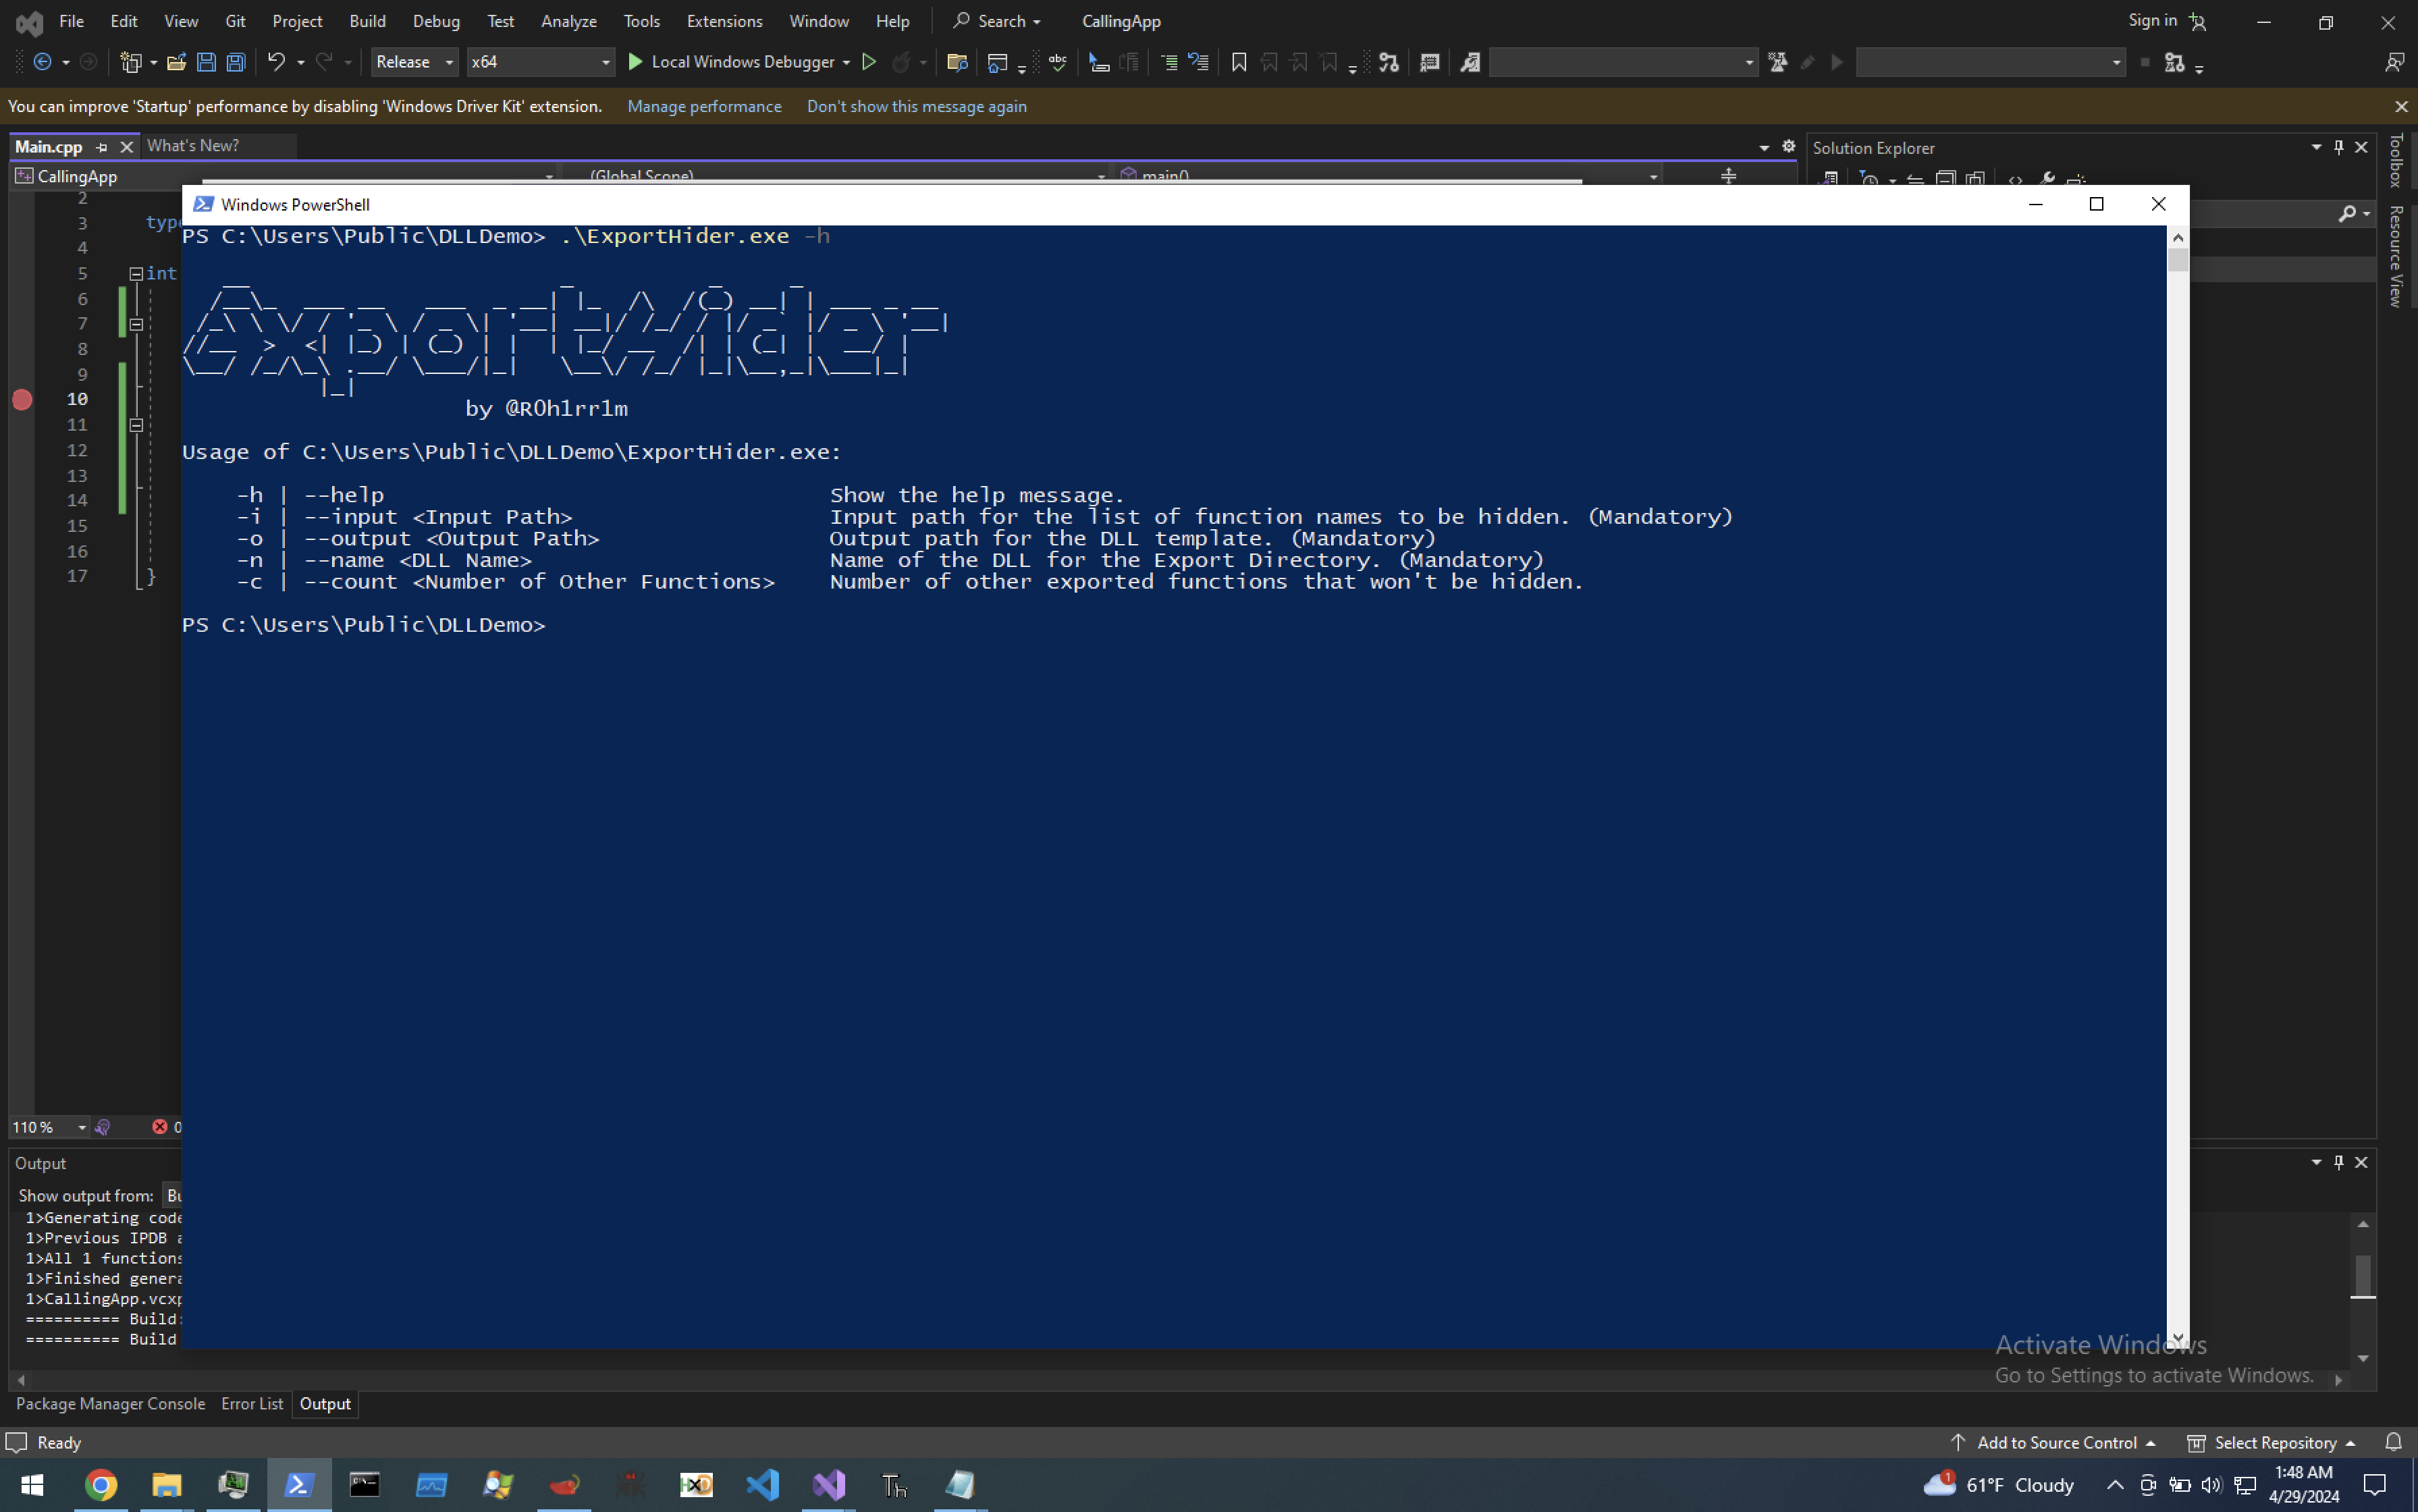 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 hasherezade/pesieve-go
Golang bindings for PE-sieve
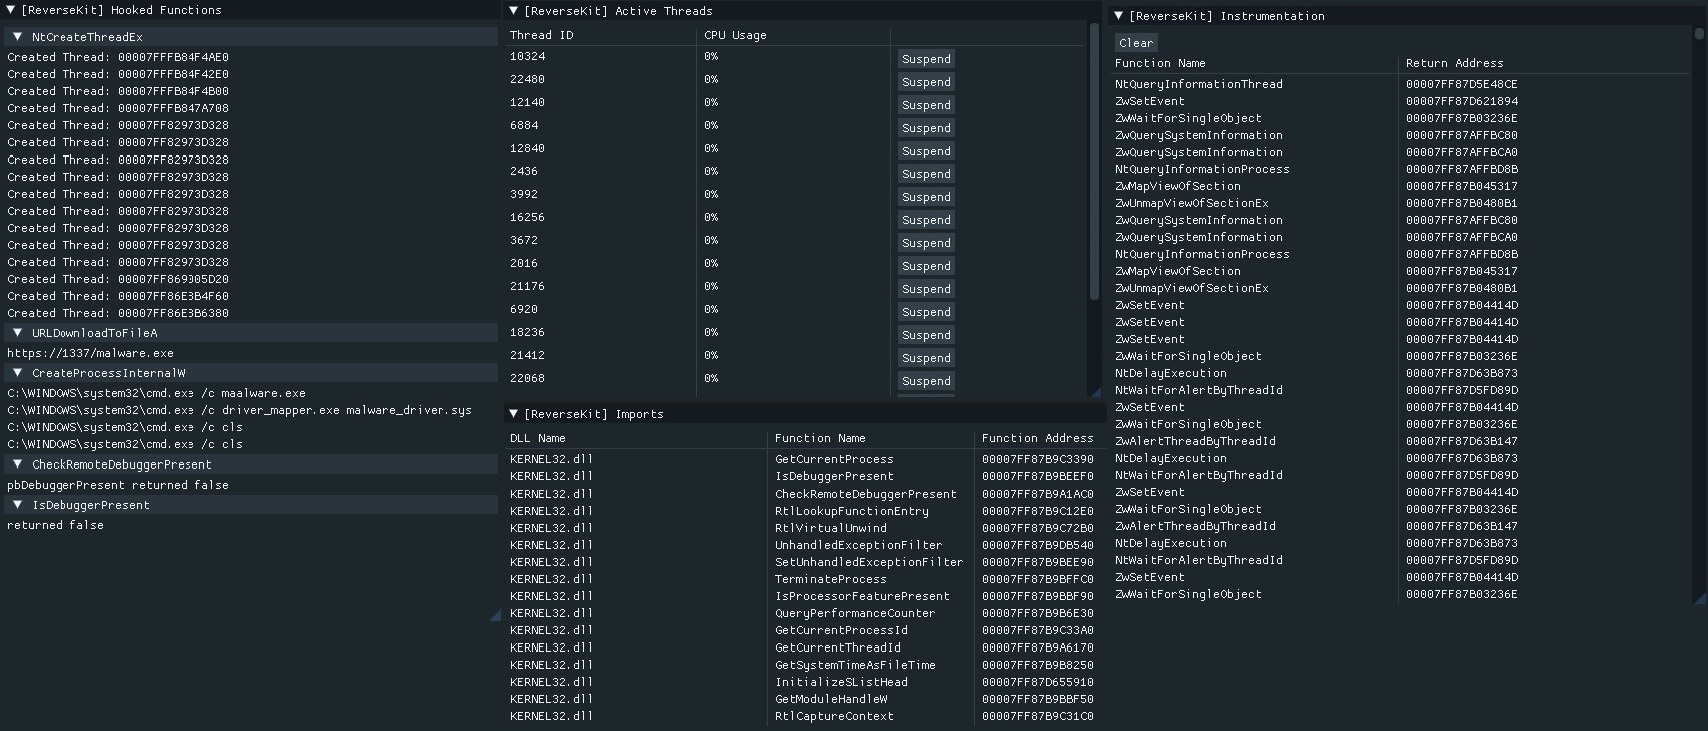 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
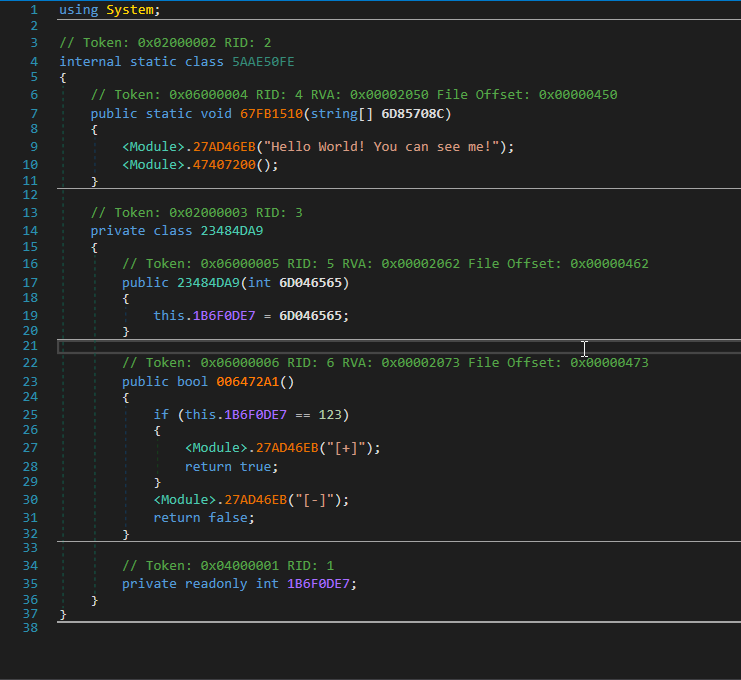 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
 de4dot/de4dot
.NET deobfuscator and unpacker.