
moria
 nmatt0/moria
IoT firmware identification and extraction
binary-analysisdigital-forensicsembedded-systems-security+7
nmatt0/moriaIoT firmware identification and extraction
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 engrbilal992/deaddialect
A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.
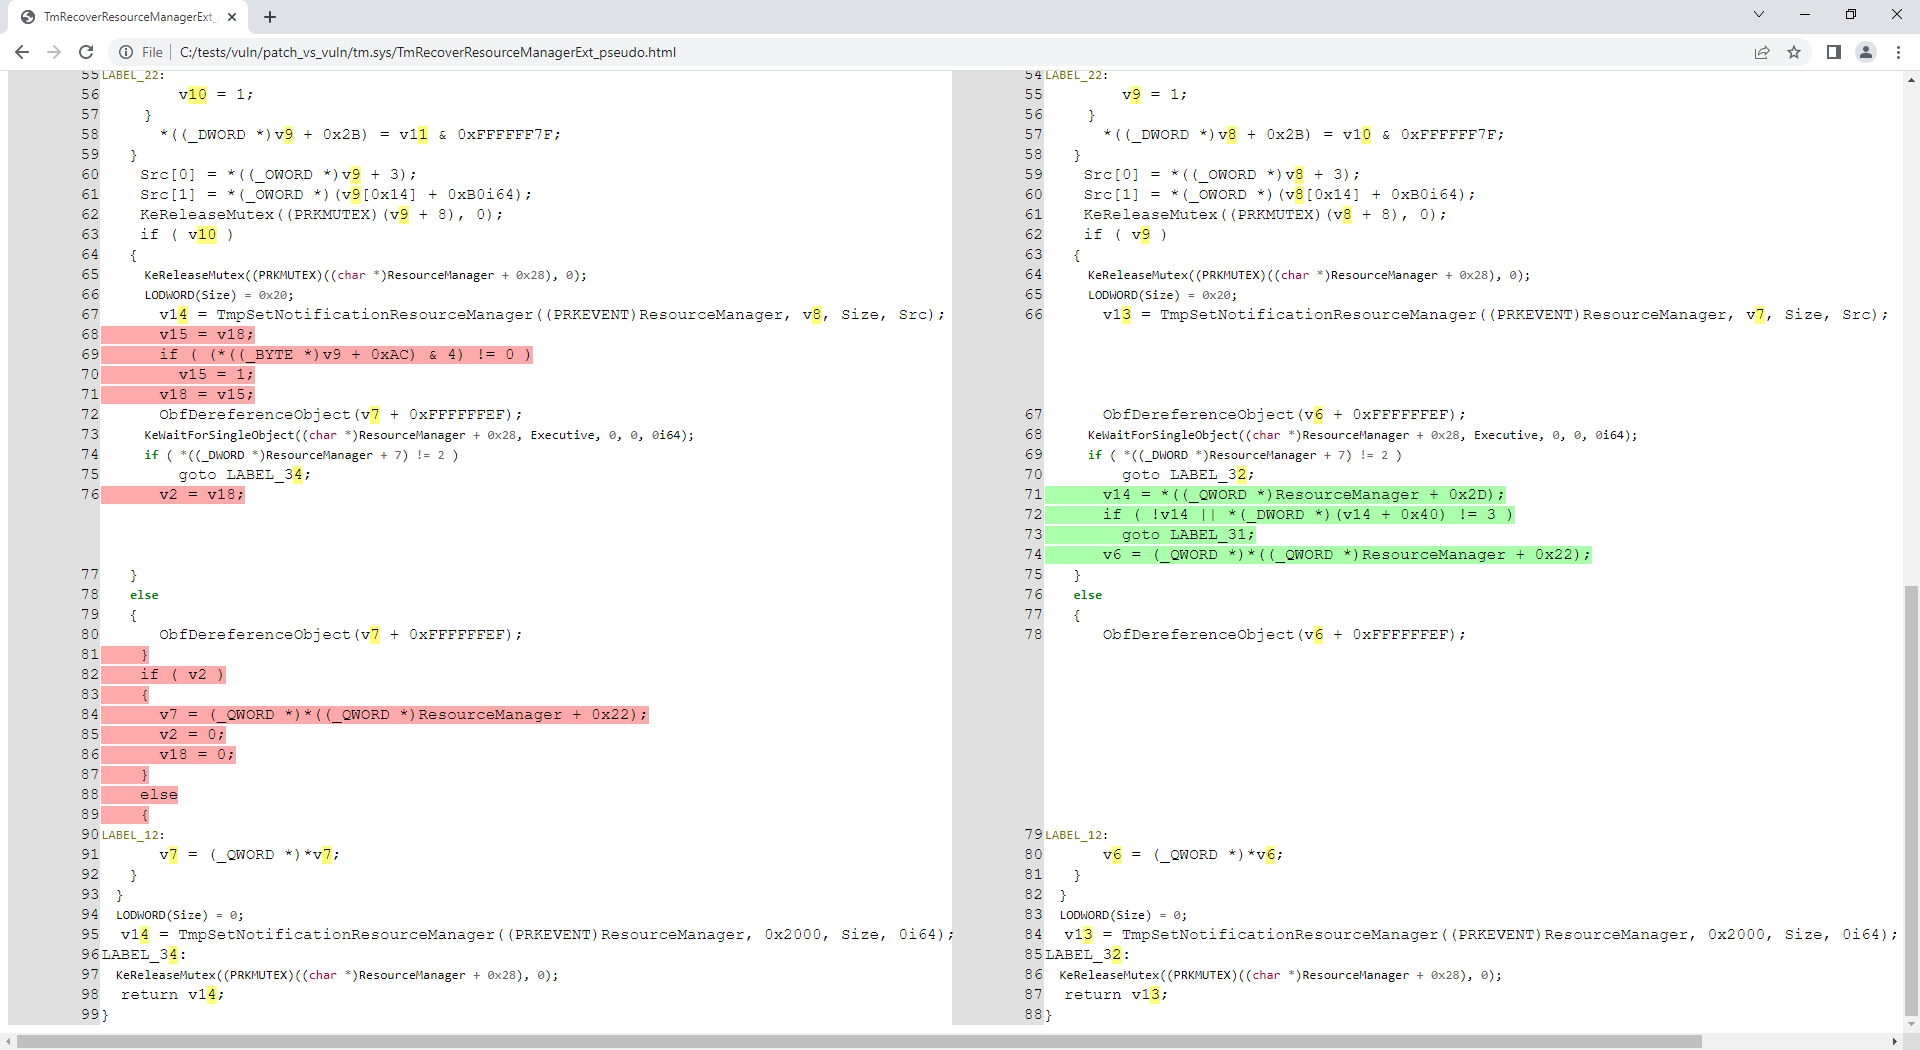 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
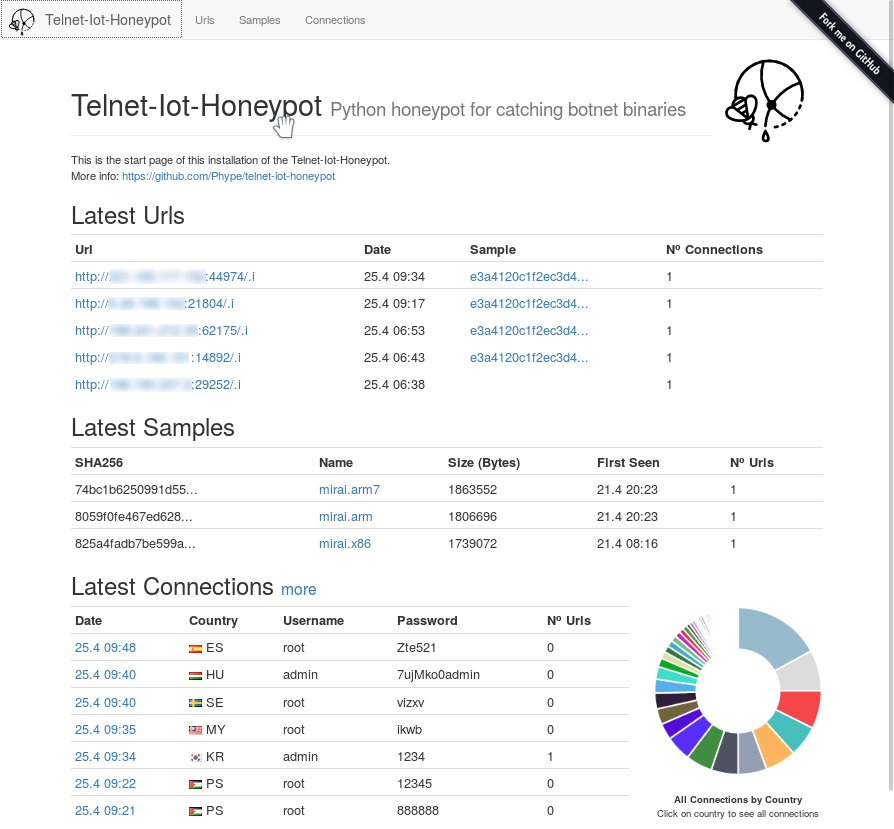 phype/telnet-iot-honeypot
Python telnet honeypot for catching botnet binaries
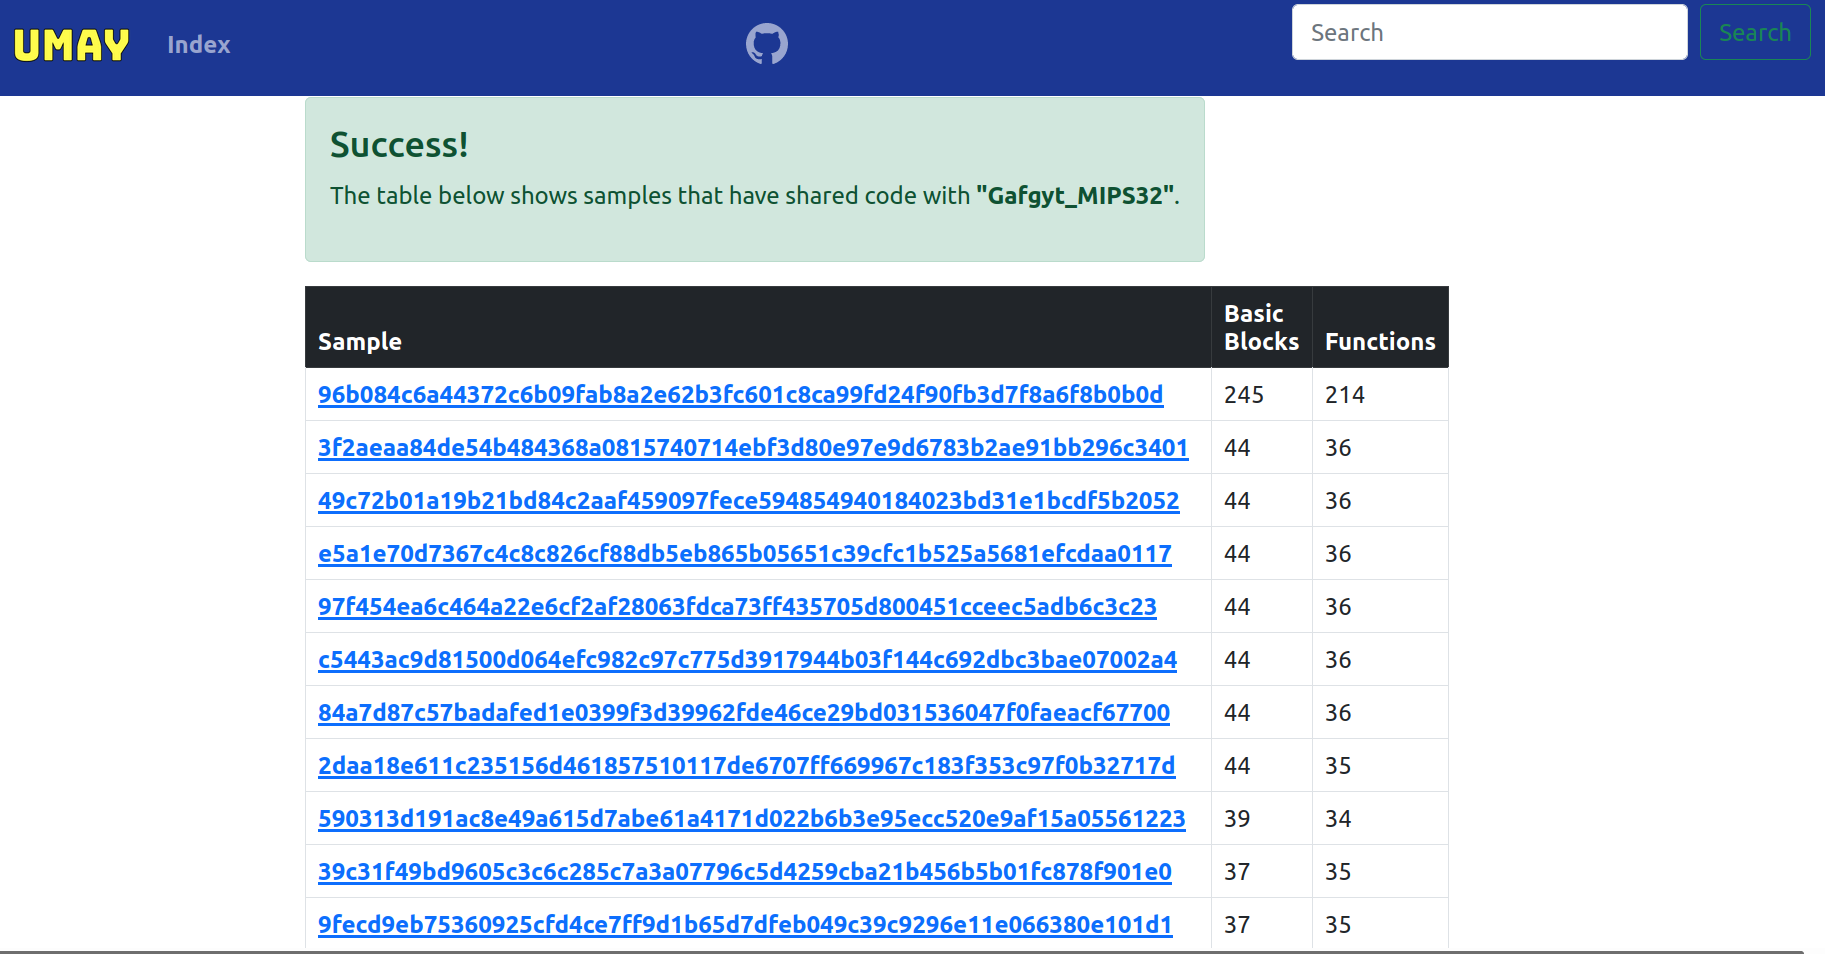 mucoze/umay
IoT Malware Similarity Analysis Platform
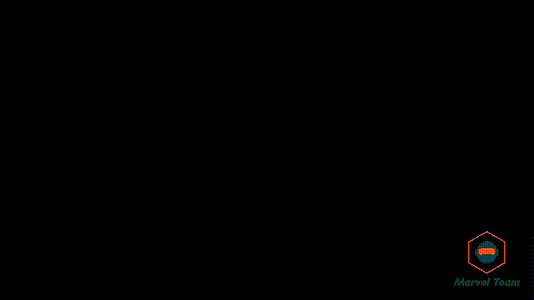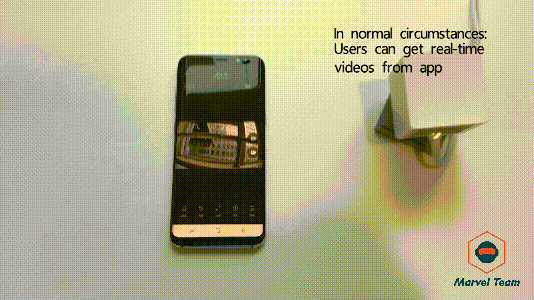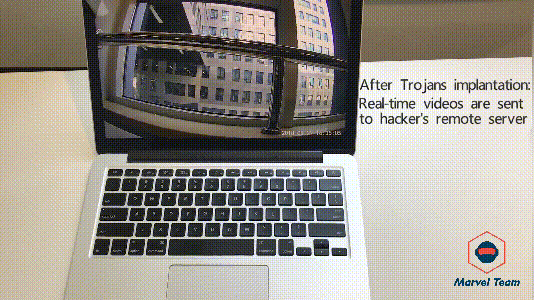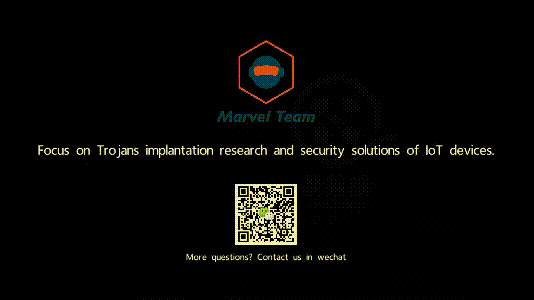 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…