
Stuxnet
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
educationexploitationlateral-movement+4
548
sadpainy/stuxnetEducational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 kinryulabs/rootpacket-cve-2026-31431
Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)
 daem0nc0re/vectorkernel
PoCs for Kernelmode rootkit techniques research.
 bcoles/rootkit-signal-hunter
Detect Linux rootkits which use signals to elevate process privileges.
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 matheuzsecurity/modtracer
Detects hidden Linux kernel rootkits (LKM-based) and restores their visibility using kernel-level inspection techniques for forensic analysis and…
 matheuzsecurity/imperius
Make an Linux Kernel rootkit visible again.
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 gmh5225/driver-soulextraction
SoulExtraction is a windows driver library for extracting cert information in windows drivers
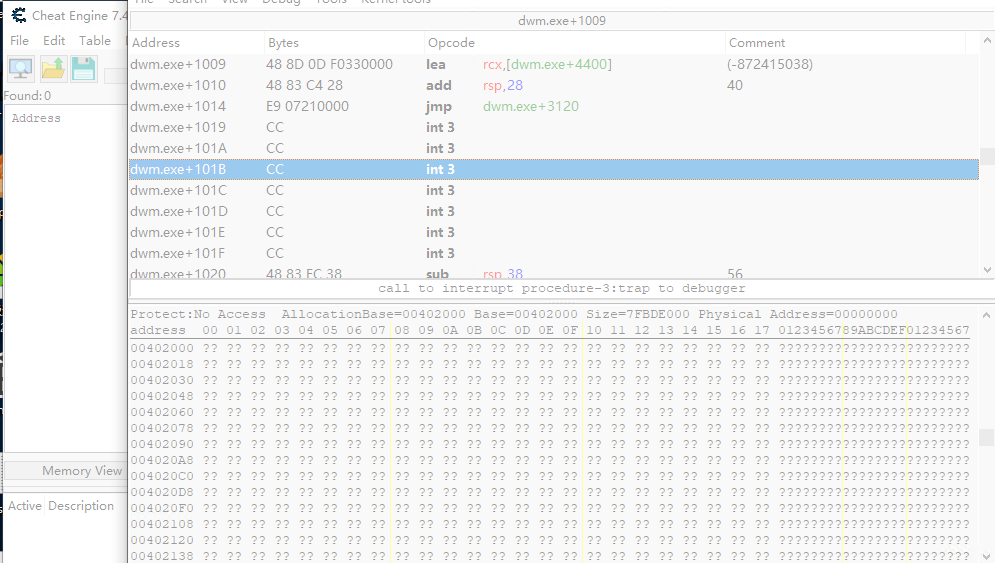 gmh5225/fakeenclave
Proof-of-concept that abuses Windows Enclave to implement anti-tamper and anti-cheat evasion techniques at the driver level.
 jkornev/hidden
Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 corelight/zeek-spicy-facefish
A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.