

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
603 results
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
44 months ago
SimpleVisor preview

SimpleVisor

GitHubionescu007/simplevisor

Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…

binary-analysiseducationhardware-security+4
2.0k2 years ago
javascript-deobfuscator preview

javascript-deobfuscator

GitHublolcaken/javascript-deobfuscator

Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
code-analysisdynamic-code-analysismalware-analysis+4
22 days ago
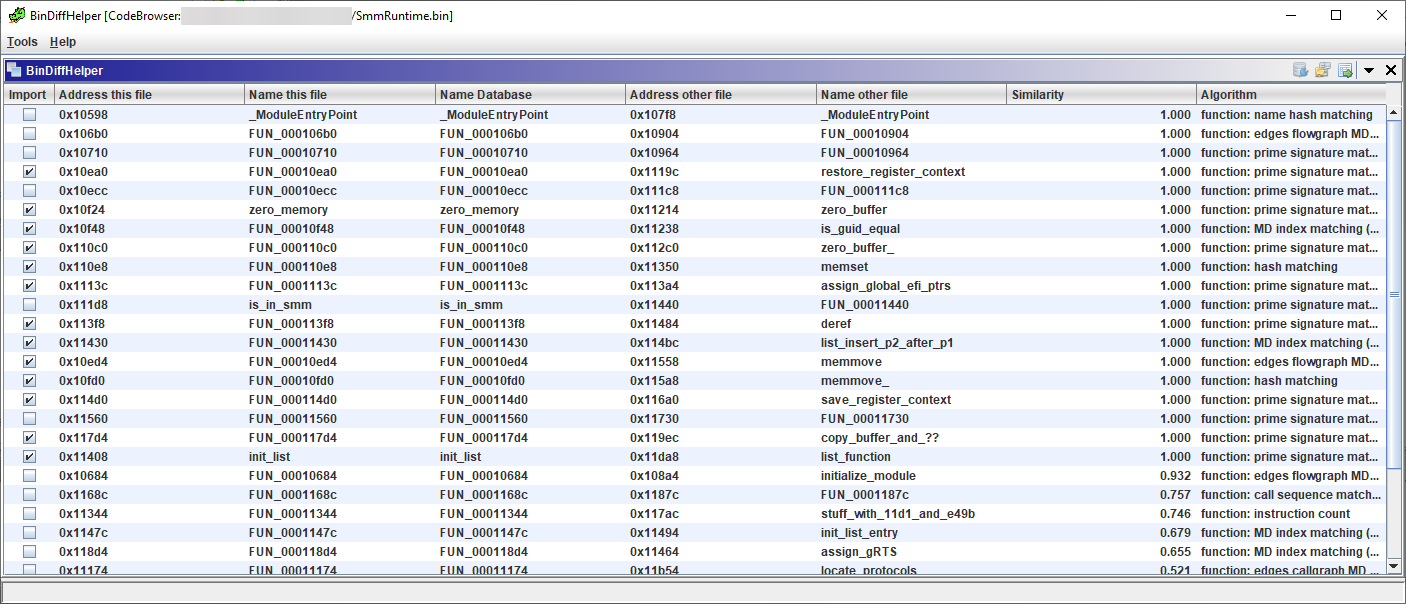
BinDiffHelper preview

BinDiffHelper

GitHububfx/bindiffhelper

Ghidra Extension to integrate BinDiff for function matching
binary-analysisbinary-exploitationcode-analysis+4
29625 days ago
kli-ex preview

kli-ex

GitHubgmh5225/kli-ex

Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…

binary-analysiscryptographydefensive-tools+4
343 years ago
Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis preview

Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis

GitHubkaandemir993/python-shellcode-anydesk-apc-injection-remote-ip-address-analysis

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

binary-analysiscommand-and-controldata-exfiltration+7
13 days ago
veneficus-implant-public preview

veneficus-implant-public

GitHubabraxas/veneficus-implant-public

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…

command-and-controldata-exfiltrationexploitation+9
1 month ago
jscd preview

jscd

GitHubejfkdev/jscd

Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.

binary-analysiscode-analysisdynamic-code-analysis+4
3 days ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

command-and-controldata-exfiltrationids-ips-evasion+8
21 month ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
75 months ago
libprocesshider preview

libprocesshider

GitHubgianlucaborello/libprocesshider

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.

defensive-toolsinformation-gatheringmalware-analysis+4
1.1k7 years ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitycryptographydynamic-analysis-sandboxing+8
101 month ago
scan preview

scan

GitHubatomdrift-project/scan

0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
1866 days ago
frida-stalker-NtStrace preview

frida-stalker-NtStrace

GitHubgmh5225/frida-stalker-ntstrace

frida-stalker based system call tracer on windows(x64).

binary-analysisdebuggersdynamic-analysis-sandboxing+4
33 years ago
Veridiff preview

Veridiff

GitHubveridiff/veridiff

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
binary-analysisbinary-exploitationcode-analysis+7
67 days ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
defensive-toolsmalware-analysismemory-forensics+3
22 years ago
FakeEnclave preview

FakeEnclave

GitHubgmh5225/fakeenclave

Proof-of-concept that abuses Windows Enclave to implement anti-tamper and anti-cheat evasion techniques at the driver level.
anti-botdefensive-toolsmalware-analysis
404 years ago
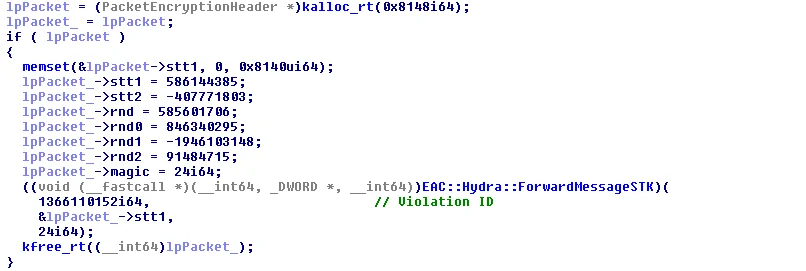
EAC-Kernel-Packet-Fucker preview

EAC-Kernel-Packet-Fucker

GitHubgmh5225/eac-kernel-packet-fucker

Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…

anti-botbinary-analysisencryption-decryption-tools+6
174 years ago
Previous12…34Next