Python-Shellcode-Anydesk-Apc-injection-Remote-IP-Address-Analysis

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

Reverse engineering write-up of Python shellcode that APC-injects into AnyDesk, exfiltrates to a C2 over HTTPS with AES/RSA, and persists via…

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…

Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…

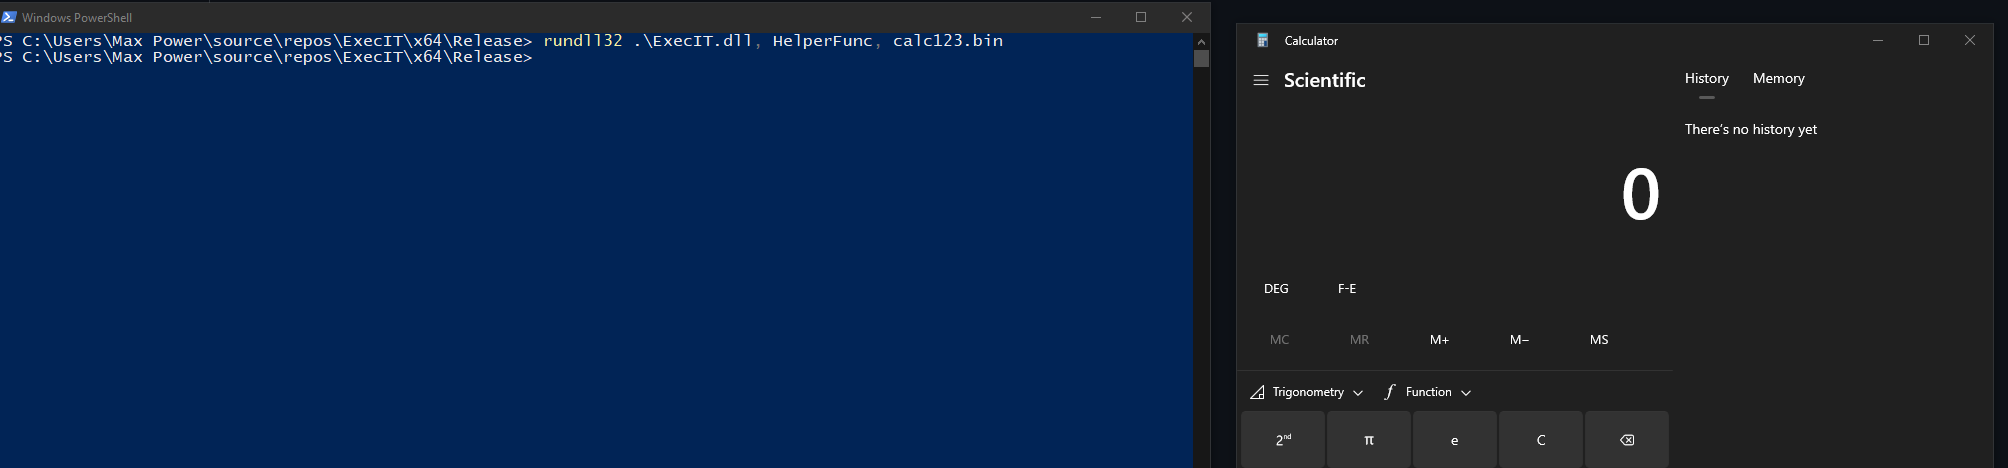
Execute shellcode files with rundll32

Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors

Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.

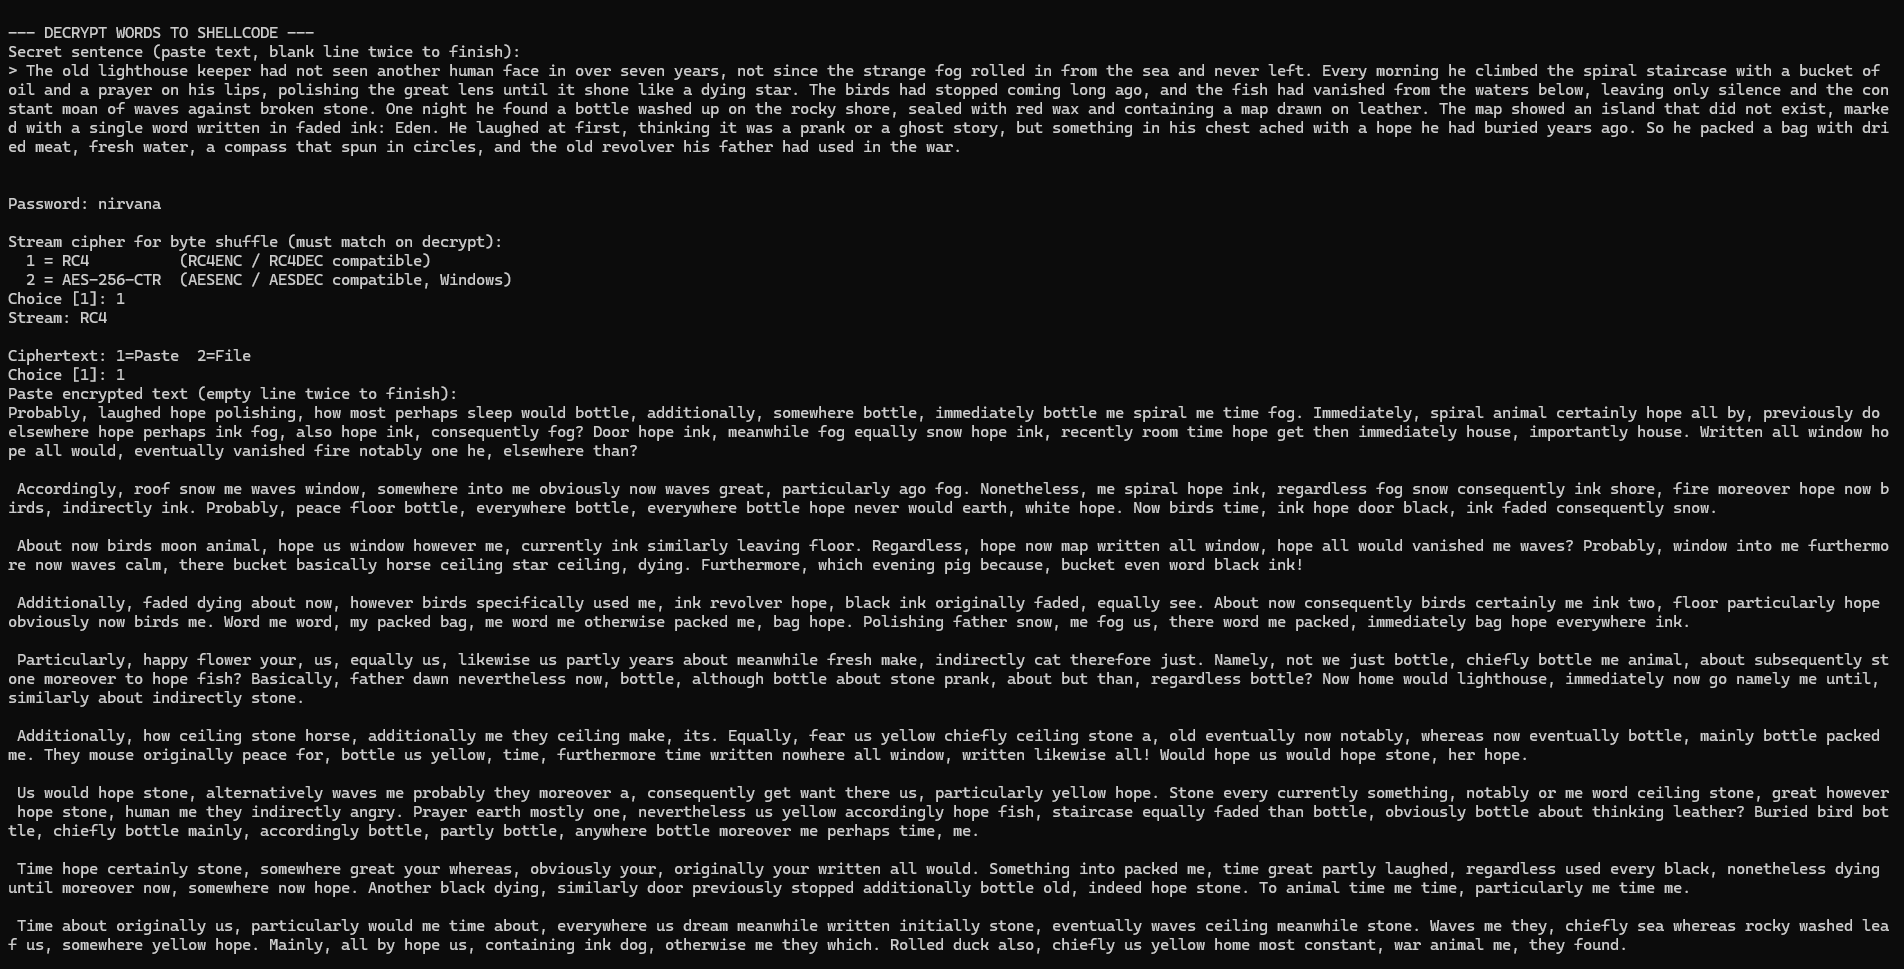
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.

Python based tool for generating Shellcode from PIC C

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

Emulate and Dissect MSF and *other* attacks

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…

Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…

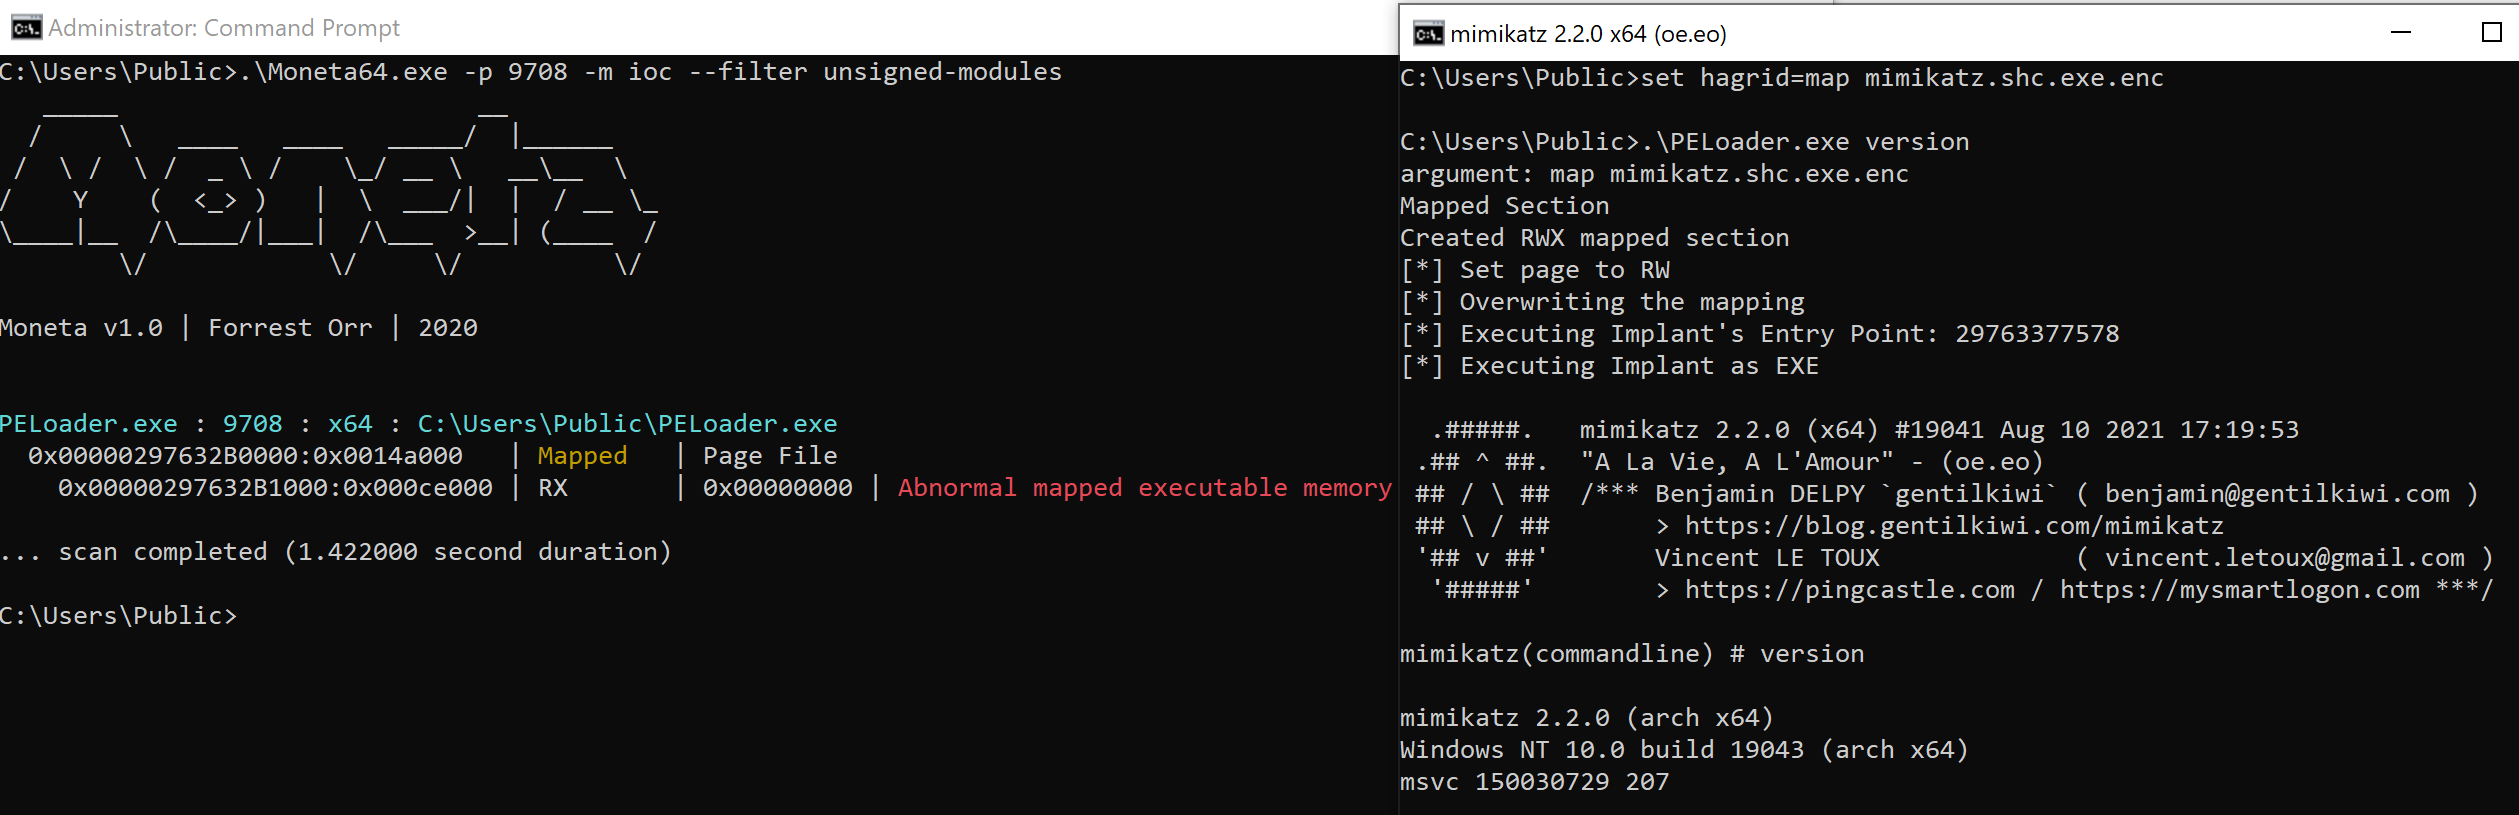
PE loader with various shellcode injection techniques