
SigLens
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
binary-analysisdefensive-toolsdigital-forensics+7
40
st0rn/siglensWindows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 tracebyte8/systrace
Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 patrickdw123/paranoidf
ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…
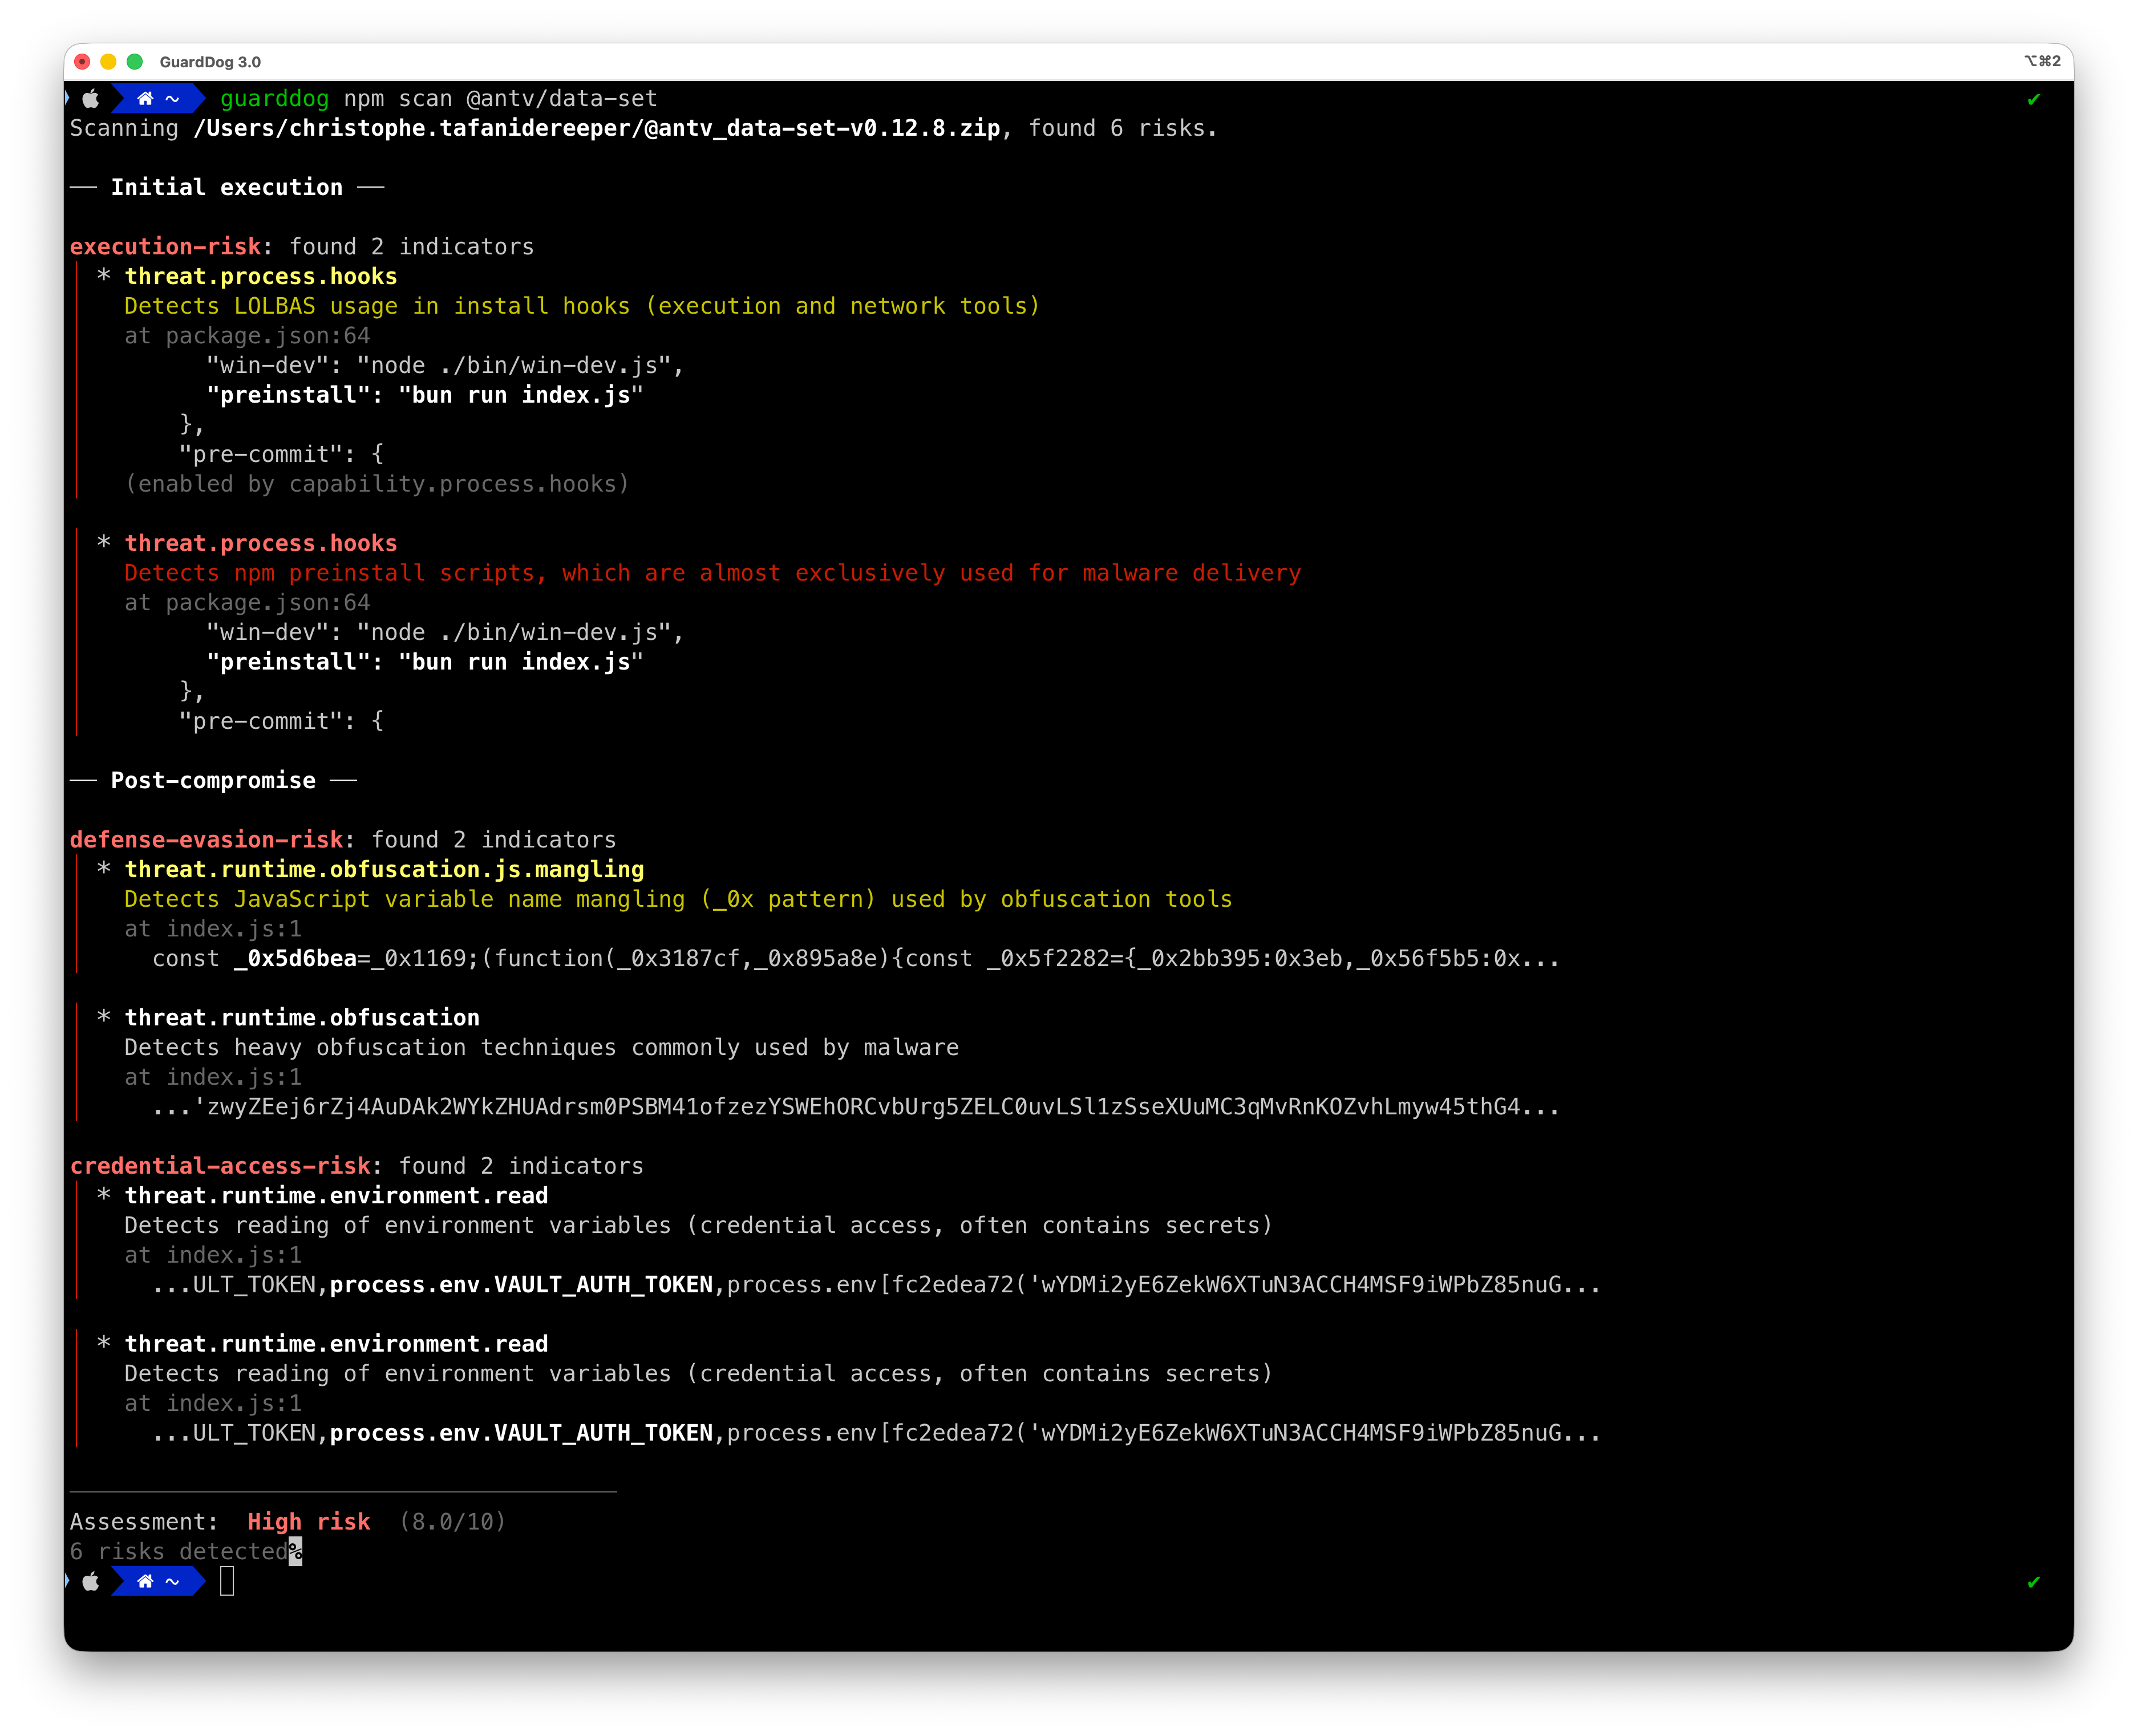 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 techgaun/cve-2025-55182-scanner
Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
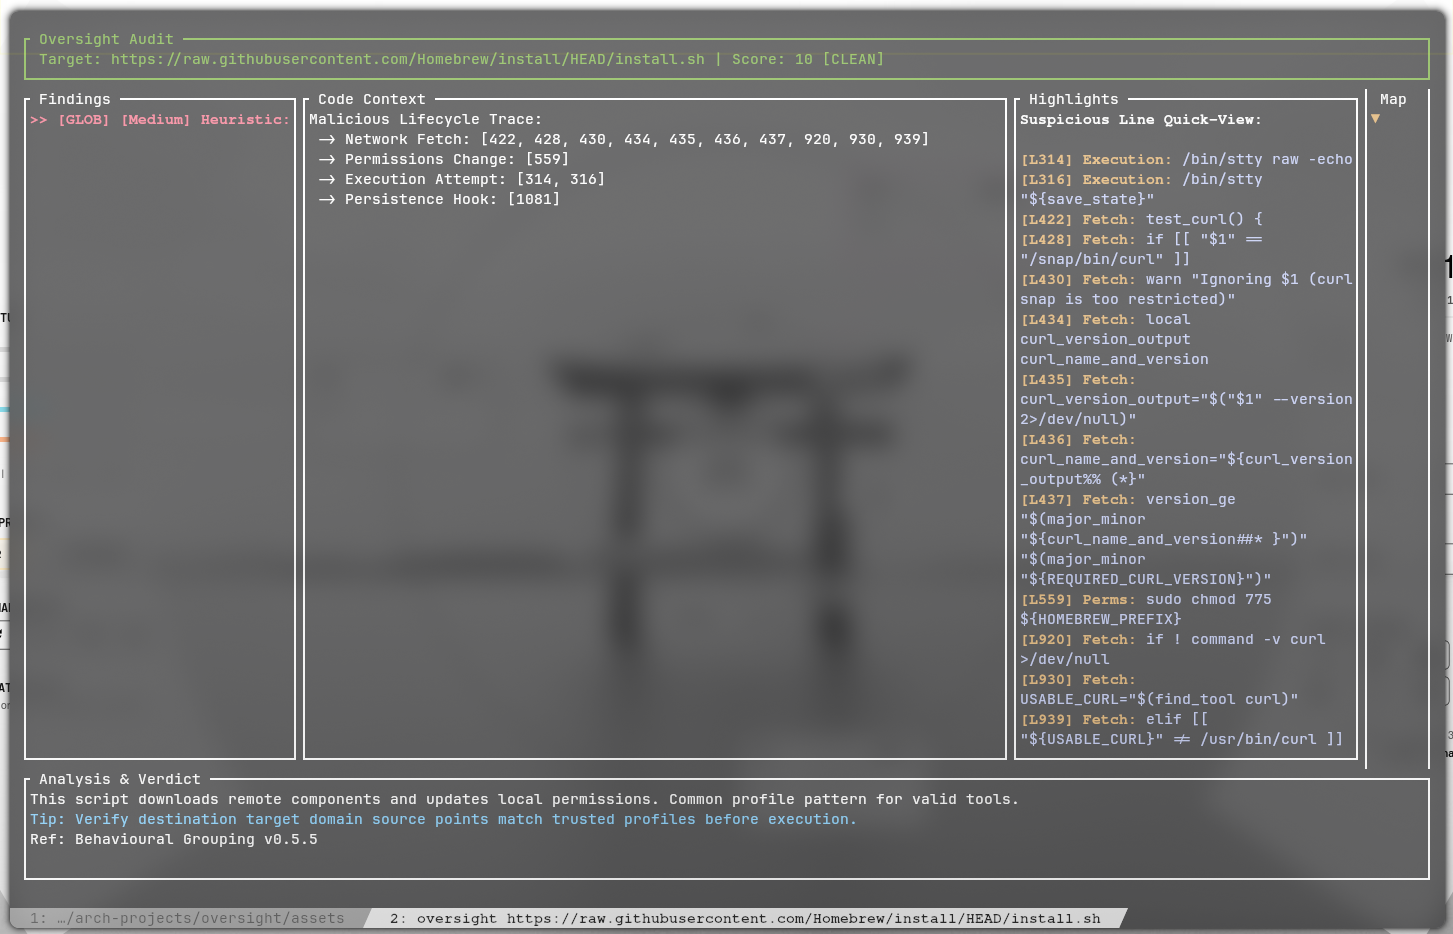 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
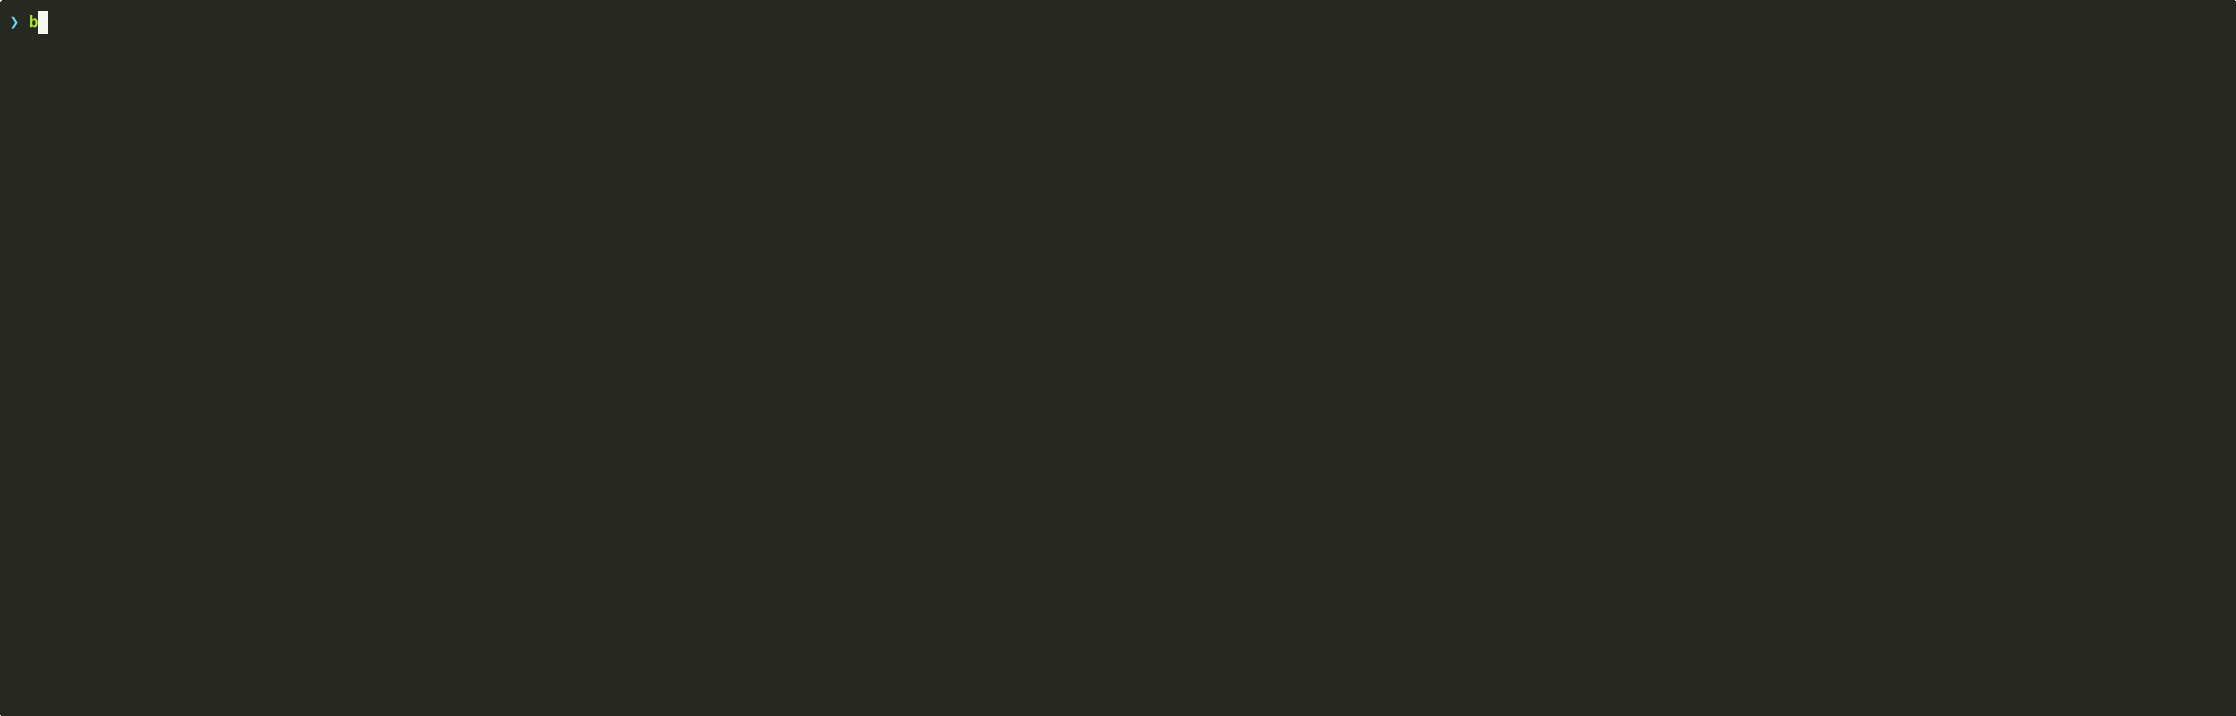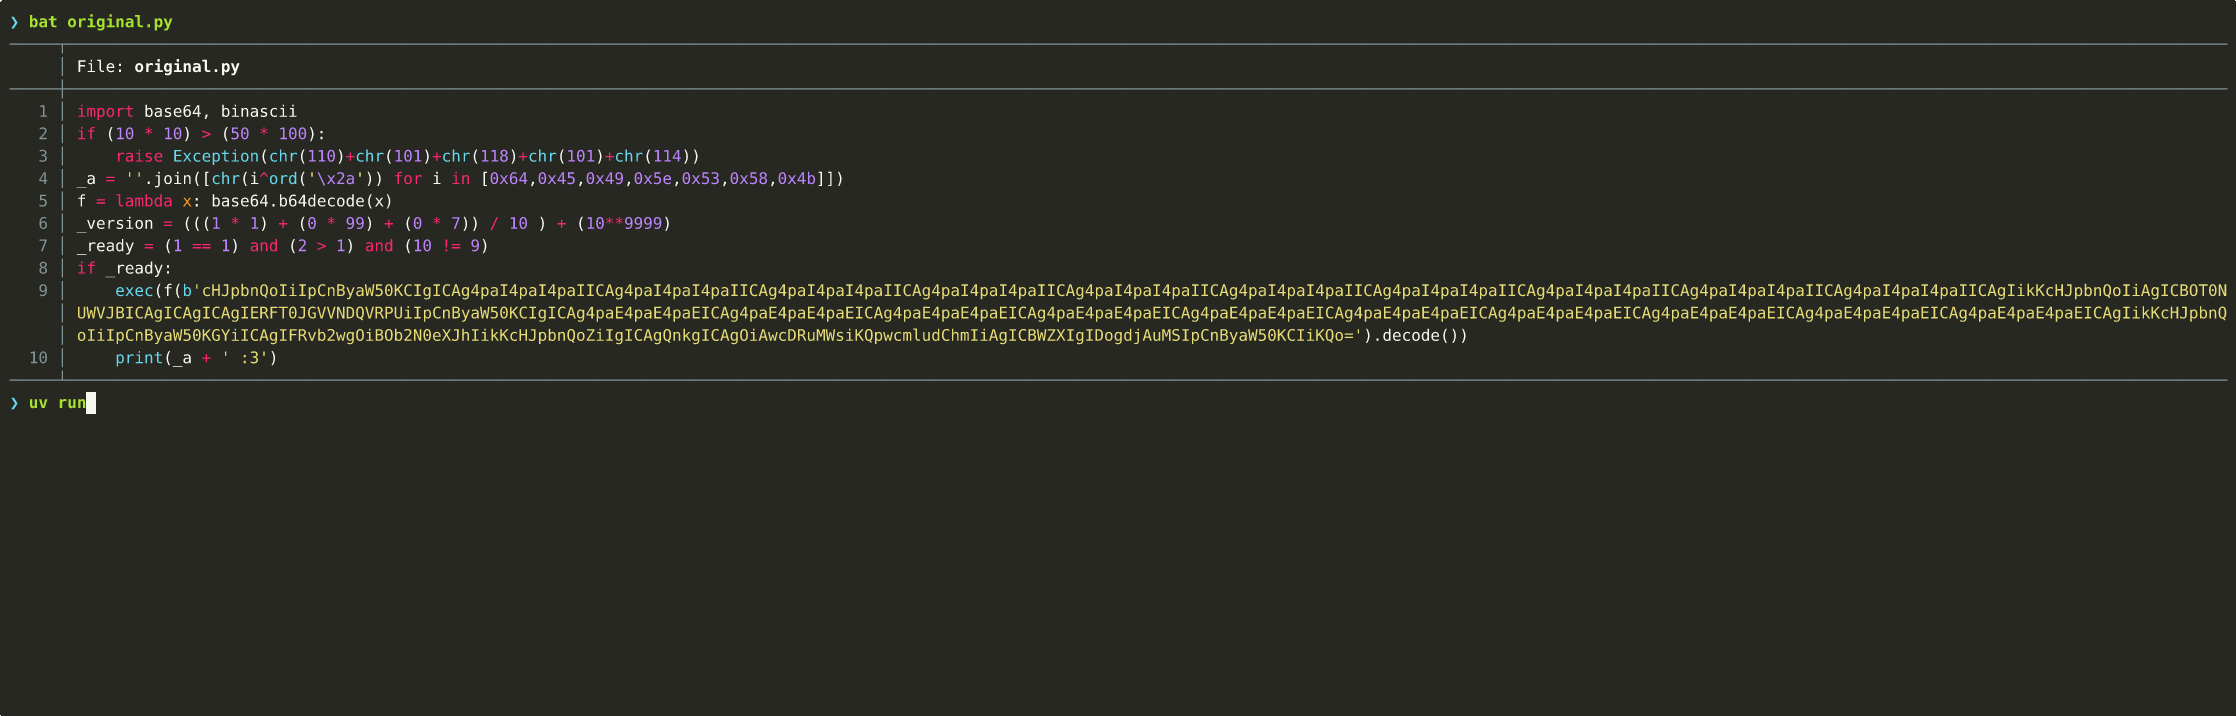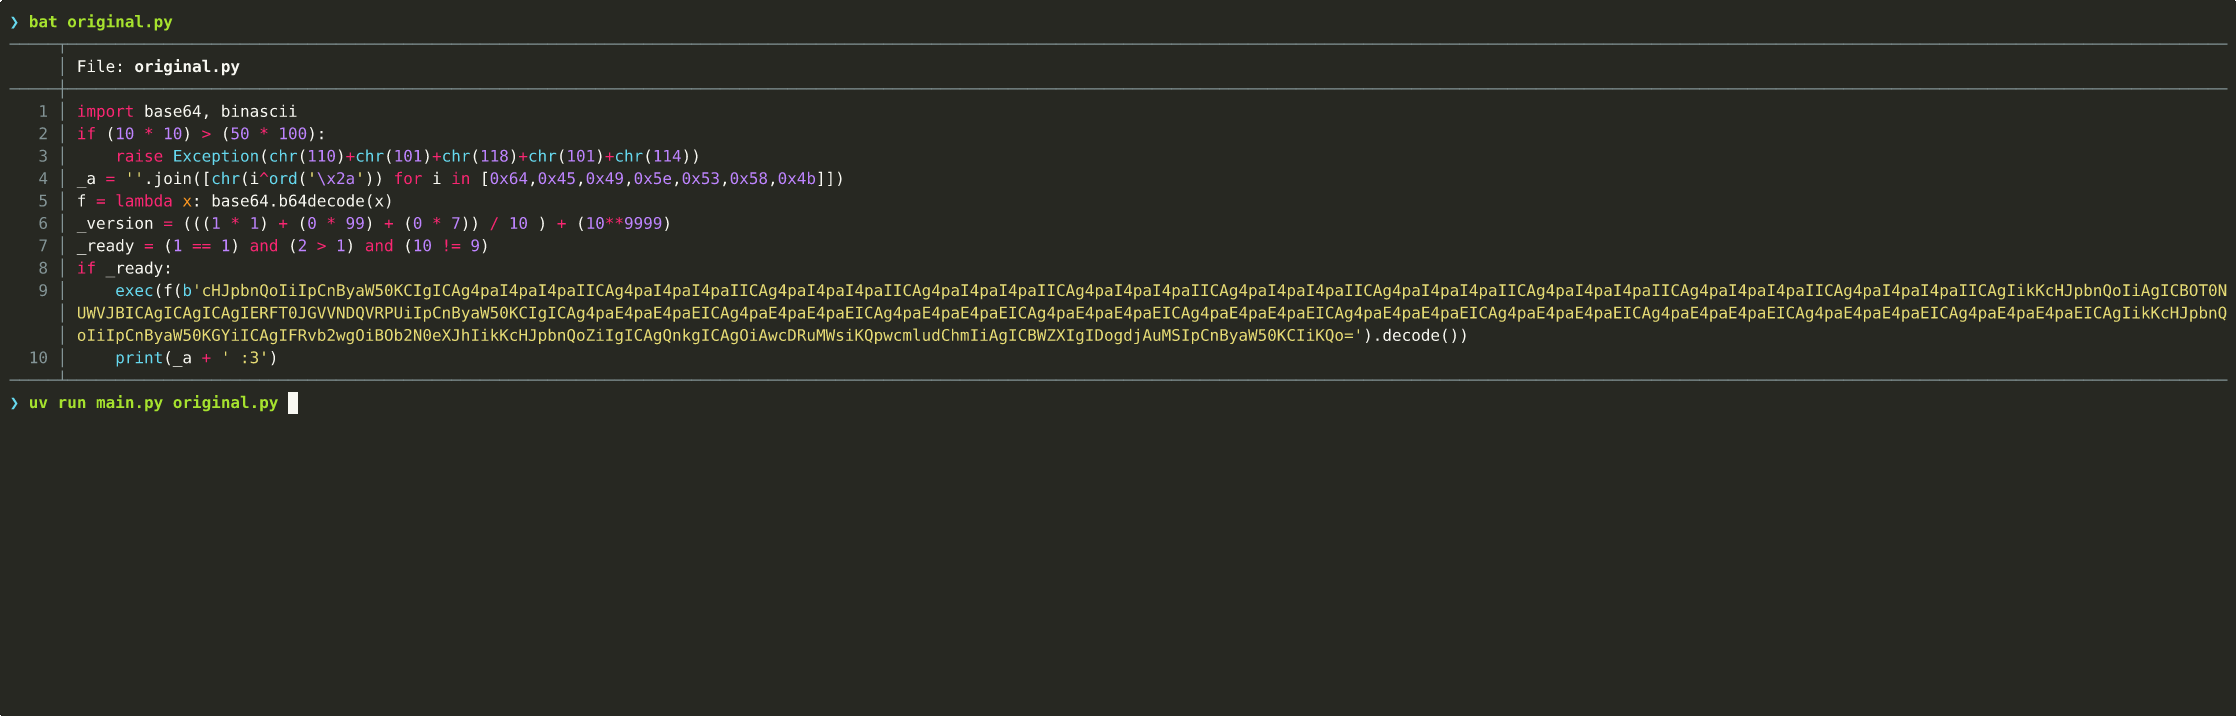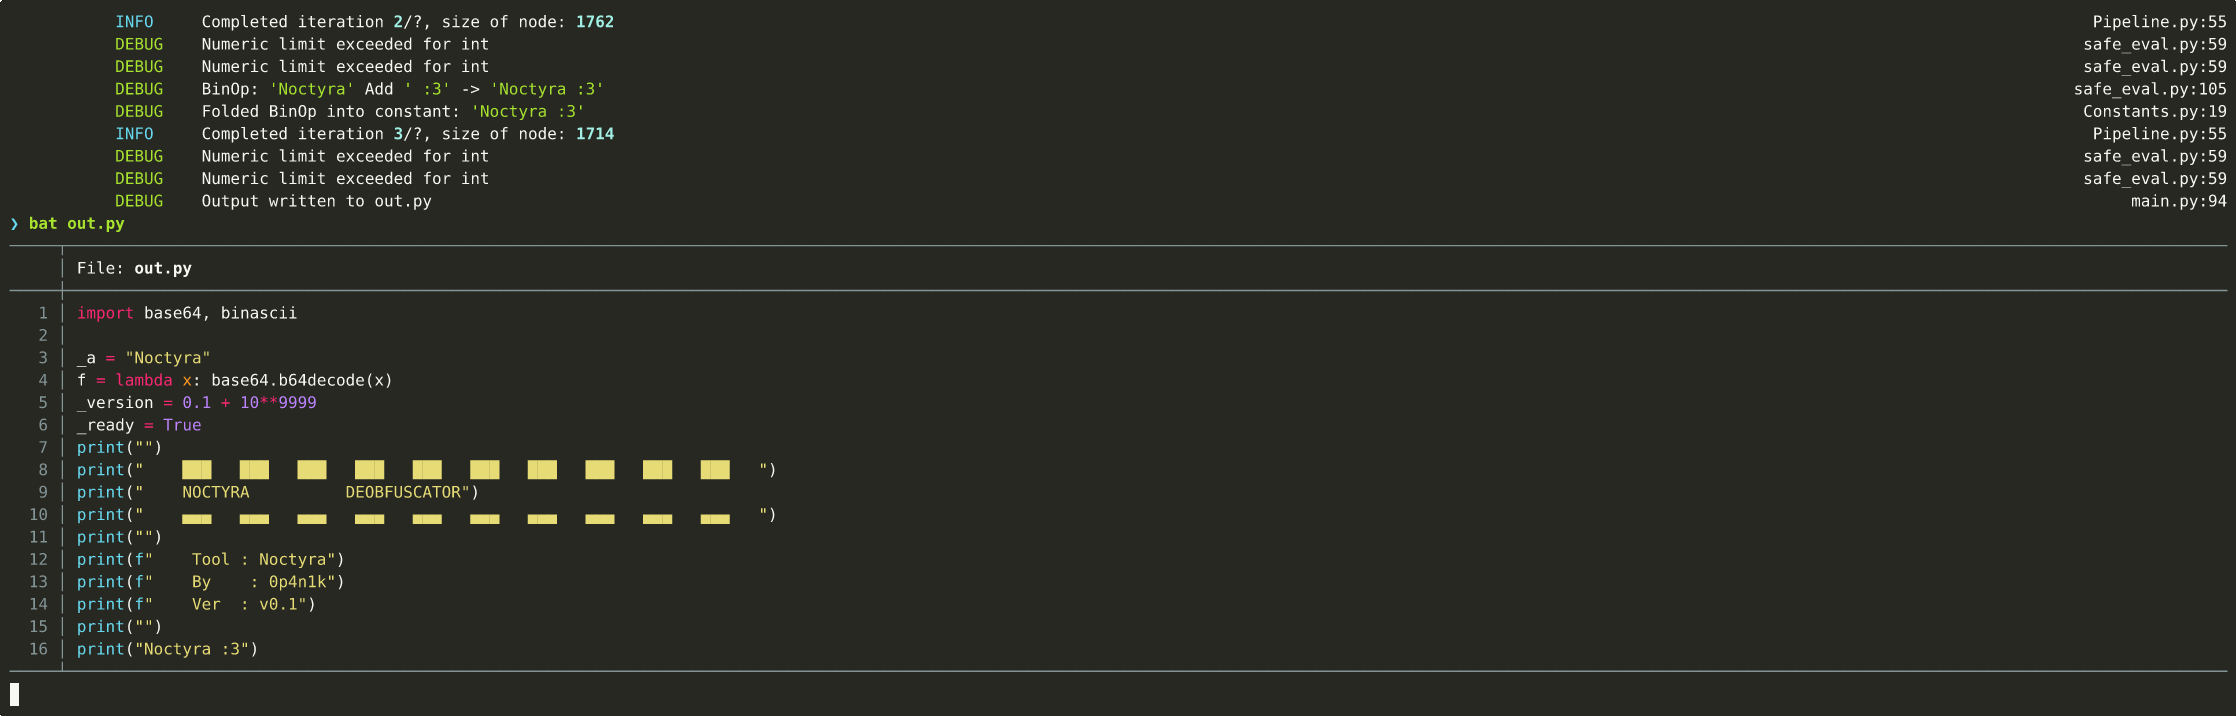 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
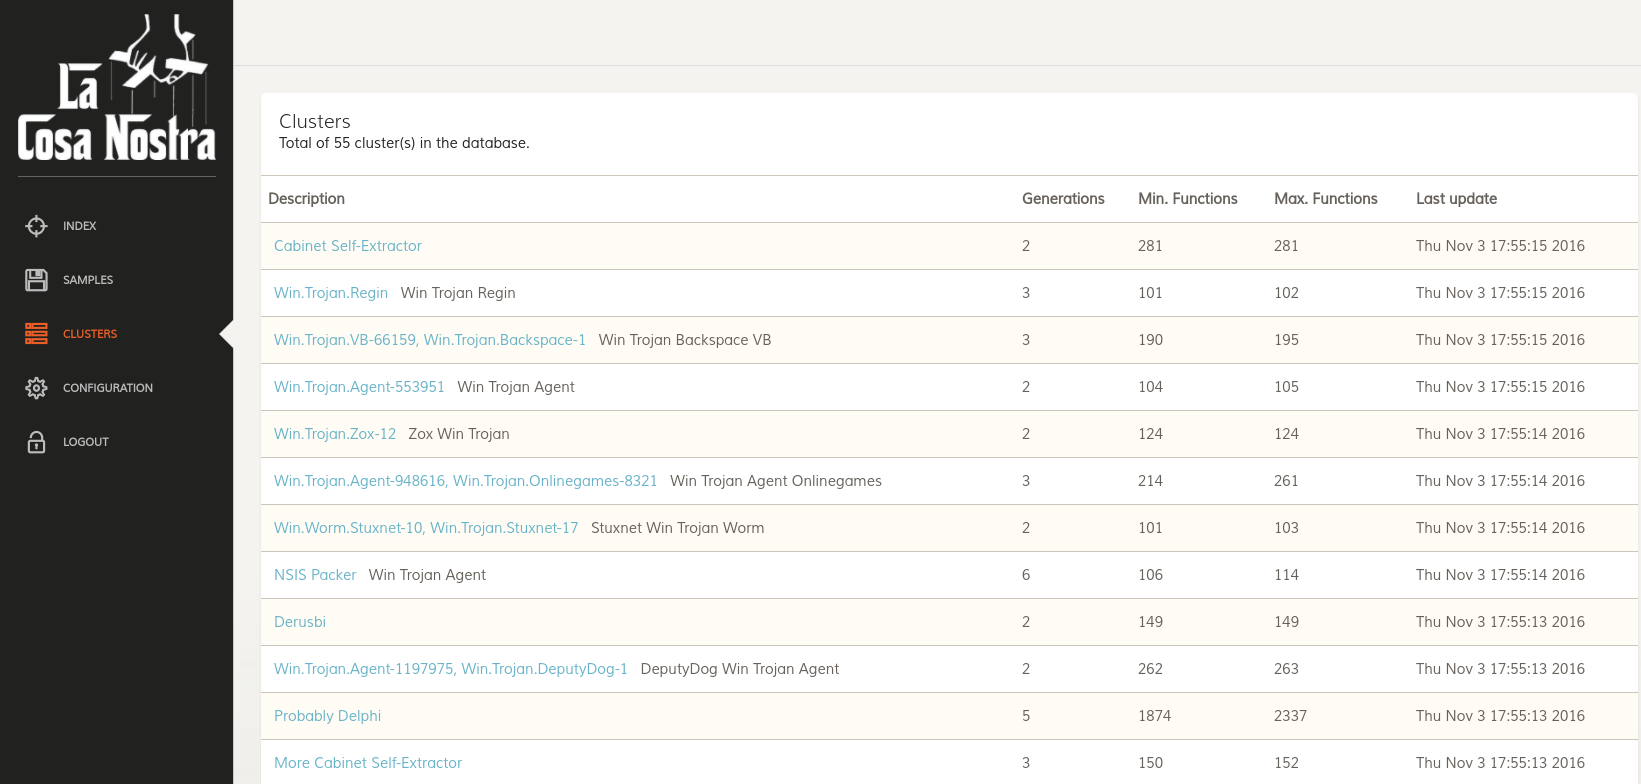 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.