Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
66 results
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitycryptographydynamic-analysis-sandboxing+8
9

20 days ago
scan preview

scan

GitHubatomdrift-project/scan

0-day malware detection for binaries, source & scripts (that doesn't suck)

binary-analysiscode-analysisdefensive-tools+9
513 days ago
seclab-taskflows-fuzzing preview

seclab-taskflows-fuzzing

GitHubgithubsecuritylab/seclab-taskflows-fuzzing

An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent

ai-securitycode-analysisdynamic-analysis-sandboxing+7
16 days ago
REx-skill preview

REx-skill

GitHubtihanyin/rex-skill

REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery

ai-assisted-reversingbinary-analysisbinary-exploitation+8
444 days ago
frida-stalker-NtStrace preview

frida-stalker-NtStrace

GitHubgmh5225/frida-stalker-ntstrace

frida-stalker based system call tracer on windows(x64).

binary-analysisdebuggersdynamic-analysis-sandboxing+4
33 years ago
Veridiff preview

Veridiff

GitHubveridiff/veridiff

Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.

binary-analysisbinary-exploitationcode-analysis+7
410 days ago
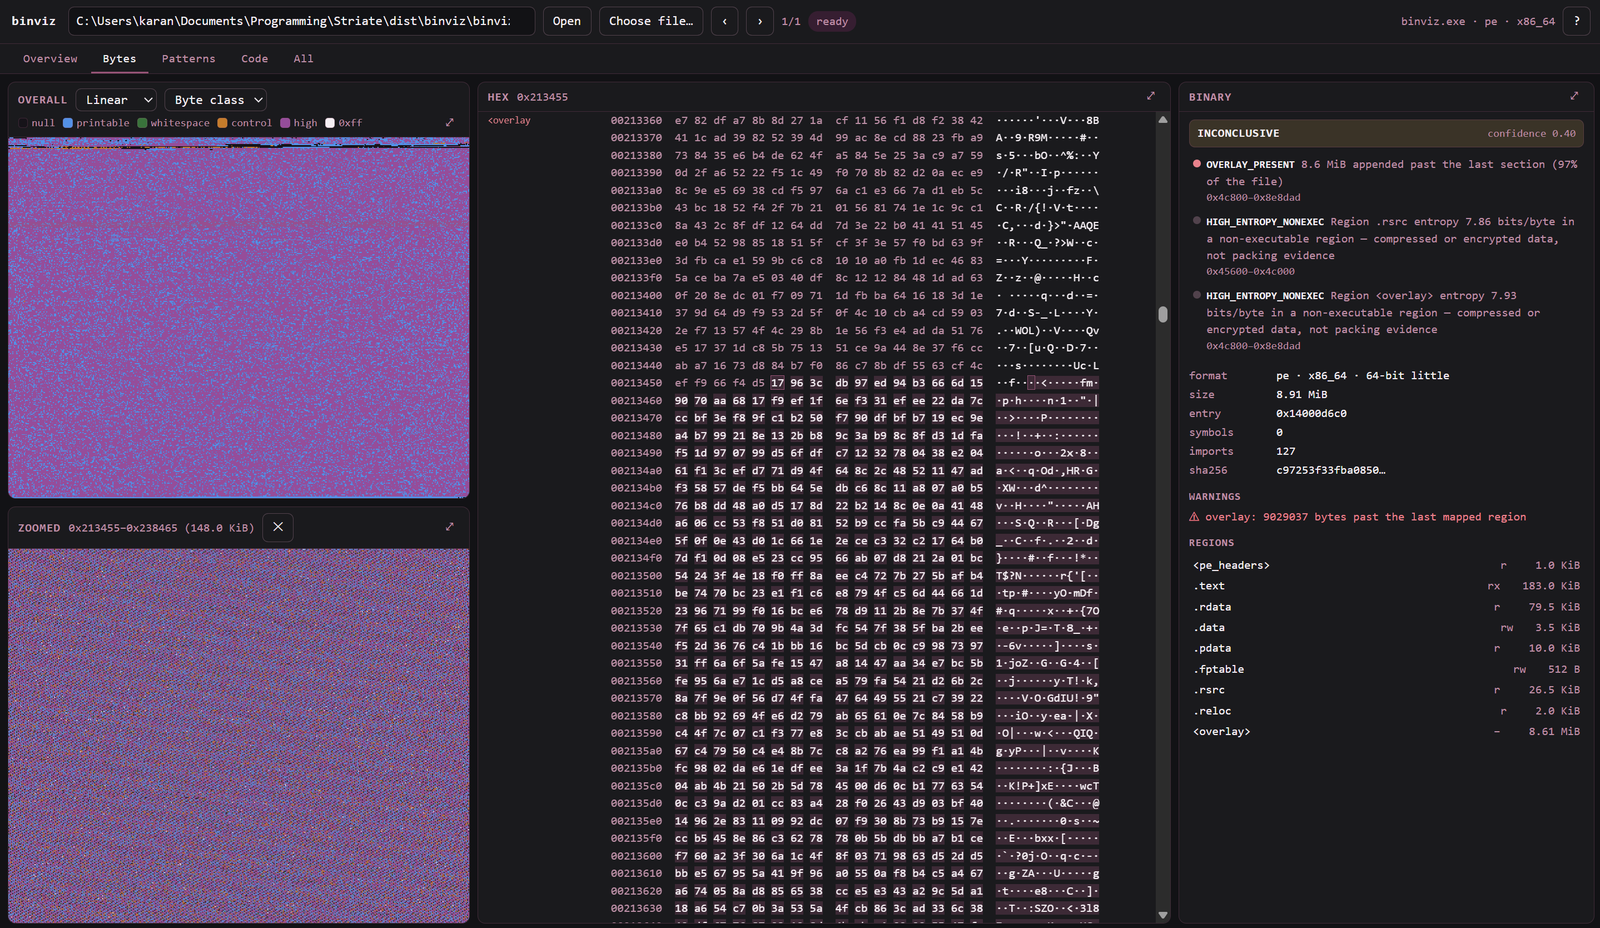
binviz preview

binviz

GitHubkarankantaria/binviz

Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.

binary-analysiseducationforensics+4
81 month ago
CVE-2026-36981-Kernel-EoP-PoC preview

CVE-2026-36981-Kernel-EoP-PoC

GitHubcanomer/cve-2026-36981-kernel-eop-poc

Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…

binary-exploitationdebuggersexploitation+4
24 months ago
fnprint preview

fnprint

GitHub1rhino2/fnprint

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.

binary-analysisdynamic-code-analysisfirmware-analysis+3
539 days ago
ctxdebug preview

ctxdebug

GitHubddudle/ctxdebug

MCP-powered reverse engineering platform connecting WinDbg, IDA Pro & x64dbg with 160+ AI-accessible debugging and analysis tools.

ai-assisted-reversingbinary-analysisdebuggers+4
244 days ago
STrace preview

STrace

GitHubmandiant/strace

A DTrace on Windows Reimplementation

debuggersdynamic-code-analysisincident-response+2
3794 months ago
ghidra_stack_strings preview

ghidra_stack_strings

GitHubzxgio/ghidra_stack_strings

A script to detect stack-strings by using emulation (leveraging Unicorn)

binary-analysisdynamic-code-analysismalware-analysis+1
359 months ago
yari preview

yari

GitHubavast/yari

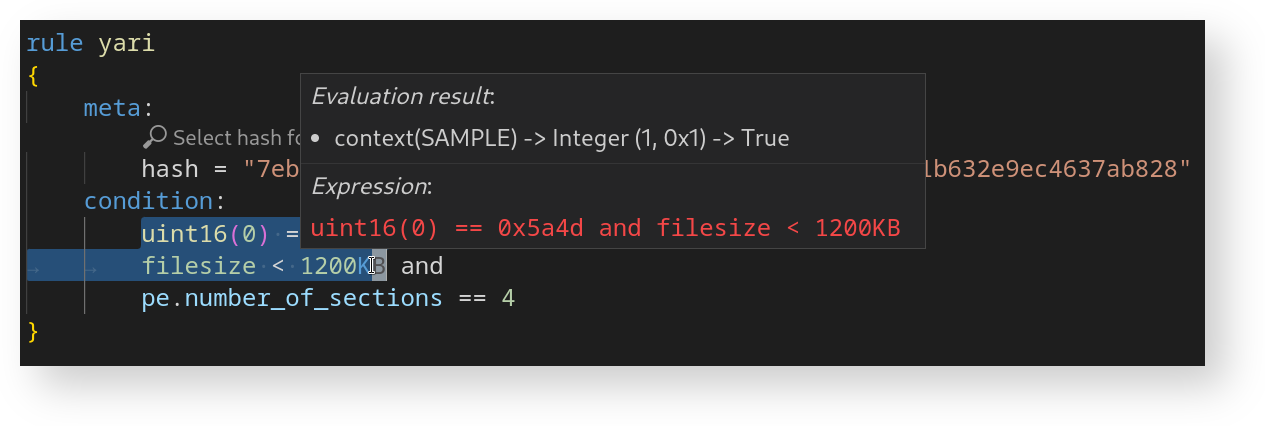
YARI is an interactive debugger for YARA Language.

binary-analysiscode-analysisdebuggers+2
901 year ago
NtDetours preview

NtDetours

GitHubrbmm/ntdetours

Detours implementation (x64/x86) which used only ntdll import

binary-analysiscode-analysisdebuggers+3
912 months ago
ReverseKit preview

ReverseKit

GitHubzer0condition/reversekit

x64 Dynamic Reverse Engineering Toolkit

binary-analysisdynamic-code-analysismalware-analysis+1
7883 years ago
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang bindings for PE-sieve

binary-analysisdynamic-code-analysismalware-analysis+1
432 years ago
VMUnprotect.Dumper preview

VMUnprotect.Dumper

GitHubvoid-stack/vmunprotect.dumper

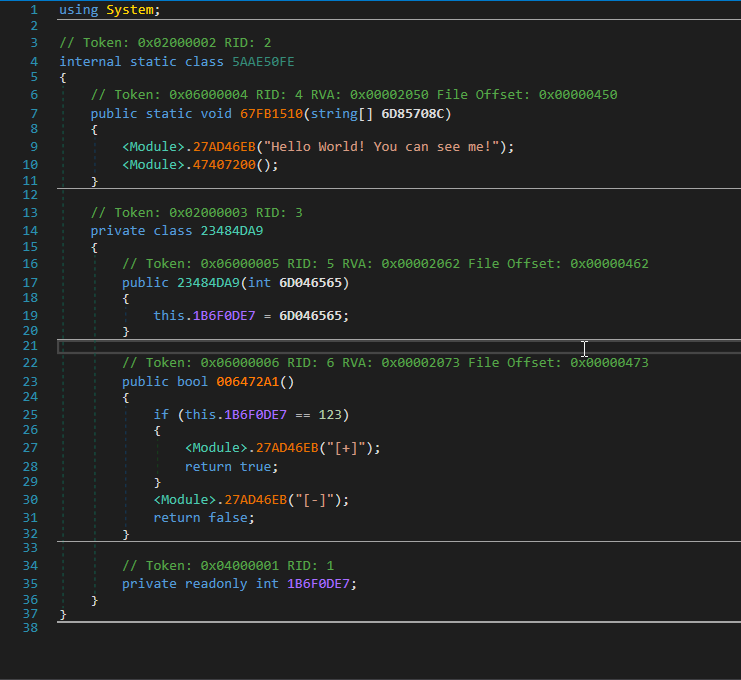
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.

binary-analysisdynamic-code-analysismalware-analysis+1
4614 years ago
diario-commandline-tools preview

diario-commandline-tools

GitHubelevenpaths/diario-commandline-tools

CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…

api-securityhash-analysisinformation-gathering+3
46 years ago
Previous1234Next