

PngLoader
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
defensive-toolseducationexploitation+6
3
i014n/pngloaderHides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
 eballoon/common-registry
Proof-of-concept C code demonstrating registry-based communication, PFN clearing, and custom process attachment techniques for stealthy payload…
 automateforceai/cve-2018-0202
Security & Privacy in Computing(Fall 2018), Final Group Project at JHUISI, clamscan vulnerability in Cisco's ClamAV 0.99.3
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
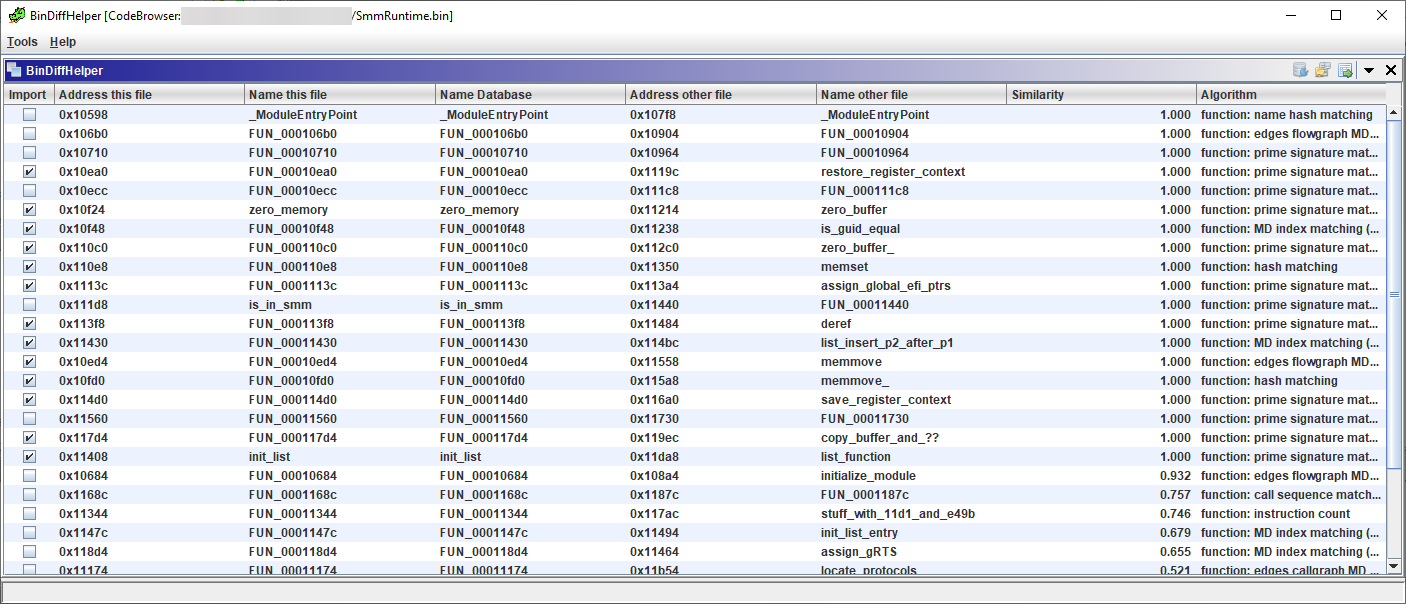 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
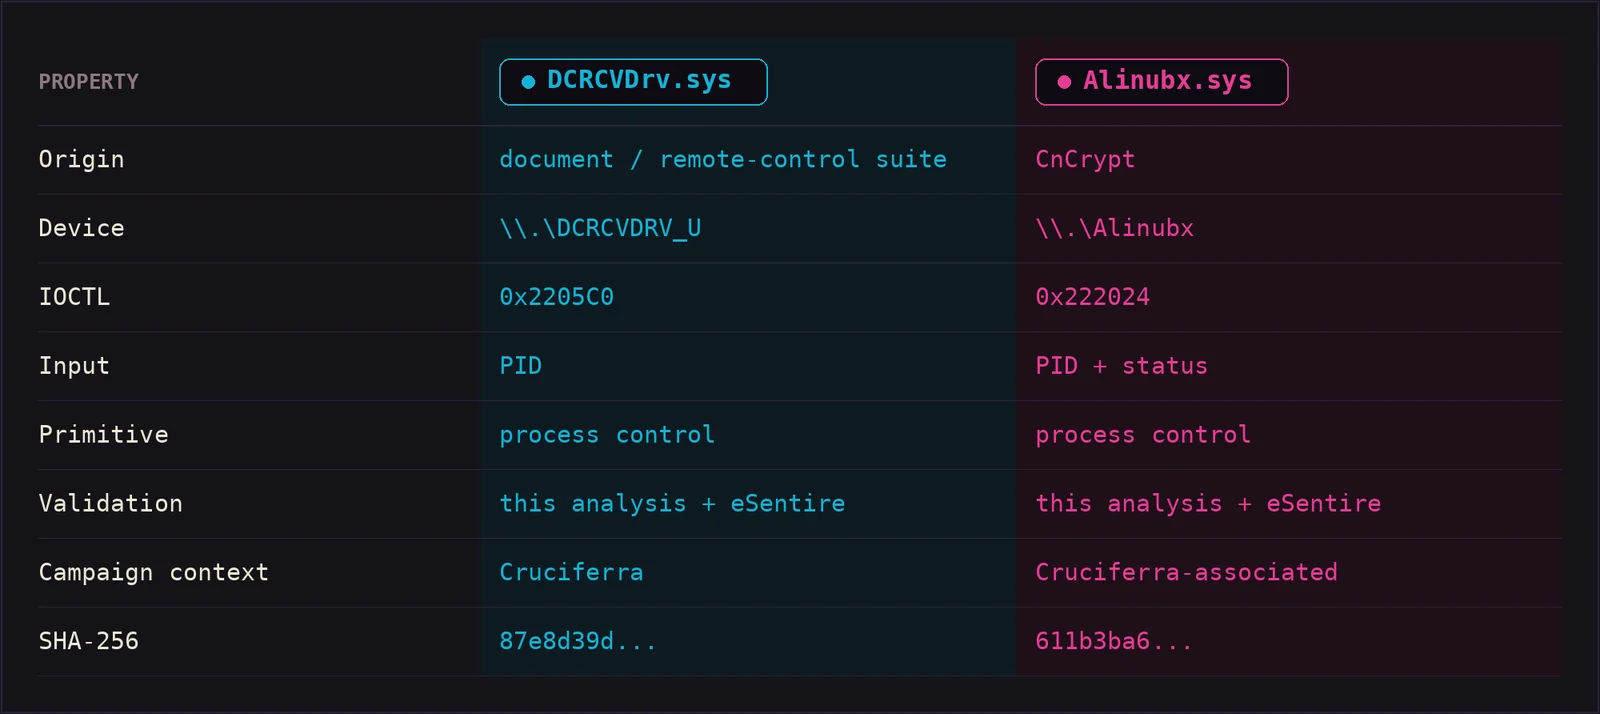 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
 mhicairo-hue/cs50-cybersecurity-final-project
Technical analysis of the XZ Utils backdoor (CVE-2024-3094), explaining the supply chain attack, obfuscation techniques, and impact on OpenSSH via…
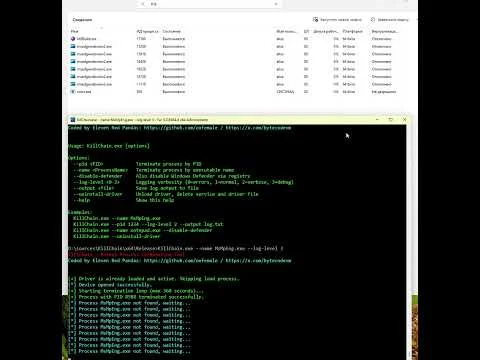 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 namegabevictoire01-sys/cs50-cybersecurity-final-project
CS50 Cybersecurity Final Project - Analysis of CVE-2024-3094
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
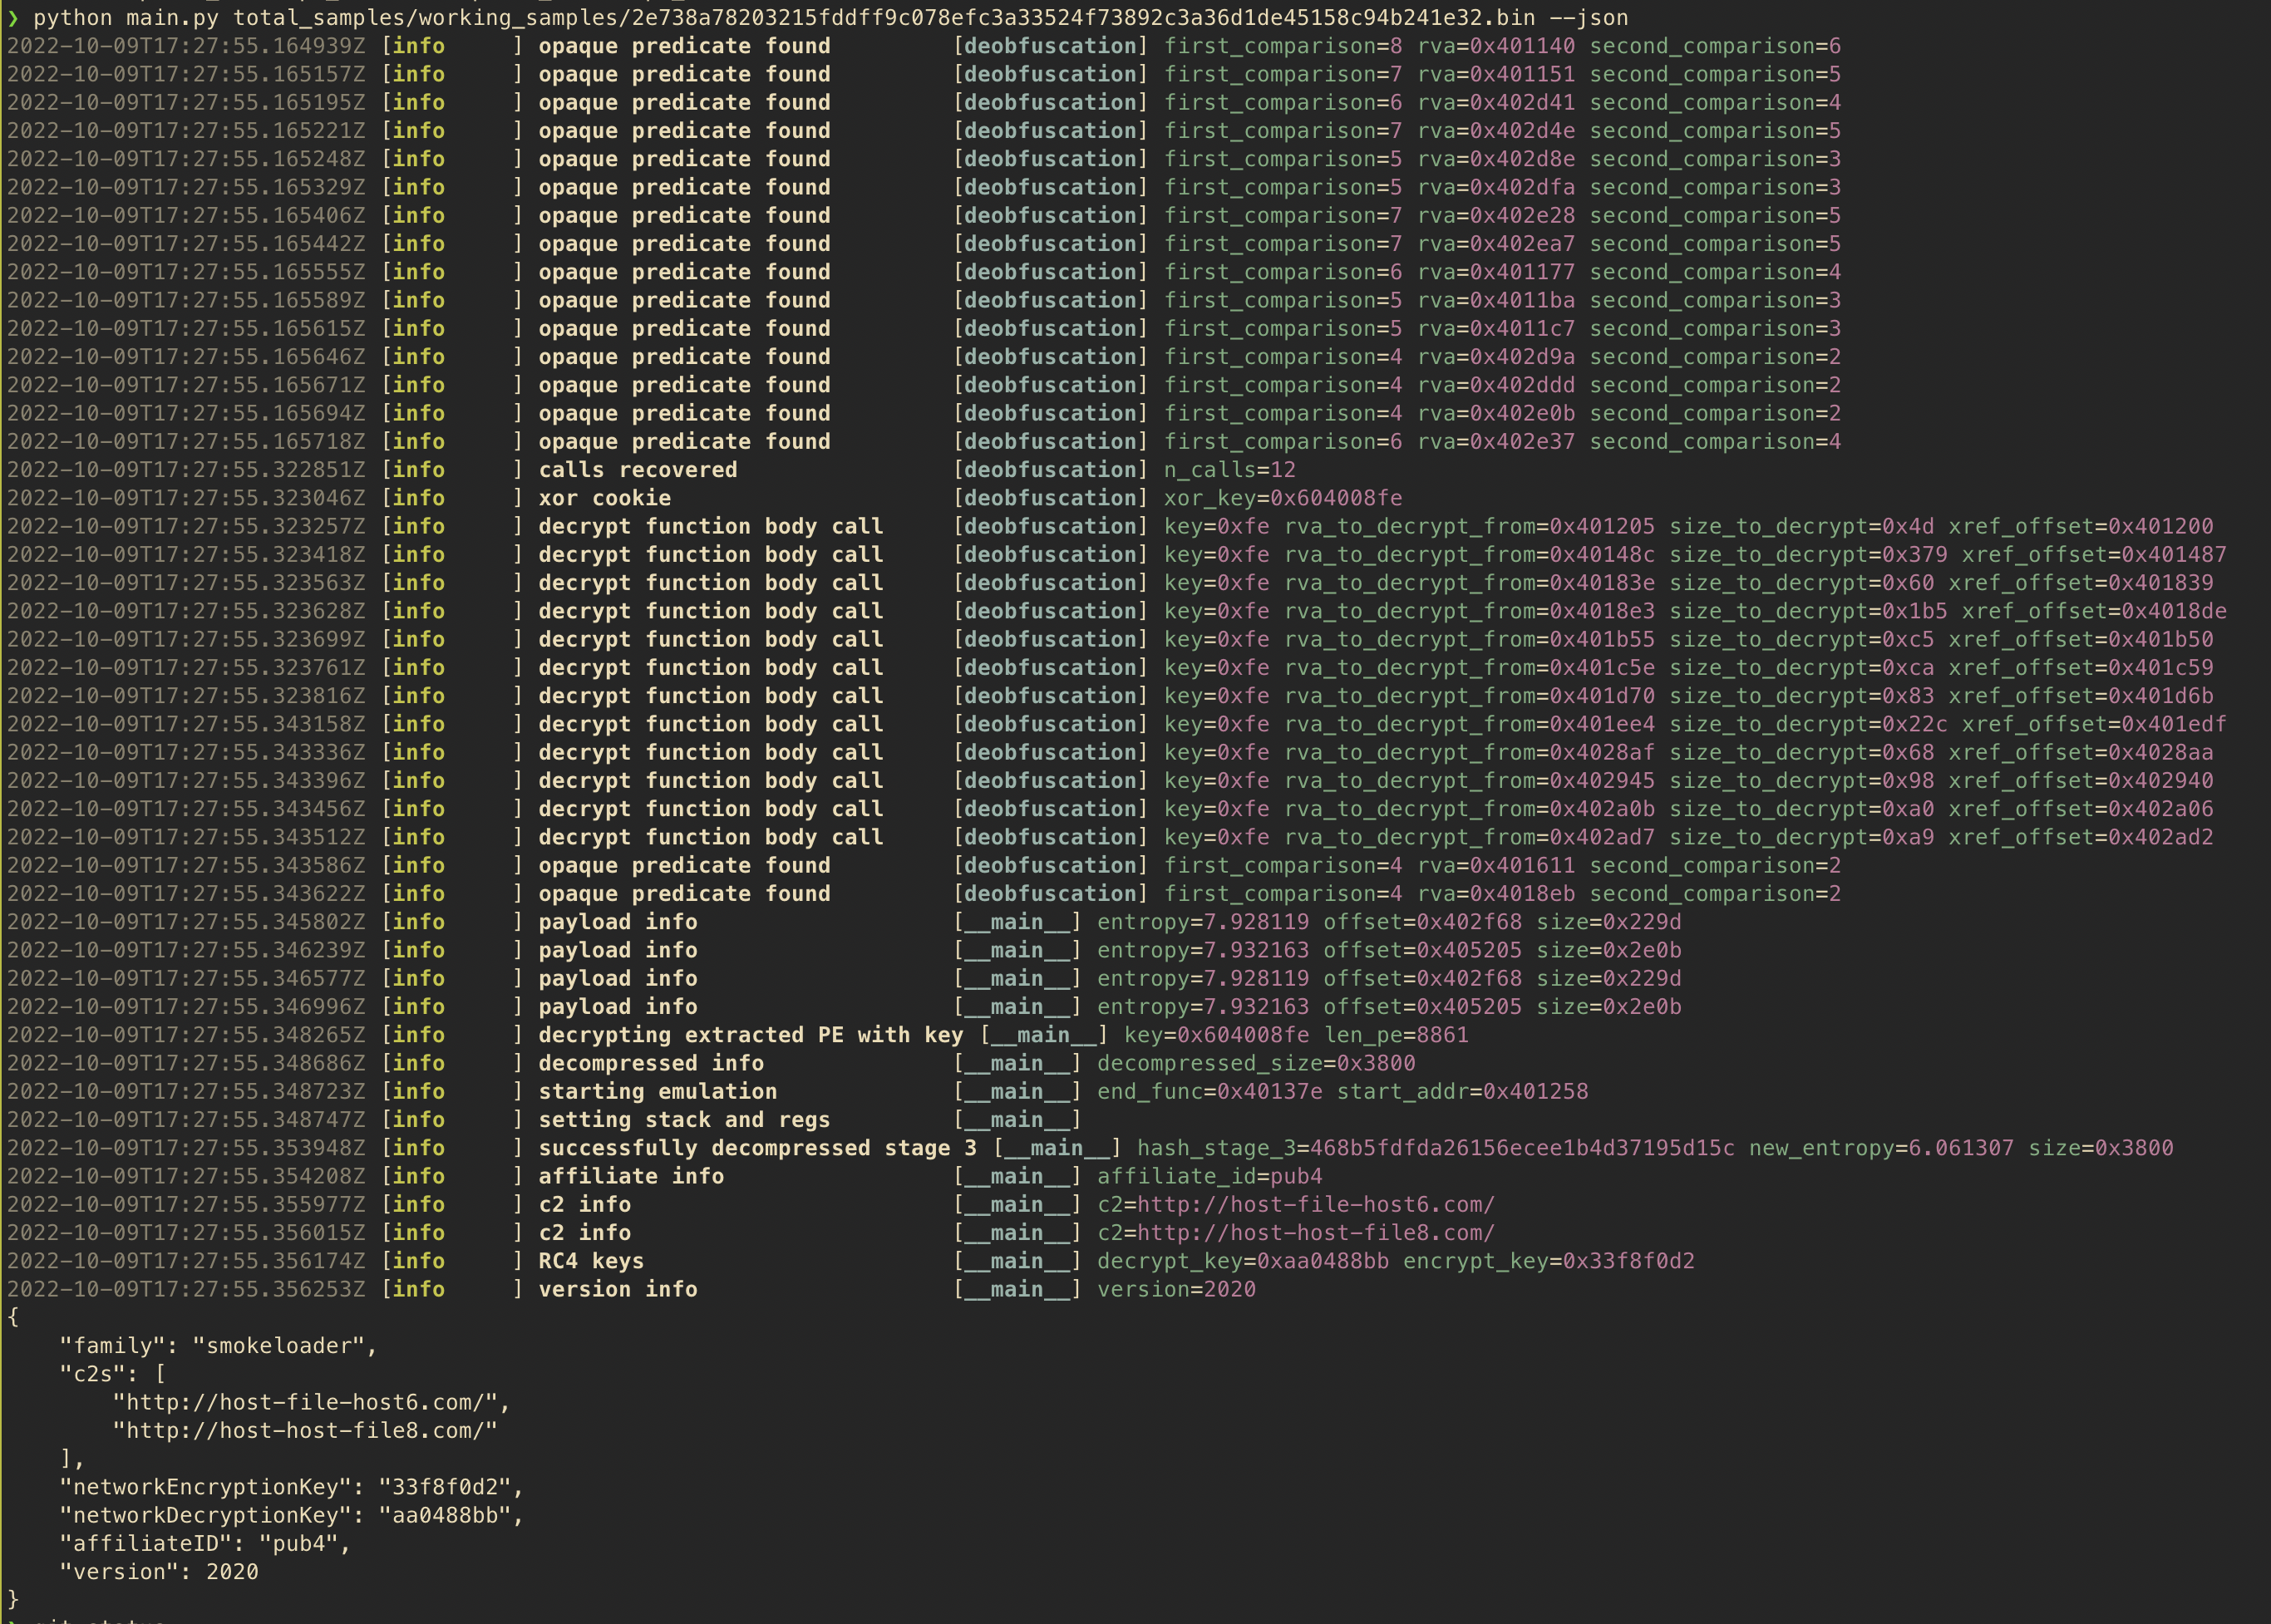 myrtus0x0/smoke_conf_extract
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
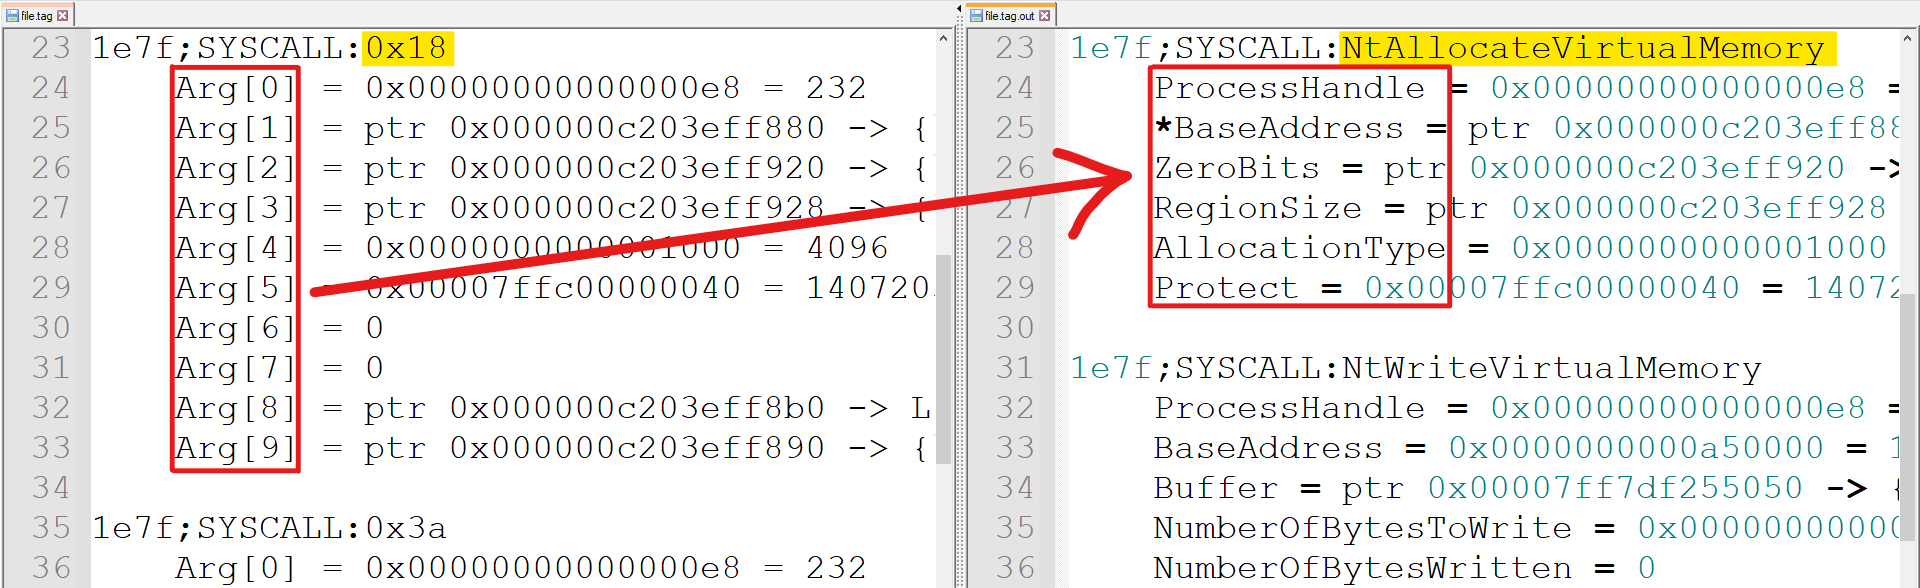 goatmilkkk/tinyprocessor
A post-processing script for TinyTracer
 hasherezade/pesieve-go
Golang bindings for PE-sieve