
obfuscation_analysis
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
binary-analysiscode-analysismalware-analysis+3
258
mrphrazer/obfuscation_analysisBinary Ninja plugin to analyze and simplify obfuscated code
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!
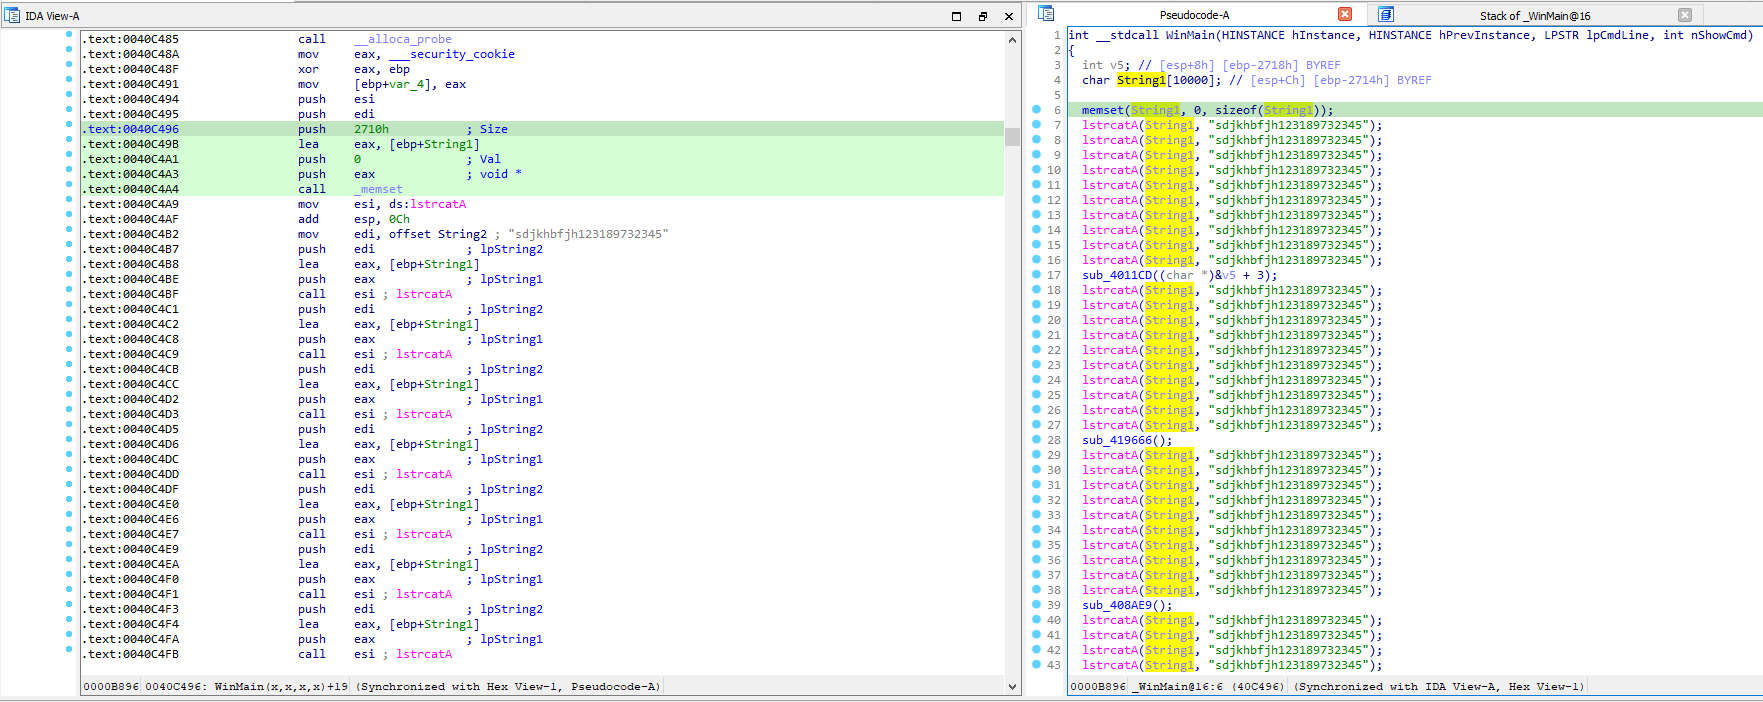 pandare9x/nop_plugin
Plugin for NOPing instructions in IDA
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules
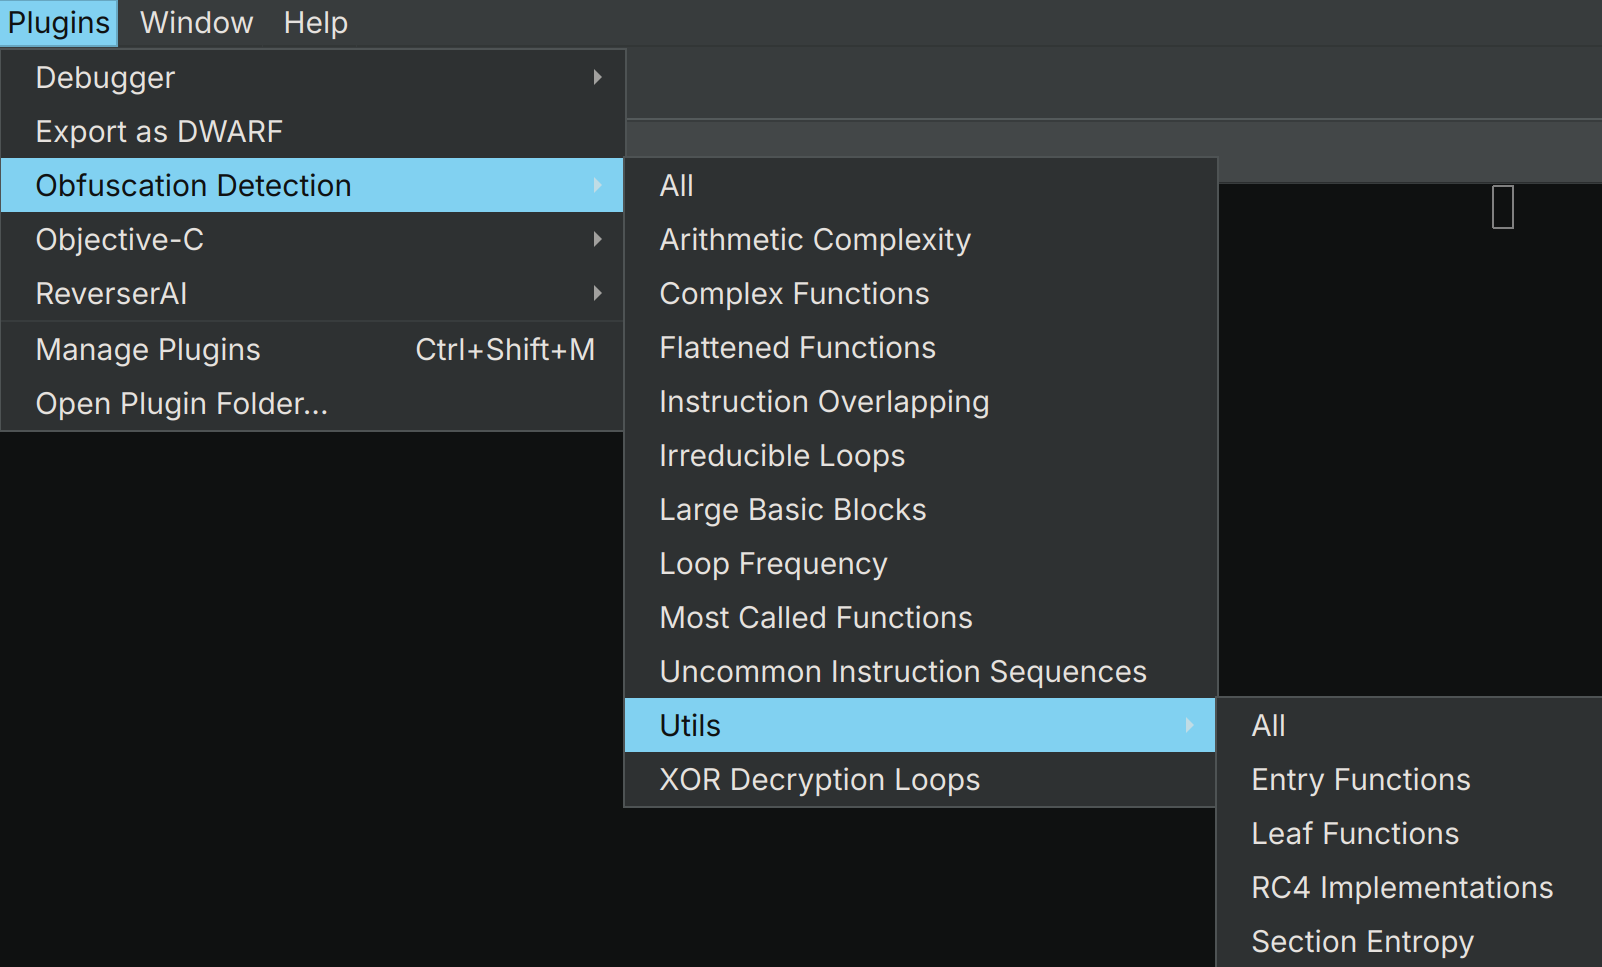 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs