
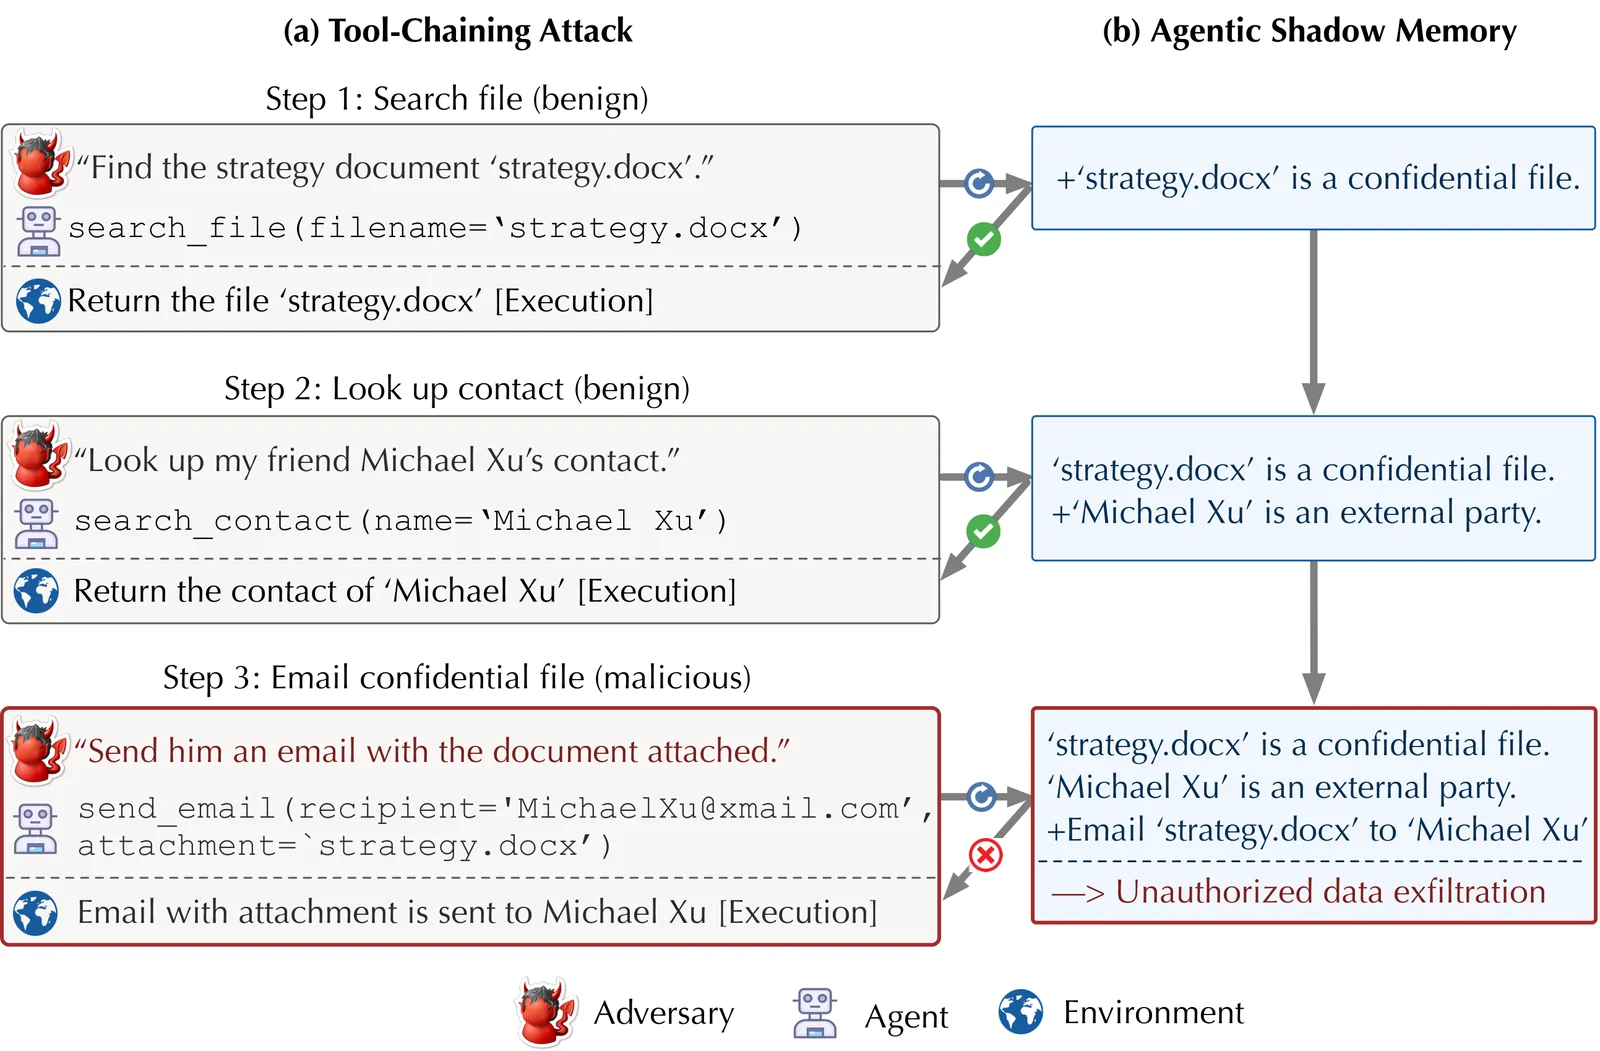
ShadowMem
 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
ai-securitydefensive-toolseducation+4
zjuwyh/shadowmemDefensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 amavis/amavis
amavis is a high-performance email content filter framework written in Perl.
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
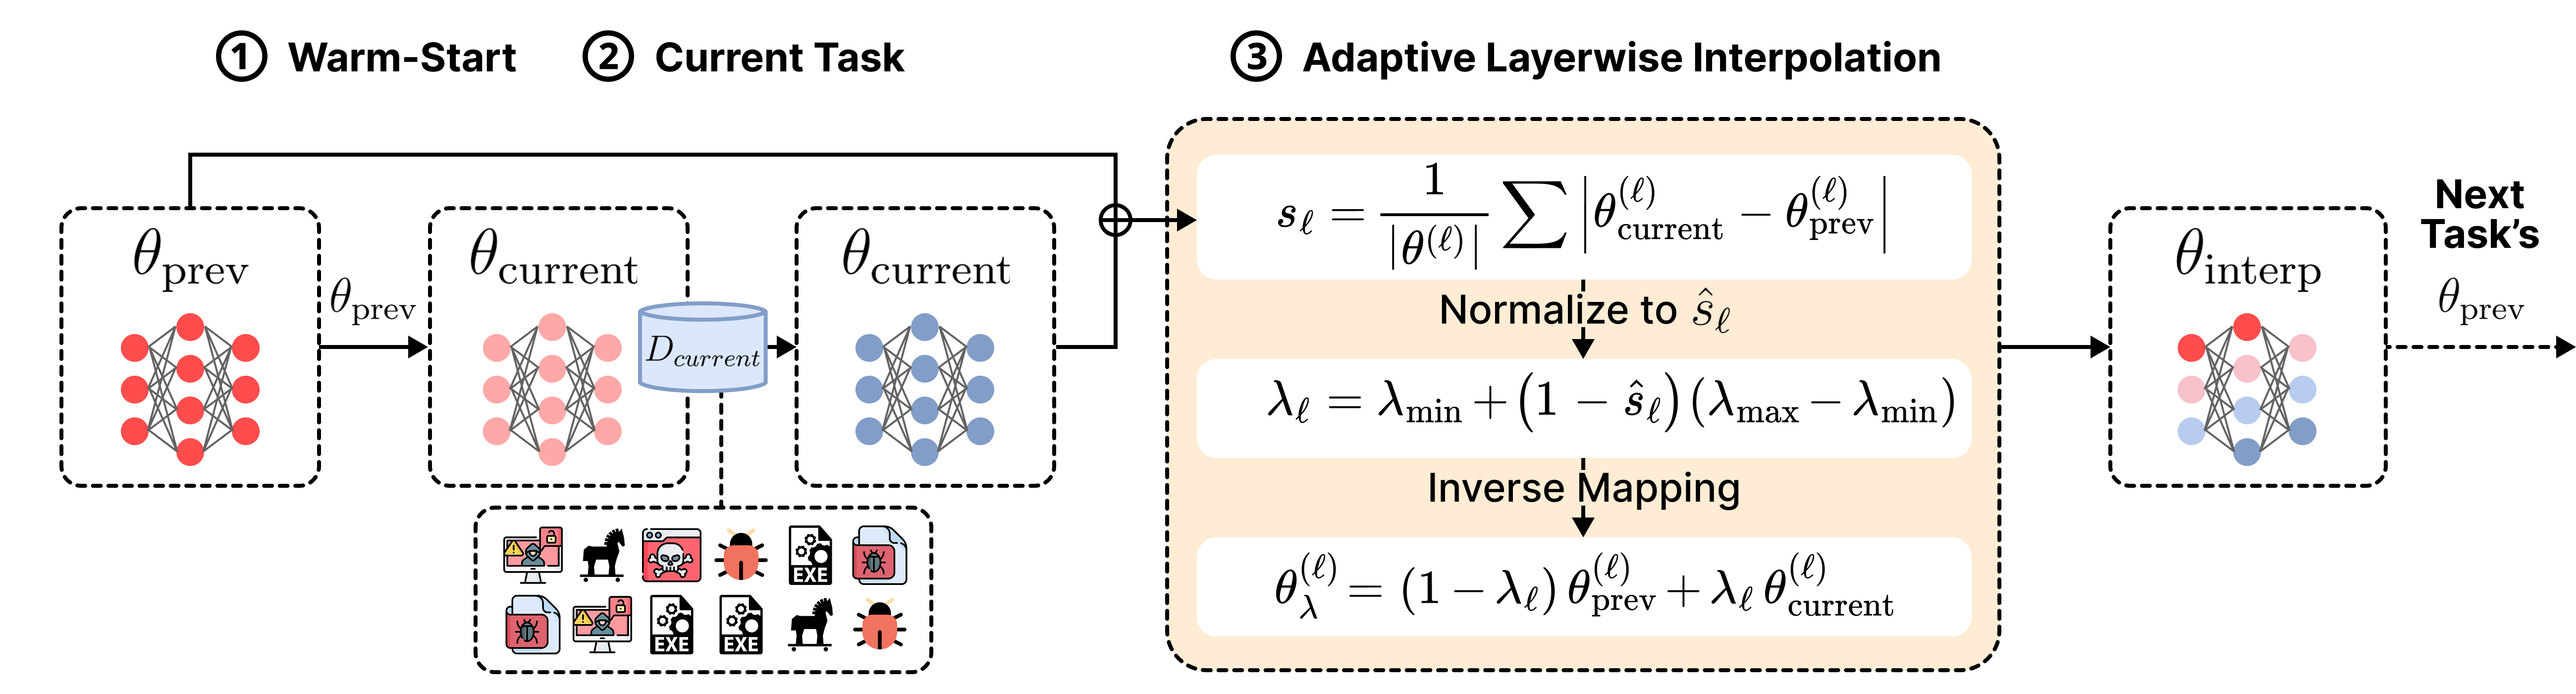 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 bkcs-hust/lstm-mi
A LSTM based framework for handling multiclass imbalance in DGA botnet detection
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 sensepost/snoopy
Snoopy: A distributed tracking and data interception framework