

cve-2021-33879
 mmiszczyk/cve-2021-33879
GameLoop update MITM
exploitationmalware-analysispenetration-testing+3
mmiszczyk/cve-2021-33879GameLoop update MITM
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 michaelweber/macrome
Excel Macro Document Reader/Writer for Red Teamers & Analysts
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 blacksnufkin/blacksnufkin
Red team operator and malware developer specializing in evasion techniques, reverse engineering, and initial access operations. Active CVE researcher…
 deepfield/public-research
DDoS botnet research and indicators of compromise from Nokia Deepfield ERT
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 ghostwolflab/apt-individual-combat-guide
Educational guide and code repository for understanding APT attack techniques, covering reconnaissance, web and service exploitation, trojans, C2,…
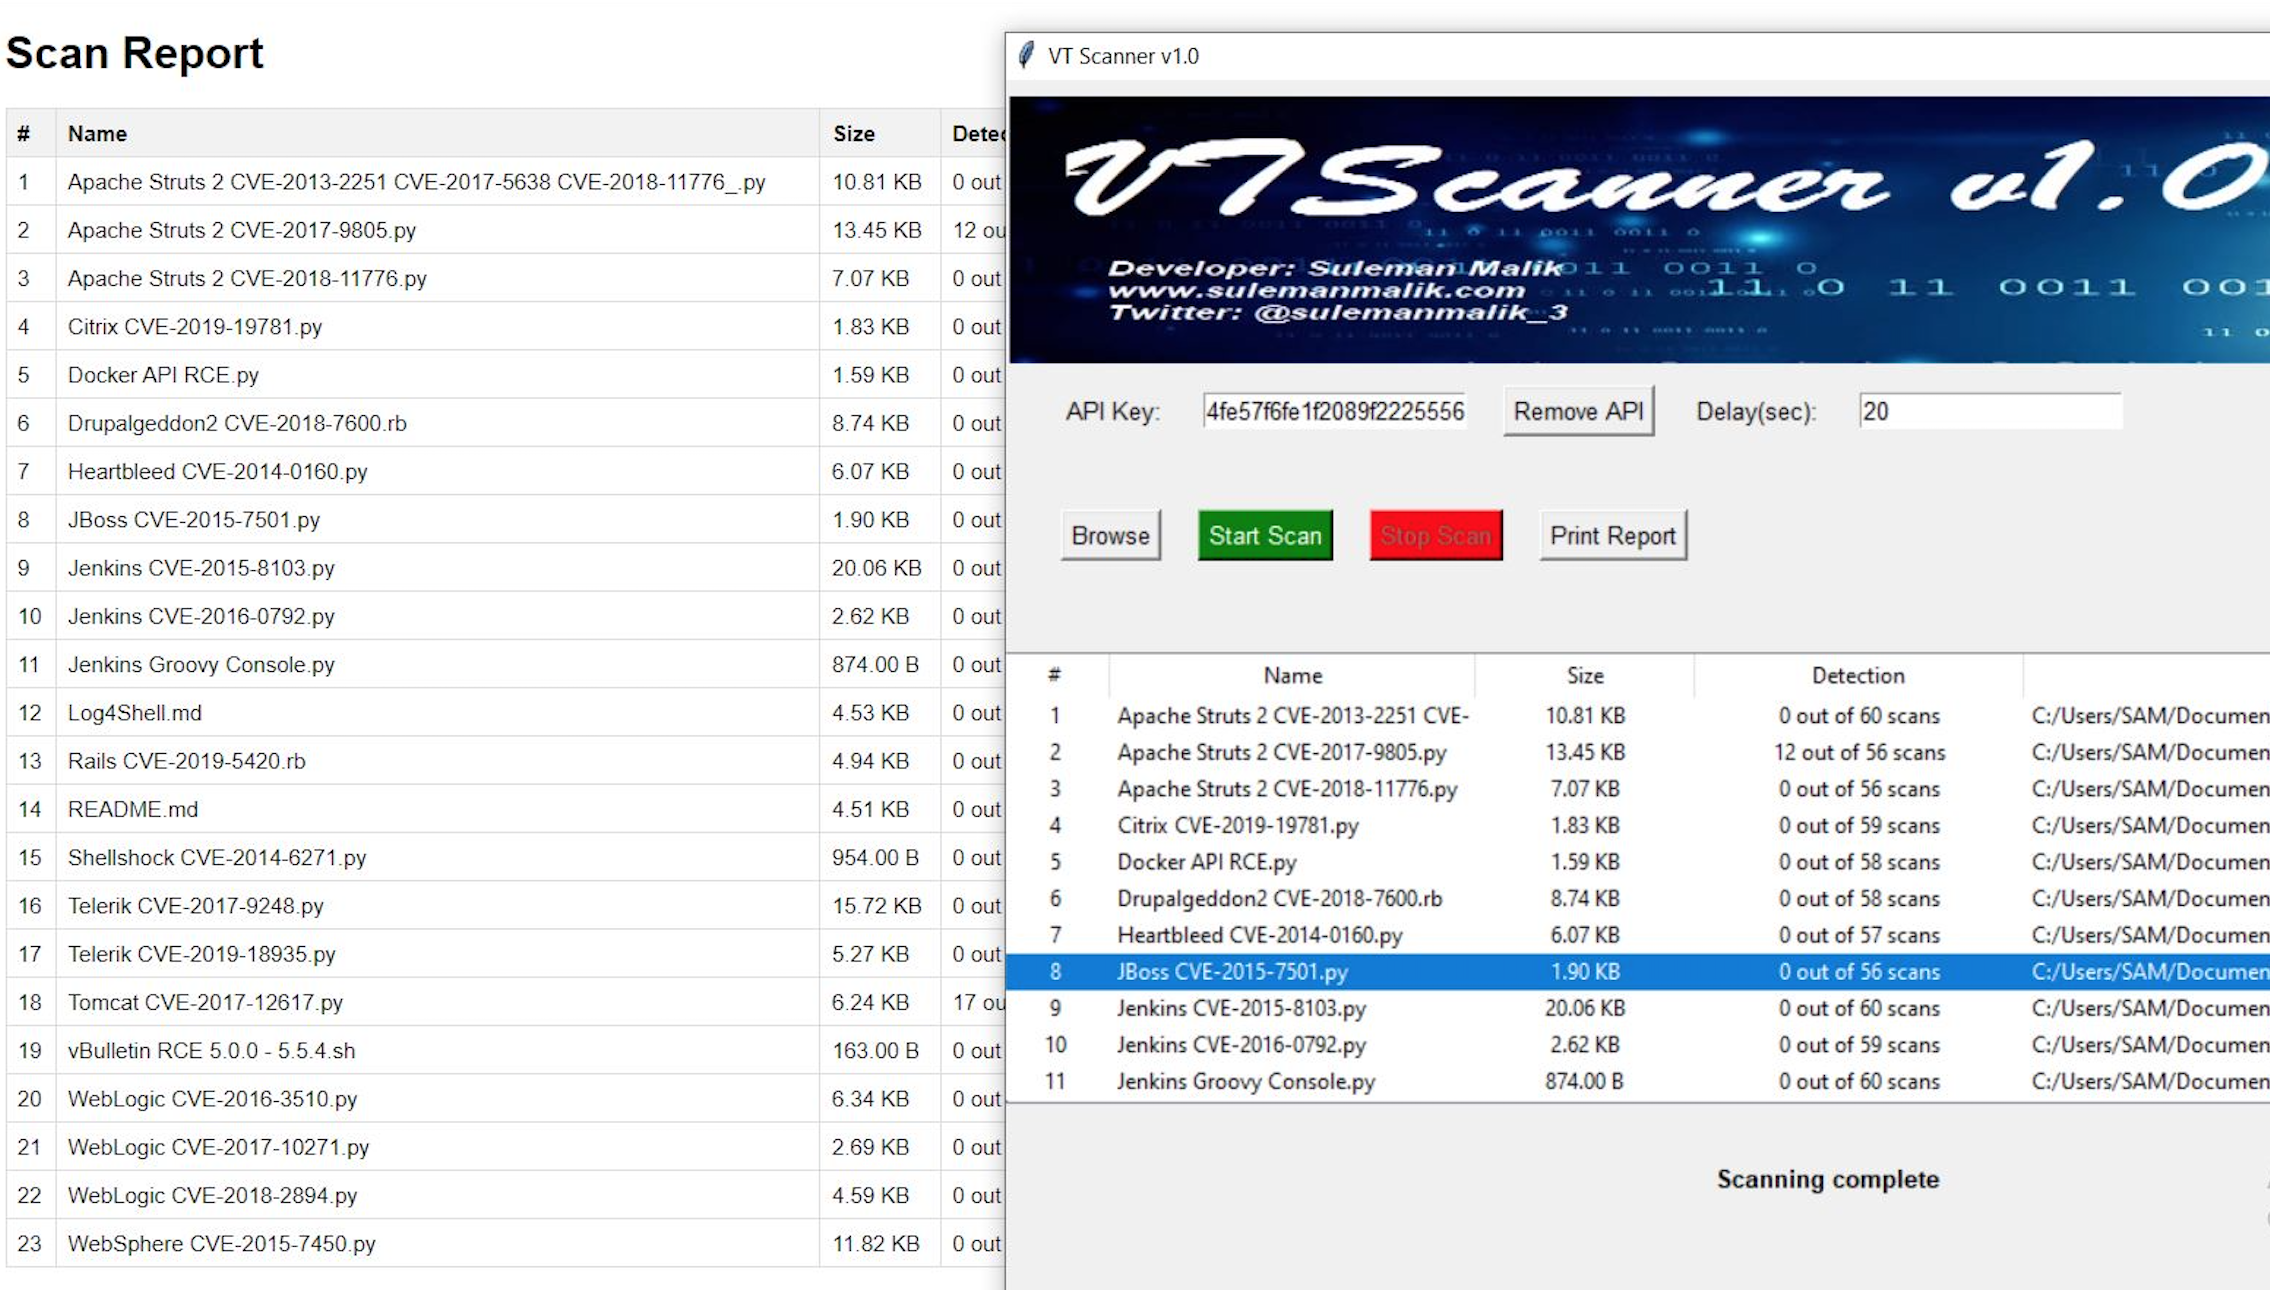 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
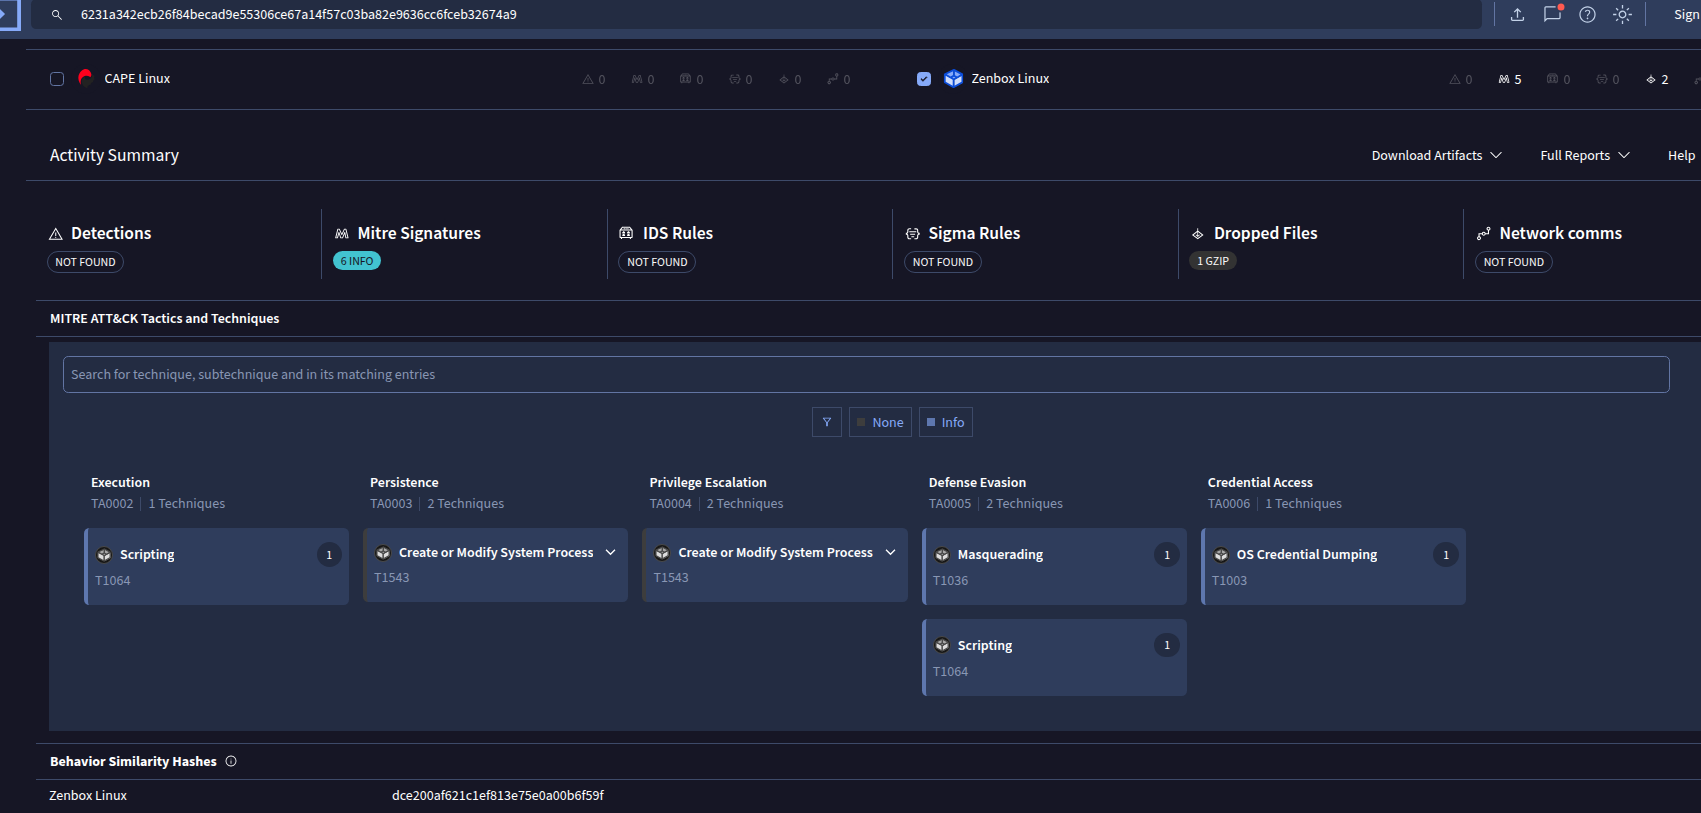 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 daniomass/slivermirage
Crystal Palace PICO loader for Sliver C2 dual-layer AMSI bypass, ETW silencing, AES-256-CBC encrypted payloads, 6 delivery variants
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 klezvirus/cve-2021-40444
CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
 maaaaz/androwarn
Yet another static code analyzer for malicious Android applications
 tyeurada/edrevasionworkshop
Workshop materials for “Step-by-Step Malware Development: Evading EDR from Loaders to the Kernel” presented at DEF CON 34 and BSidesLV 2026. Covers…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.