
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
34 results
SysTrace preview

SysTrace

GitHubtracebyte8/systrace

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…
anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
24
1 month ago
DrSemu preview

DrSemu

GitHubsecrary/drsemu

DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2807 years ago
stringsifter preview

stringsifter

GitHubmandiant/stringsifter

A machine learning tool that ranks strings based on their relevance for malware analysis.
binary-analysismachine-learningmalware-analysis+2
7663 years ago
SigLens preview

SigLens

GitHubst0rn/siglens

Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
binary-analysisdefensive-toolsdigital-forensics+7
4015 days ago
dynmx preview

dynmx

GitHub0x534a/dynmx

Signature-based detection of malware features based on Windows API call sequences. It's like YARA for sandbox API traces!
dynamic-analysis-sandboxingmalware-analysis
843 years ago
retdec preview

retdec

GitHubavast/retdec

RetDec is a retargetable machine-code decompiler based on LLVM.
binary-analysismalware-analysisreverse-engineering+1
8.6k4 months ago
flashmingo preview
Archived

flashmingo

GitHubmandiant/flashmingo

Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
binary-analysisdynamic-analysis-sandboxingeducation+6
1207 years ago
guarddog preview

guarddog

GitHubdatadog/guarddog

🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
code-analysisdevsecopsdynamic-analysis-sandboxing+6
1.2k1 month ago
pyghidra-mcp preview

pyghidra-mcp

GitHubclearbluejar/pyghidra-mcp

Python Command-Line Ghidra MCP
ai-assisted-reversingbinary-analysiscode-analysis+7
4467 days ago
pyrebox preview
Archived

pyrebox

GitHubcisco-talos/pyrebox

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
binary-analysisdebuggersdigital-forensics+5
1.7k2 years ago
Cmulator preview
Archived

Cmulator

GitHubcoldzer0/cmulator

Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
binary-analysisdebuggersdynamic-analysis-sandboxing+4
3044 years ago
BIDO preview

BIDO

GitHubwhatishope/bido

Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
android-securityeducationmachine-learning+3
28 months ago
mal_unpack preview

mal_unpack

GitHubhasherezade/mal_unpack

Dynamic unpacker based on PE-sieve
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
8426 months ago
zelos preview

zelos

GitHubzeropointdynamics/zelos

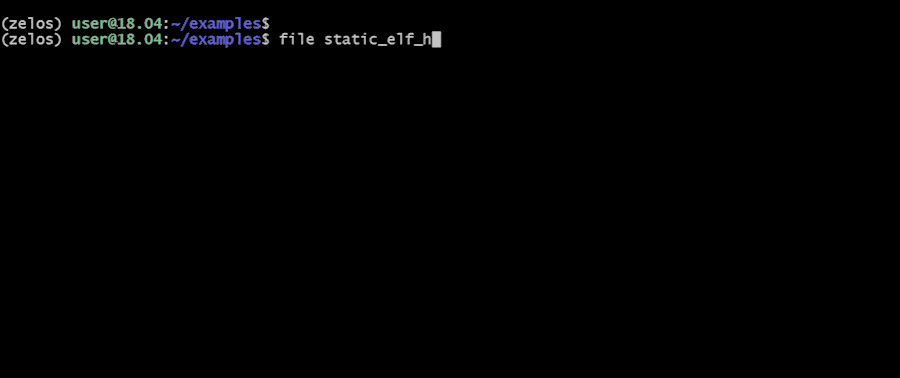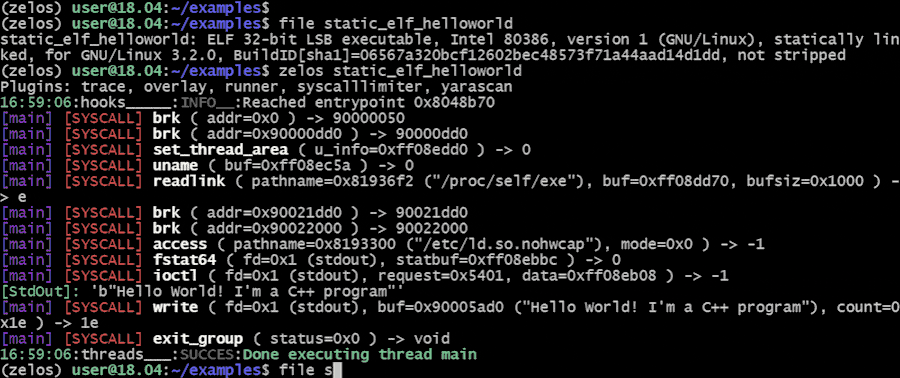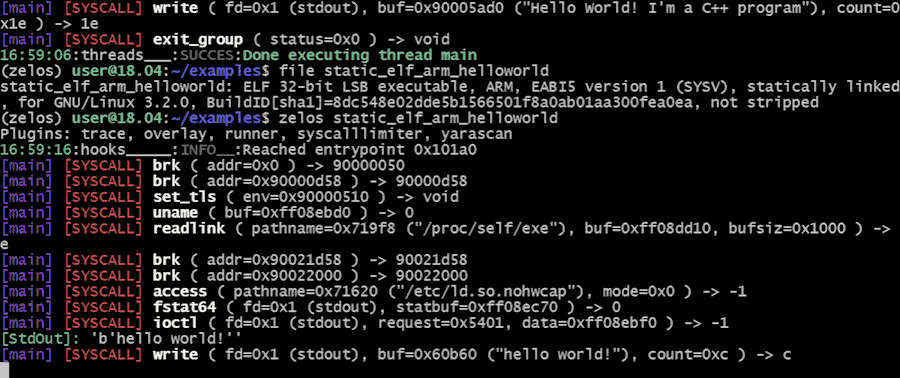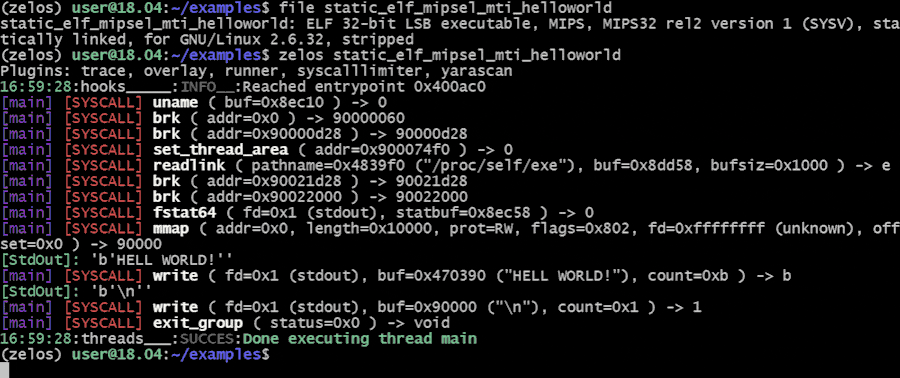
A comprehensive binary emulation and instrumentation platform.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
4203 years ago
flare-qdb preview
Archived

flare-qdb

GitHubmandiant/flare-qdb

Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
binary-analysisdebuggersdynamic-analysis-sandboxing+3
1643 years ago
ThePhish preview

ThePhish

GitHubemalderson/thephish

ThePhish: an automated phishing email analysis tool
digital-forensicsemail-securityincident-response+5
1.4k2 years ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
binary-analysisbinary-exploitationmalware-analysis+3
4032 years ago
ParanoiDF preview

ParanoiDF

GitHubpatrickdw123/paranoidf

ParanoiDF - PDF Analysis Suite based on PeePDF by Jose Miguel Esparza (http://peepdf.eternal-todo.com/). Tools added: Password cracking, redaction…

data-recoverydigital-forensicsencryption-decryption-tools+6
1123 years ago
Previous12Next