

scan
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
22411h 54m ago
atomdrift-project/scan0-day malware detection for binaries, source & scripts (that doesn't suck)
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 matonis/ripvt
Virus Total API Maltego Transform Set For Canari
 magnetforensics/swishdbgext
Incident Response & Digital Forensics Debugging Extension
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 kaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis
Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
 mitre/multiscanner
Modular file scanning/analysis framework
 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 dodo-sec/kpot-string-decrypter
IDA python scripts to decrypt strings from KPOT and set those as comments
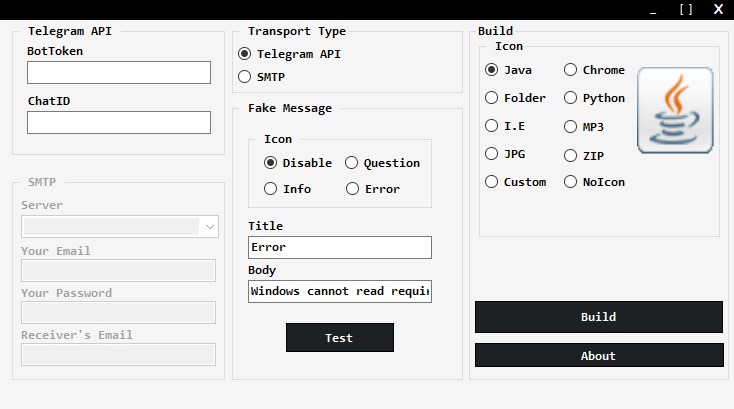 parsingteam/teleshadow2
TeleShadow - Telegram Desktop Session Stealer (Windows)
 withsecurelabs/garbageman
GarbageMan is a set of tools for analyzing .NET binaries through heap analysis.
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 withsecurelabs/doublepulsar-detection-script
A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.
 cmatthewbrooks/r2kit
A set of scripts for a radare-based malware code analysis workflow
 gmh5225/driver-hidekernelthread-iocancelirp
Windows kernel driver technique that hides kernel threads by abusing IoCancelIrp and IRP cancel routines, with detection methods for identifying…
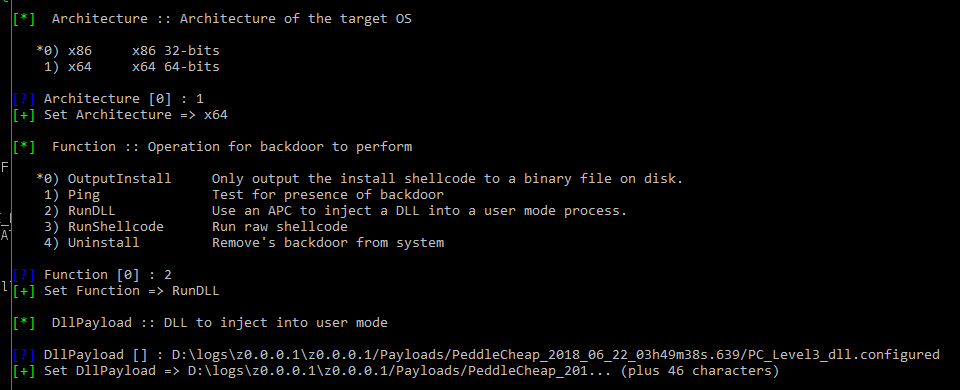 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands