
cowrie
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
defensive-toolsincident-responseinformation-gathering+3
cowrie/cowrieCowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 soheiltnt/jakeylogger
Python-based keylogger for capturing and logging keystrokes. Designed for educational security research and testing.
 pjlantz/hale
Botnet command & control monitor
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 malwaretech/follinaextractor
Extract payload URLs from Follina (CVE-2022-30190) docx and rtf files
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 silascutler/malpipe
Malware/IOC ingestion and processing engine
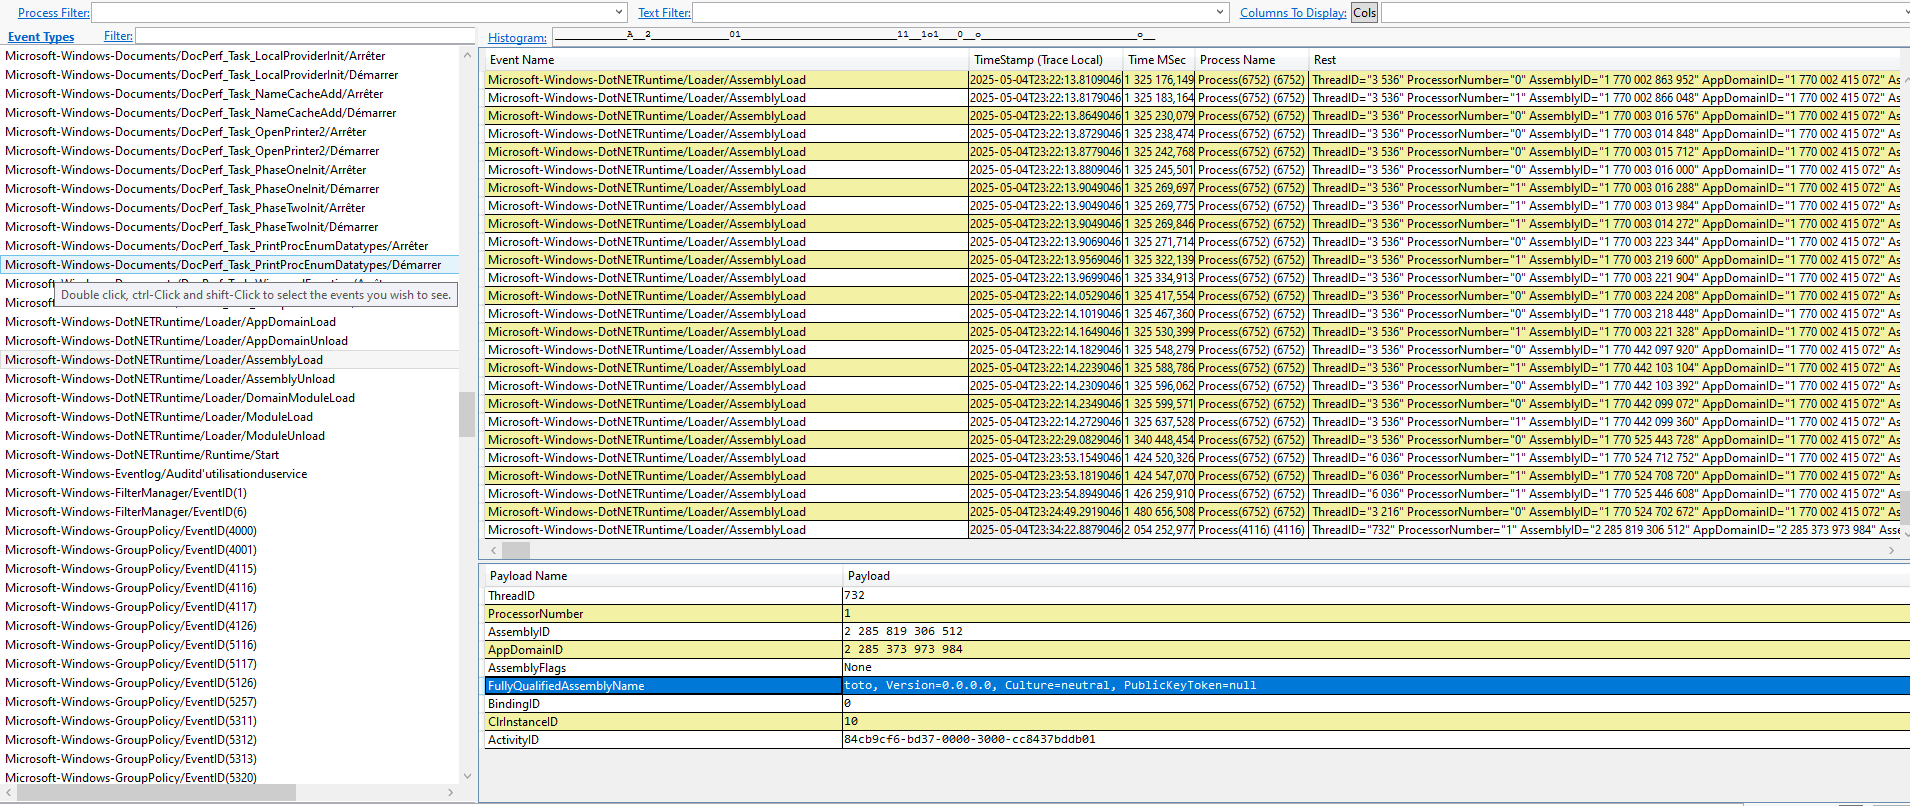 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
 mrprogrammer2938/black-tool
Install the tools and start Attacking , black-tool v5.5.5 ! ⬛
 aniket2912/all-cehv13-module-wise-pdf-reports
Practical labs, notes, and reports for CEH v13 modules — covering web hacking, network pentesting, malware analysis, social engineering, and security…
 elevenpaths/neto
Neto | A tool to analyse browser extensions
 krmaxwell/maltrieve
A tool to retrieve malware directly from the source for security researchers.
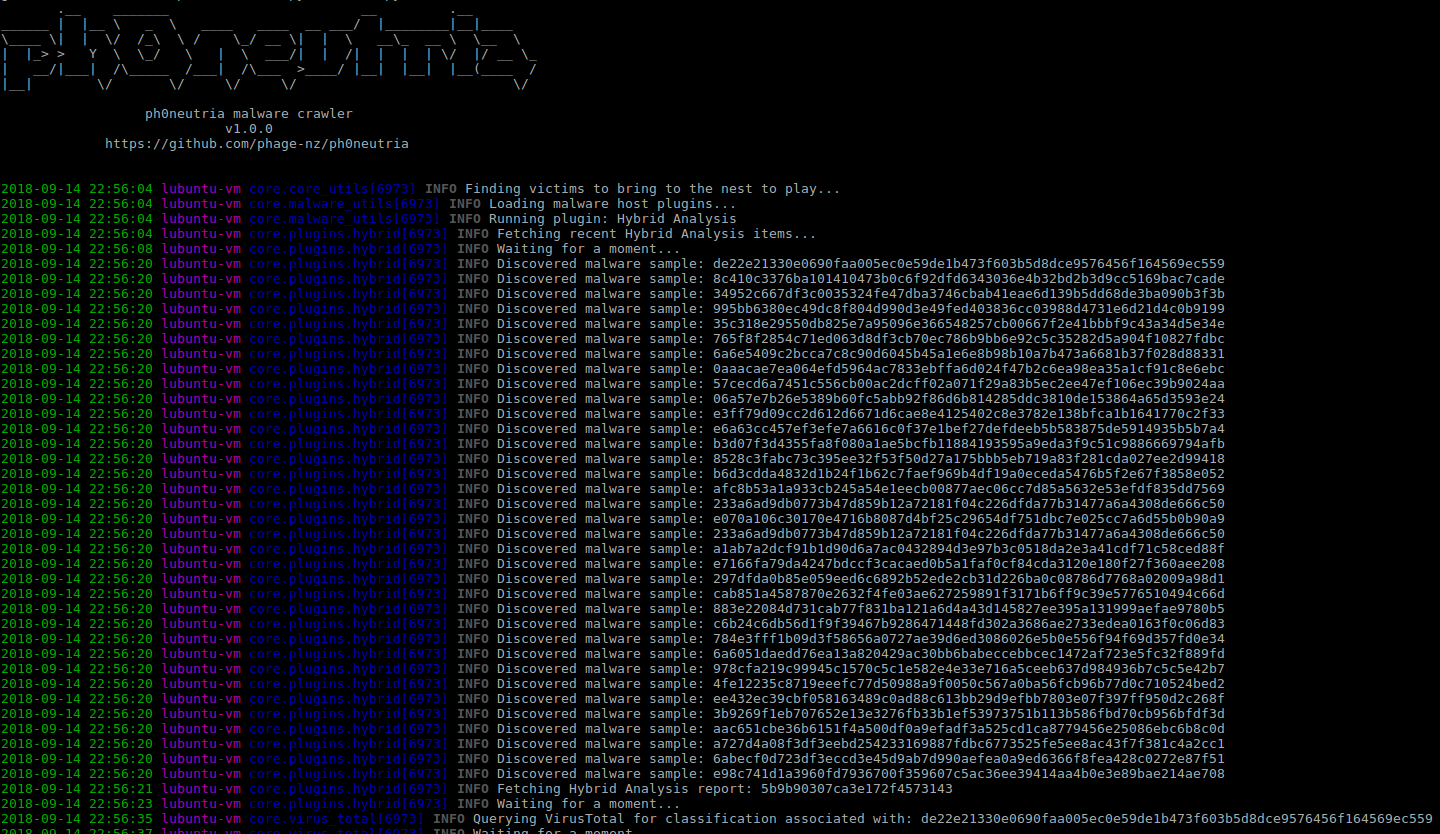 phage-nz/ph0neutria
ph0neutria is a malware zoo builder that sources samples straight from the wild. Everything is stored in Viper for ease of access and manageability.
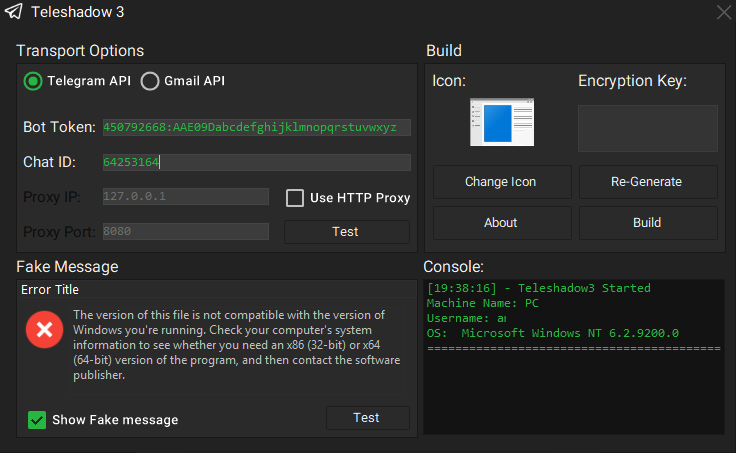 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.