

PCAPdroid
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
android-securitydns-analysiseducation+8
emanuele-f/pcapdroidNo-root network monitor, firewall and PCAP dumper for Android
 ytisf/thezoo
Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
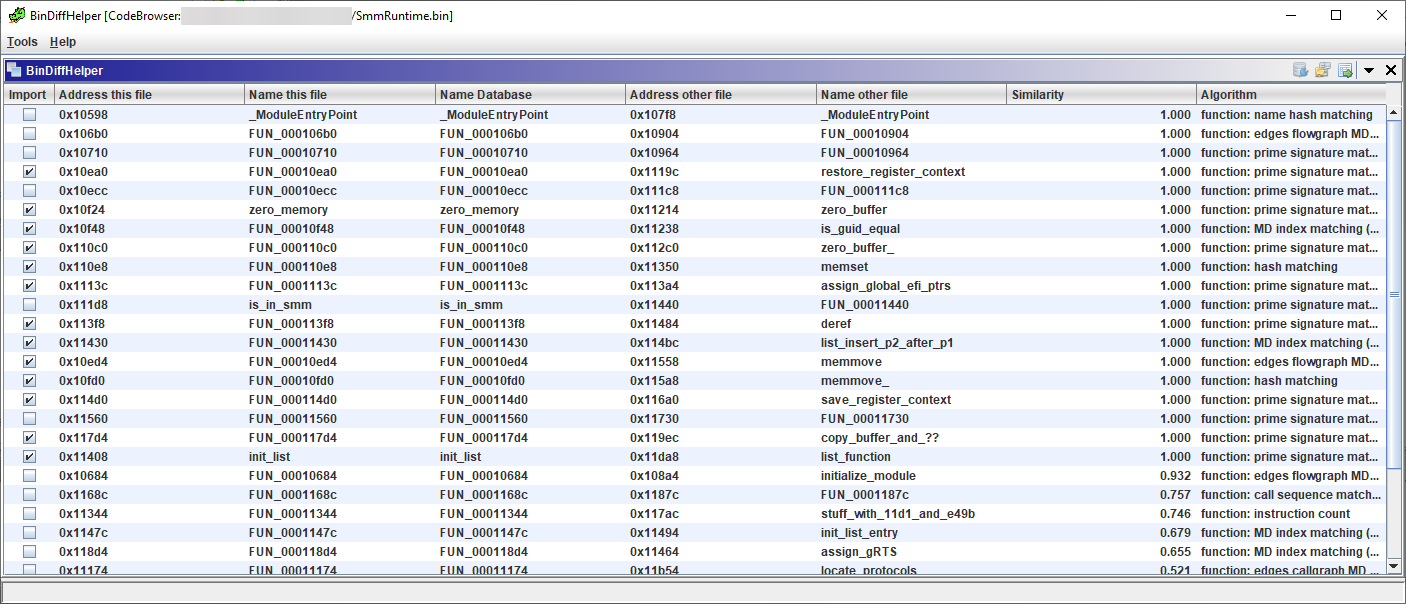 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 ashishb/android-security-awesome
A collection of android security related resources
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
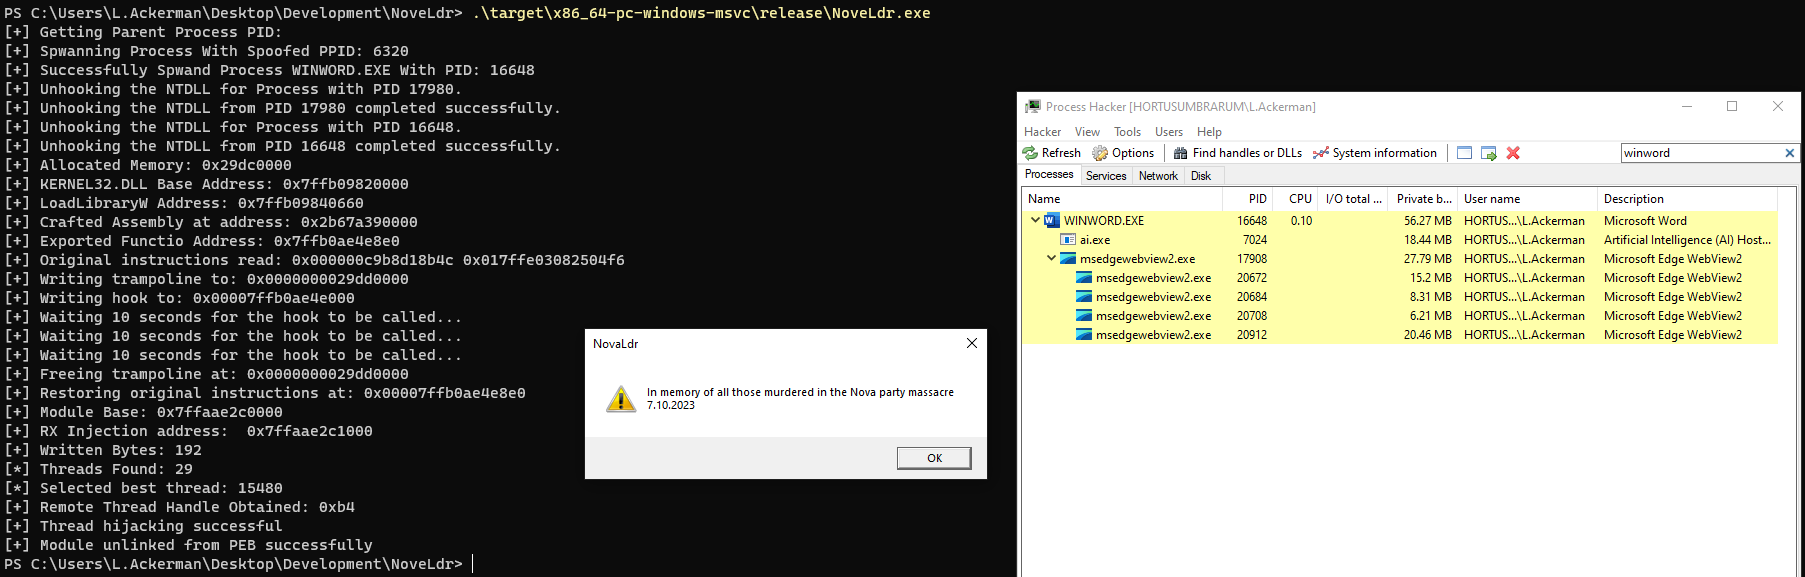 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 bst04/cybersources
A curated list of cybersecurity tools and resources.
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 sh3llyr/statistrings
YARA Rule Strings Statistics Calculator and Malware Research Helper
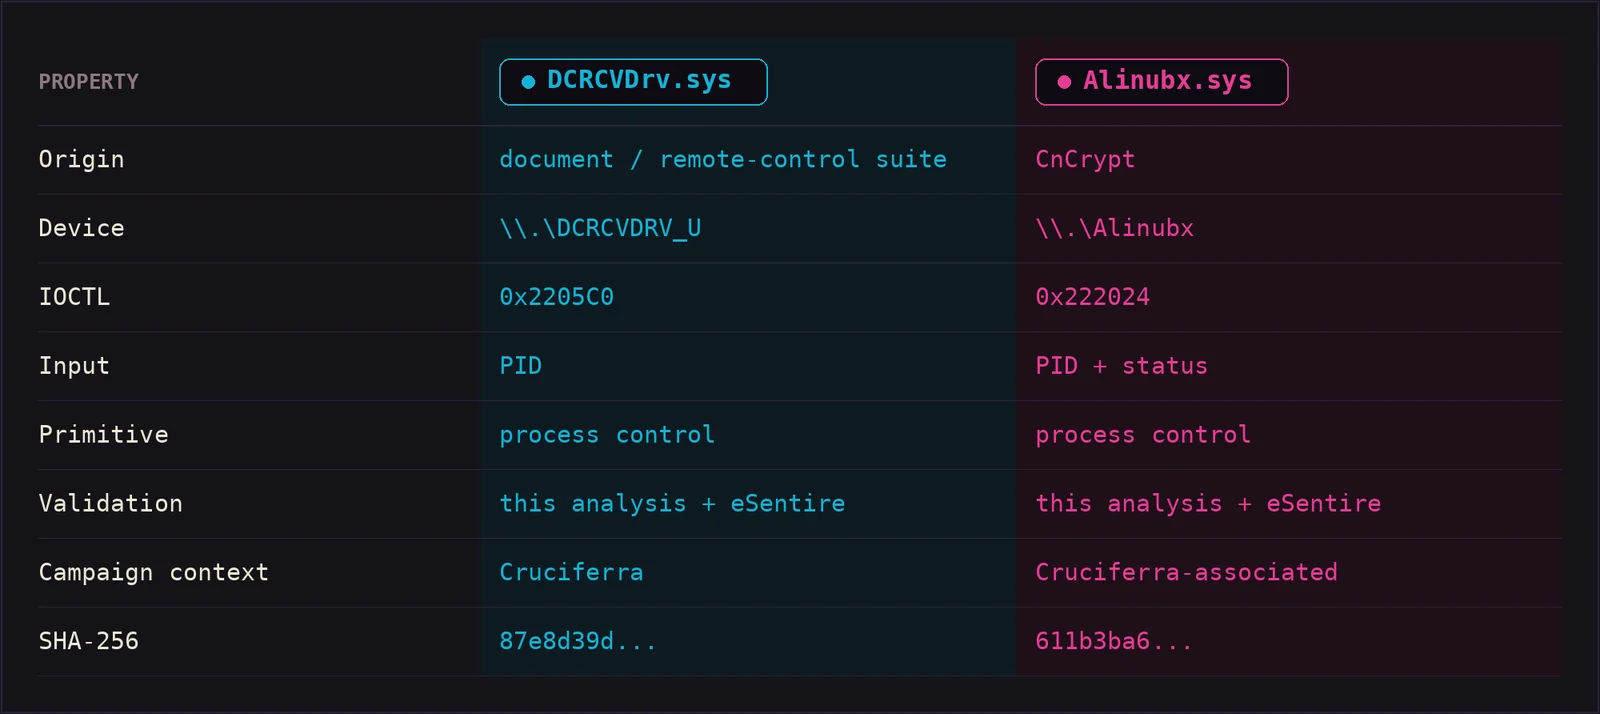 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 secrary/ssma
SSMA - Simple Static Malware Analyzer [This project is not maintained anymore by me]
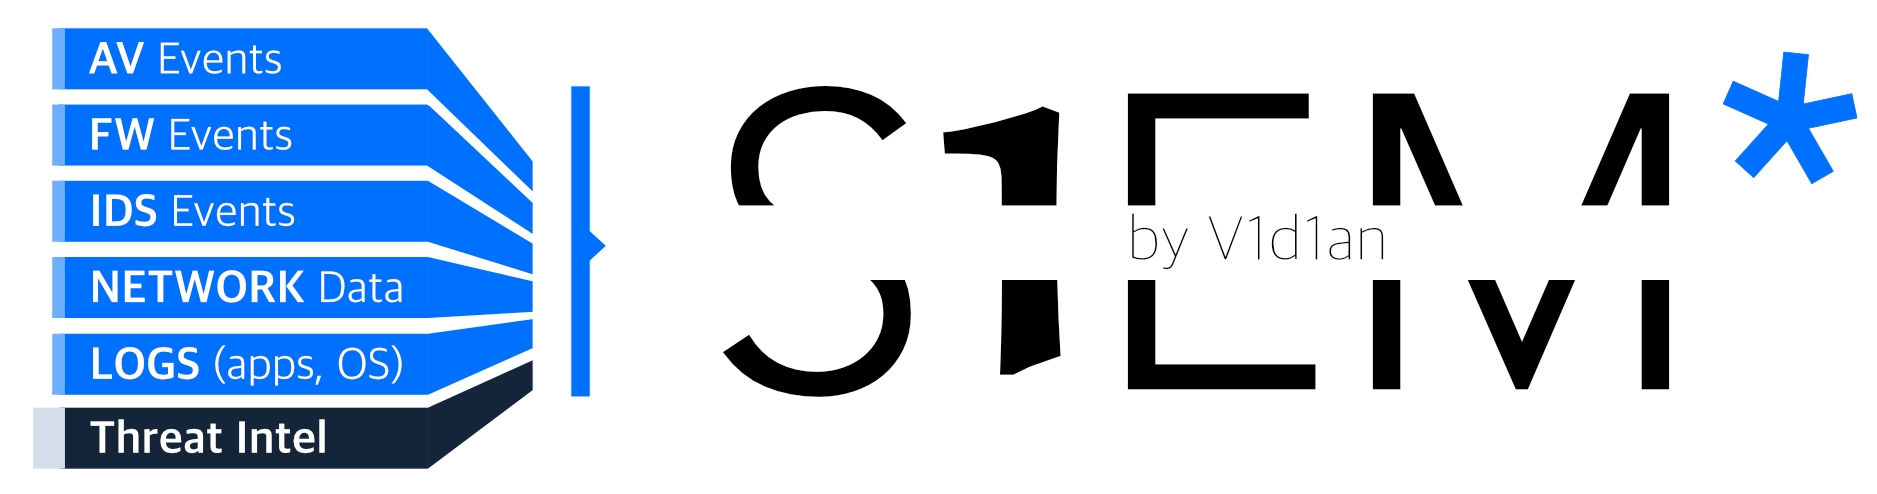 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…