

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
148 results
wazuh preview

wazuh

GitHubwazuh/wazuh

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17k20h 17m ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
binary-analysisdata-recoveryforensics+3
1321 month ago
diario-commandline-tools preview

diario-commandline-tools

GitHubelevenpaths/diario-commandline-tools

CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…

api-securityhash-analysisinformation-gathering+3
46 years ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k8 months ago
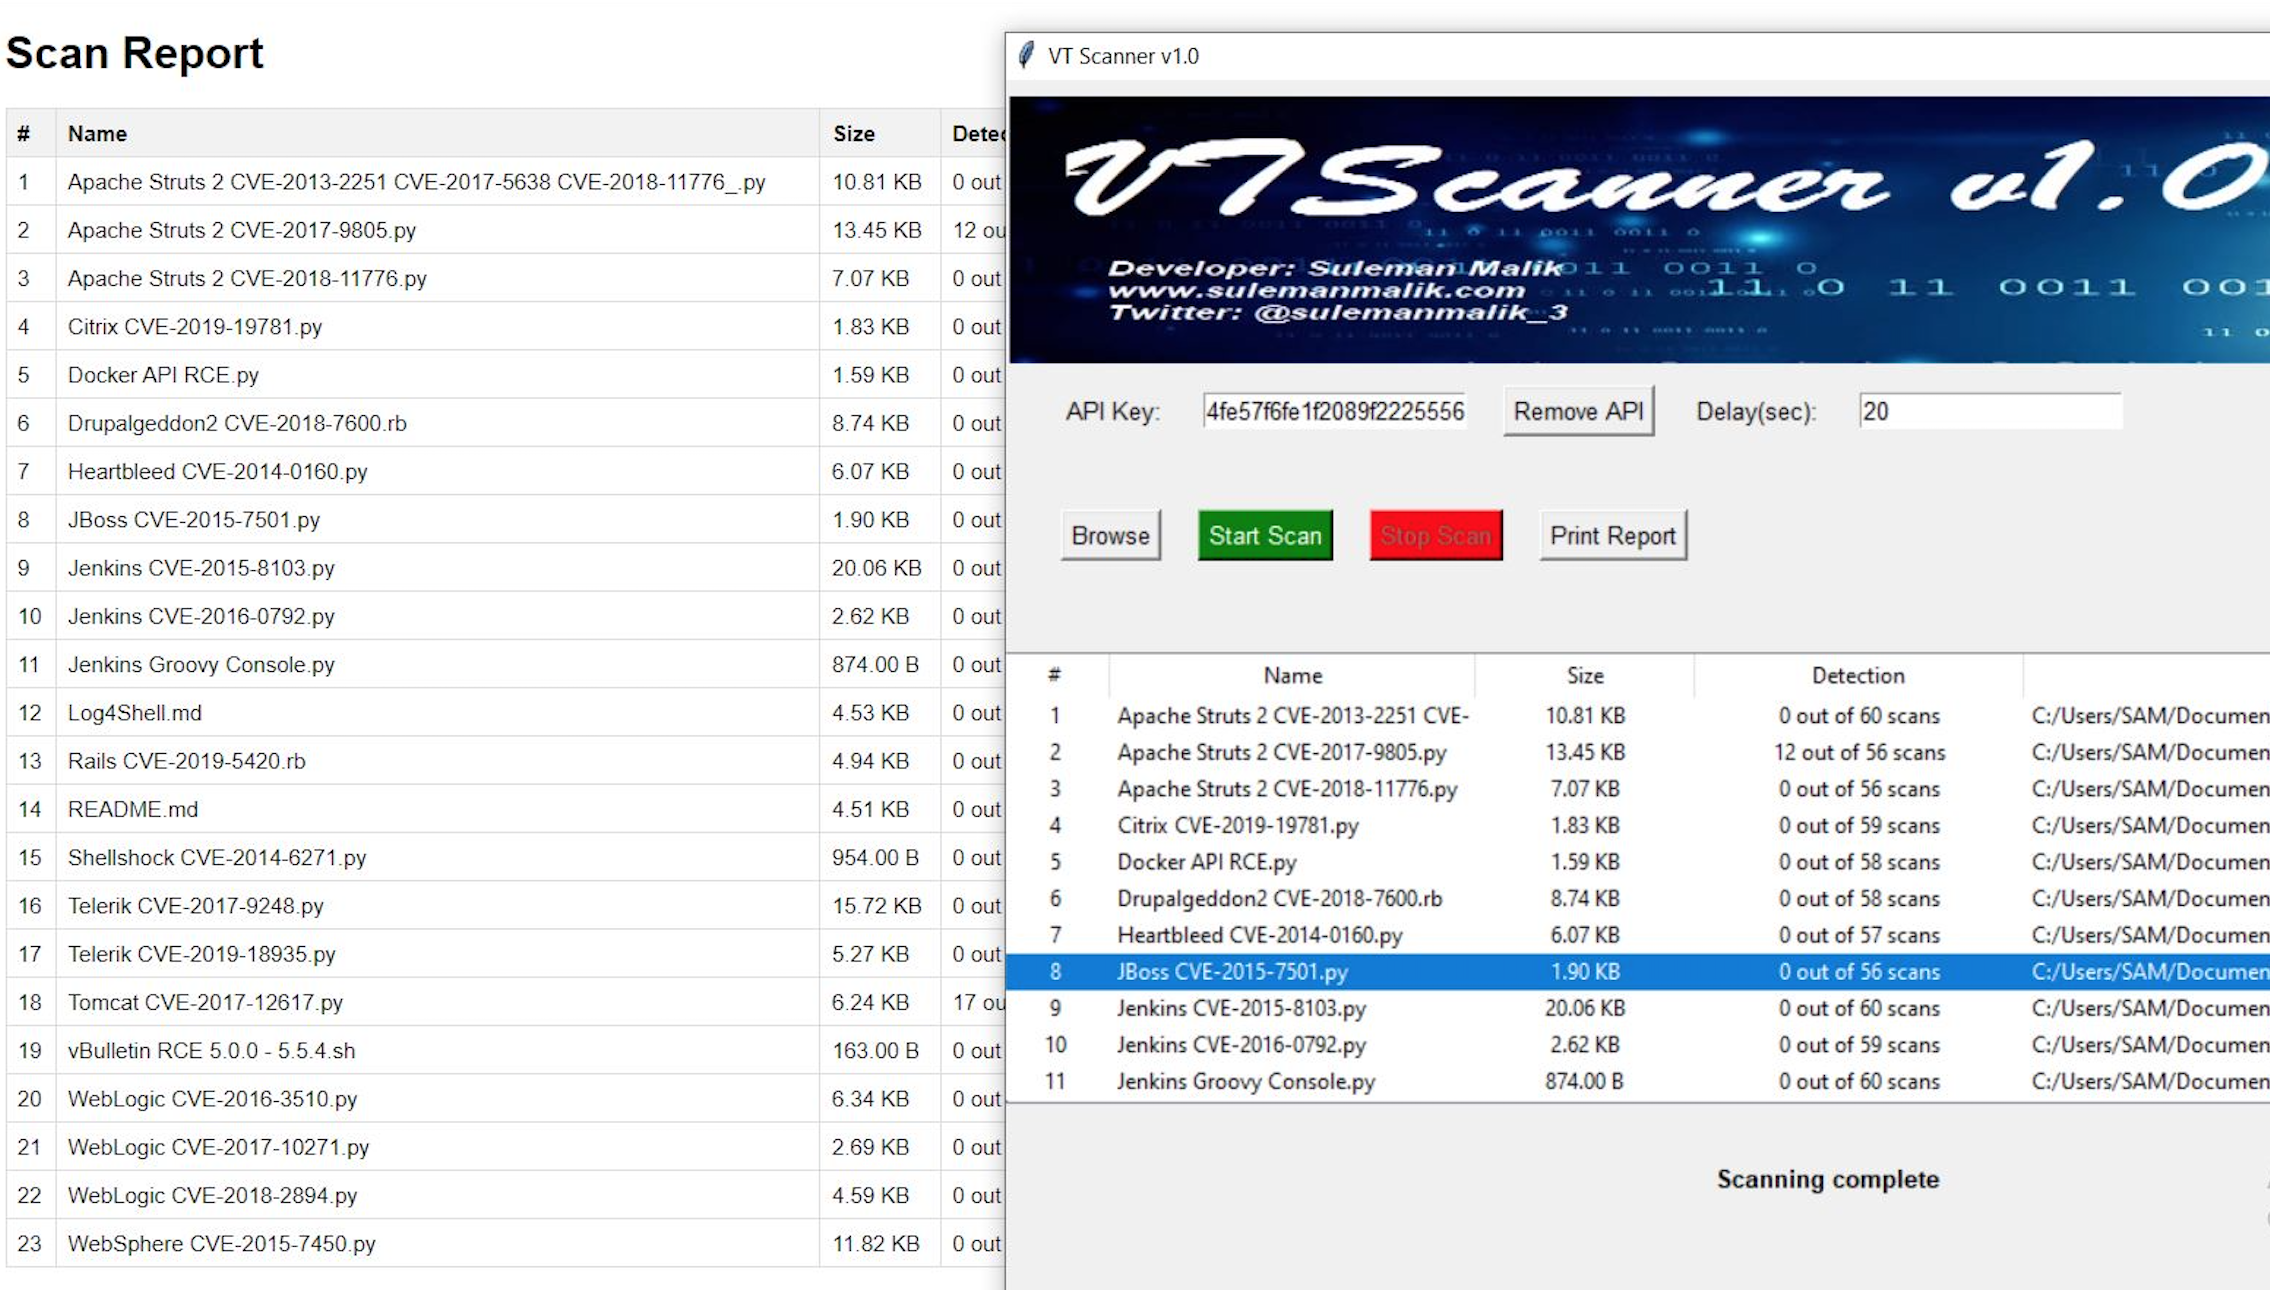
VTScanner preview

VTScanner

GitHubsamhaxr/vtscanner

A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.

hash-analysisinformation-gatheringmalware-analysis+1
1123 years ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
54.9k3 days ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
5 days ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k11 days ago
BlueBox preview

BlueBox

GitHubsvdwi/bluebox

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
ioc-managementmachine-learningmalware-analysis+4
504 years ago
SysTrace preview

SysTrace

GitHubtracebyte8/systrace

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…

anomaly-detectiondynamic-analysis-sandboxingmachine-learning+1
2424 days ago
Cryptolocker preview

Cryptolocker

GitHubajayrandhawa/cryptolocker

CryptoLocker is open source files encrypt-er. Crypto is developed in Visual C++. It has features encrypt all file, lock down the system and send keys…

educationencryption-decryption-toolsmalware-analysis
1432 months ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

digital-forensicsdisk-forensicsforensics+5
915 months ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
database-securitydigital-forensicsdisk-forensics+8
855 months ago
ExtensionSpoofer preview

ExtensionSpoofer

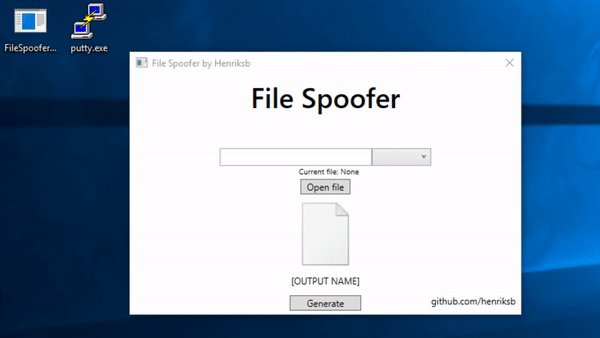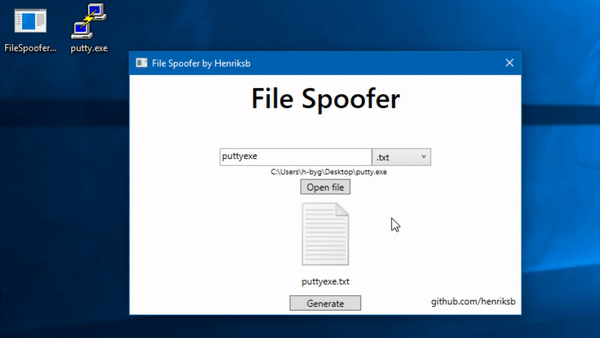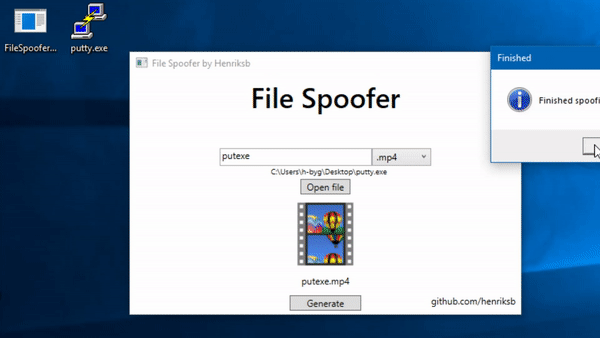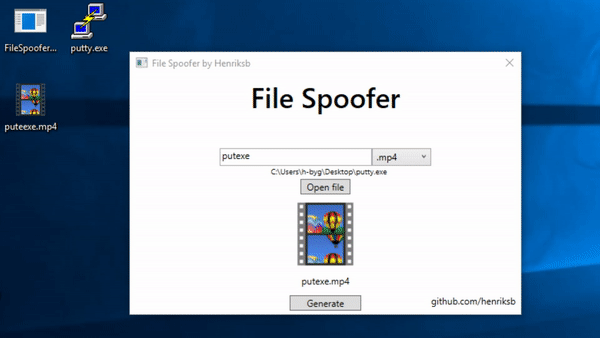
GitHubhenriksb/extensionspoofer

Spoof file icons and extensions in Windows
ids-ips-evasionimpersonation-toolsmalware-analysis+3
1871 month ago
Nodejs-Tracer preview

Nodejs-Tracer

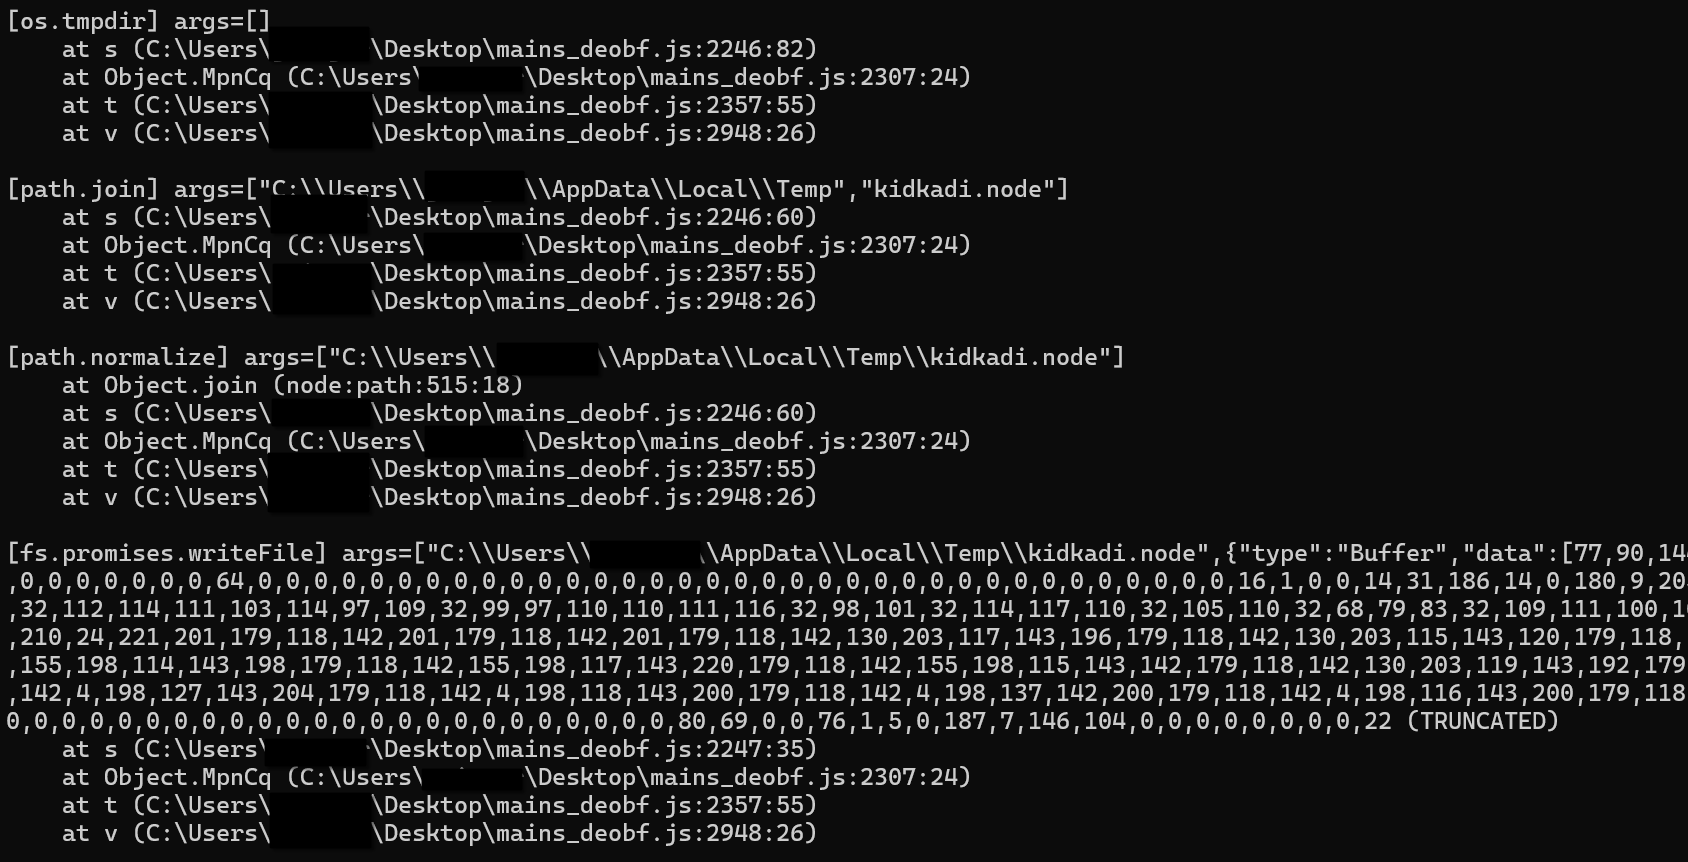
GitHubcheckpointsw/nodejs-tracer

Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
anti-botdynamic-analysis-sandboxingids-ips-evasion+3
818 months ago
DGA-Detection preview

DGA-Detection

GitHubphilarkwright/dga-detection

DGA Domain Detection using Bigram Frequency Analysis

dns-analysismachine-learningmalware-analysis+1
569 years ago
Docx-Exploit-2021 preview

Docx-Exploit-2021

GitHublazarusreborn/docx-exploit-2021

This docx exploit uses res files inside Microsoft .docx file to execute malicious files. This exploit is related to CVE-2021-40444
command-and-controlexploitationmalware-analysis+3
54 years ago
CVE-2023-38831 preview

CVE-2023-38831

GitHubmishra0230/cve-2023-38831

CVE-2023-38831 - WinRAR

binary-exploitationeducationexploitation+8
8 months ago
Previous12…9Next