Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
spectrIDA-Reverse_Engineering_Stack preview

spectrIDA-Reverse_Engineering_Stack

GitHubggfuchsi-oss/spectrida-reverse_engineering_stack

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

ai-assisted-reversingbinary-analysisctf+8
63
2 months ago
Phantom-Evasion-Loader preview

Phantom-Evasion-Loader

GitHubjm00nj/phantom-evasion-loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

binary-exploitationcommand-and-controleducation+6
1132 months ago
capstone preview

capstone

GitHubcapstone-engine/capstone

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.0k22h 41m ago
Simple-Polymorphic-Engine-SPE32 preview

Simple-Polymorphic-Engine-SPE32

GitHubpelock/simple-polymorphic-engine-spe32

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

encryption-decryption-toolsmalware-analysisreverse-engineering+1
1583 years ago
Sandb0x-Xtract0r preview

Sandb0x-Xtract0r

GitHubdarnellwashingtonjr94-art/sandb0x-xtract0r

Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…

dynamic-analysis-sandboxingmalware-analysismemory-forensics+3
39 days ago
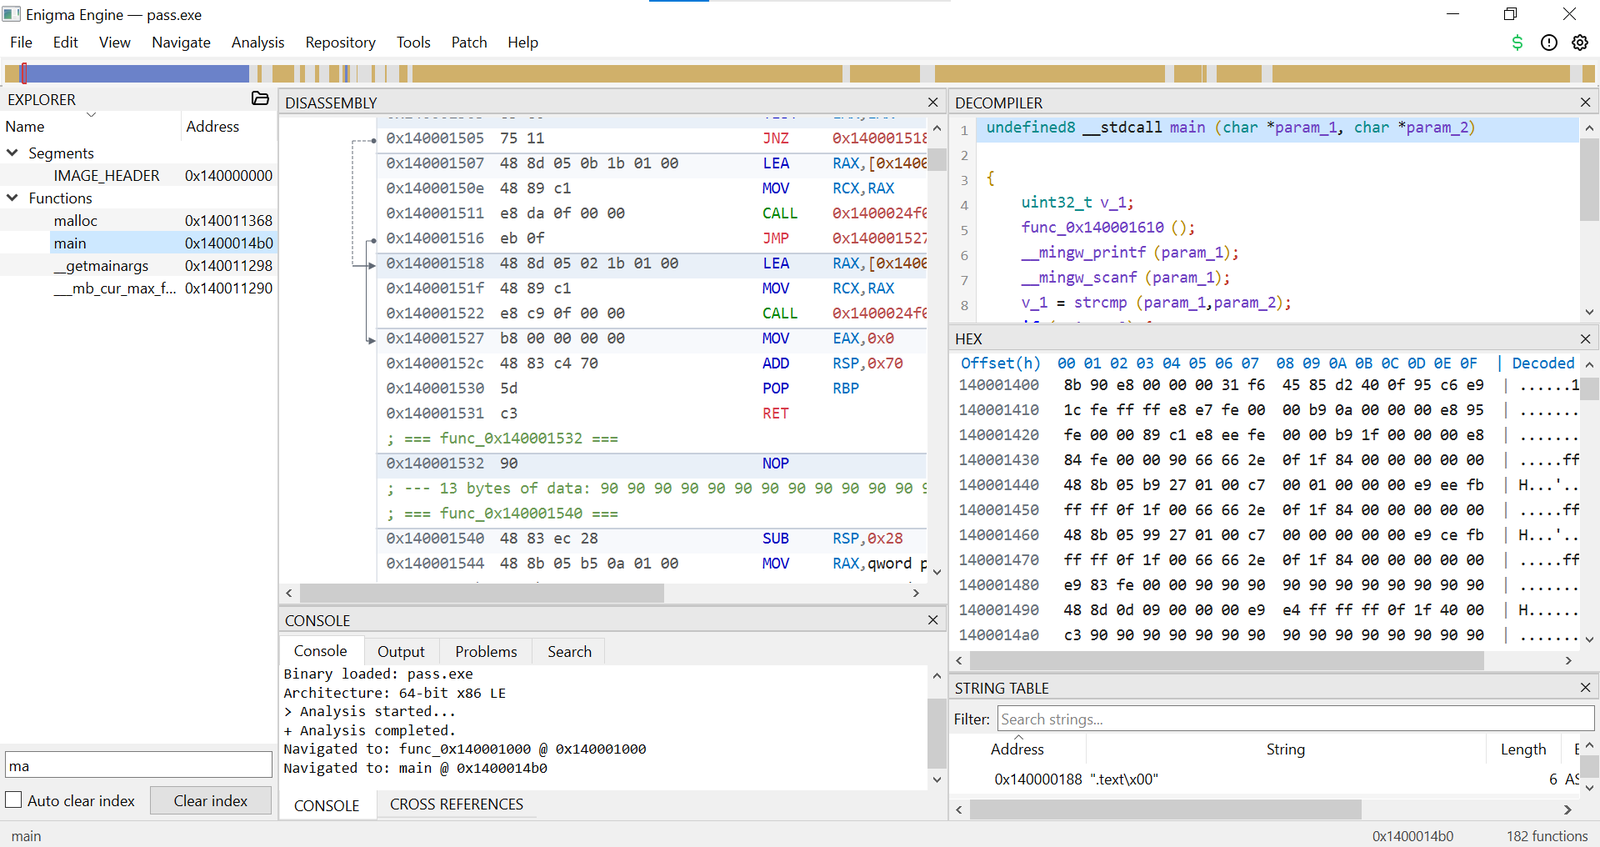
Enigma preview

Enigma

GitHubbunnybuzz/enigma

Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…

ai-assisted-reversingbinary-analysisdebuggers+3
617 days ago
flare-emu preview

flare-emu

GitHubmandiant/flare-emu

Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
9551 year ago
clamav preview

clamav

GitHubcisco-talos/clamav

Open-source antivirus engine for detecting trojans, viruses, and malware via signature-based scanning; includes a daemon, on-demand CLI, and…

defensive-toolsemail-securitymalware-analysis
7.3k1 month ago
TrueVerdict preview

TrueVerdict

GitHubprox0959/trueverdict

Zero-dependency Windows PE provenance and false-positive reduction engine (Embedded Authenticode + OS Security Catalogs, Rich Header ROL32…

binary-analysisdefensive-toolsdigital-forensics+6
12 days ago
cheat-engine-undetectable preview

cheat-engine-undetectable

GitHubgmh5225/cheat-engine-undetectable

Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).

binary-exploitationeducationexploitation+3
1 month ago
quark-engine preview

quark-engine

GitHubev-flow/quark-engine

Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…

android-securitydynamic-analysis-sandboxingmalware-analysis+3
1.7k5 days ago
Crawlector preview

Crawlector

GitHubmfmokbel/crawlector

Crawlector is a threat hunting framework designed for scanning websites for malicious objects.

crawlerinformation-gatheringmalware-analysis+5
1239 months ago
shredder-rs preview

shredder-rs

GitHubzx0cf1/shredder-rs

A high-fidelity x86_64 polymorphic mutation engine focused on instruction-level fragmentation and context preservation.

binary-analysiseducationexploitation+4
1128 months ago
CVE-2026-2441 preview

CVE-2026-2441

GitHubmartinastarone/cve-2026-2441

Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…

binary-exploitationcommand-and-controleducation+8
4 months ago
iocx preview

iocx

GitHubiocx-dev/iocx

An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…

binary-analysisdevsecopsforensics+6
2920 days ago
Cmulator preview
Archived

Cmulator

GitHubcoldzer0/cmulator

Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…

binary-analysisdebuggersdynamic-analysis-sandboxing+4
3044 years ago
YARAify preview

YARAify

GitHubabusech/yaraify

Open YARA scan- and search engine

hash-analysismalware-analysisstatic-analysis+1
271 year ago
Cortex preview

Cortex

GitHubthehive-project/cortex

Cortex: a Powerful Observable Analysis and Active Response Engine

digital-forensicsincident-responseinformation-gathering+5
1.6k3 months ago
Previous123Next