
cheat-engine-undetectable
 gmh5225/cheat-engine-undetectable
Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
binary-exploitationeducationexploitation+3
1
gmh5225/cheat-engine-undetectableAcademic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 racoten/reflectivepluginloader
Reflective PE mapper and evasion-hardened module stomping engine for Windows x64
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 cisco-talos/clamav
Open-source antivirus engine for detecting trojans, viruses, and malware via signature-based scanning; includes a daemon, on-demand CLI, and…
 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
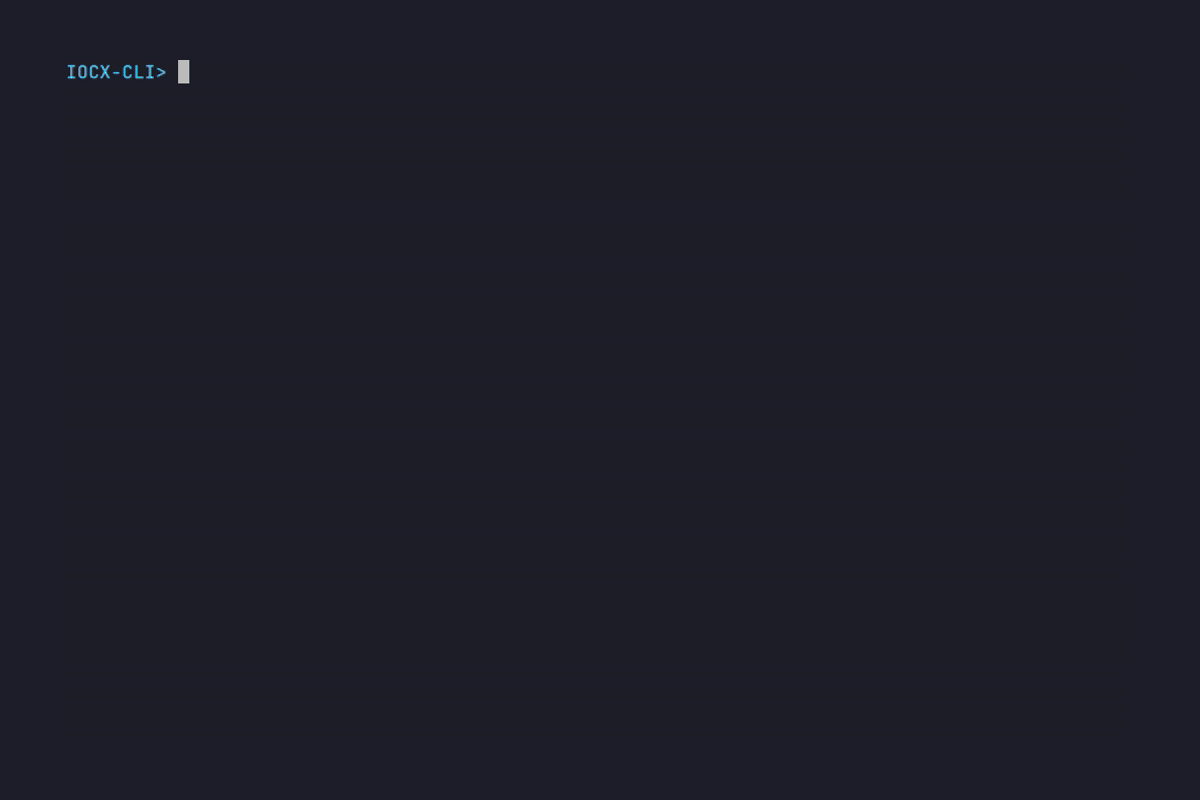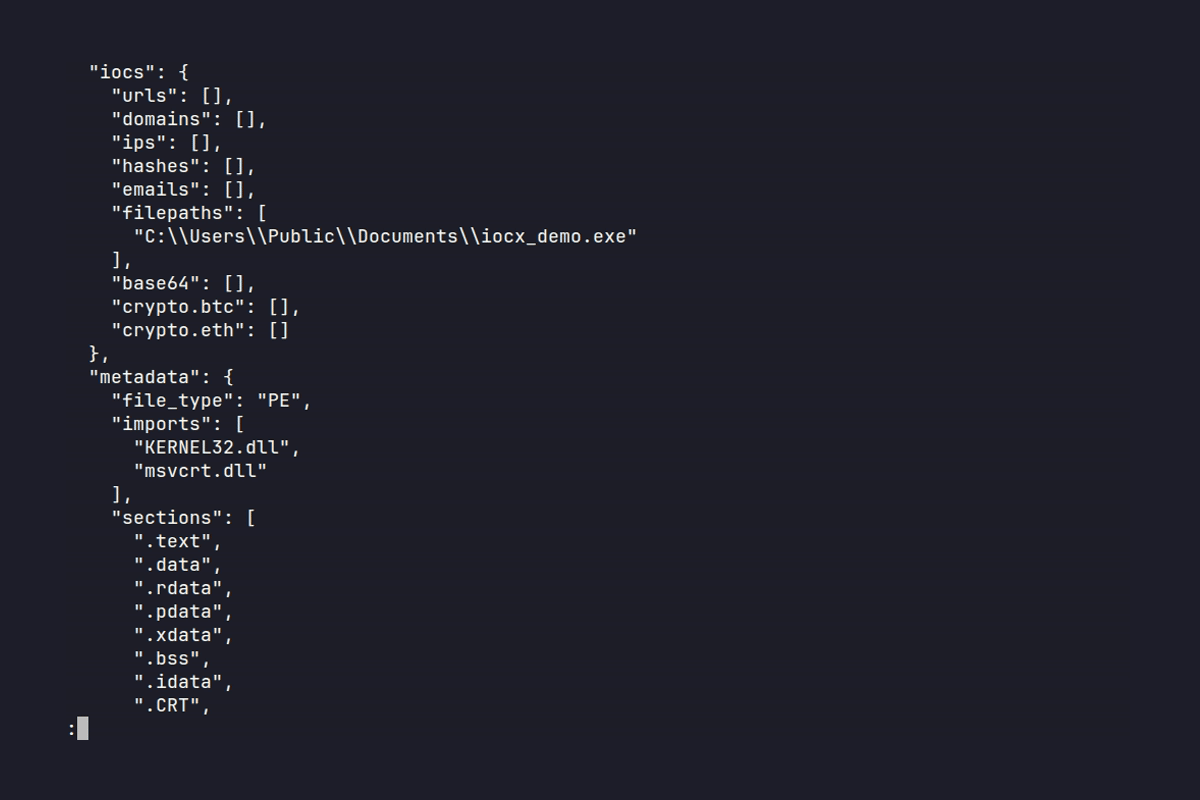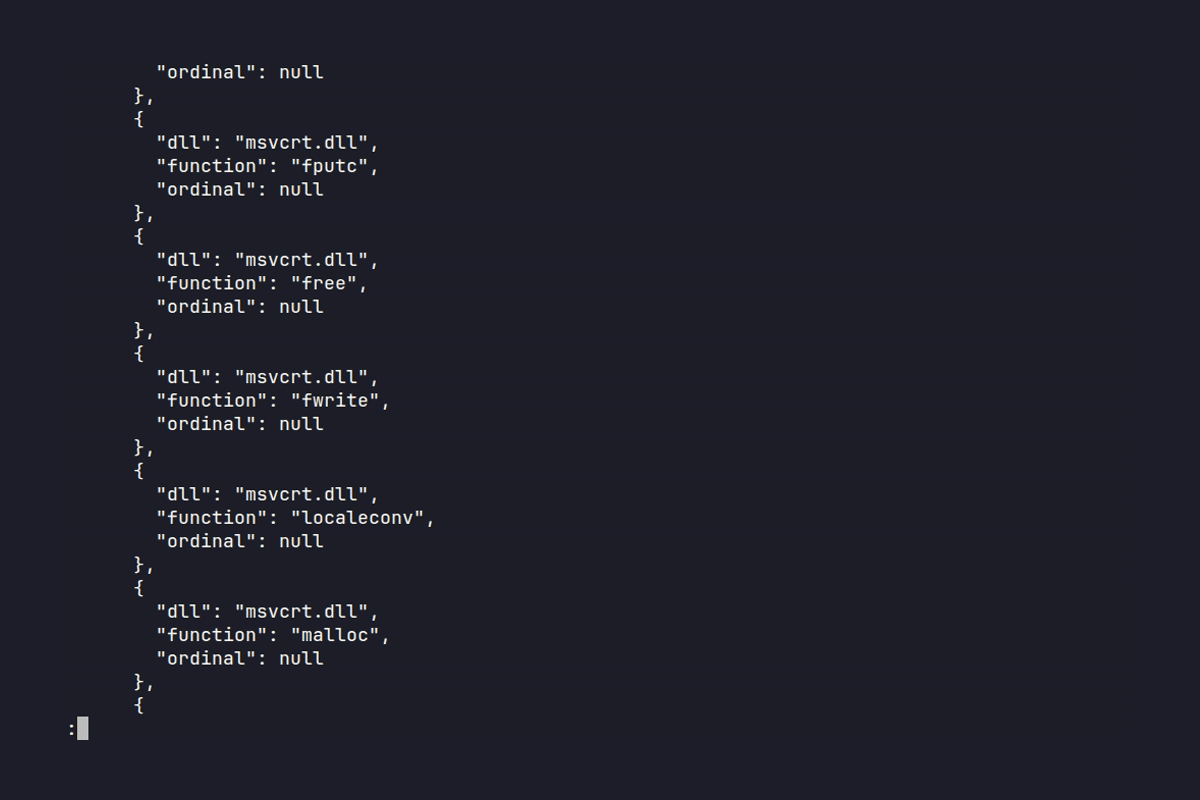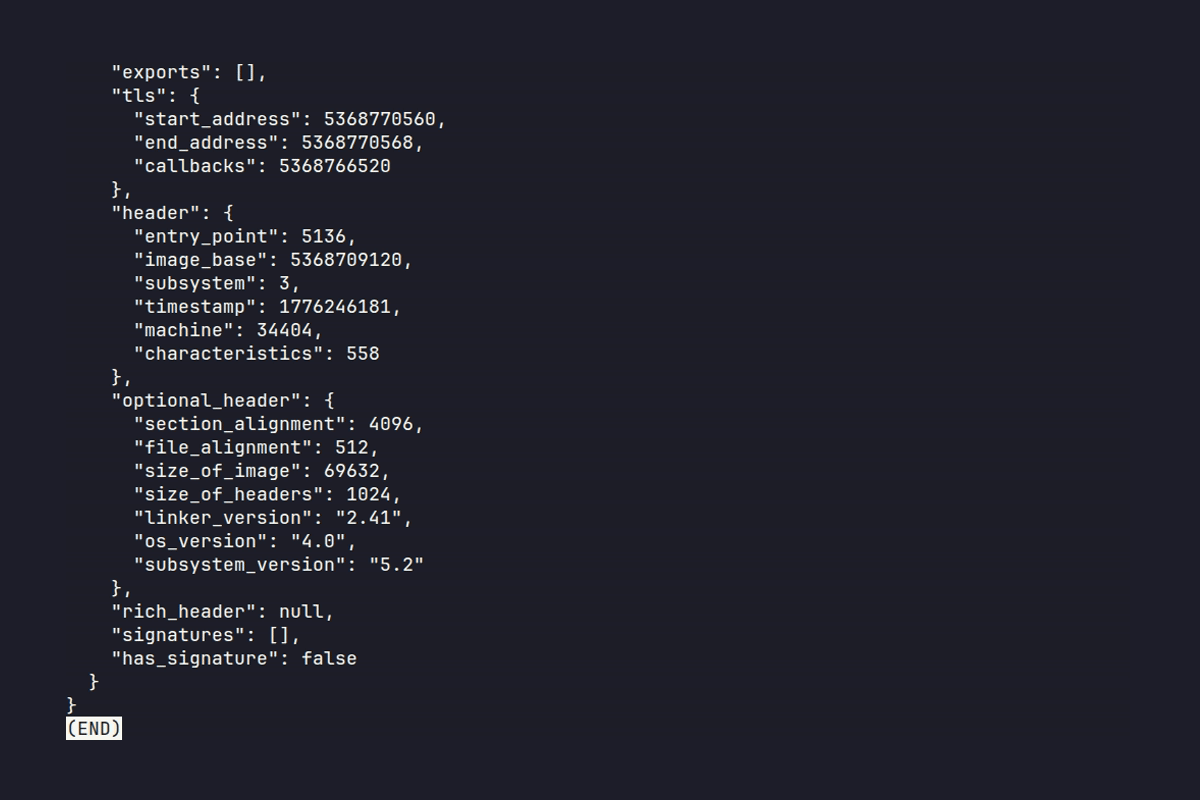 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 dwexi/entropystrip
Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine
 martinastarone/cve-2026-2441
Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering