

Awesome-Hacking
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
ctfcurated-resourceseducation+7
124.1k
hack-with-github/awesome-hackingA collection of various awesome lists for hackers, pentesters and security researchers
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

 nccgroup/pybeacon
A collection of scripts for dealing with Cobalt Strike beacons in Python
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 doctorwebltd/malware-iocs
Curated Indicators of Compromise (IOCs) from Doctor Web malware investigations, published for threat intelligence, detection engineering, and…
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 mentebinaria/retoolkit
Pre-configured bundle of reverse engineering and malware analysis tools for x86/x64 Windows systems, with desktop integration and plugin-ready…
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 ashishb/android-security-awesome
A collection of android security related resources
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
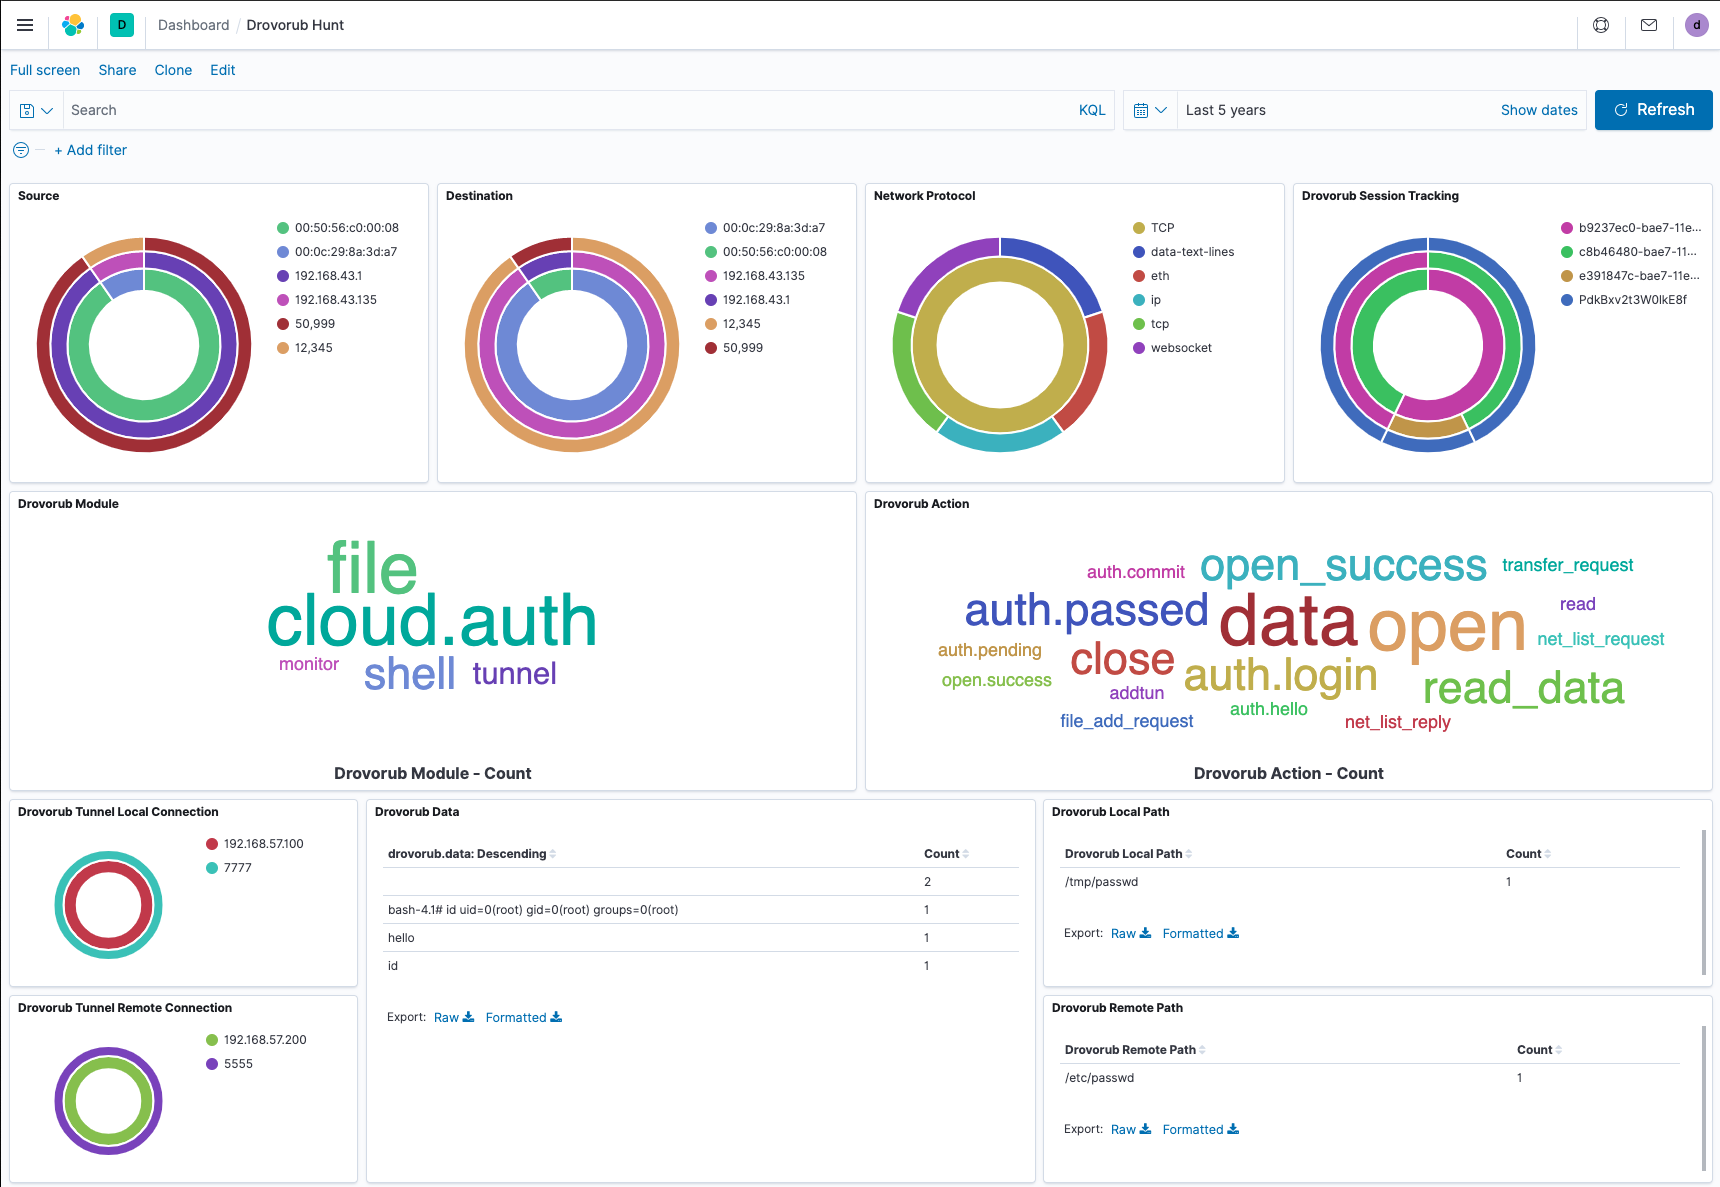 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 vc0rexor/quick-analysis
Provides rapid triage and summarization of malware samples and threat indicators, highlighting key behavioral and contextual details for analysts.