
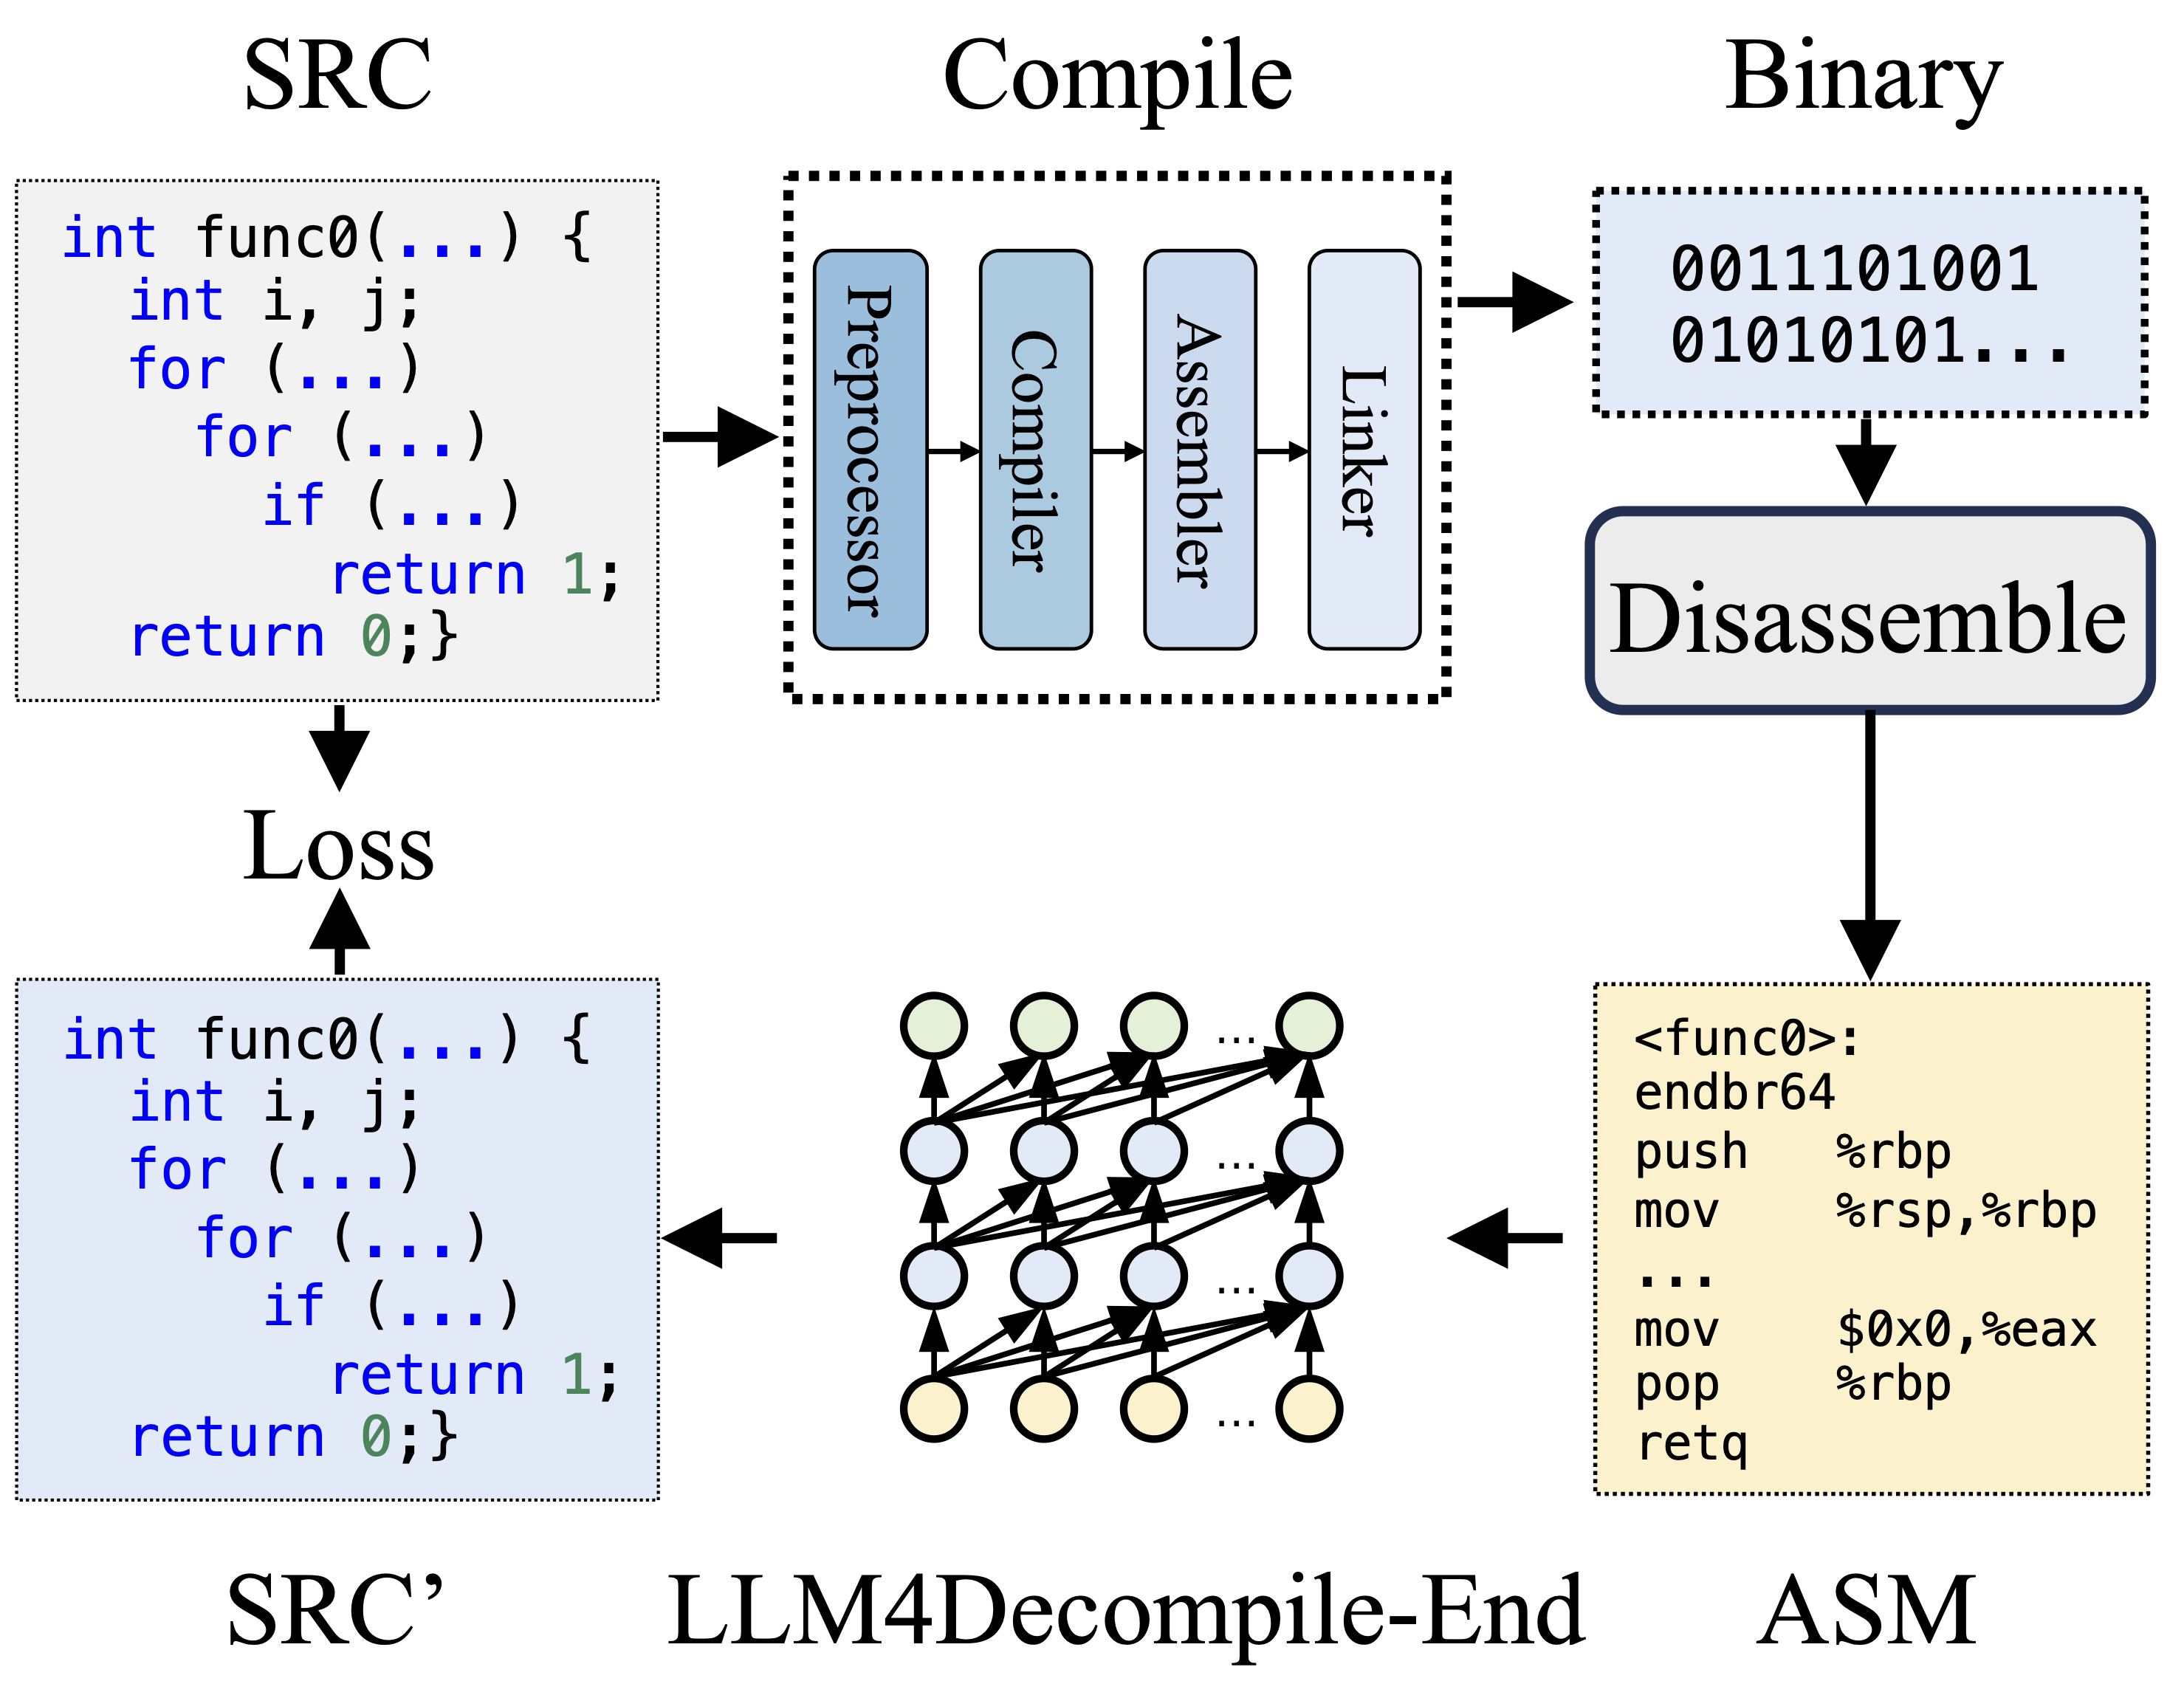
LLM4Decompile
 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
ai-assisted-reversingbinary-analysismachine-learning+1
7.0k
albertan017/llm4decompileReverse Engineering: Decompiling Binary Code with Large Language Models
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
 jhuapl/codecut
A Ghidra plugin for locating object file boundaries.
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
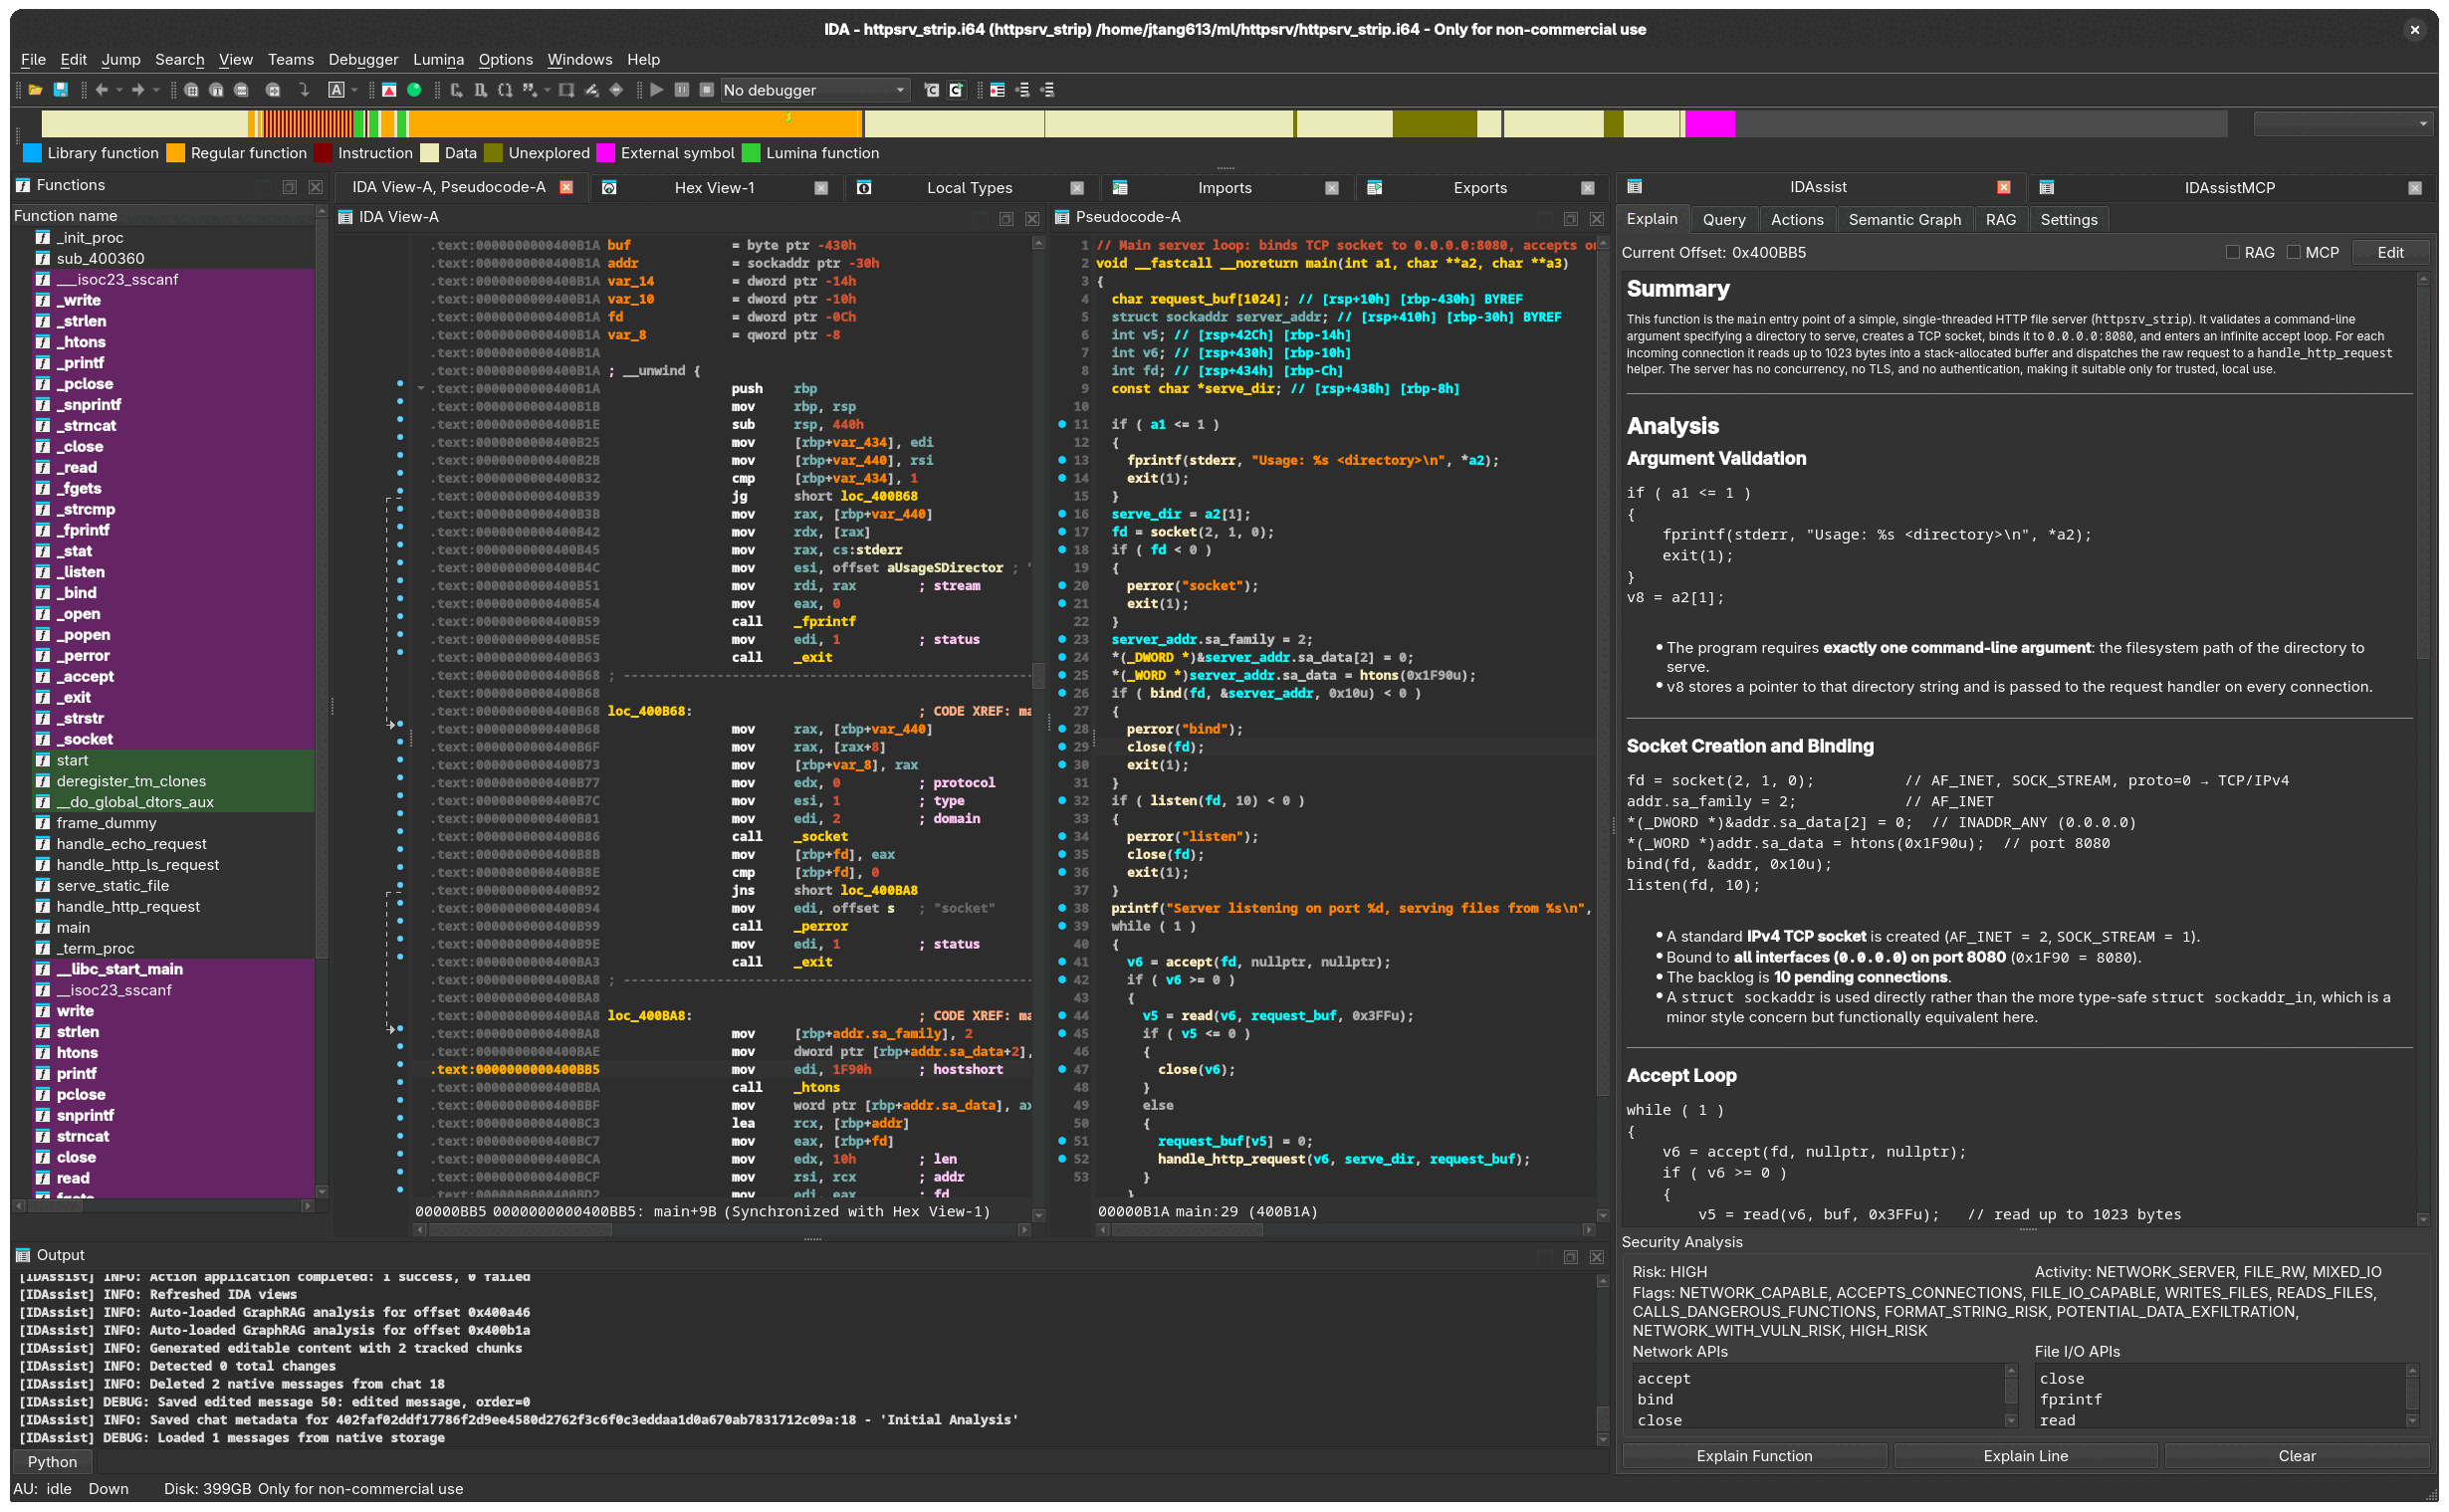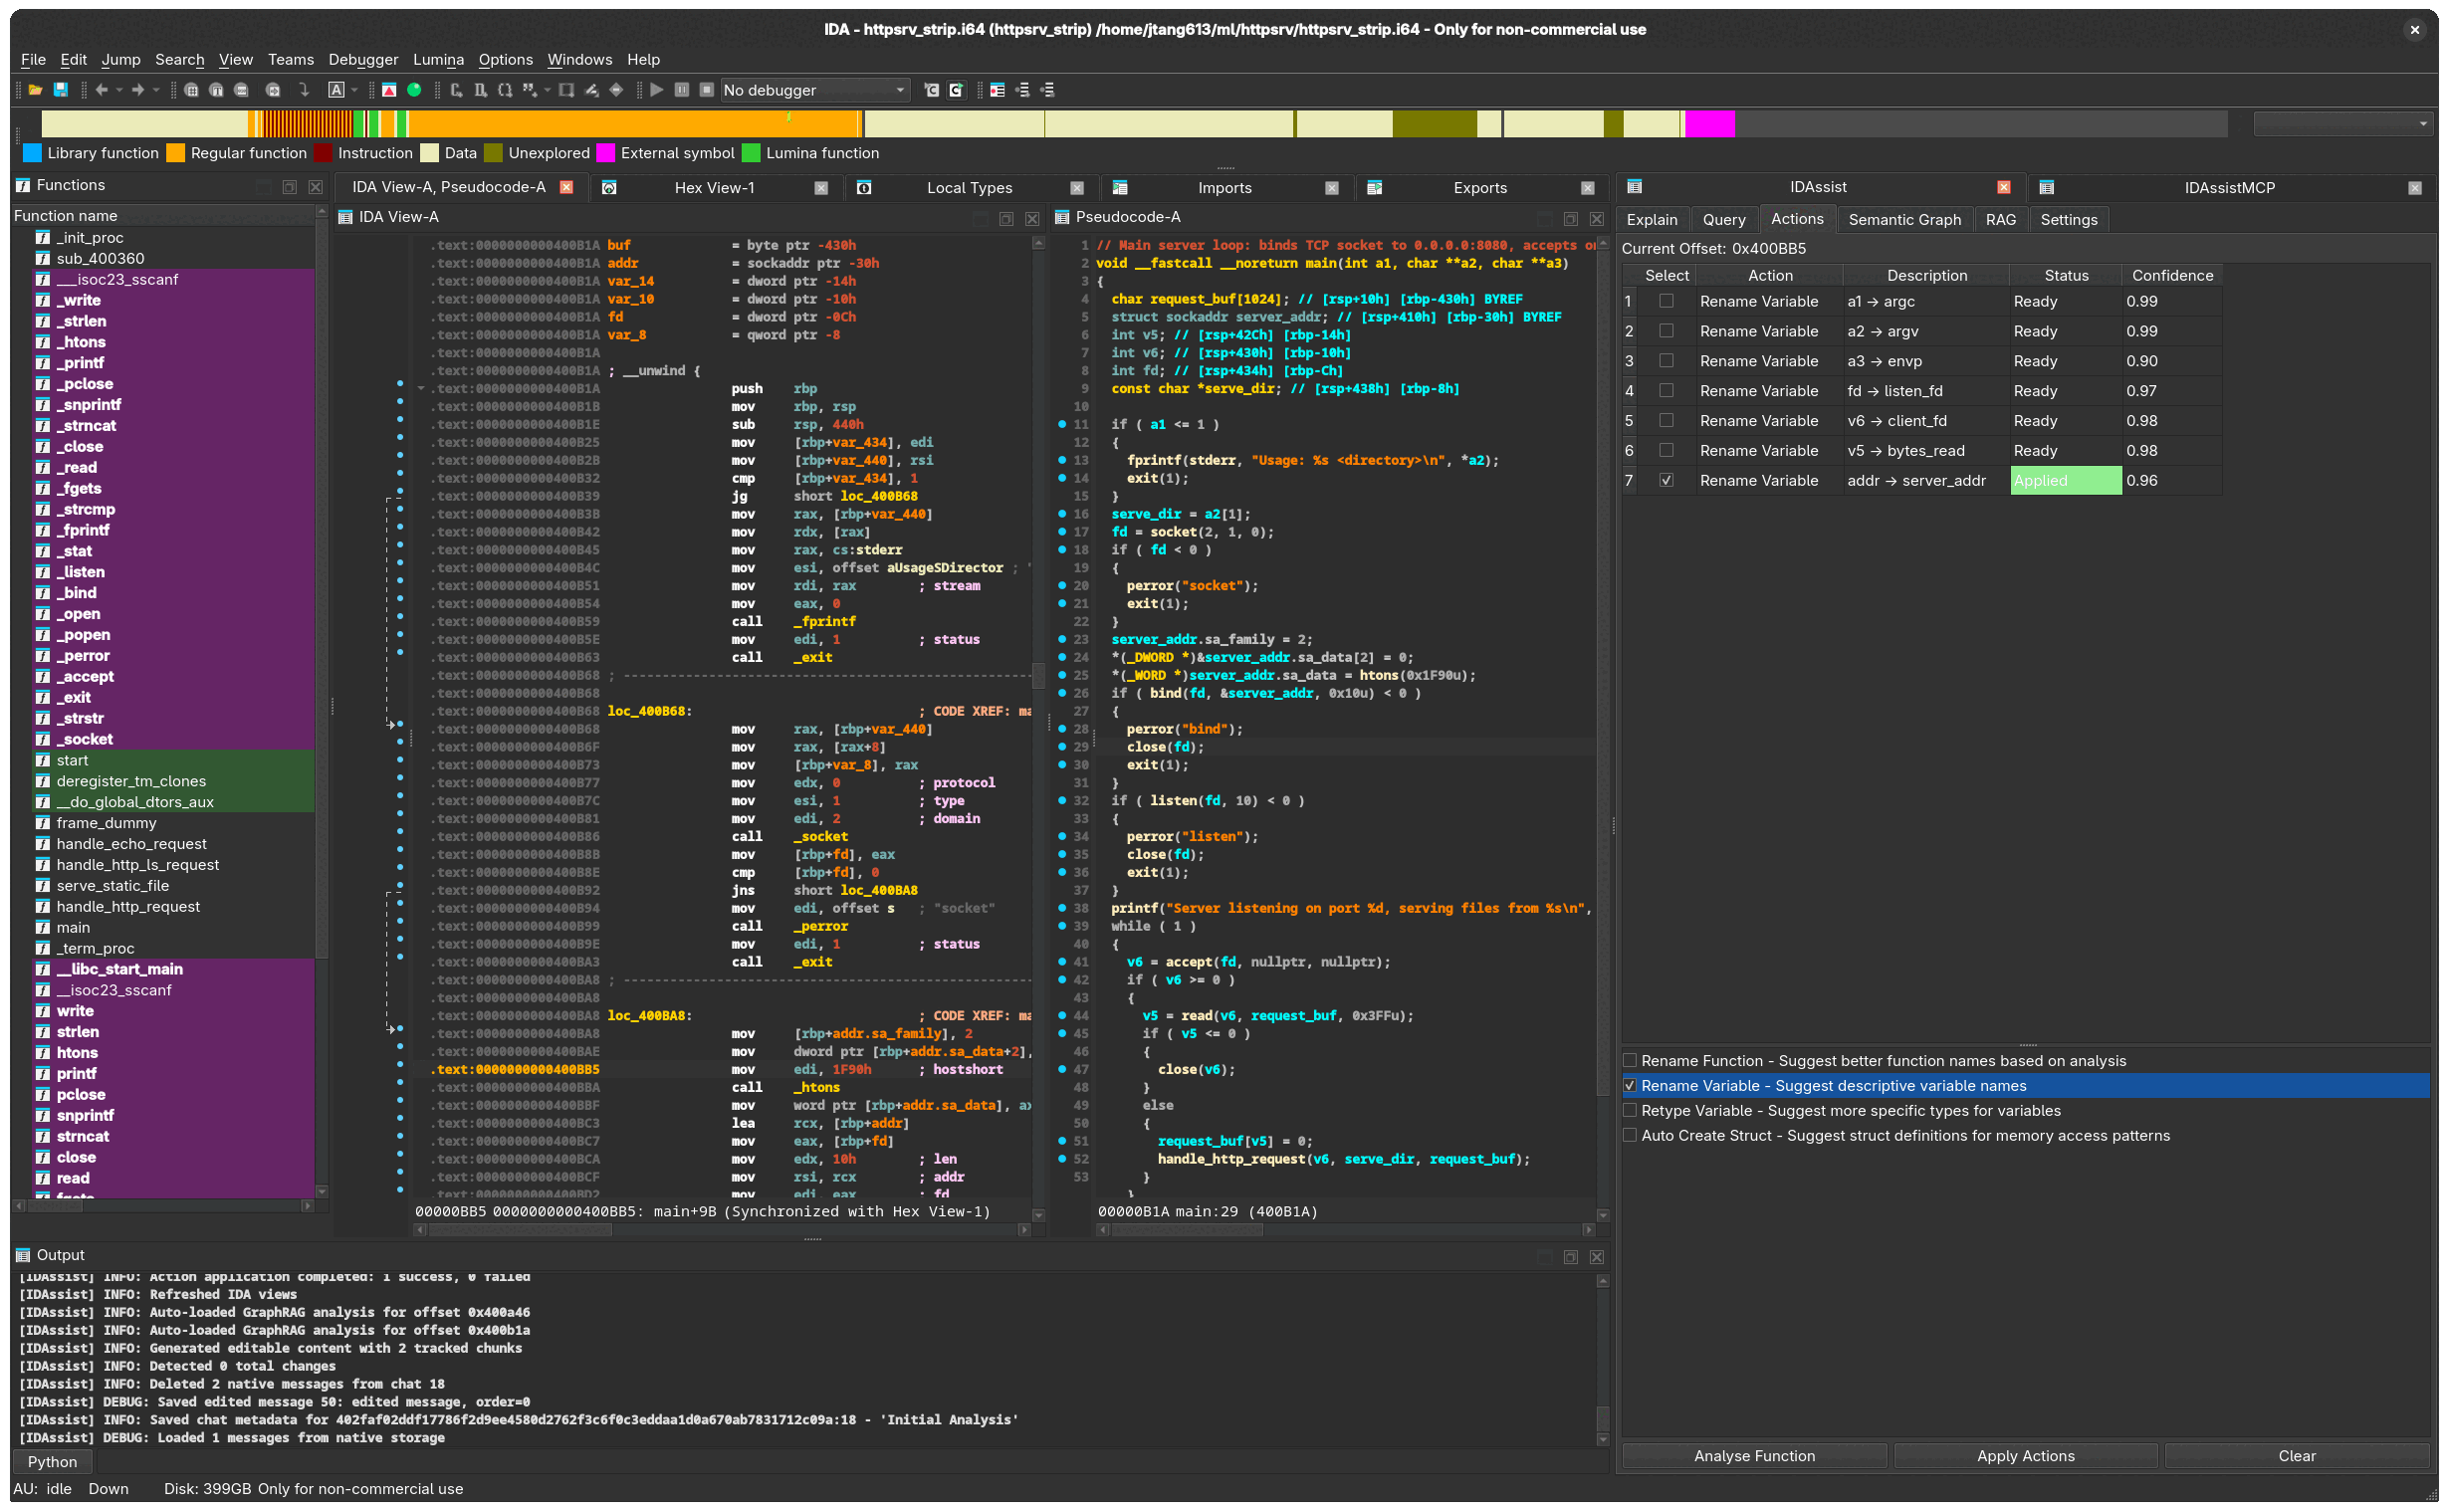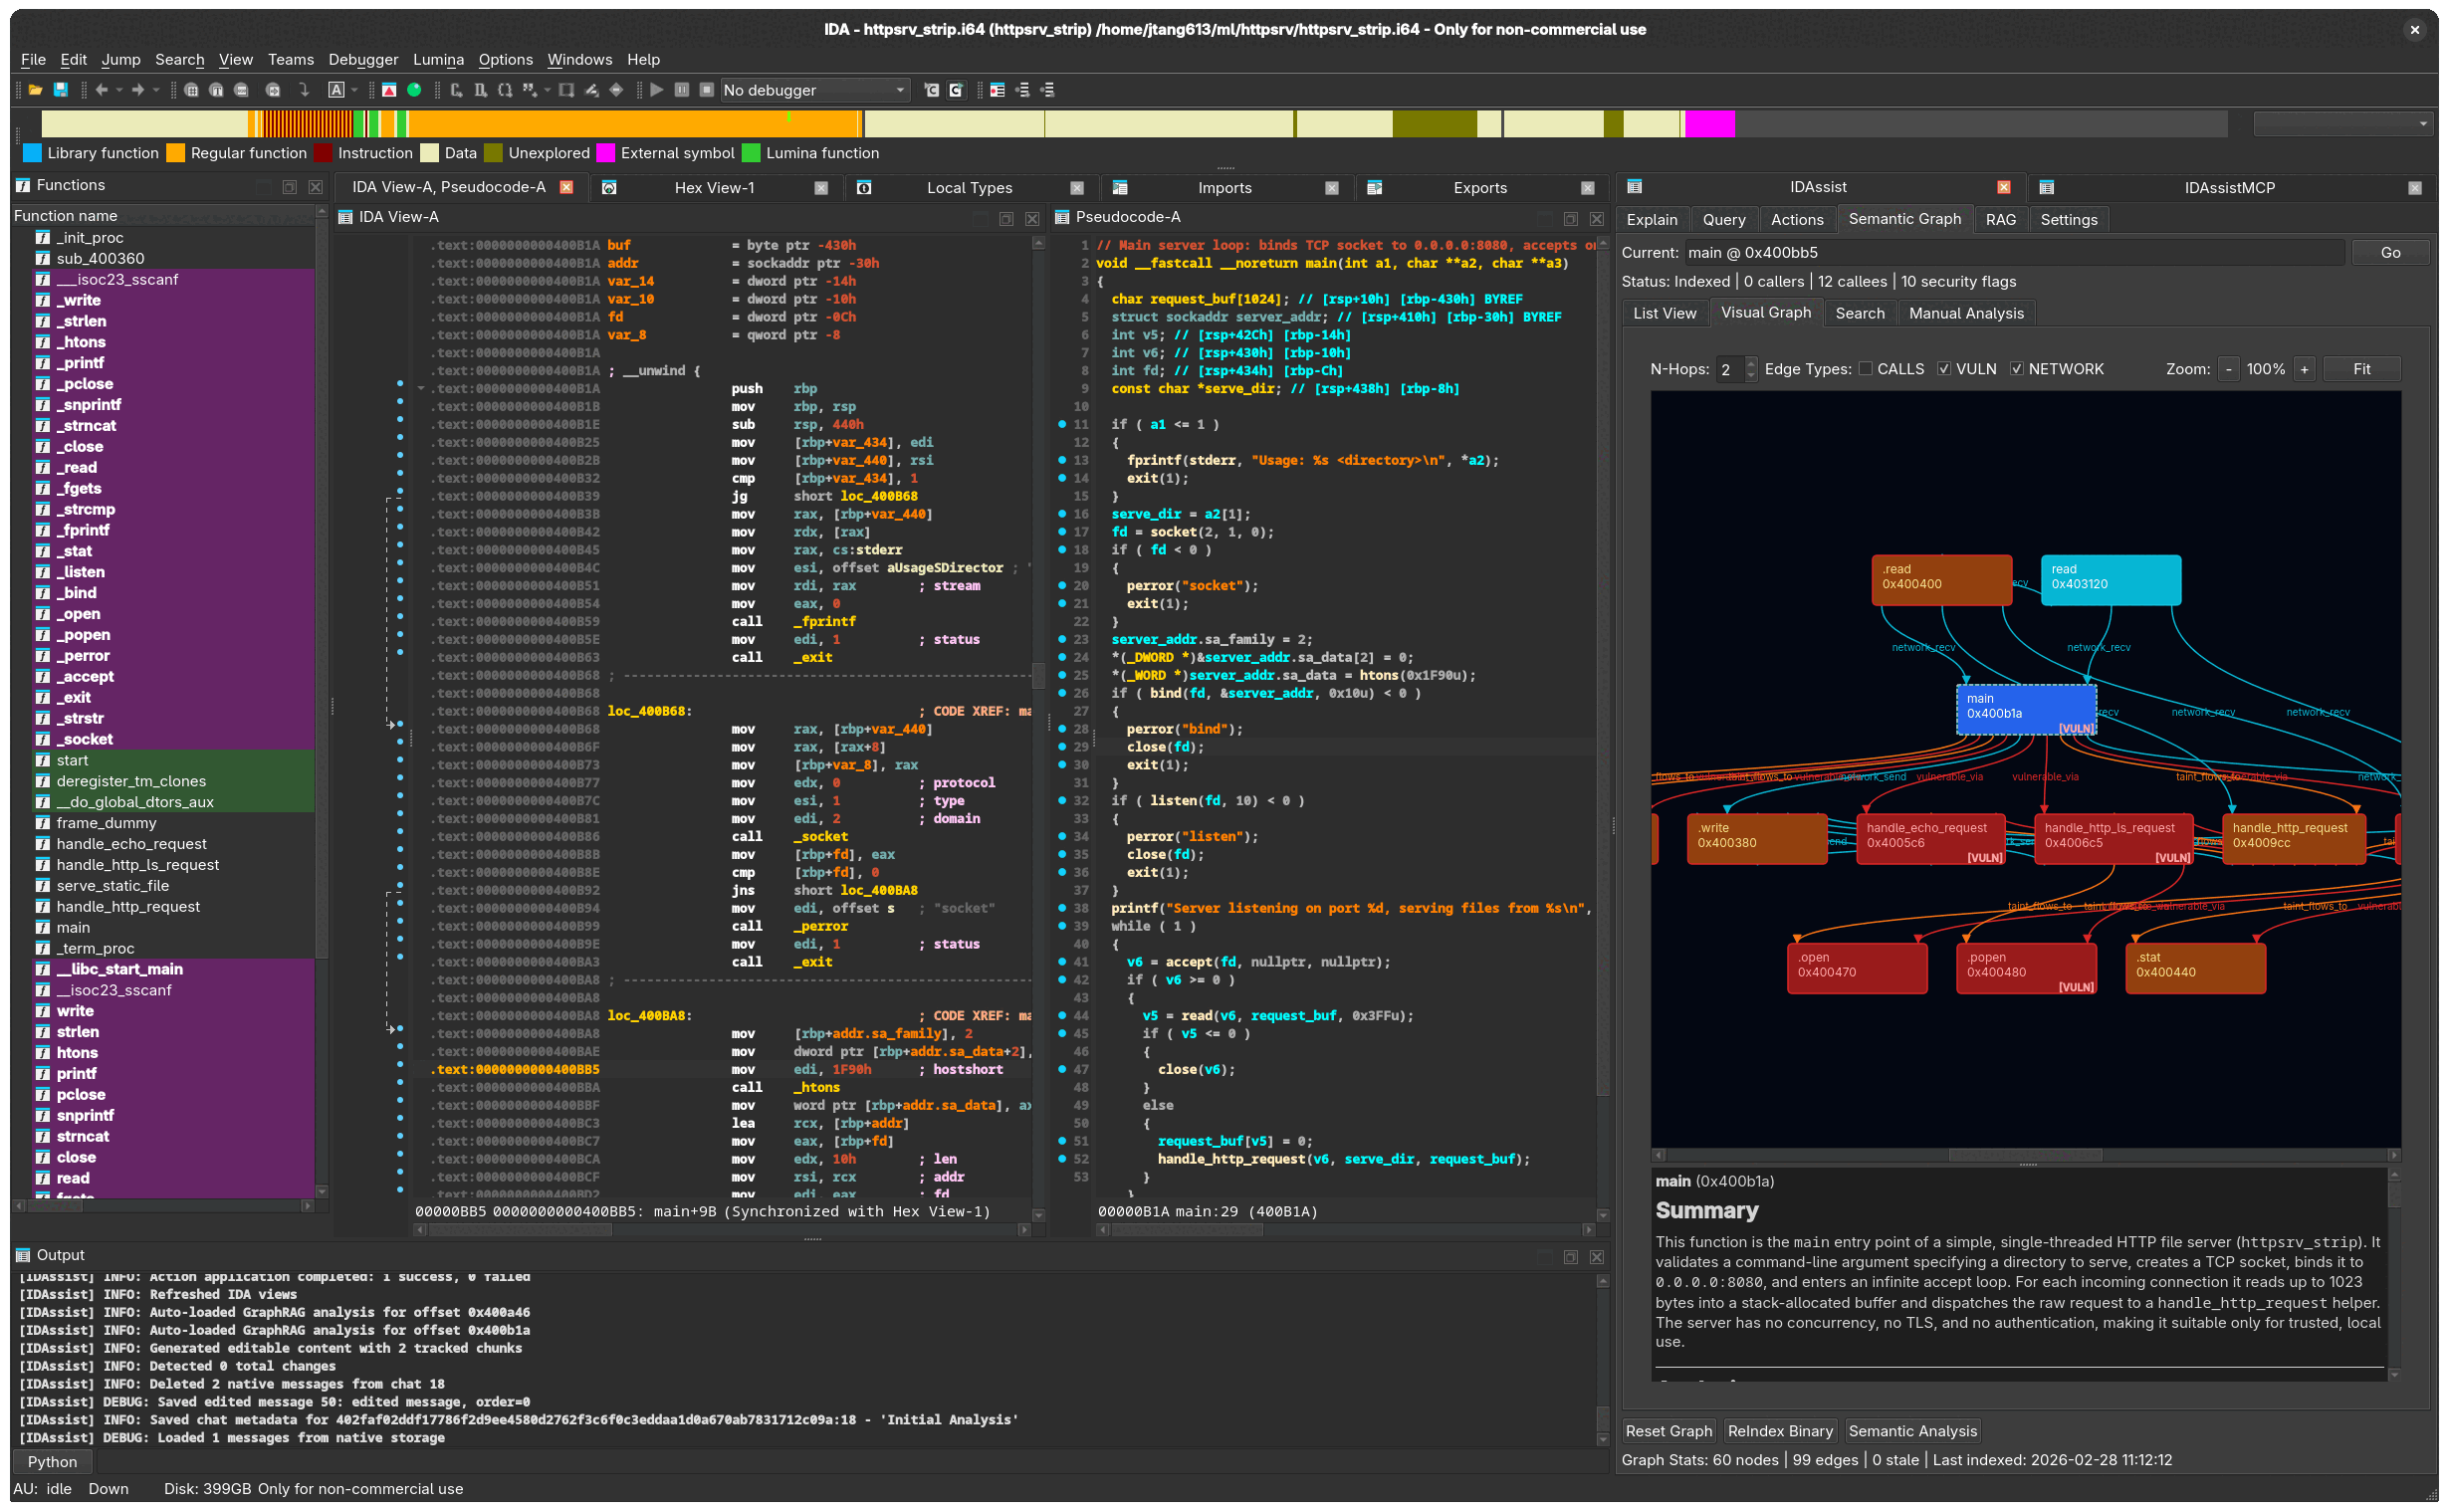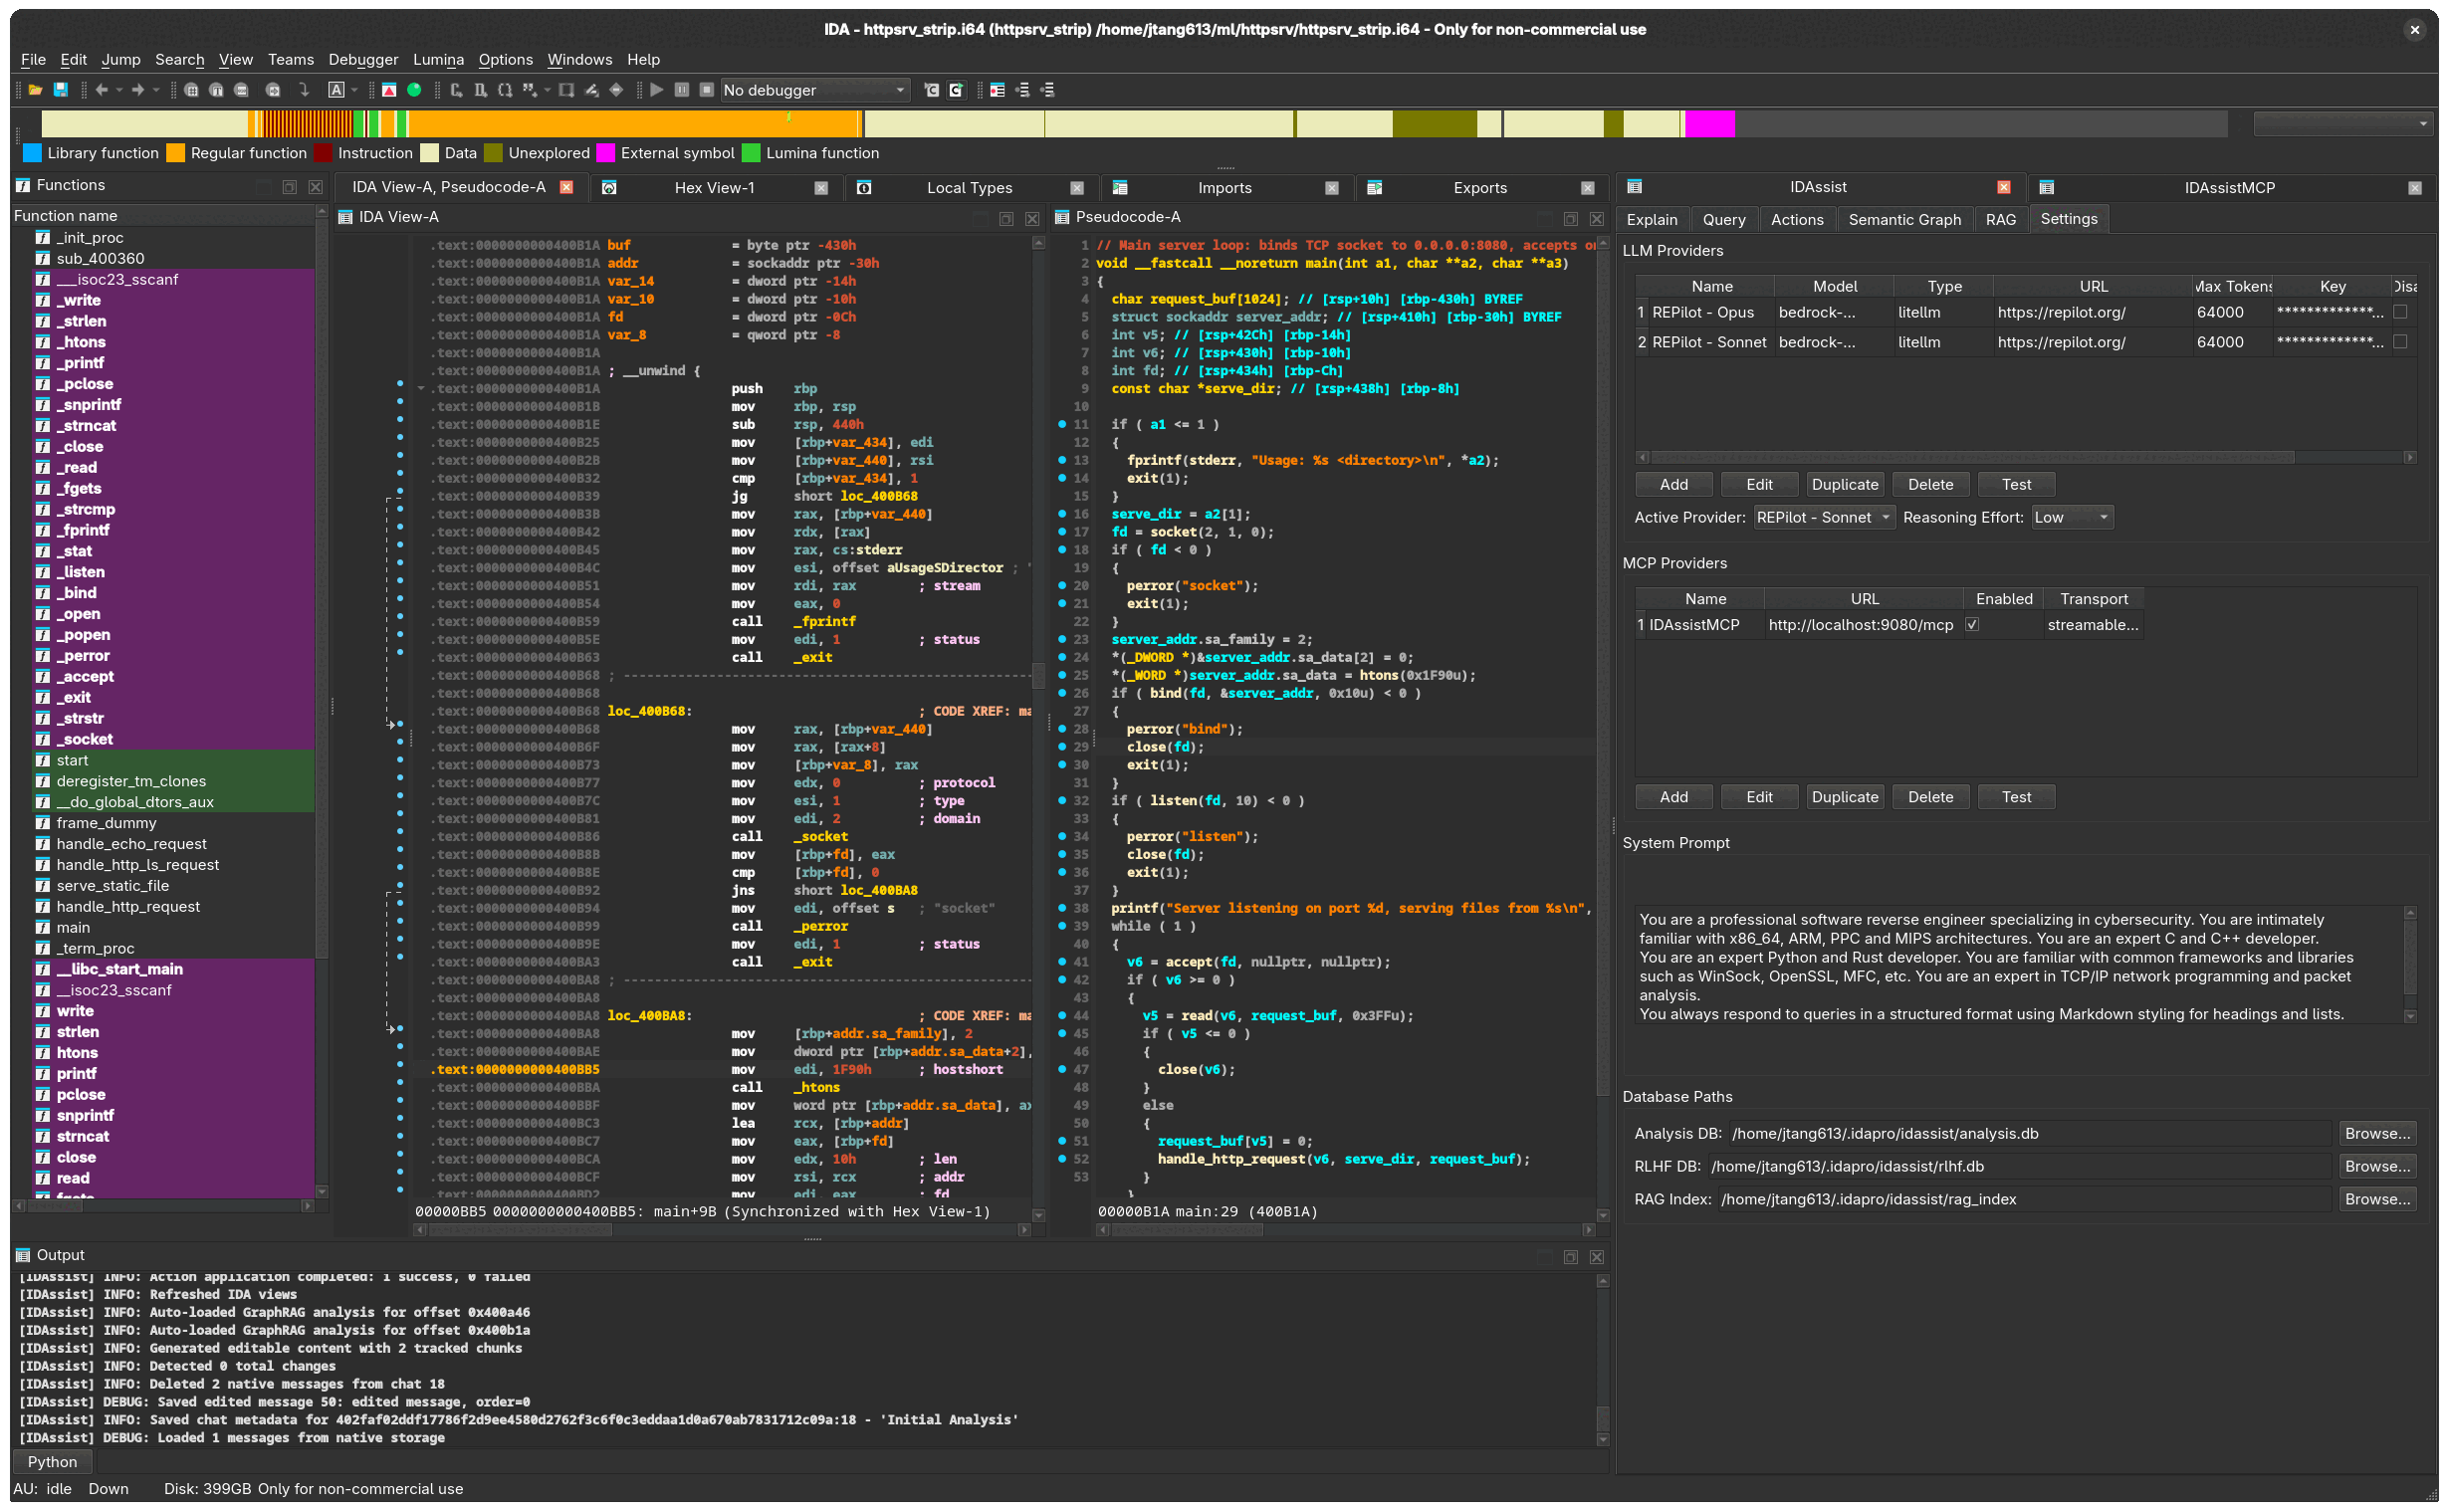 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text
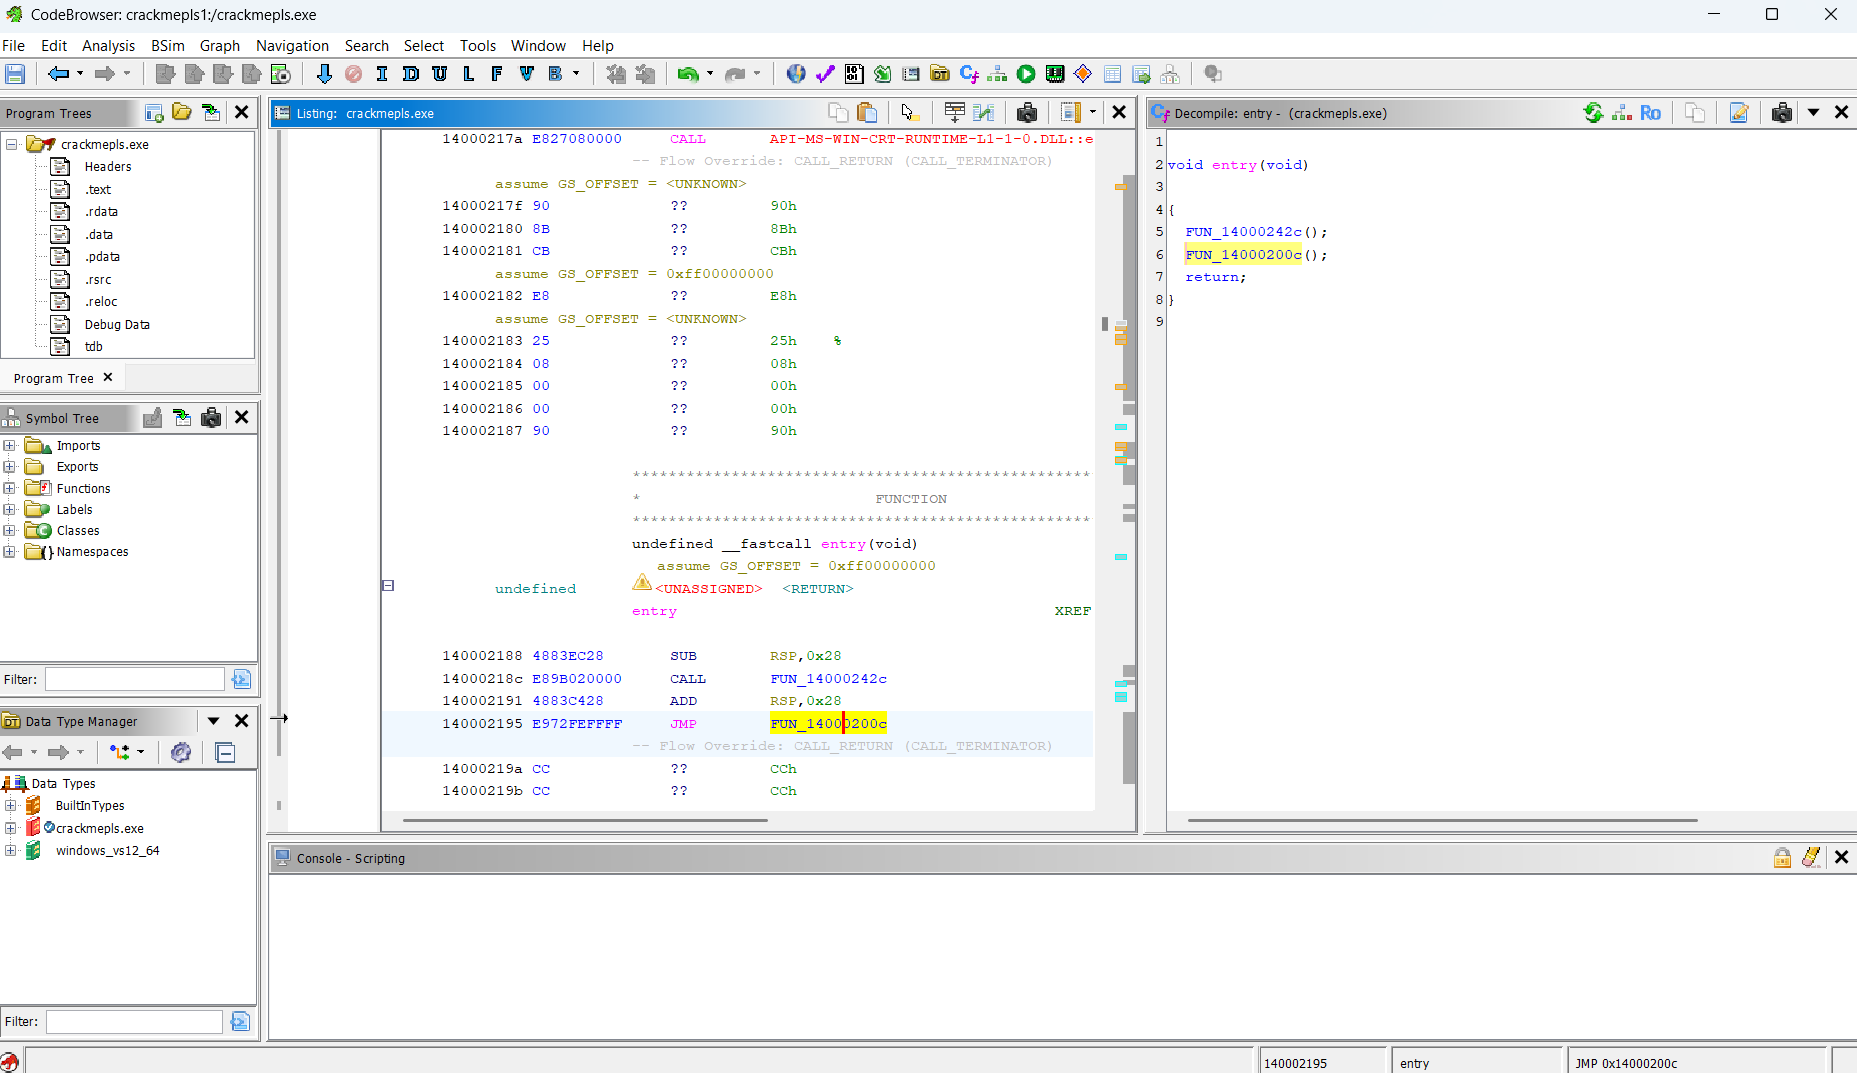 markoglasgow/gemma_crackme_tutorial
Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 qbnasasn/google-tensor-chips
Google Tensor Cracks
 lauriewired/ghidramcp
MCP Server for Ghidra
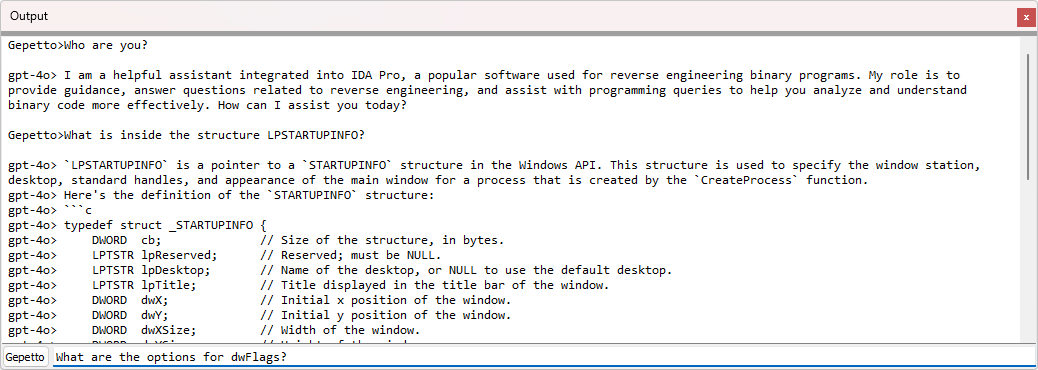 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 trailofbits/fickling
A Python pickling decompiler and static analyzer