
engine
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
android-securitybinary-analysisdynamic-analysis-sandboxing+4
480
droidefense/engineDroidefense: Advance Android Malware Analysis Framework
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
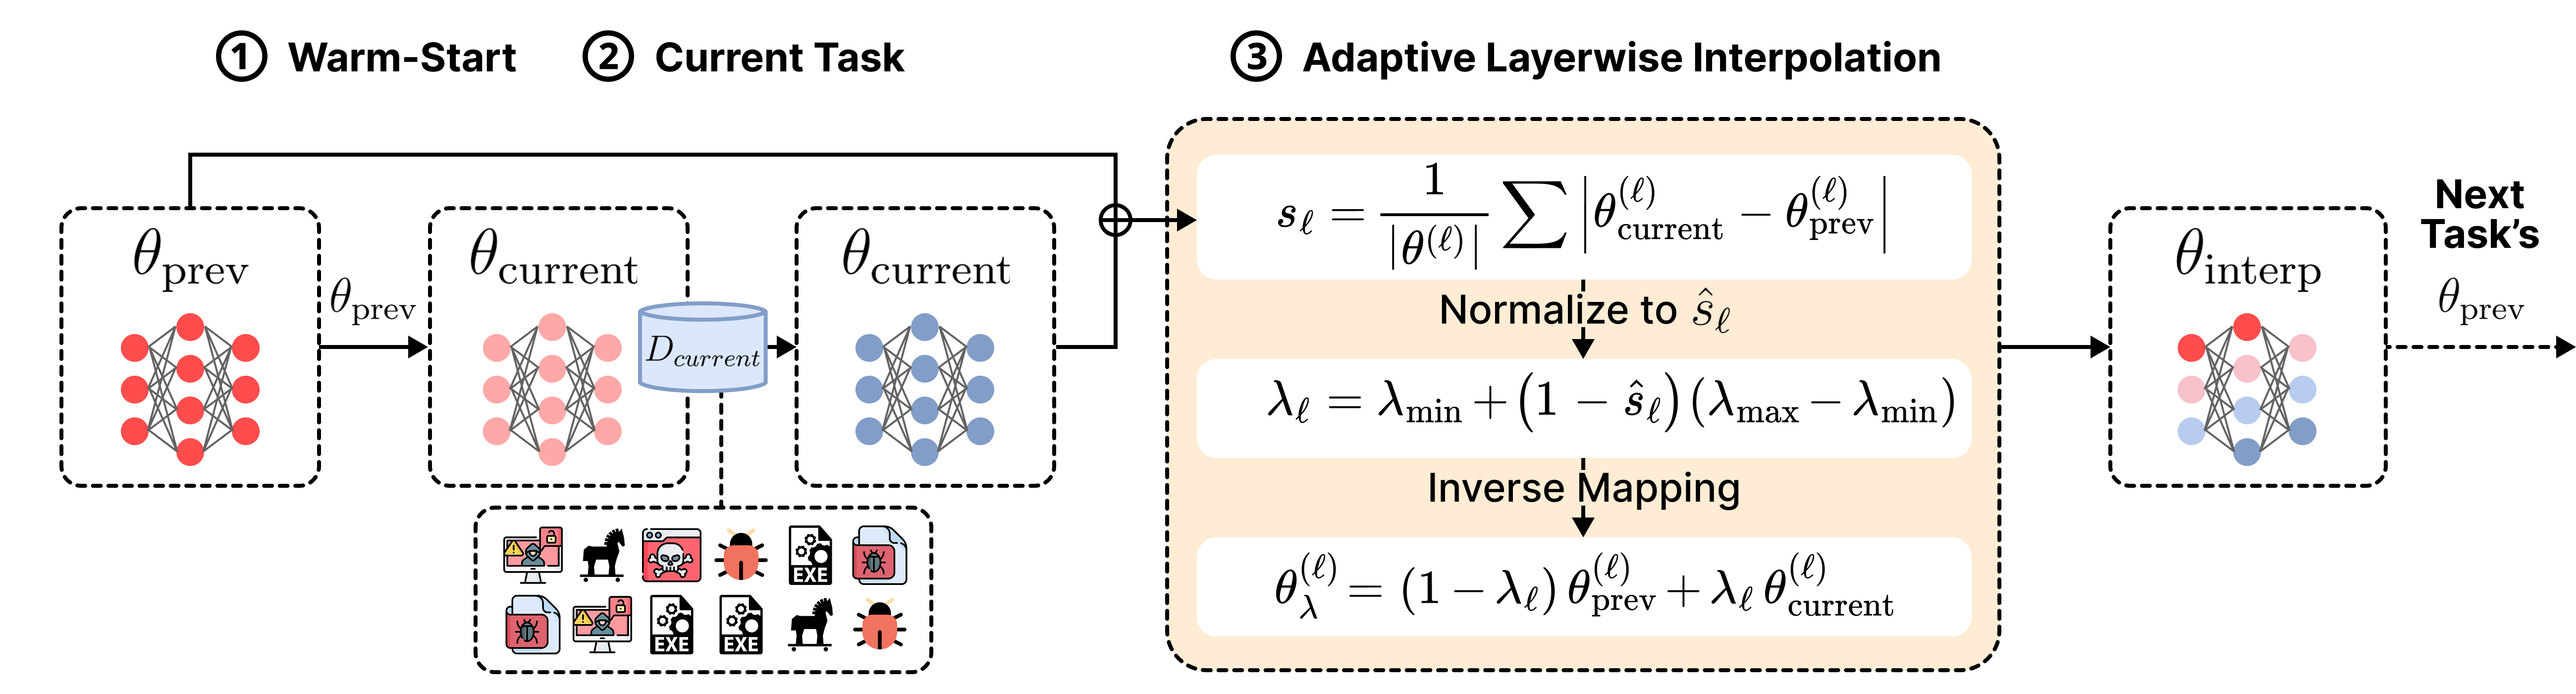 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 vinsontang1/vultriage
The code of VulTriage: Triple-Path Context Augmentation for LLM-Based Vulnerability Detection
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 jonrau1/syntheticsun
Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…
 munshi007/aura-state
Python framework for building LLM workflows as state machines with formal verification via Z3 theorem proving, CTL model checking, and conformal…
 bkcs-hust/lstm-mi
A LSTM based framework for handling multiclass imbalance in DGA botnet detection
 renweimeng/vlun-agent-x
VulnAgent-X: A Layered Agentic Framework for Repository-Level Vulnerability Detection
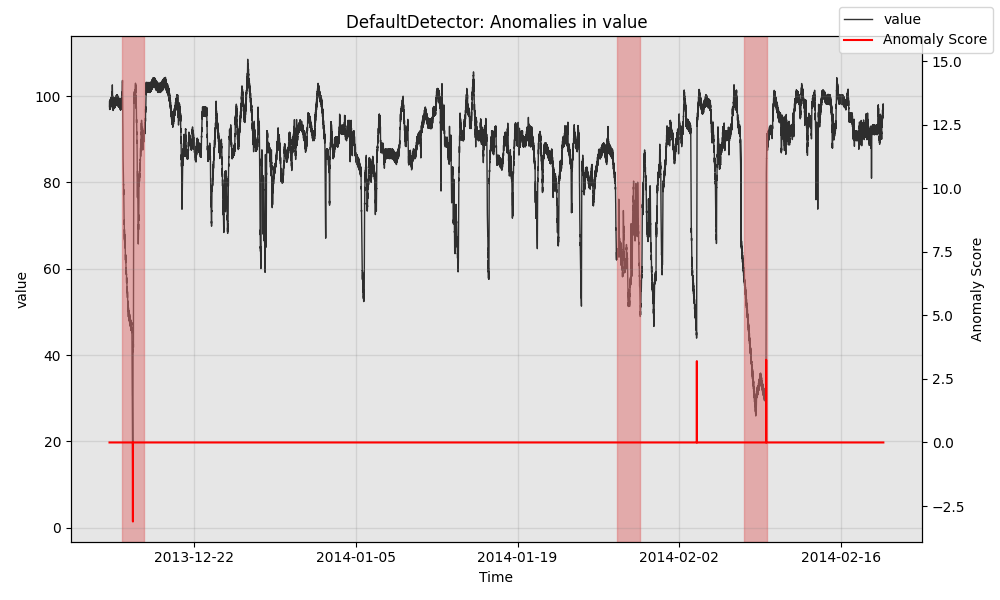 salesforce/merlion
End-to-end Python framework for time series intelligence, offering anomaly detection, forecasting, change point detection, AutoML, ensembles, and…
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
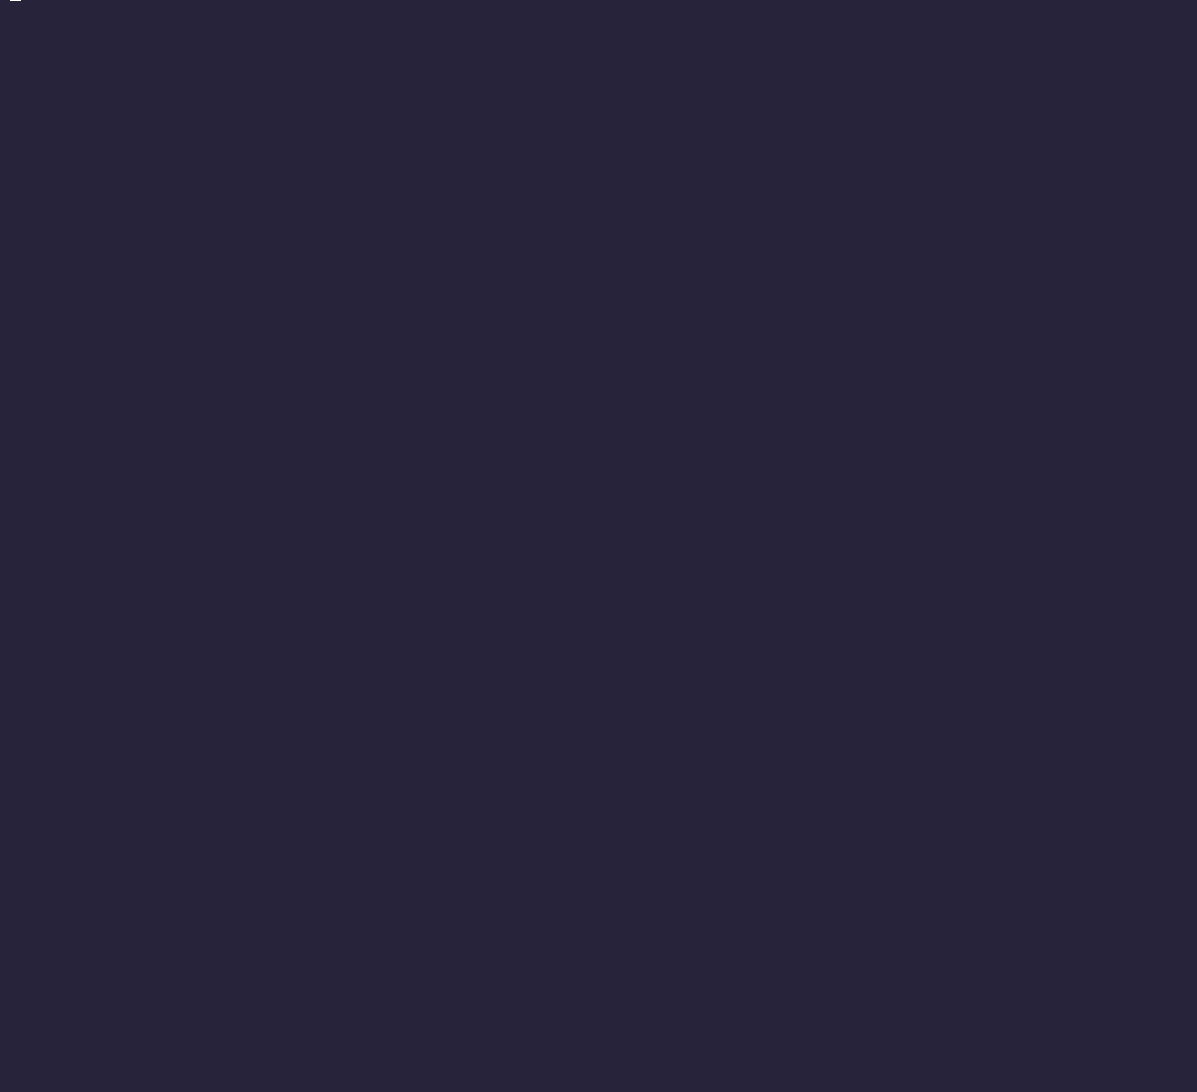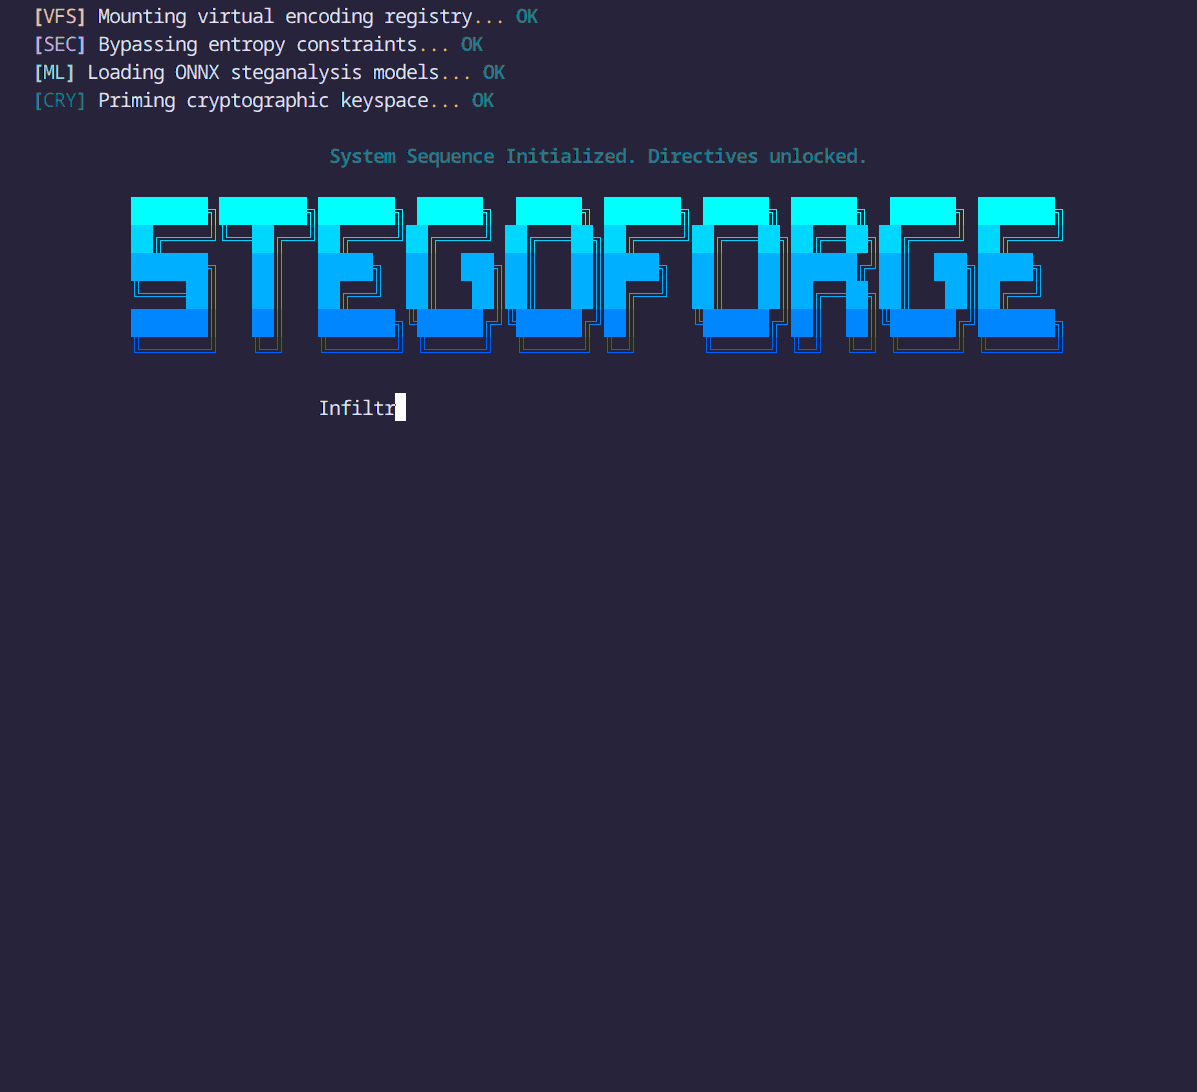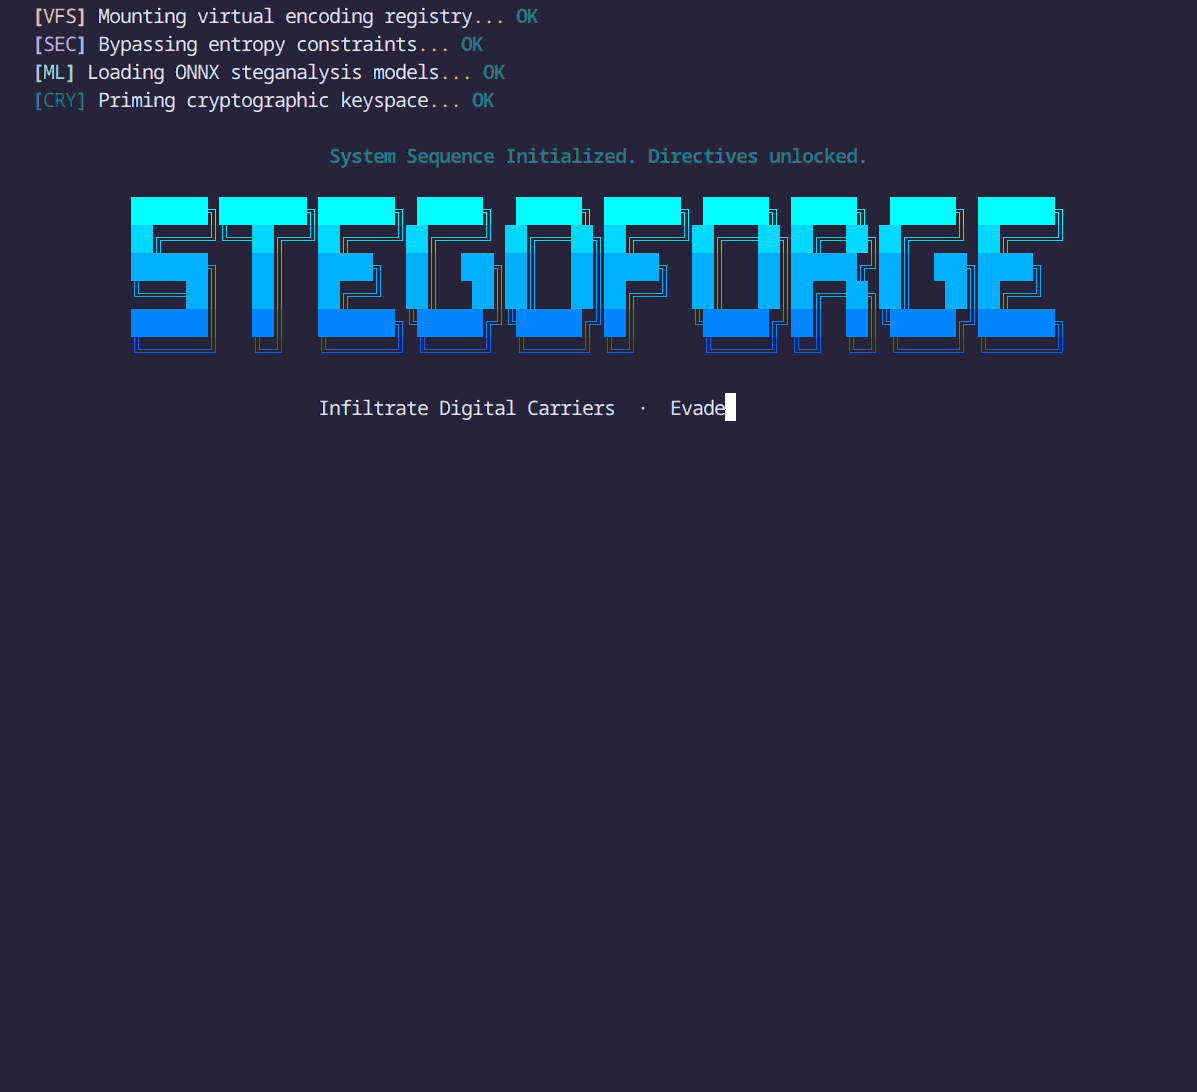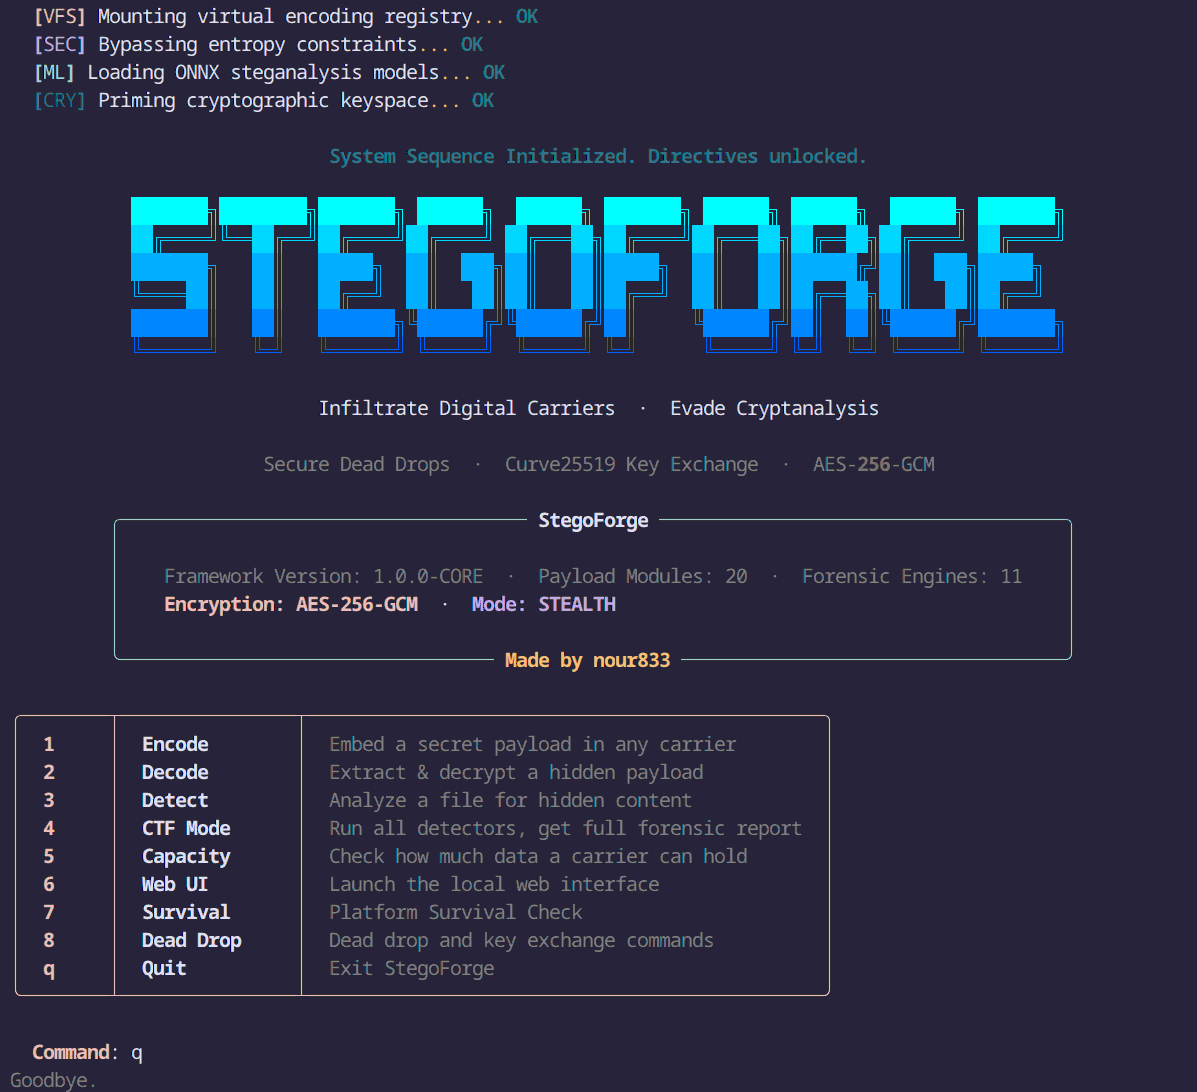 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…